
fsociety
 manisso/fsociety
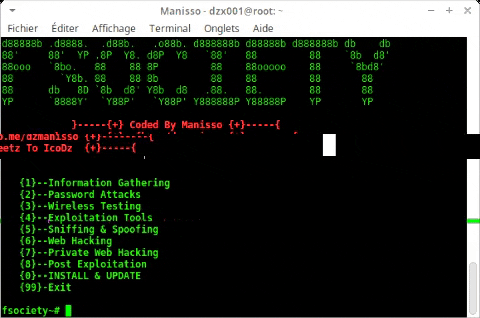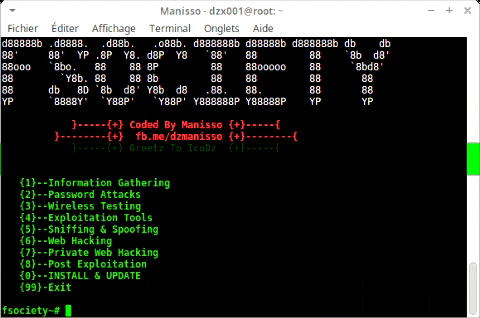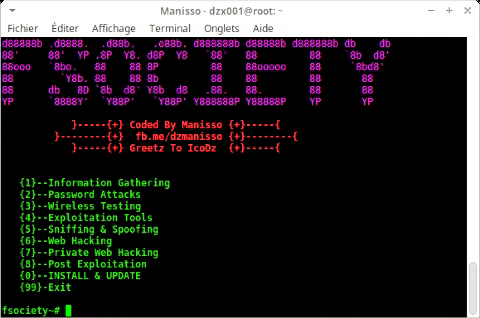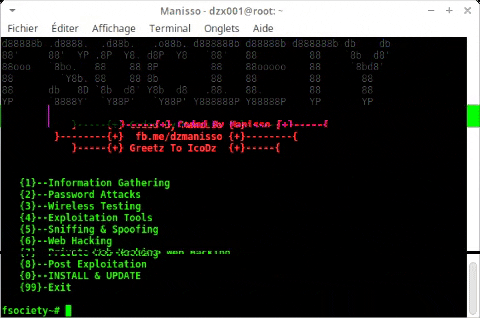
fsociety Hacking Tools Pack – A Penetration Testing Framework
exploitationinformation-gatheringpassword-attacks+6
manisso/fsocietyfsociety Hacking Tools Pack – A Penetration Testing Framework
 capture0x/xss-loader
Xss Payload Generator ~ Xss Scanner ~ Xss Dork Finder
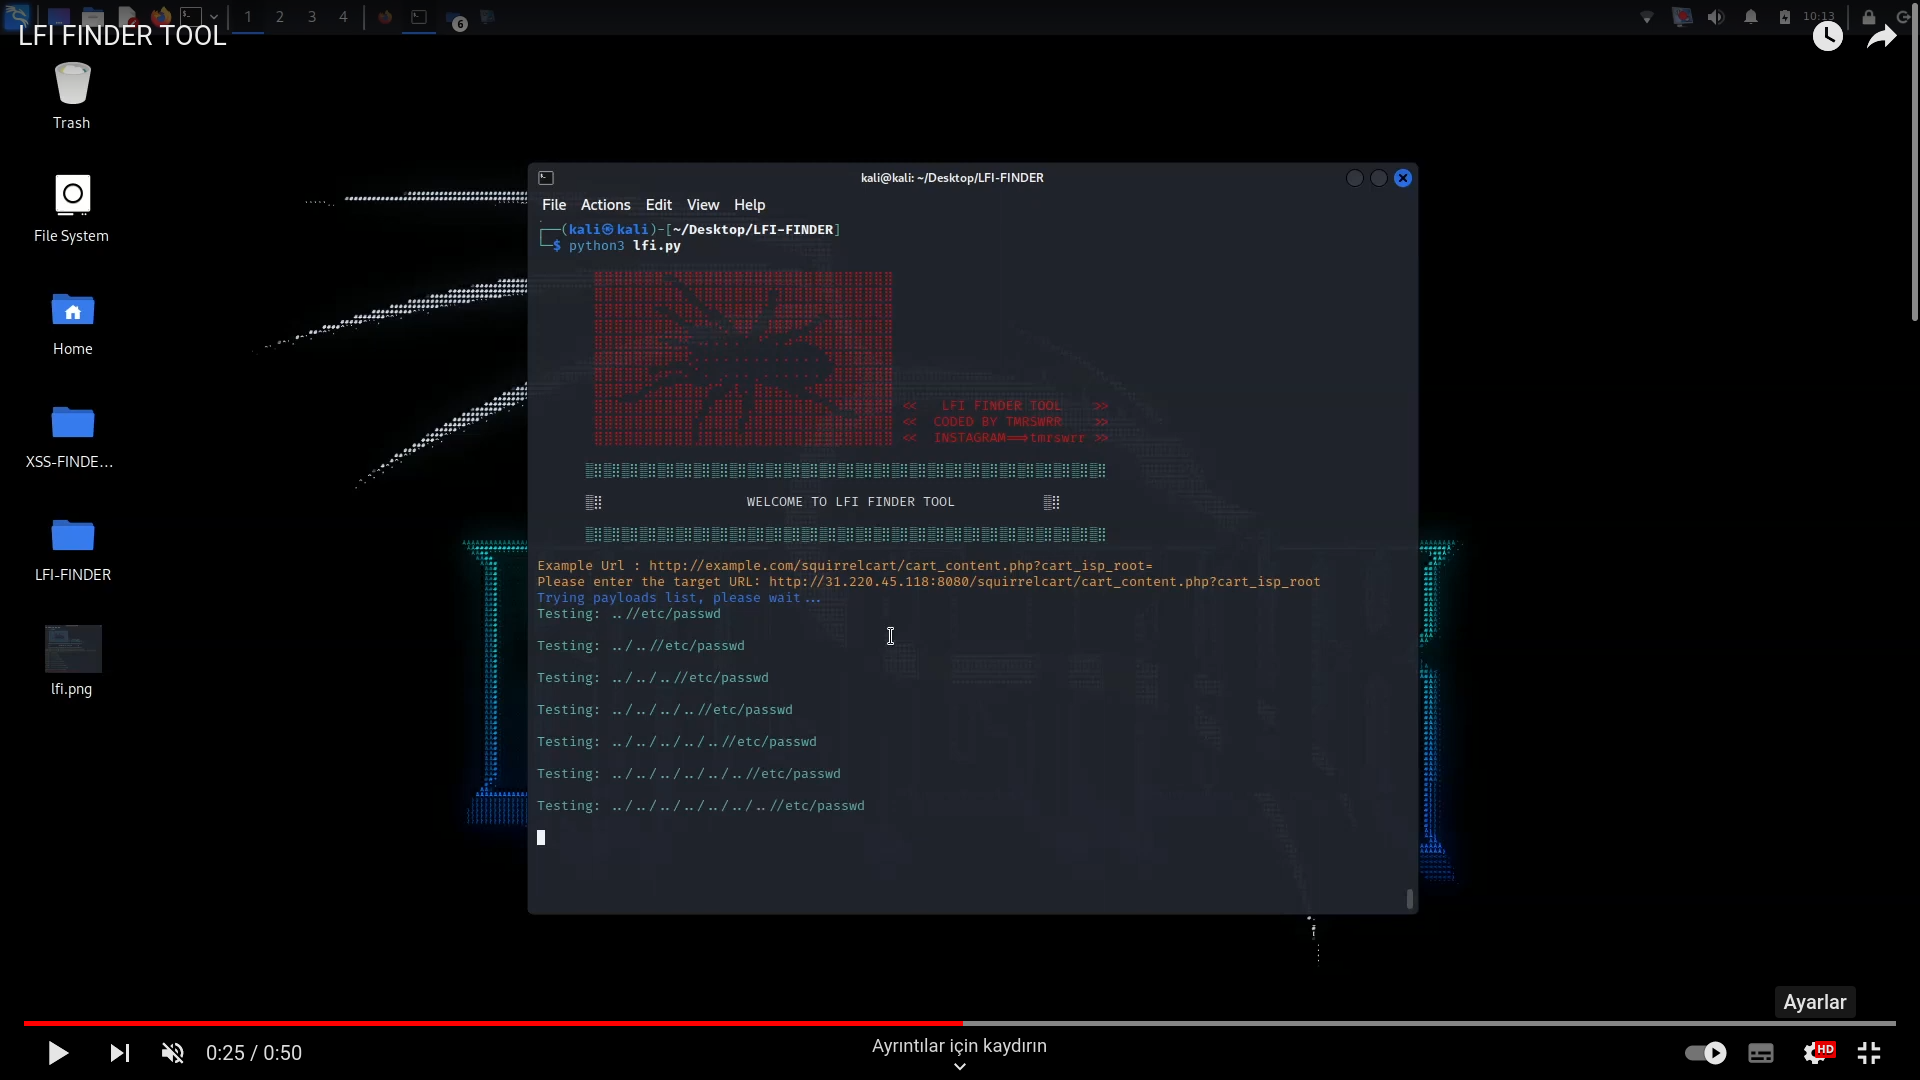 capture0x/lfi-finder
Automated scanner for detecting Local File Inclusion (LFI) vulnerabilities in web applications by analyzing URLs and testing payloads via geckodriver.
 ksharinarayanan/ssrfire
An automated SSRF finder. Just give the domain name and your server and chill! ;) Also has options to find XSS and open redirects
 offxec/thedoc
Automates SQL injection exploitation with SQLMAP, crawls for vulnerabilities, extracts database credentials, finds admin login pages, and cracks…
 bdblackhat/admin-panel-finder
Python script to discover admin panel URLs of websites, aiding in security reconnaissance and penetration testing.
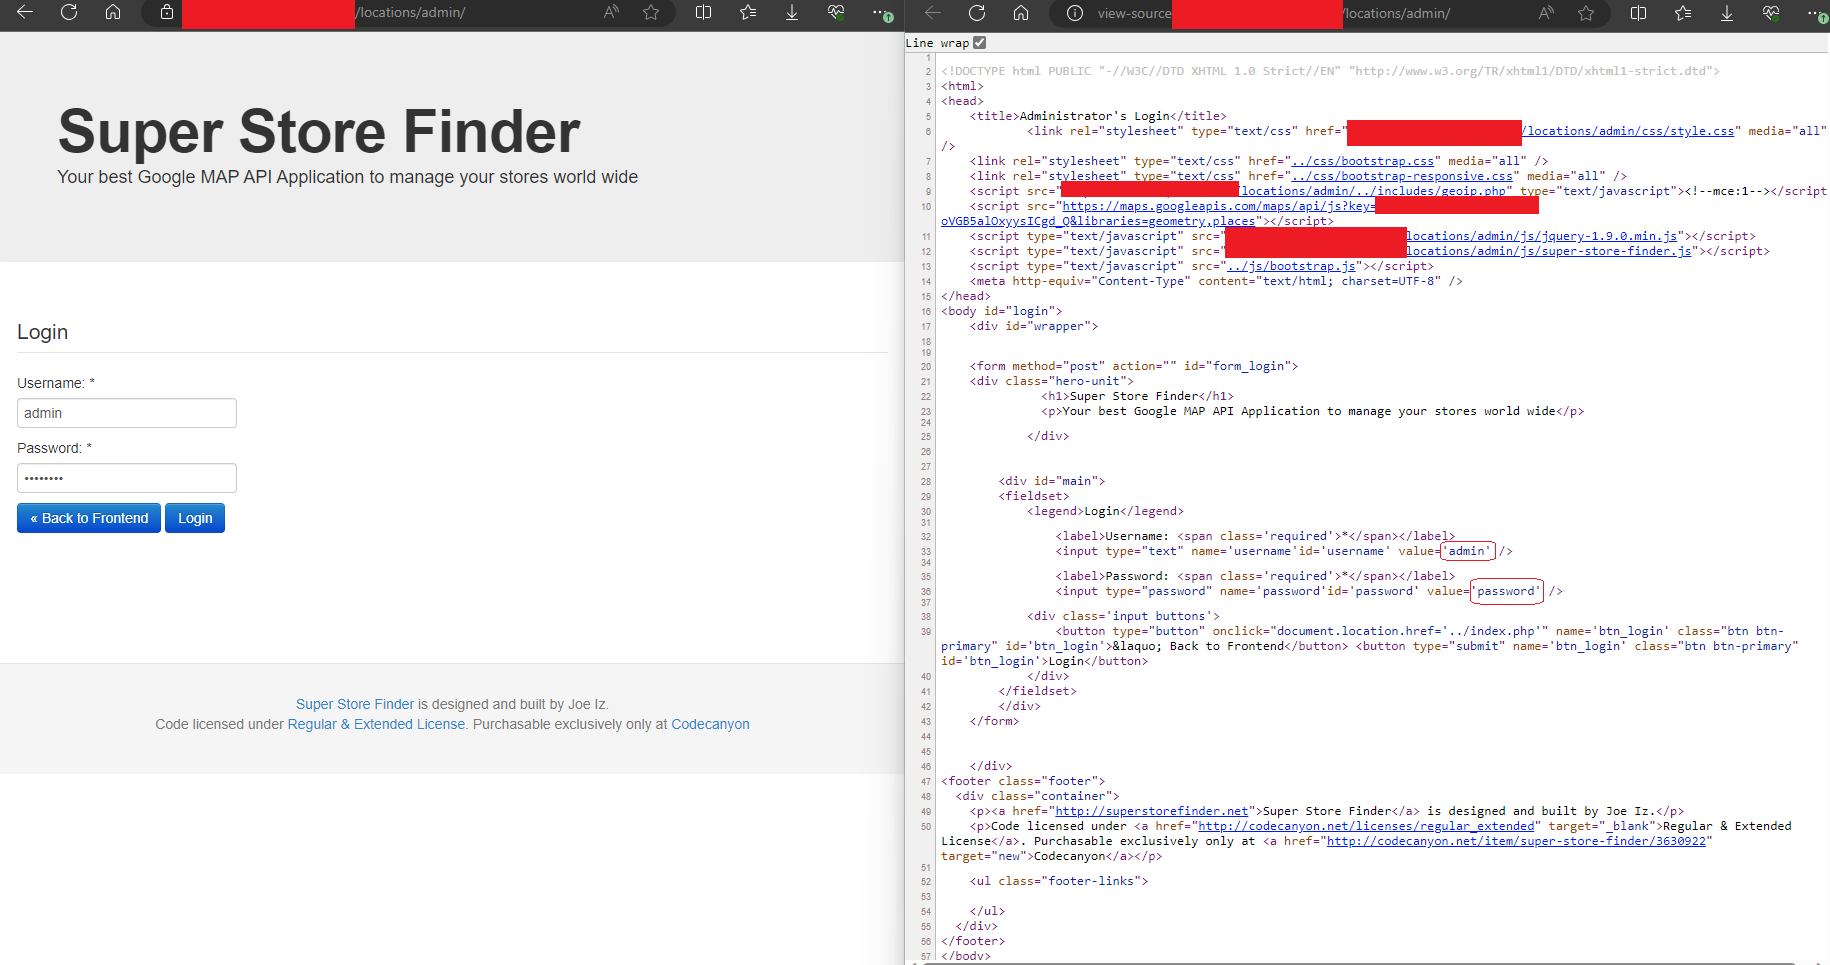 redblueteam/cve-2023-41508
CVE-2023-41508 - A hard-coded password in Super Store Finder v3.6 allows attackers to access the administration panel.
 m4rgs/cve-2025-5947_exploit
An mini exploit for the Service Finder -Bookings plugin WP
 sachinart/cve-2025-54322
CVE-2025-54322 - XSpeeder SXZOS Pre-Auth RCE 0day Finder Quick
 jenderal92/open-redirect-finder
Open Redirect Finder is an automation tool used to detect open redirect vulnerabilities on a URL.
 4xura/cve-2026-44011-craftcms-auth-rce
The PoC of CVE-2026-44011: Craft CMS RCE with an authenticated user.
 xxconi/cve-2025-5947
CVE-2025-5947 WordPress Service Finder Bookings ≤ 6.0 Exploit
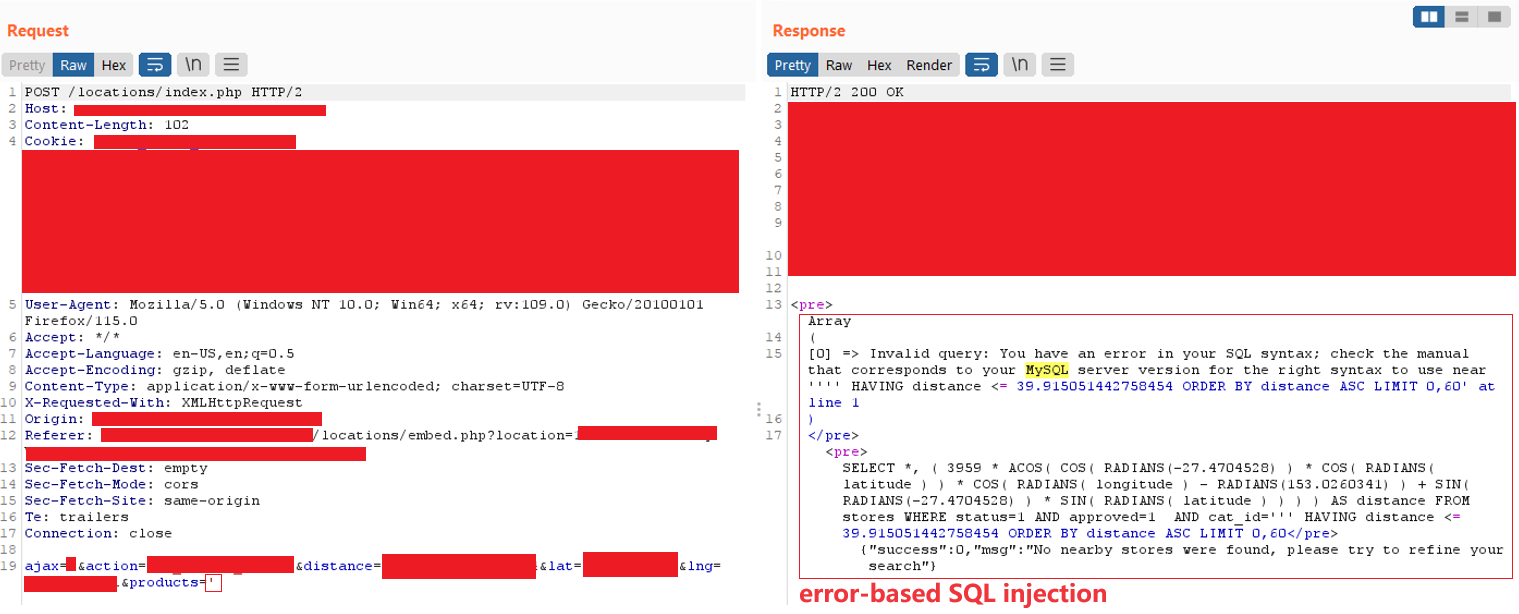 redblueteam/cve-2023-41507
CVE-2023-41507 A hard coded password in Super Store Finder v3.6 allows attackers to access the administration panel.
 wilsc0w/cve-2015-2794-finder
CVE-2015-2794 auto finder