

awswaf
 xkiian/awswaf
AWS WAF Solver, full reverse implemented in 100% Python & Golang.
anti-botcaptcha-bypassids-ips-evasion+3
xkiian/awswafAWS WAF Solver, full reverse implemented in 100% Python & Golang.
 blacklanternsecurity/trevorproxy
A SOCKS proxy written in Python that randomizes your source IP address. Round-robin your evil packets through SSH tunnels or give them billions of…
 fatguru/cve-2025-55182-scanner
A non-intrusive surface scanner for CVE-2025-55182 (React Server Components RCE). Detects exposed RSC endpoints in React 19 and Next.js applications
 perimeterx/cve-2020-6519
Proof-of-concept exploit for CVE-2020-6519, a Content Security Policy bypass vulnerability in Chromium 83, enabling full CSP bypass across platforms.
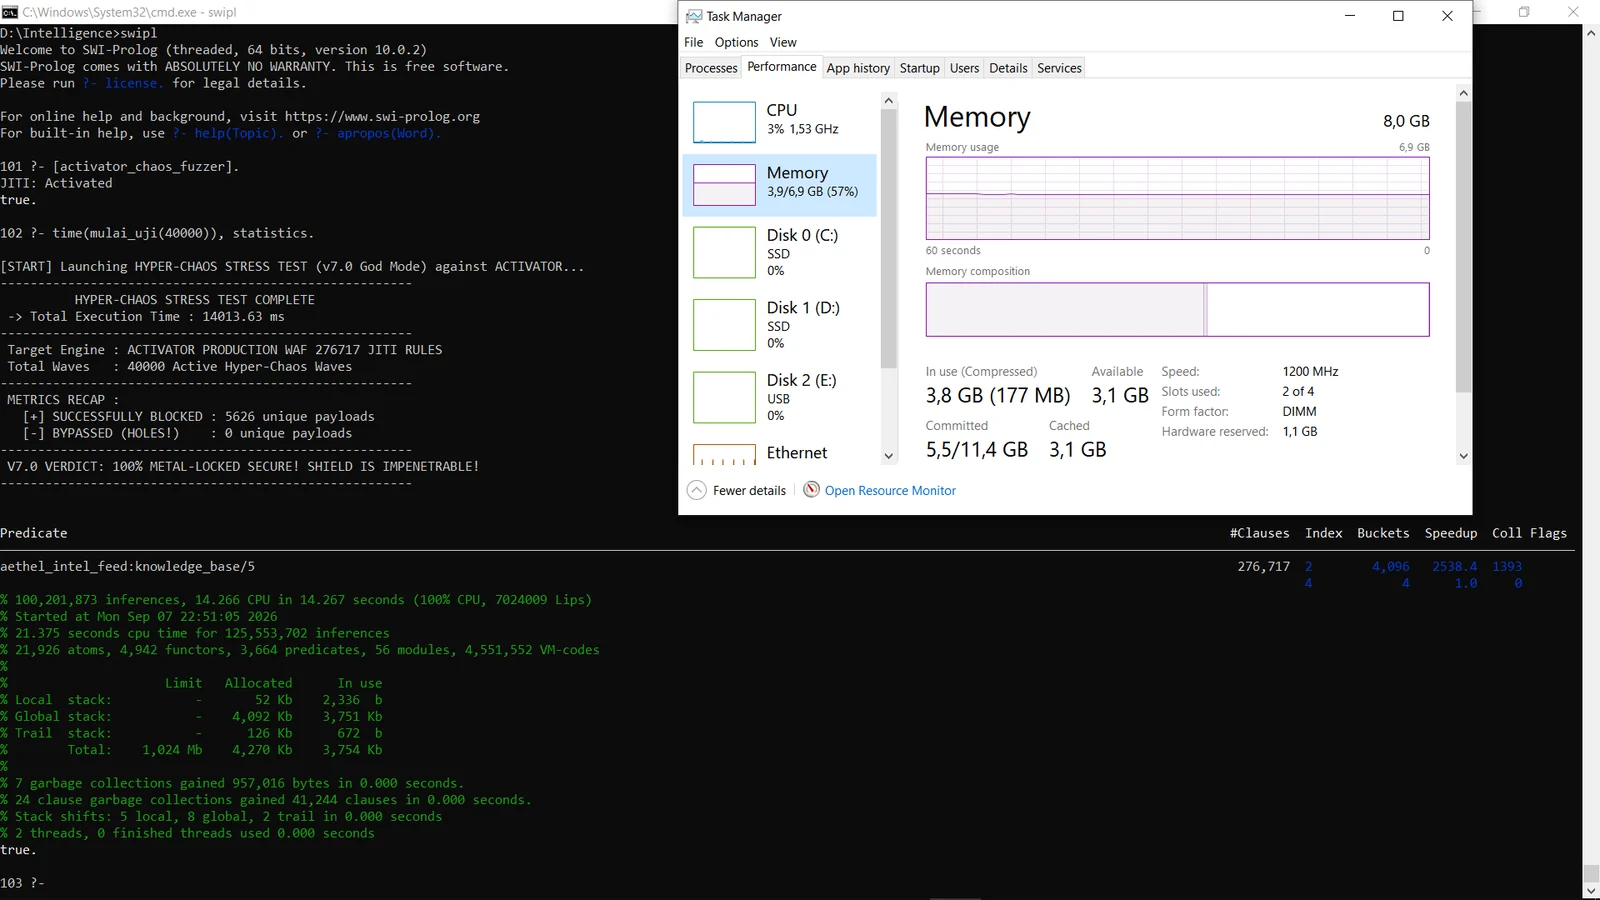 lokinpendawa/aethel_core
Next-gen logical WAF engine built in SWI-Prolog. Features an inductive learning brain running at 2M+ LIPS with an integrated recursive decoder to…
 farhan9488/cve-2025-55182-research
🛡️ Explore CVE-2025-55182, a critical RCE vulnerability in React's Flight Protocol, demonstrating exploitation techniques and mitigation strategies.
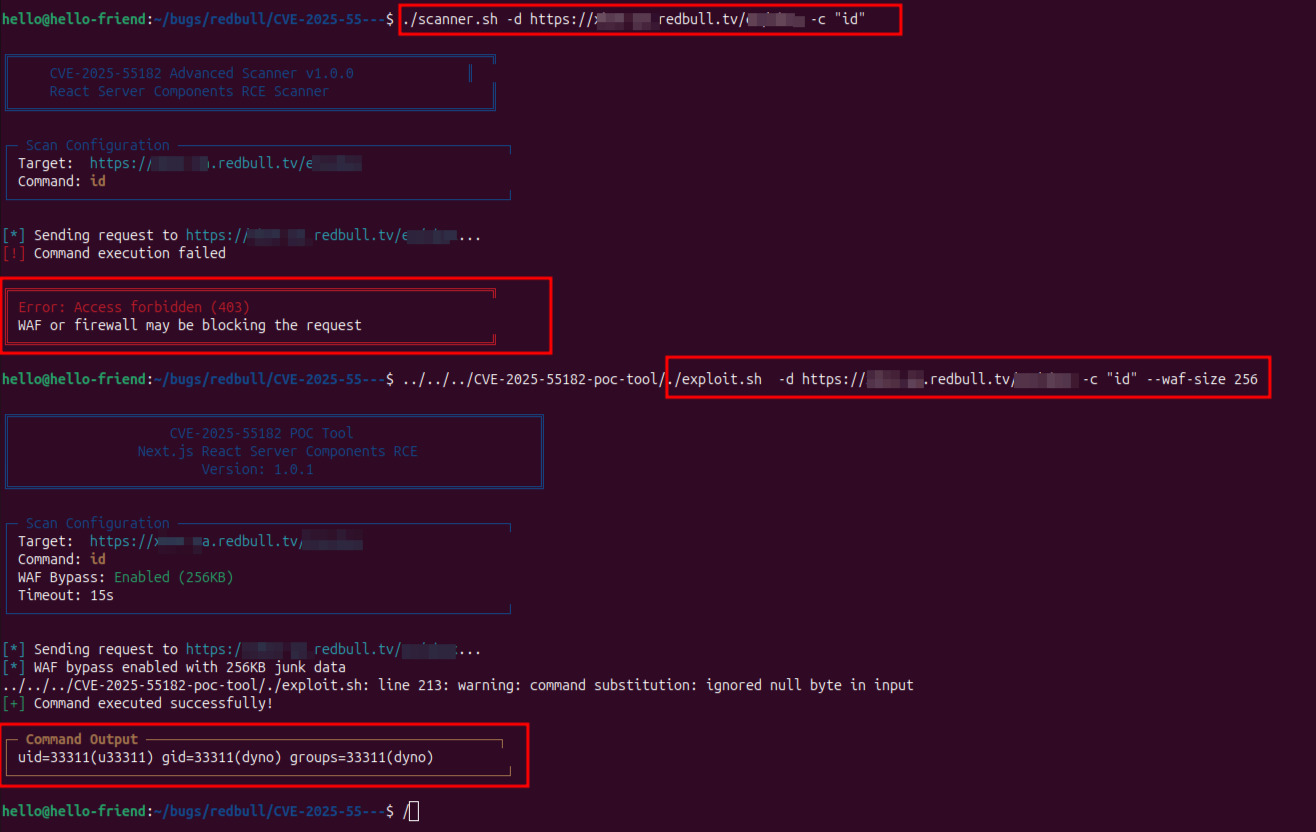 dh4v4l8/cve-2025-55182-poc-tool
Automated exploit tool for CVE-2025-55182 in Next.js React Server Components. Enables remote command execution with built-in WAF bypass, custom…
 joelvaiju/react2shell-cve-2025-55182-poc
Python PoC for CVE-2025-55182 (React2Shell) RCE in Next.js/React Server Components with dynamic WAF bypass padding for authorized security testing.
 harness-security-labs/cve-2025-55182-checker
Multi-technique vulnerability detector for CVE-2025-55182 in React/Next.js applications. Tests gadget chains, RCE payloads, and WAF bypass variants…
 ancs21/react2shell-scanner-rust
Detect CVE-2025-55182 & CVE-2025-66478 in Next.js/RSC applications (Rust)
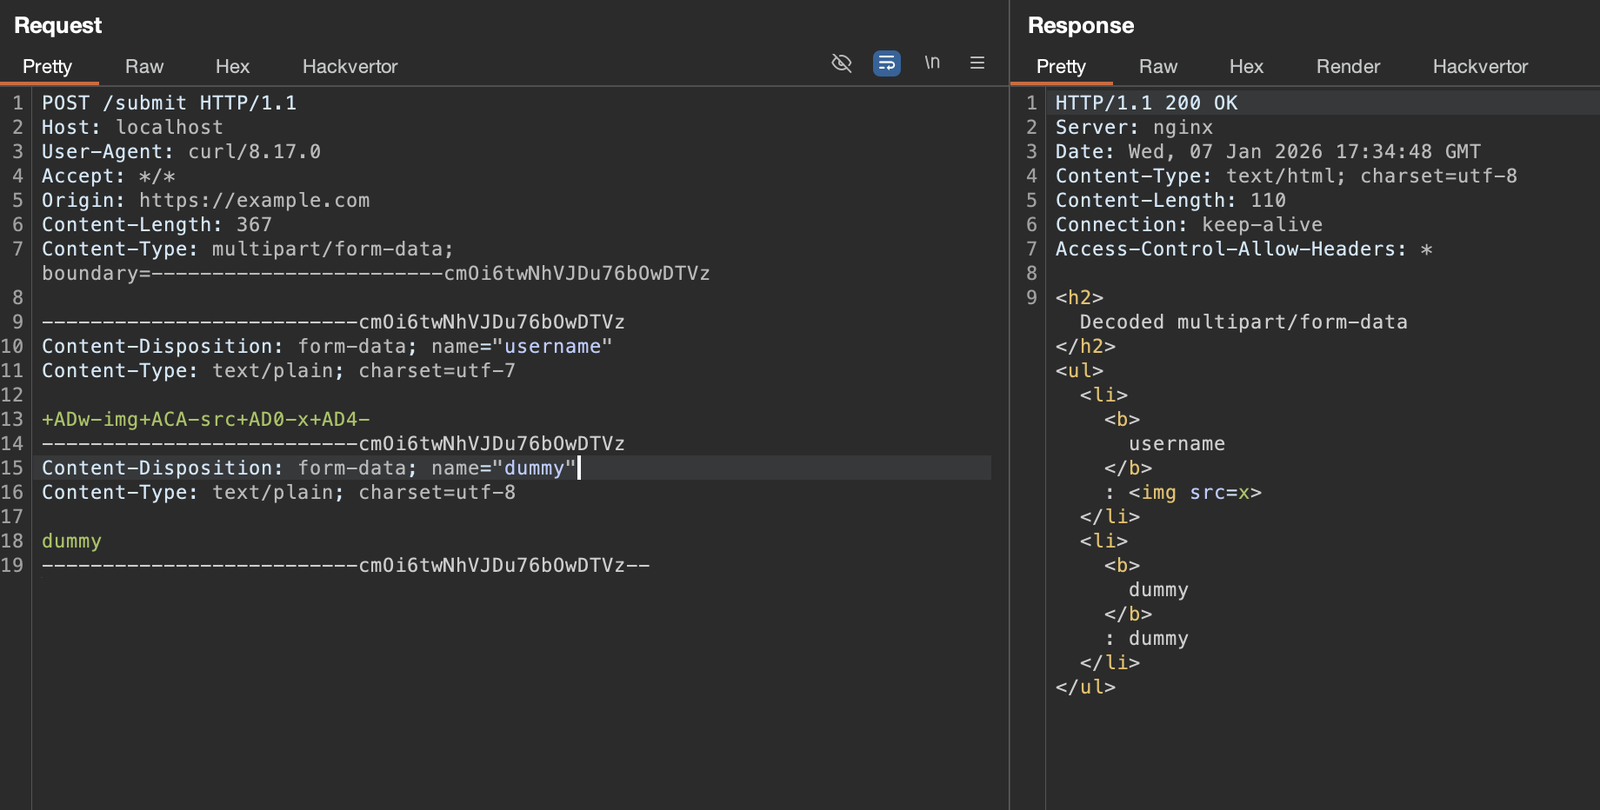 mefhika120/cve-2026-21876
Minimal PoC and Docker container demonstrating a WAF bypass in OWASP ModSecurity CRS via multipart charset handling, leading to XSS payload delivery.
 imbas007/cve-2025-32429-checker
Python-based vulnerability scanner for detecting CVE-2025-32429 SQL injection in XWiki platforms. Supports single/bulk scanning, WAF detection,…
 bytereaper77/cve-2025-59342
C exploit for CVE-2025-59342 path traversal in esm.sh CDN (v136 and earlier). Injects payloads via X-Zone-Id header with WAF bypass and cookie…
 bytereaper77/cve-2025-41373
PoC for CVE-2025-41373 Authenticated SQL Injection in Gandia Integra Total v2.1.2217.3–4.4.2236.1

 epi052/feroxbuster
A fast, simple, recursive content discovery tool written in Rust.
 wallarm/gotestwaf
An open-source project in Golang to asess different API Security tools and WAF for detection logic and bypasses
 lobuhi/byp4xx
40X/HTTP bypasser in Go. Features: Verb tampering, headers, #bugbountytips, User-Agents, extensions, default credentials...