
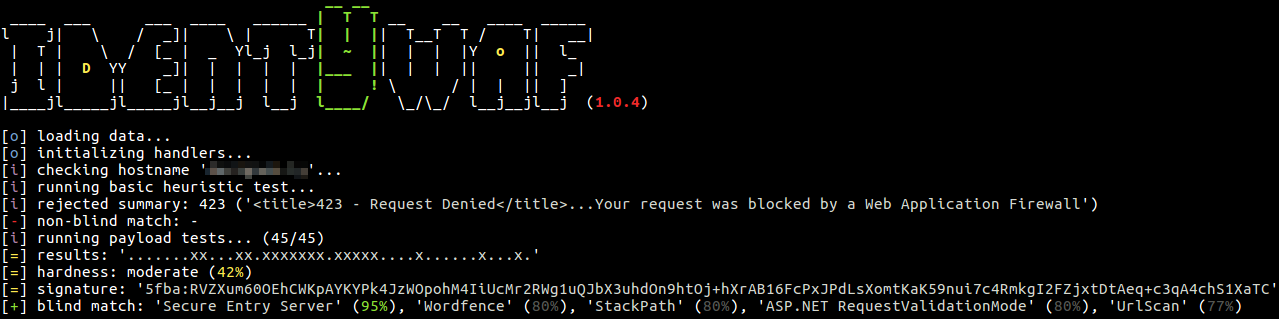
identYwaf
 stamparm/identywaf
Blind WAF identification tool
information-gatheringvulnerability-scannerswaf-bypass+1
stamparm/identywafBlind WAF identification tool
 al0ne/vxscan
python3写的综合扫描工具,主要用来存活验证,敏感文件探测(目录扫描/js泄露接口/html注释泄露),WAF/CDN识别,端口扫描,指纹/服务识别,操作系统识别,POC扫描,SQL注入,绕过CDN,查询旁站等功能,主要用来甲方自测或乙方授权测试,请勿用来搞破坏。
 matrixleons/evilwaf
evilwaf is a penetration testing tool designed to detect and bypass common Web Application Firewalls (WAFs).
 lobuhi/byp4xx
40X/HTTP bypasser in Go. Features: Verb tampering, headers, #bugbountytips, User-Agents, extensions, default credentials...
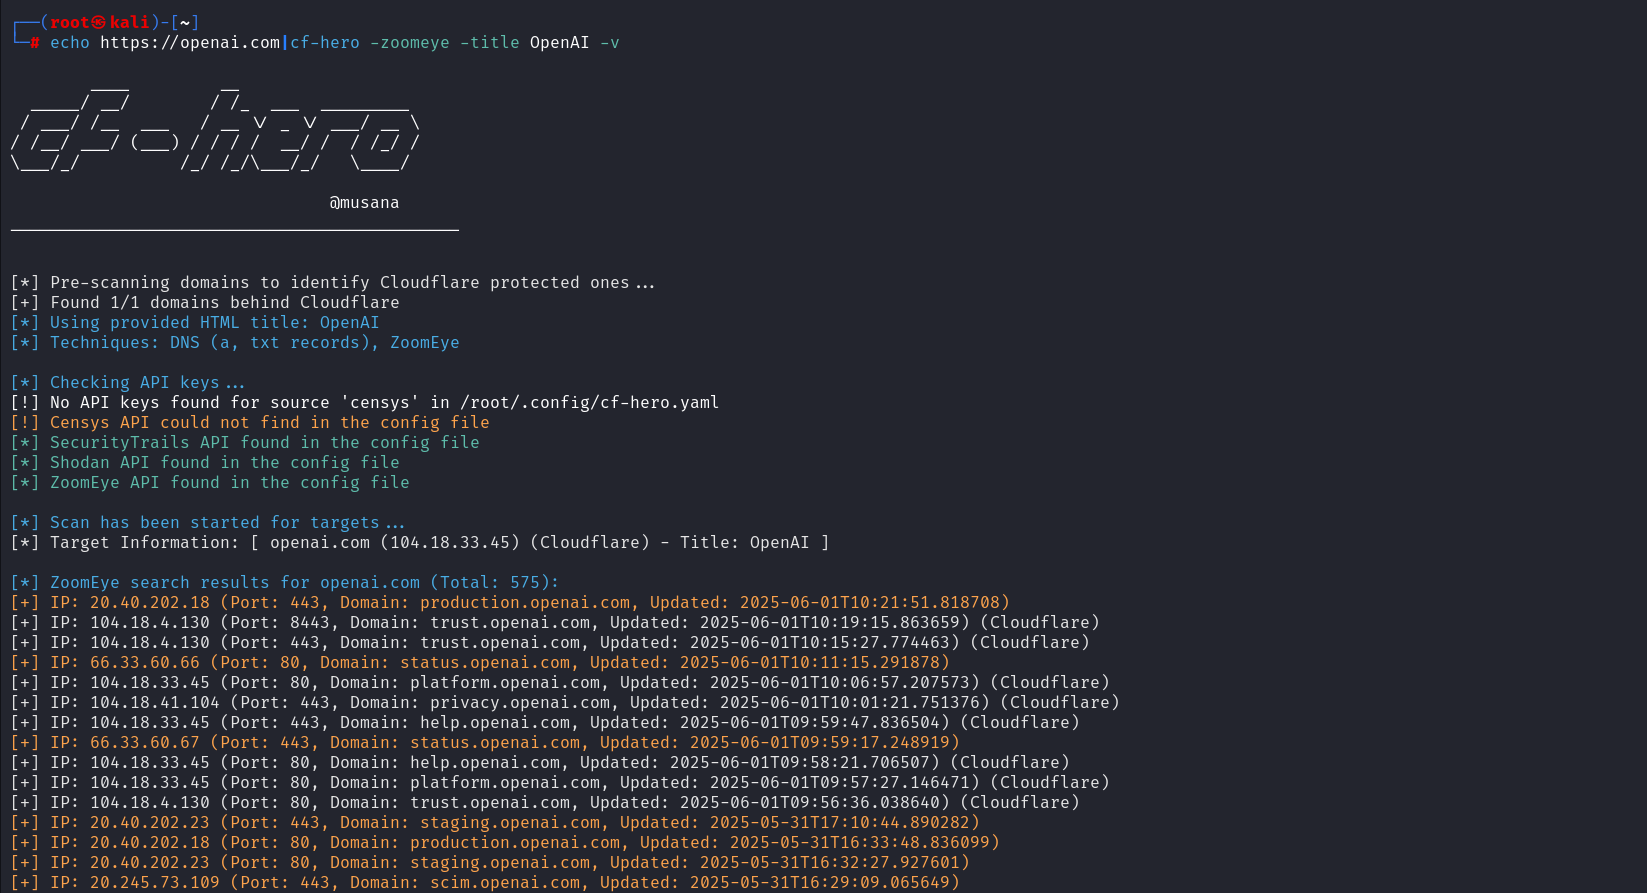 musana/cf-hero
CF-Hero is a reconnaissance tool that uses multiple data sources to discover the origin IP addresses of Cloudflare-protected web applications
 hakluke/hakoriginfinder
Tool for discovering the origin host behind a reverse proxy. Useful for bypassing cloud WAFs!
 laluka/bypass-url-parser
Tests hundreds of URL bypass techniques against 40X protected pages using raw curl requests, with multi-mode scanning, header spoofing, and JSON/HTML…
 ekultek/zeus-scanner
Advanced reconnaissance utility
 zigoo0/jsonbee
A ready to use JSONP endpoints/payloads to help bypass content security policy (CSP) of different websites.
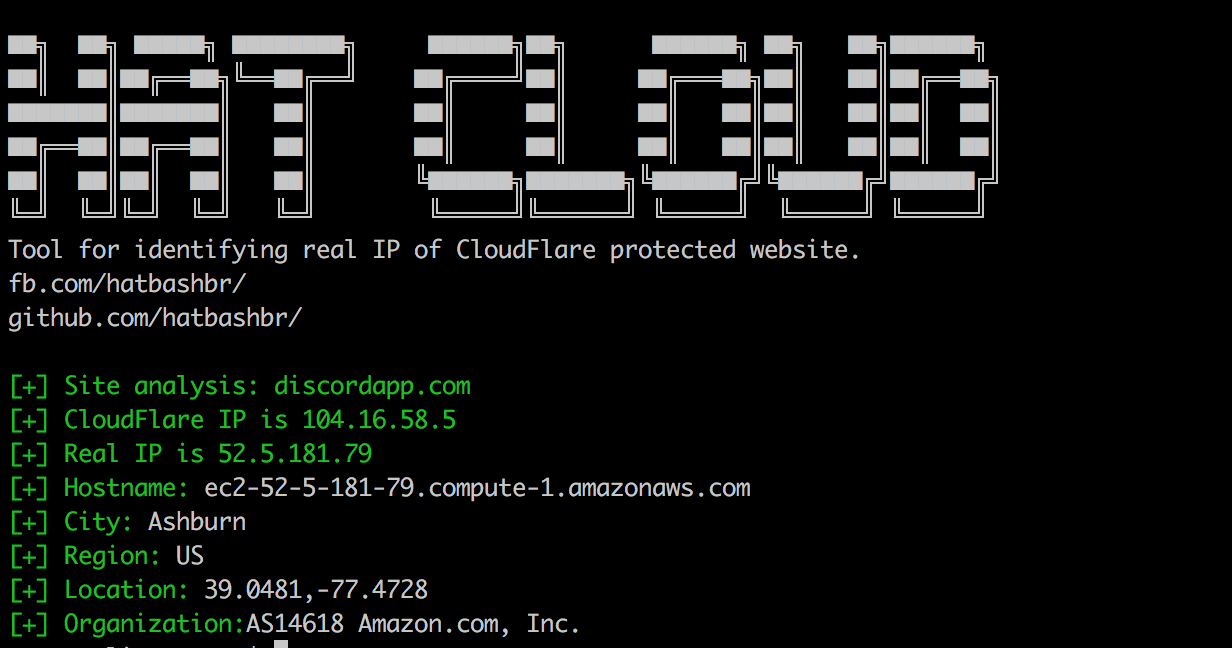
 zigoo0/webpwn3r
WebPwn3r - Web Applications Security Scanner.
 c0dejump/hawkscan
Security Tool for Reconnaissance and Information Gathering on a website. (python 3.x)
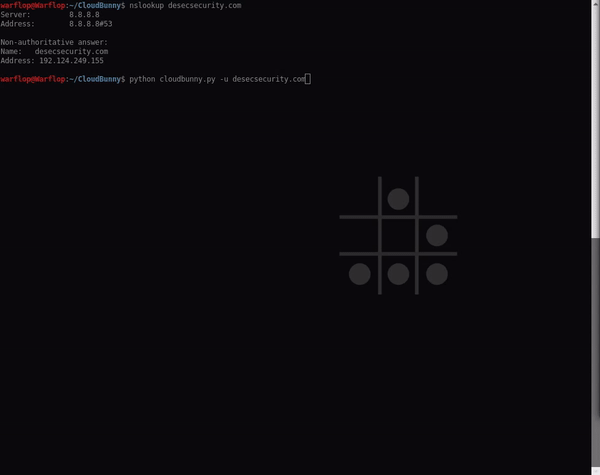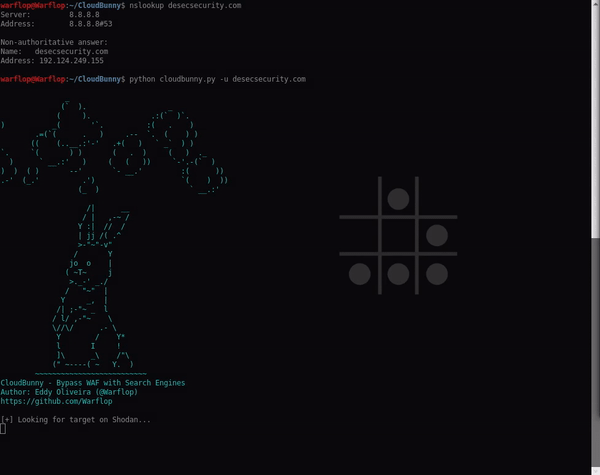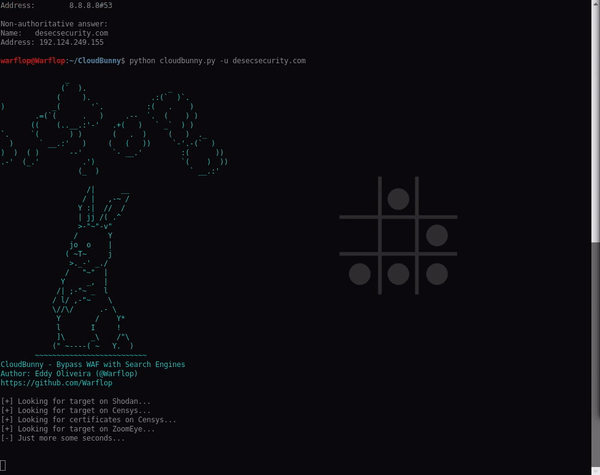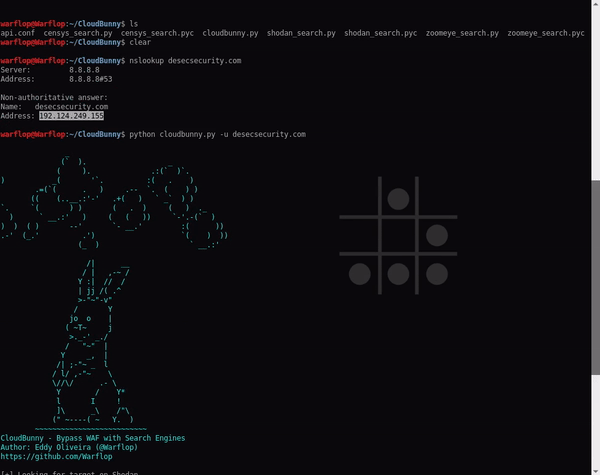 warflop/cloudbunny
CloudBunny is a tool to capture the real IP of the server that uses a WAF as a proxy or protection. In this tool we used three search engines to…
 codingo/crithit
Takes a single wordlist item and tests it one by one over a large collection of websites before moving onto the next. Create signatures to…
 keramas/mssqli-duet
SQL injection script for MSSQL that extracts domain users from an Active Directory environment based on RID bruteforcing
 ammarion/waf-detector
🛡️ High-performance WAF & CDN detection tool. Identify protection layers (Cloudflare, Akamai, AWS, Fastly, and more), run effectiveness and…
 san-tus/dorkwright
From Dork to Download: Automating Google Dorks with Playwright
 yehia-mamdouh/xssya-v-2.0
Python XSS scanner that confirms reflected and encoded-payload injection, executes payloads to capture cookies, detects WAFs, and tests XST with a…