
CRLFsuite
 raghavd3v/crlfsuite
The most powerful CRLF injection (HTTP Response Splitting) scanner.
penetration-testingvulnerability-scannerswaf-bypass+2
6002 years ago
raghavd3v/crlfsuiteThe most powerful CRLF injection (HTTP Response Splitting) scanner.
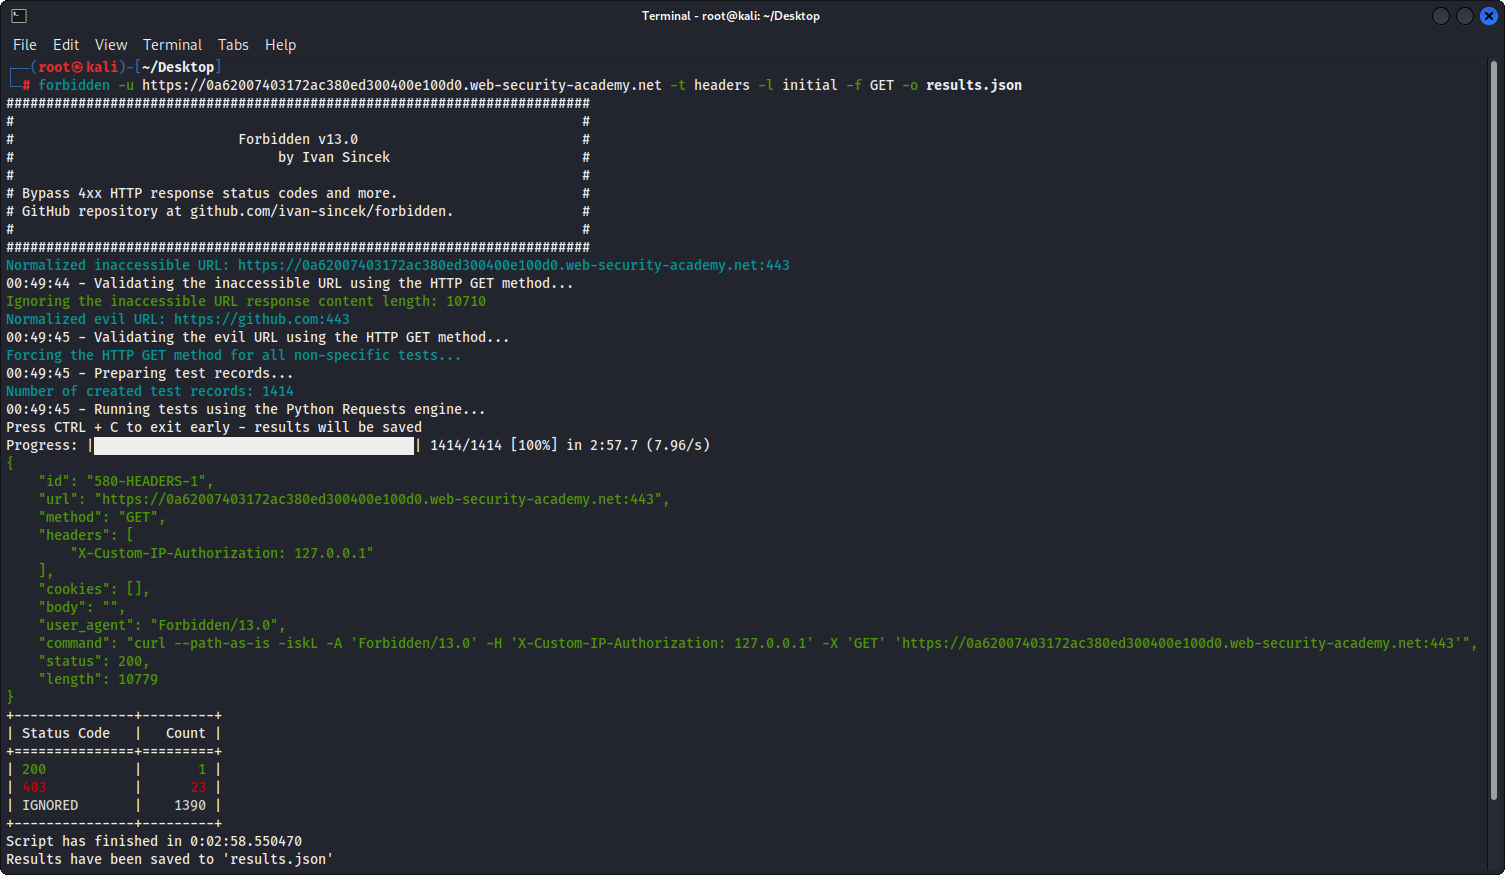 ivan-sincek/forbidden
Bypass 4xx HTTP response status codes and more. The tool is based on Python Requests, PycURL, and HTTP Client.
 th-secforge/cve-2025-55182
Scans for CVE-2025-55182, a critical RCE in React Server Components, with safe-check mode, WAF bypass, and multi-target scanning.

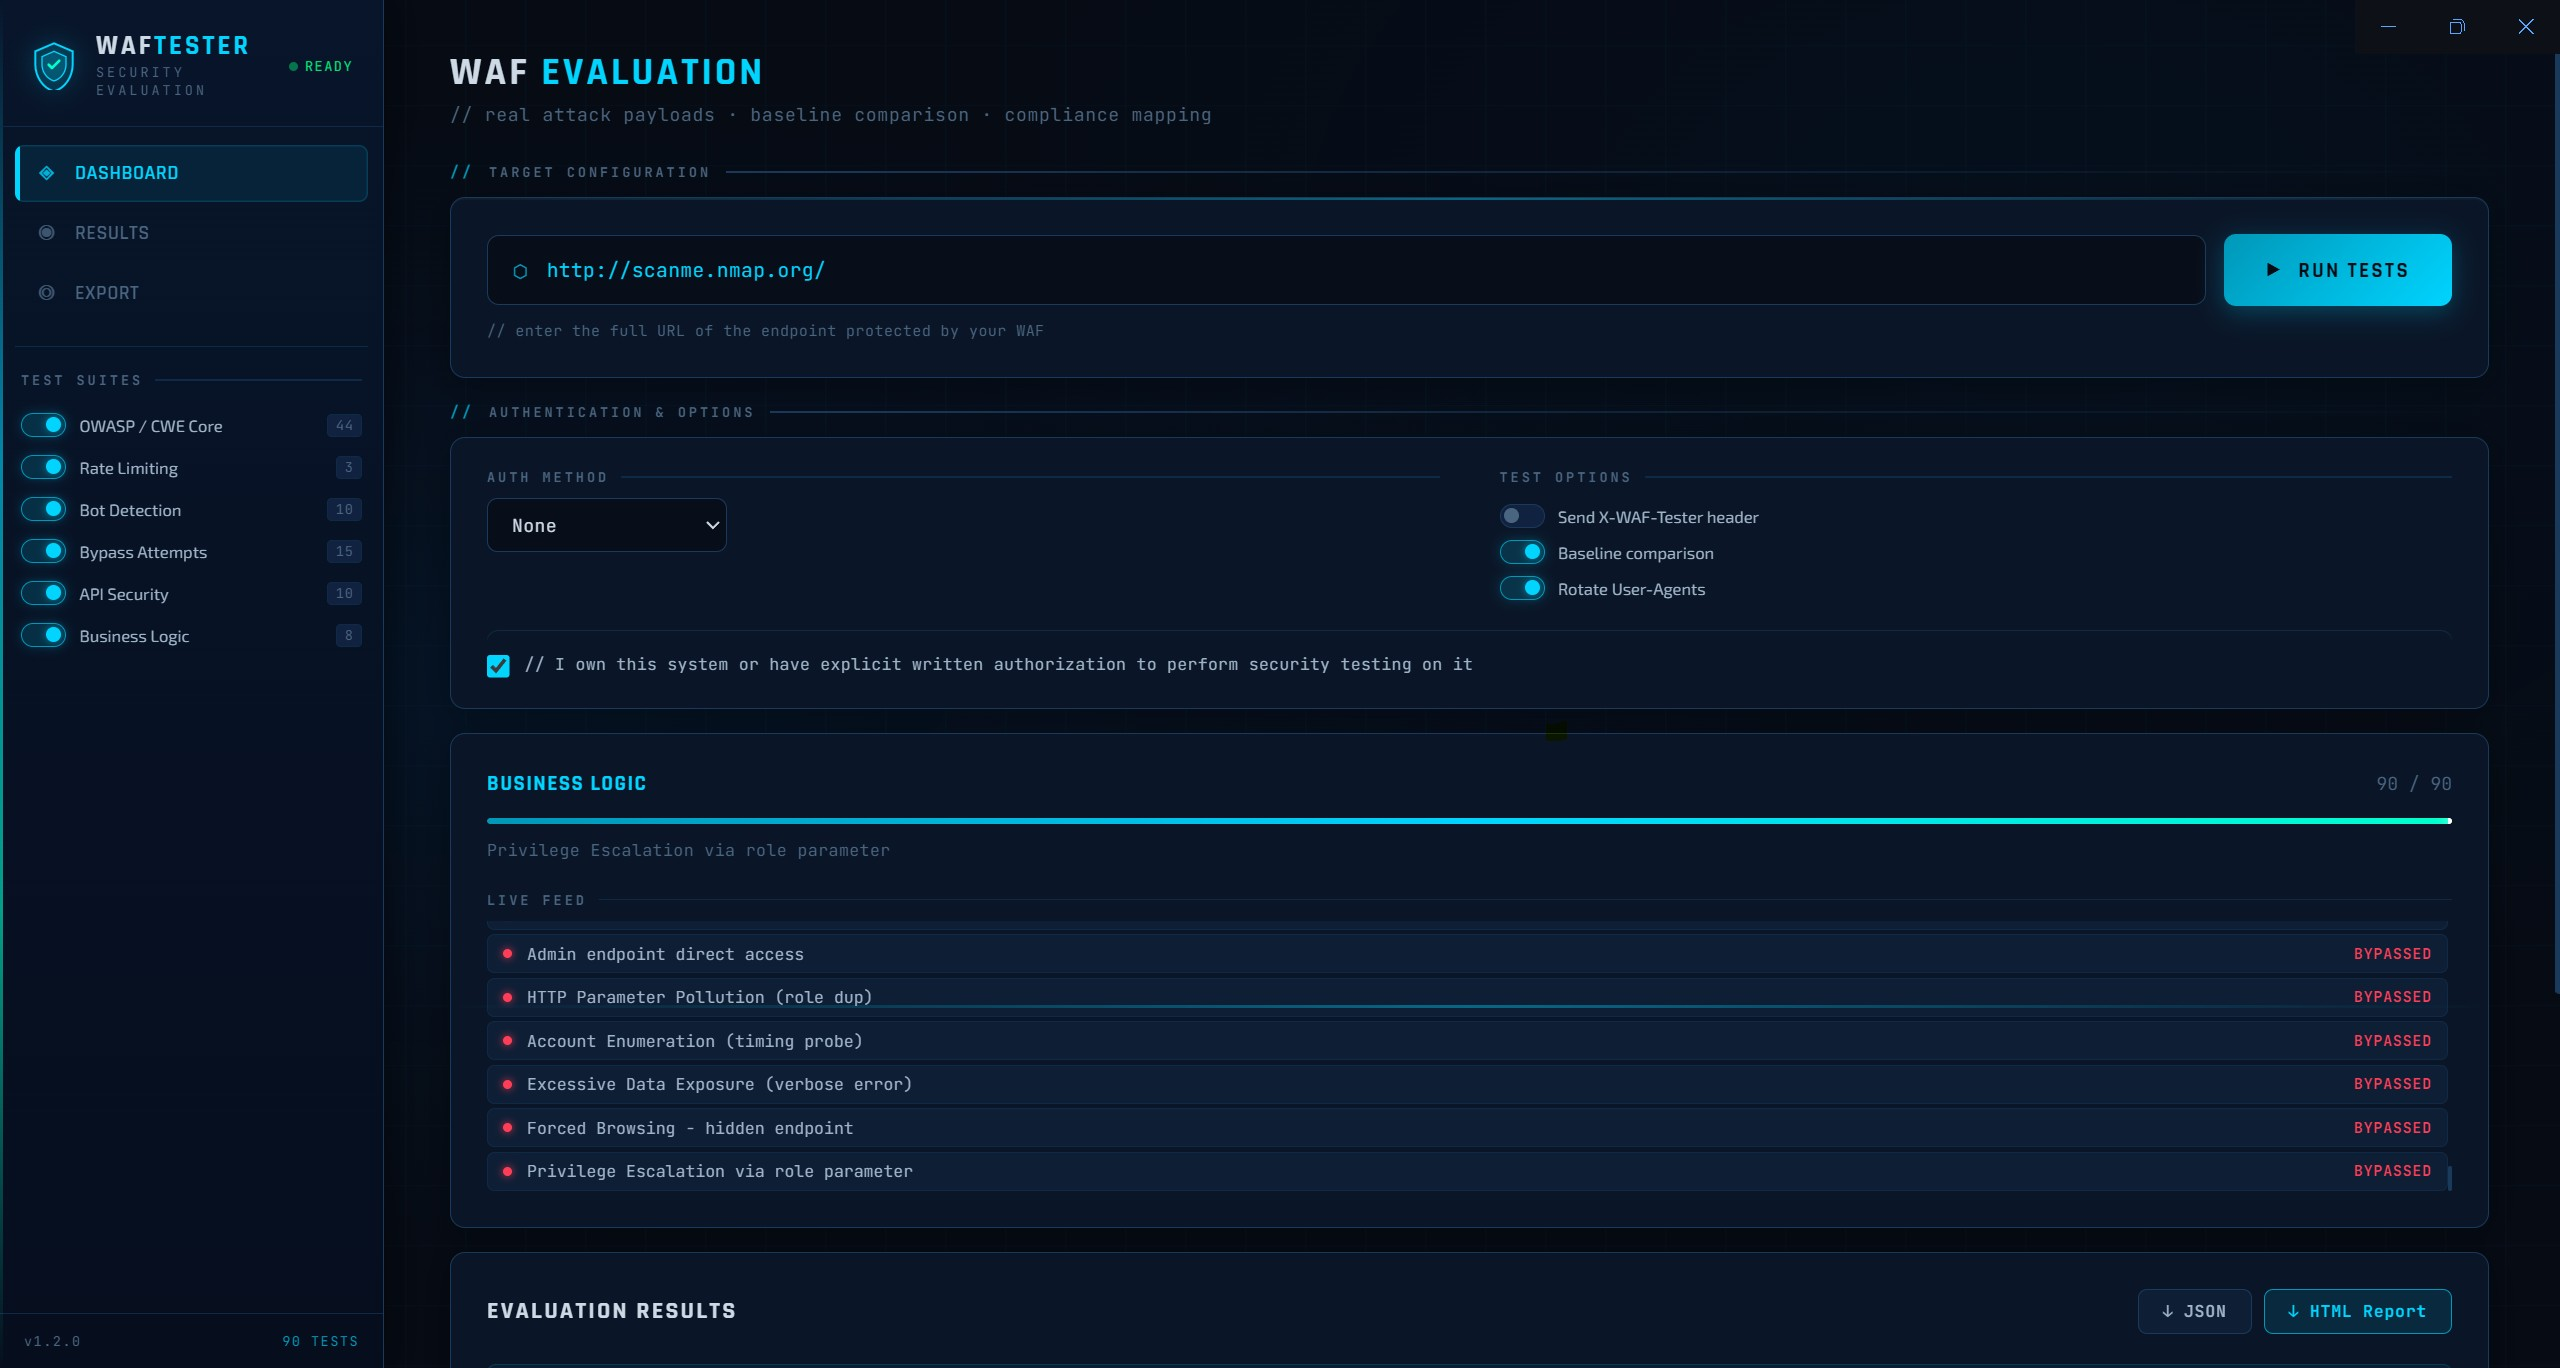 kpomin57/waf-tester
A program for testing WAF functionality
 hidden-investigations/react2shell-scanner
Precision-Based Detection of RSC/Next.js Remote Code Execution Vulnerabilities (CVE-2025-55182, CVE-2025-66478)