
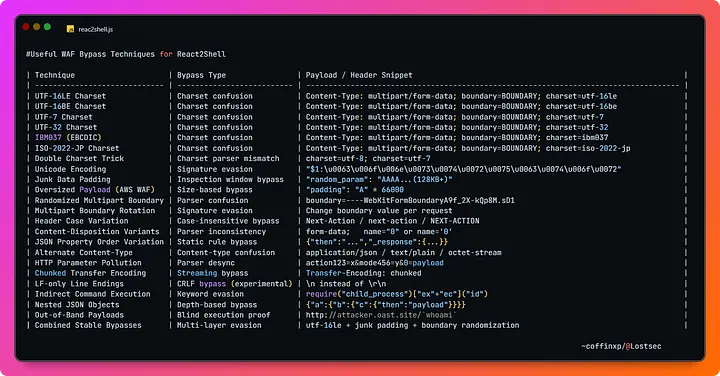
CVE-2025-55182-Waf
 l0n3m4n/cve-2025-55182-waf
CVE-2025-55182 RCE vulnerability in Next.js/React RSC servers (exploit and scanner)
command-and-controlexploitationpayload-generation+5
2
l0n3m4n/cve-2025-55182-wafCVE-2025-55182 RCE vulnerability in Next.js/React RSC servers (exploit and scanner)
 gellin/bantam
A PHP backdoor management and generation tool/C2 featuring end to end encrypted payload streaming designed to bypass WAF, IDS, SIEM systems.
 matrixleons/evilwaf
evilwaf is a penetration testing tool designed to detect and bypass common Web Application Firewalls (WAFs).
 sn1r/forbidden-buster
A tool designed to automate various techniques in order to bypass HTTP 401 and 403 response codes and gain access to unauthorized areas in the…
 mmarting/unwaf
Go tool that passively discovers the real origin IP behind a WAF/CDN using multiple OSINT sources, then verifies candidates via HTML similarity, SSL…
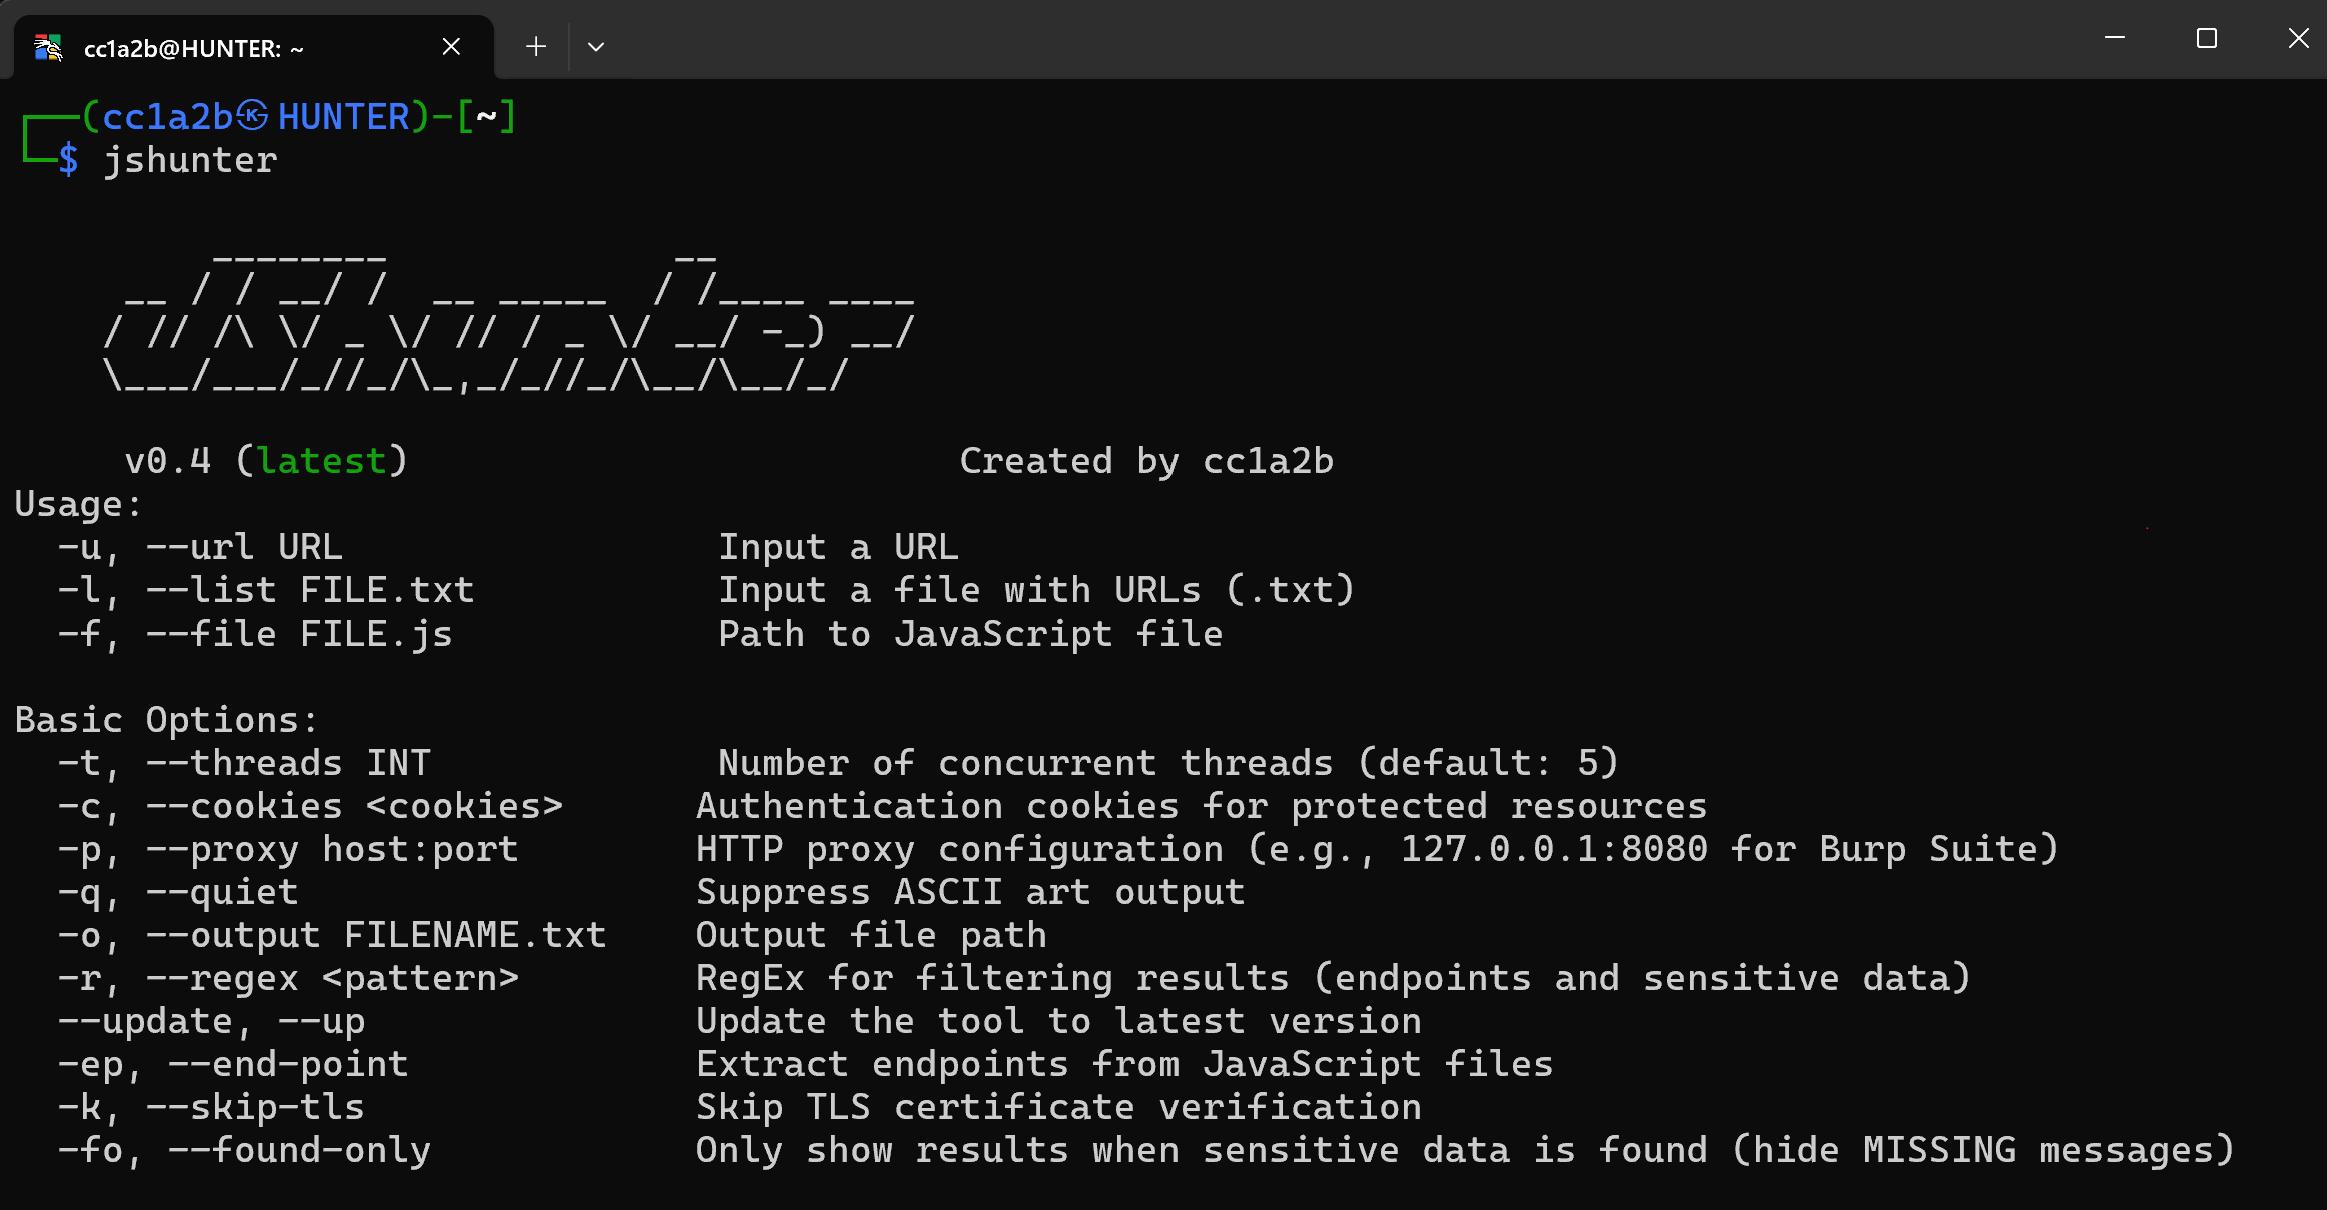 cc1a2b/jshunter
jshunter is a command-line tool designed for analyzing JavaScript files and extracting endpoints. This tool specializes in identifying sensitive…