

Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
34 results
mitmproxy preview

mitmproxy

GitHubmitmproxy/mitmproxy

An interactive TLS-capable intercepting HTTP proxy for penetration testers and software developers.

android-securityapi-securityapi-security-testing+12
45.2k
15h 22m ago
teler-waf preview

teler-waf

GitHubteler-sh/teler-waf

teler-waf is a Go HTTP middleware that protects local web services from OWASP Top 10 threats, known vulnerabilities, malicious actors, botnets,…
api-securitydefensive-toolsids-ips-evasion+5
4081 year ago
nomore403 preview

nomore403

GitHubdevploit/nomore403

🚫 Advanced tool for security researchers to bypass 403/40X restrictions through smart techniques and adaptive request manipulation. Fast. Precise.…

ids-ips-evasionpenetration-testingreconnaissance+3
1.9k3 months ago
httpx preview

httpx

GitHubprojectdiscovery/httpx

Fast, multi-probe HTTP toolkit for reconnaissance and information gathering. Probes TLS, CSP, headers, tech stack, and CDN. Supports matchers,…

api-securityapi-security-testingcrawler+18
10.4k21 days ago
coraza preview

coraza

GitHubcorazawaf/coraza

Go-based Web Application Firewall library compatible with ModSecurity SecLang rules and OWASP Core Rule Set v4, providing real-time HTTP traffic…

api-securityapi-security-testingdefensive-tools+7
3.9k13h 56m ago
SafeLine preview

SafeLine

GitHubchaitin/safeline

Self-hosted WAF and reverse proxy that filters malicious HTTP traffic, blocks SQL injection, XSS, and bot attacks, with rate limiting and dynamic…

anti-botapi-securityapi-security-testing+8
22.7k10 days ago
crowdsec preview

crowdsec

GitHubcrowdsecurity/crowdsec

Open-source IDS/IPS and WAF engine that analyzes logs and HTTP requests to detect and block malicious IPs, leveraging a crowdsourced community…

anti-botdefensive-toolsids-ips-evasion+6
15.0k5h 36m ago
ModSecurity preview

ModSecurity

GitHubowasp-modsecurity/modsecurity

ModSecurity is an open source, cross platform web application firewall (WAF) engine for Apache, IIS and Nginx. It has a robust event-based…

anti-botapi-securitydefensive-tools+7
9.8k1 day ago
wafw00f preview

wafw00f

GitHubenablesecurity/wafw00f

Automated Web Application Firewall fingerprinting tool that identifies and detects over 200 WAF products by analyzing HTTP responses to normal and…

crawlerdynamic-code-analysisinformation-gathering+6
6.6k5 months ago
http-request-smuggler preview

http-request-smuggler

GitHubportswigger/http-request-smuggler

Burp Suite extension for automated detection and exploitation of HTTP request smuggling vulnerabilities, supporting HTTP/1.1 and HTTP/2-downgrade…
dynamic-analysis-sandboxingpenetration-testingvulnerability-scanners+3
1.2k1 month ago
thermoptic preview

thermoptic

GitHubmandatoryprogrammer/thermoptic

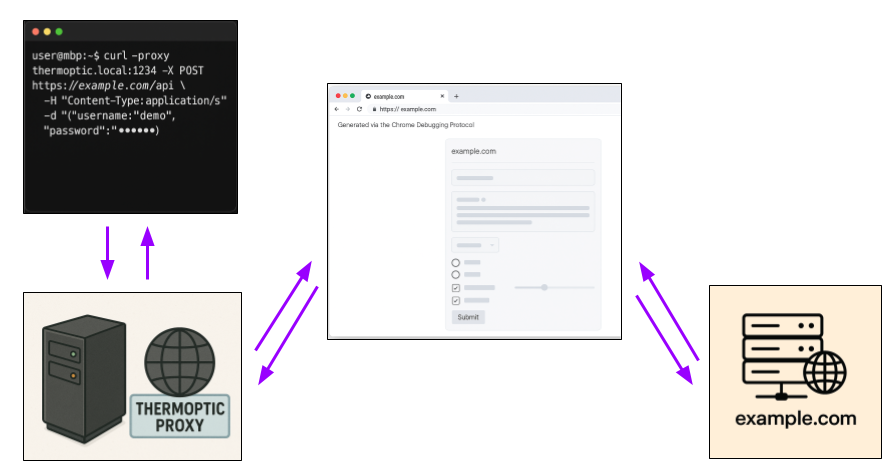
A next-generation HTTP stealth proxy which perfectly cloaks requests as the Chrome browser across all layers of the stack.
anti-botcaptcha-bypasscrawler+5
1.0k6 months ago
403bypasser preview

403bypasser

GitHubyunemse48/403bypasser

Automates HTTP 403 access control bypass techniques using header manipulation, path obfuscation, and HTTP method conversion for web application…
ids-ips-evasioninformation-gatheringpenetration-testing+2
9605 years ago
CRLFsuite preview

CRLFsuite

GitHubraghavd3v/crlfsuite

The most powerful CRLF injection (HTTP Response Splitting) scanner.
penetration-testingvulnerability-scannerswaf-bypass+2
6002 years ago
agartha preview

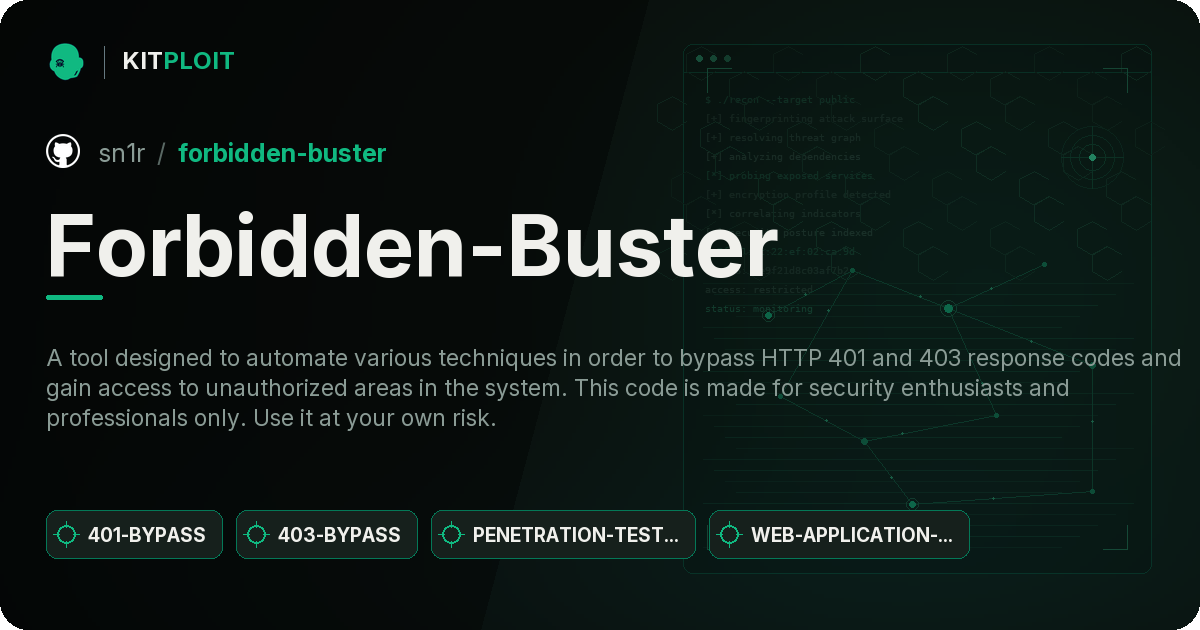
agartha

GitHubvolkandindar/agartha

A Burp Suite extension for identifying injection flaws (LFI, RCE, SQLi), authentication/authorization issues, and HTTP 403 access violations. It…
authentication-authorizationpayload-generationpenetration-testing+4
4124 months ago
Forbidden-Buster preview

Forbidden-Buster

GitHubsn1r/forbidden-buster

A tool designed to automate various techniques in order to bypass HTTP 401 and 403 response codes and gain access to unauthorized areas in the…

fuzzingids-ips-evasionpenetration-testing+2
2522 years ago
forbiddenpass preview

forbiddenpass

GitHubgotr00t0day/forbiddenpass

Multi-domain HTTP 403 bypass scanner that tests header manipulation techniques to discover hidden access paths on web servers, supporting bulk domain…
penetration-testingwaf-bypassweb-application-exploitation+1
2013 years ago
forbidden preview

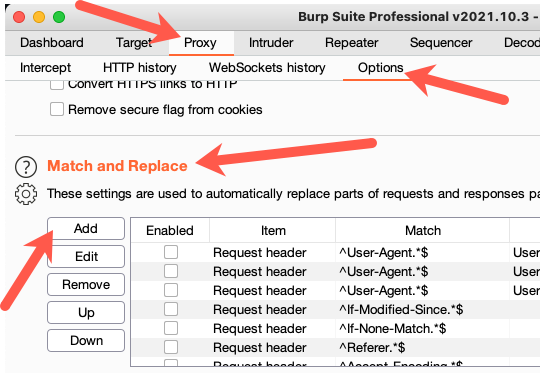
forbidden

GitHubivan-sincek/forbidden

Bypass 4xx HTTP response status codes and more. The tool is based on Python Requests, PycURL, and HTTP Client.
fuzzingids-ips-evasioninformation-gathering+5
2571 year ago
Imperva_gzip_WAF_Bypass preview

Imperva_gzip_WAF_Bypass

GitHubbishopfox/imperva_gzip_waf_bypass

Exploit for Imperva Cloud WAF bypass using gzip Content-Encoding header to evade WAF rules on HTTP POST requests. Includes detection script and…

ids-ips-evasionpenetration-testingvulnerability-analysis+2
1684 years ago
Previous12Next