

Trust-Decision-Security
 ak3zaidan/trust-decision-security
Reverse Engineer of Trust Decision Chinese Security
anti-botencryption-decryption-toolsfingerprint-spoofing+3
9
ak3zaidan/trust-decision-securityReverse Engineer of Trust Decision Chinese Security
 ammarion/waf-detector
🛡️ High-performance WAF & CDN detection tool. Identify protection layers (Cloudflare, Akamai, AWS, Fastly, and more), run effectiveness and…
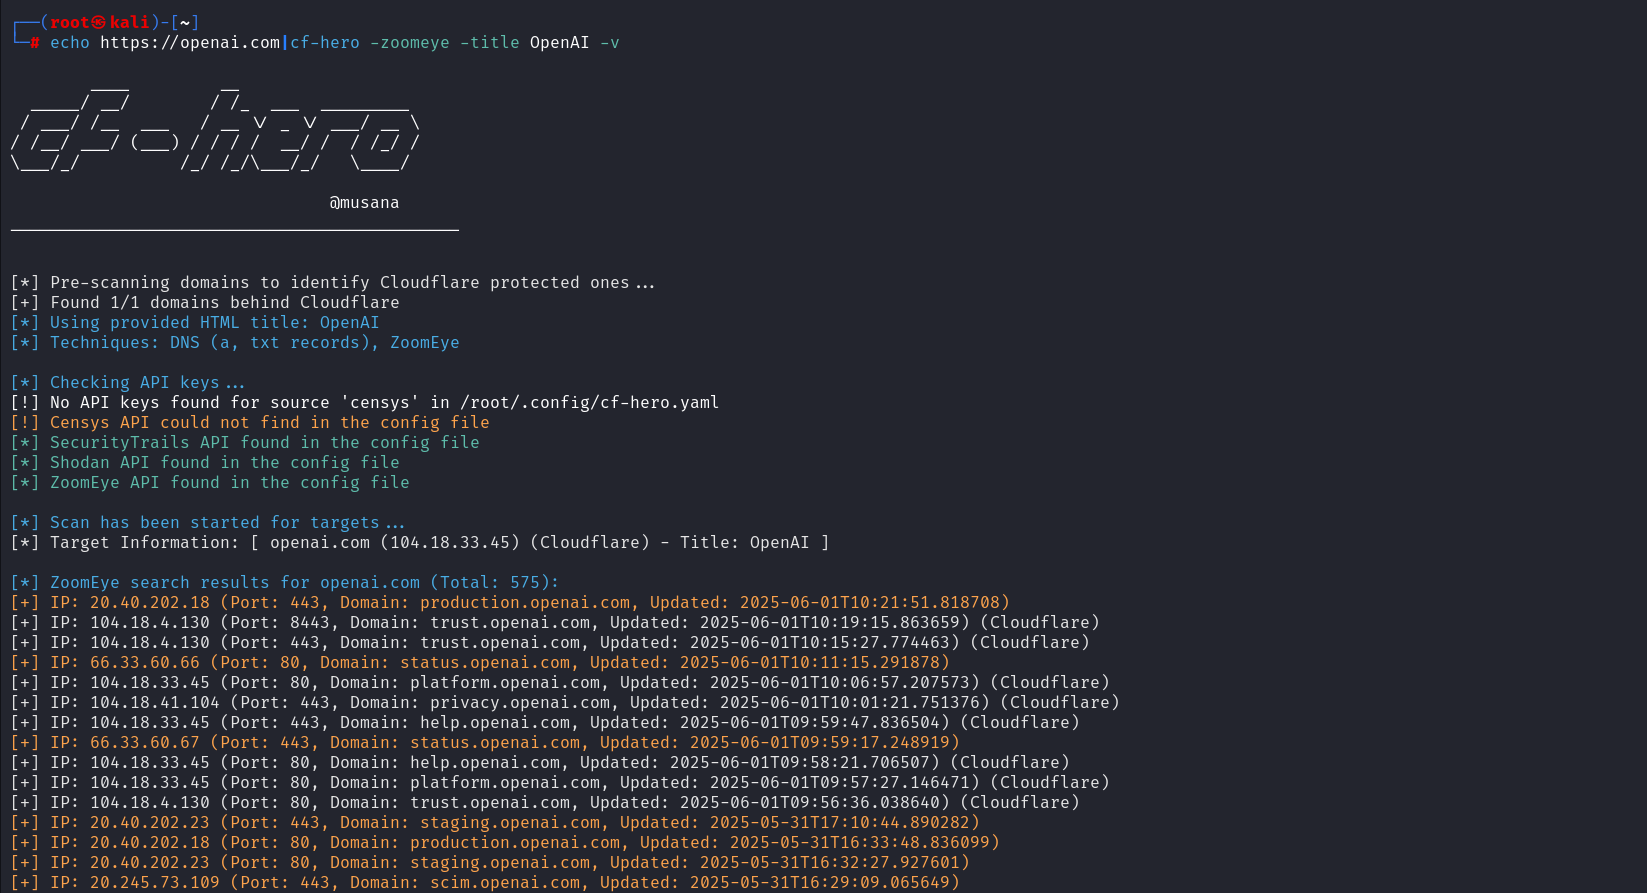 musana/cf-hero
CF-Hero is a reconnaissance tool that uses multiple data sources to discover the origin IP addresses of Cloudflare-protected web applications
 zigoo0/jsonbee
A ready to use JSONP endpoints/payloads to help bypass content security policy (CSP) of different websites.
 laluka/bypass-url-parser
Tests hundreds of URL bypass techniques against 40X protected pages using raw curl requests, with multi-mode scanning, header spoofing, and JSON/HTML…
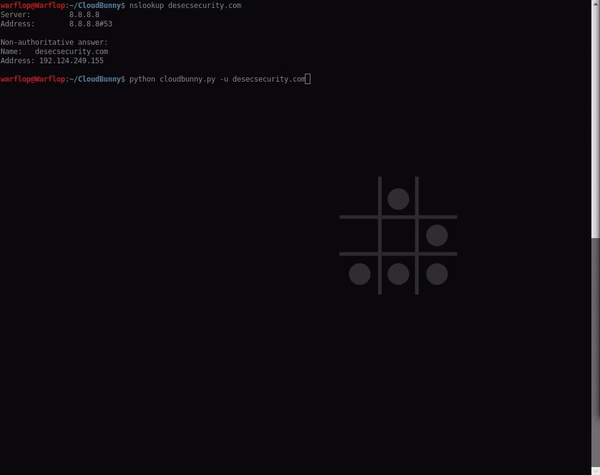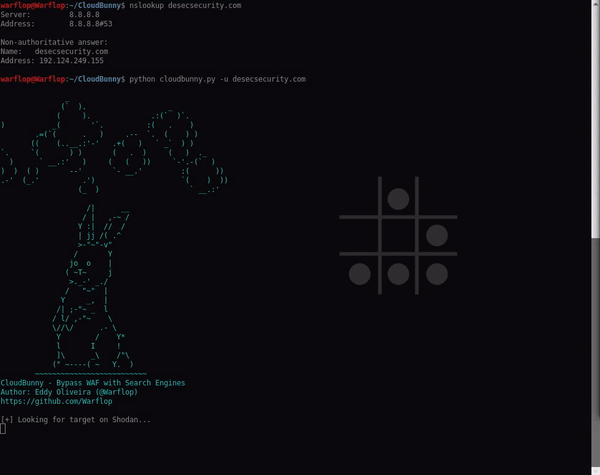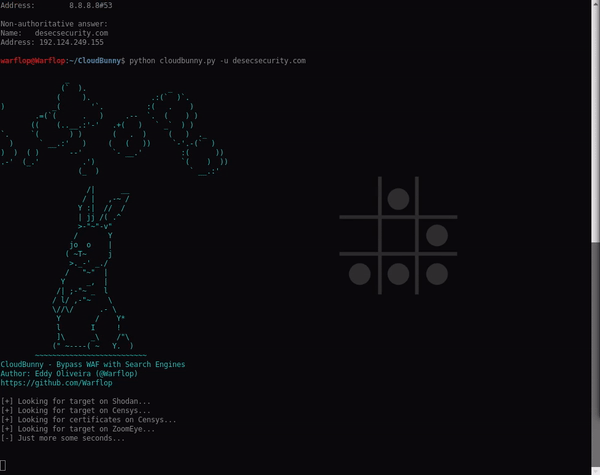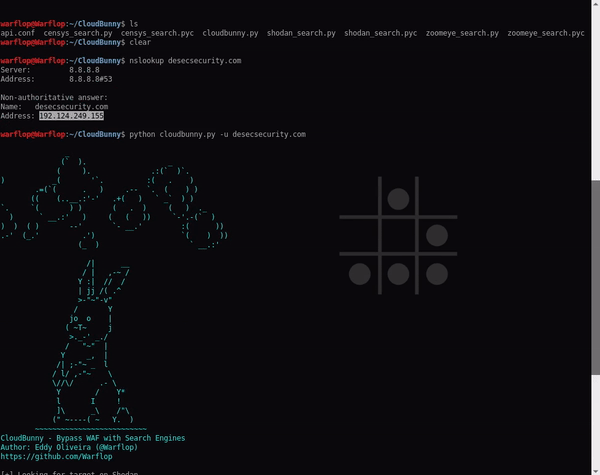 warflop/cloudbunny
CloudBunny is a tool to capture the real IP of the server that uses a WAF as a proxy or protection. In this tool we used three search engines to…
 codingo/crithit
Takes a single wordlist item and tests it one by one over a large collection of websites before moving onto the next. Create signatures to…
 secdev/scapy
Python-based interactive packet manipulation library for forging, decoding, sending, capturing, and analyzing network packets across a wide range of…
 owasp-modsecurity/modsecurity
ModSecurity is an open source, cross platform web application firewall (WAF) engine for Apache, IIS and Nginx. It has a robust event-based…
 ultrafunkamsterdam/nodriver
Successor of Undetected-Chromedriver. Providing a blazing fast framework for web automation, webscraping, bots and any other creative ideas which are…
 kaliiiiiiiiii-vinyzu/patchright
Undetected version of the Playwright testing and automation library.
 kleiton0x00/advanced-sql-injection-cheatsheet
A cheat sheet that contains advanced queries for SQL Injection of all types.
 portswigger/http-request-smuggler
Burp Suite extension for automated detection and exploitation of HTTP request smuggling vulnerabilities, supporting HTTP/1.1 and HTTP/2-downgrade…
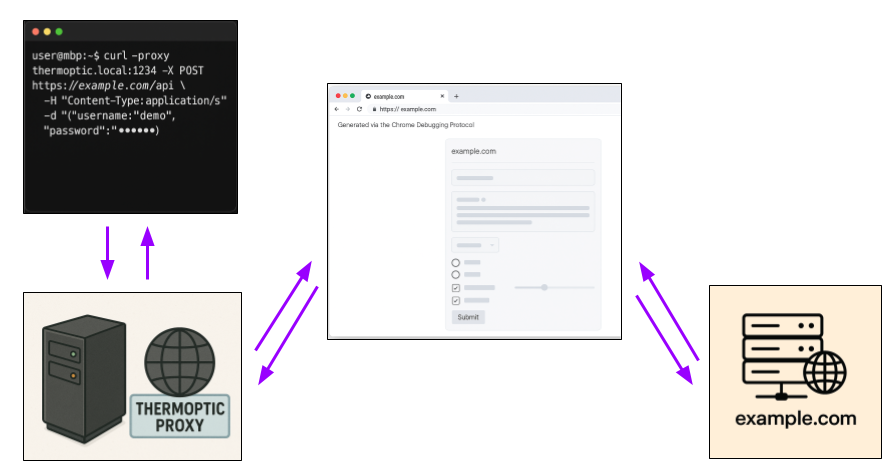 mandatoryprogrammer/thermoptic
A next-generation HTTP stealth proxy which perfectly cloaks requests as the Chrome browser across all layers of the stack.
 assetnote/nowafpls
Burp Plugin to Bypass WAFs through the insertion of Junk Data
 ejpir/cve-2025-55182-research
Technical proof-of-concept and deep-dive analysis of CVE-2025-55182, a critical RCE vulnerability in React's Flight Protocol via path traversal, fake…
 gal-nagli/shockwave-oss
Curated collection of bug bounty tips, one-liners, and automation workflows for recon, fuzzing, and web exploitation, with private nuclei templates…
 waf-bypass-maker/waf-community-bypasses
Curated CSV collection of community-sourced Web Application Firewall bypass payloads for testing and validating WAF protections.