
JSONBee
 zigoo0/jsonbee
A ready to use JSONP endpoints/payloads to help bypass content security policy (CSP) of different websites.
crawlerinformation-gatheringpenetration-testing+2
7672 years ago
zigoo0/jsonbeeA ready to use JSONP endpoints/payloads to help bypass content security policy (CSP) of different websites.
 nccgroup/burpsuitehttpsmuggler
A Burp Suite extension to help pentesters to bypass WAFs or test their effectiveness using a number of techniques
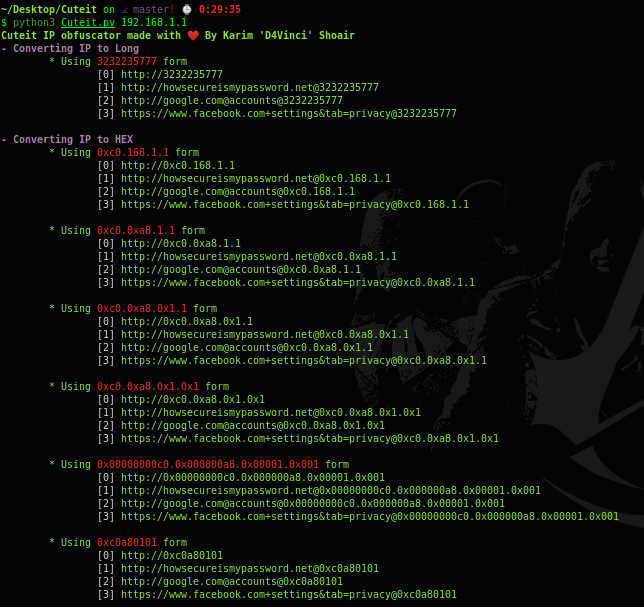 d4vinci/cuteit
IP obfuscator made to make a malicious ip a bit cuter
 mmarting/unwaf
Go tool that passively discovers the real origin IP behind a WAF/CDN using multiple OSINT sources, then verifies candidates via HTML similarity, SSL…
 coreruleset/ftw
YAML-driven framework for testing Web Application Firewall (WAF) rules using OWASP Core Rule Set baselines. Automates regression detection and…
 aiexz/cve-2025-66478-kinda-waf
Let's help websites stay safe until they are properly patched!