php-cve-2026-10961x-lab-poc

PHP CVE-2026-109618/109619 — self-contained unauthenticated RCE on stock PHP 8.5.11 (in-band PS(id)→cookie memory disclosure + UAF chain), full…

PHP CVE-2026-109618/109619 — self-contained unauthenticated RCE on stock PHP 8.5.11 (in-band PS(id)→cookie memory disclosure + UAF chain), full…

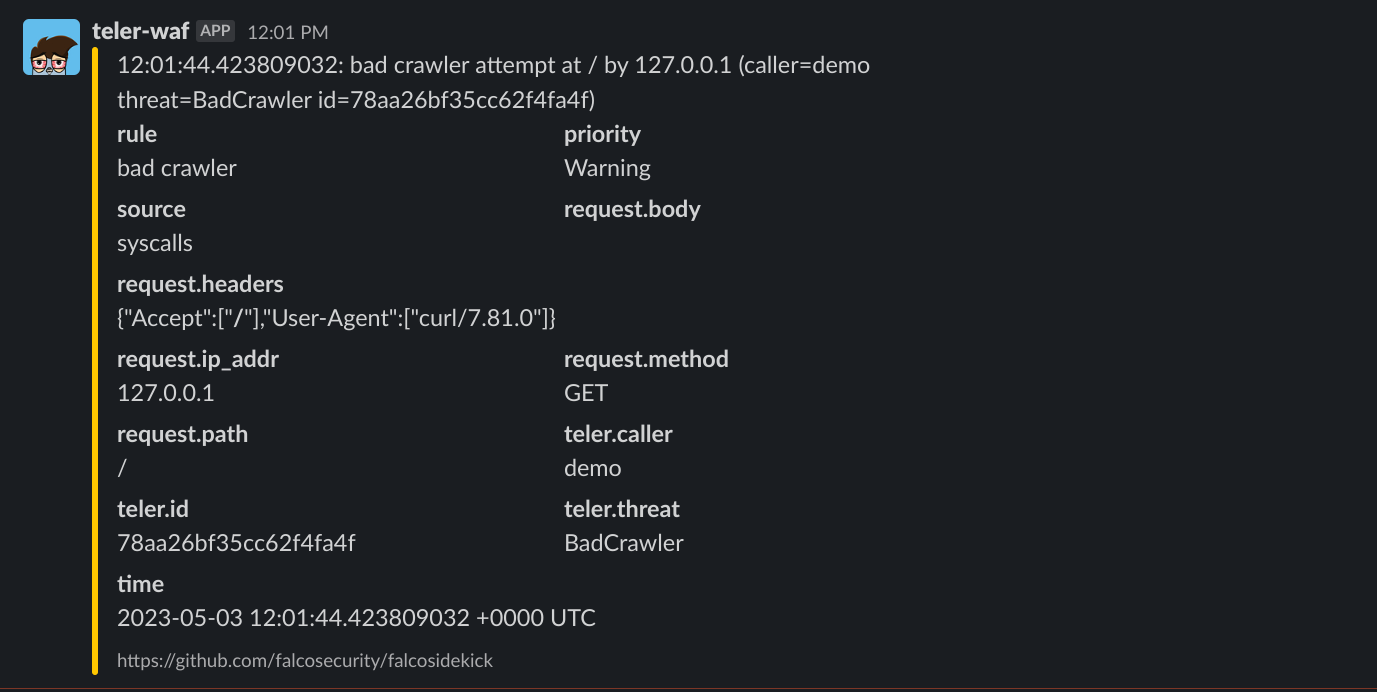
teler-waf is a Go HTTP middleware that protects local web services from OWASP Top 10 threats, known vulnerabilities, malicious actors, botnets,…

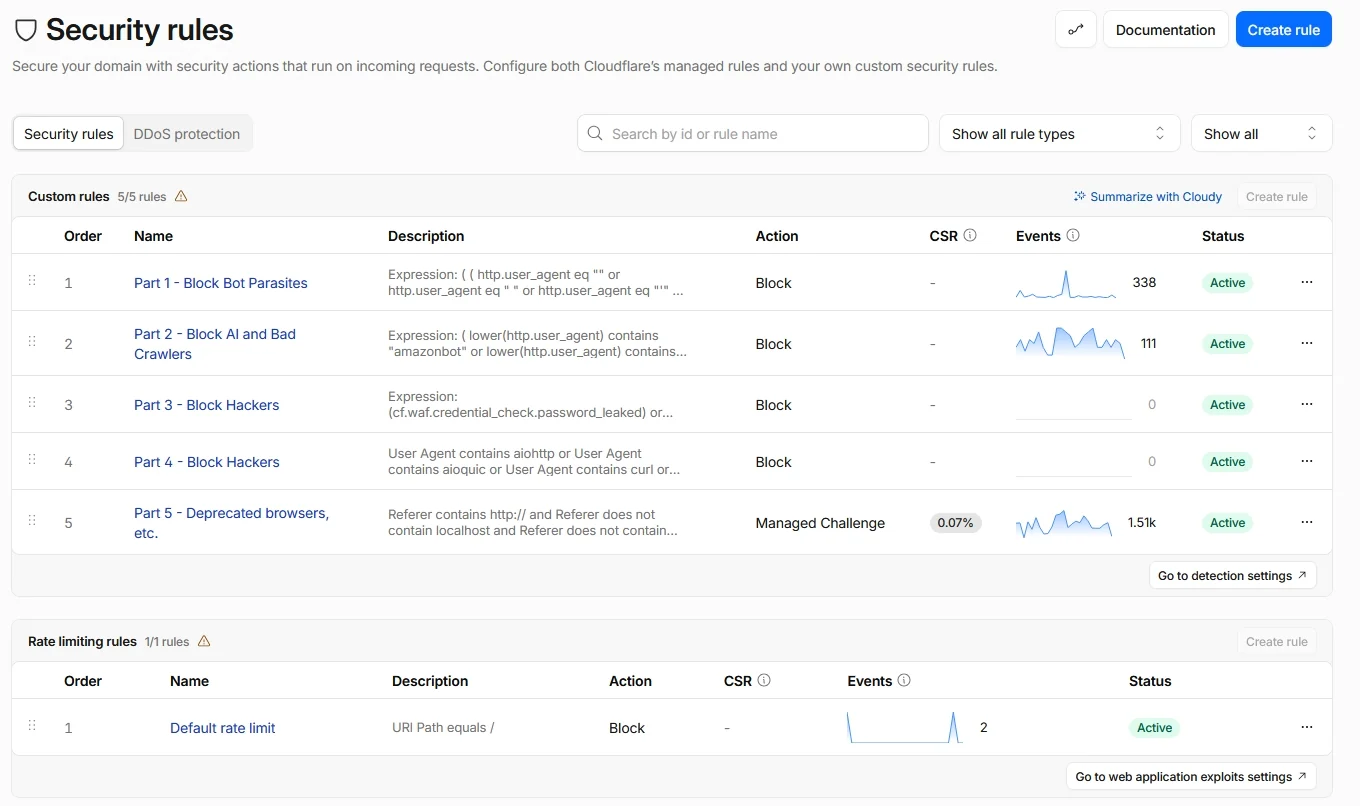
Cloudflare Free Plan security rules (Zero Trust approach) for small websites

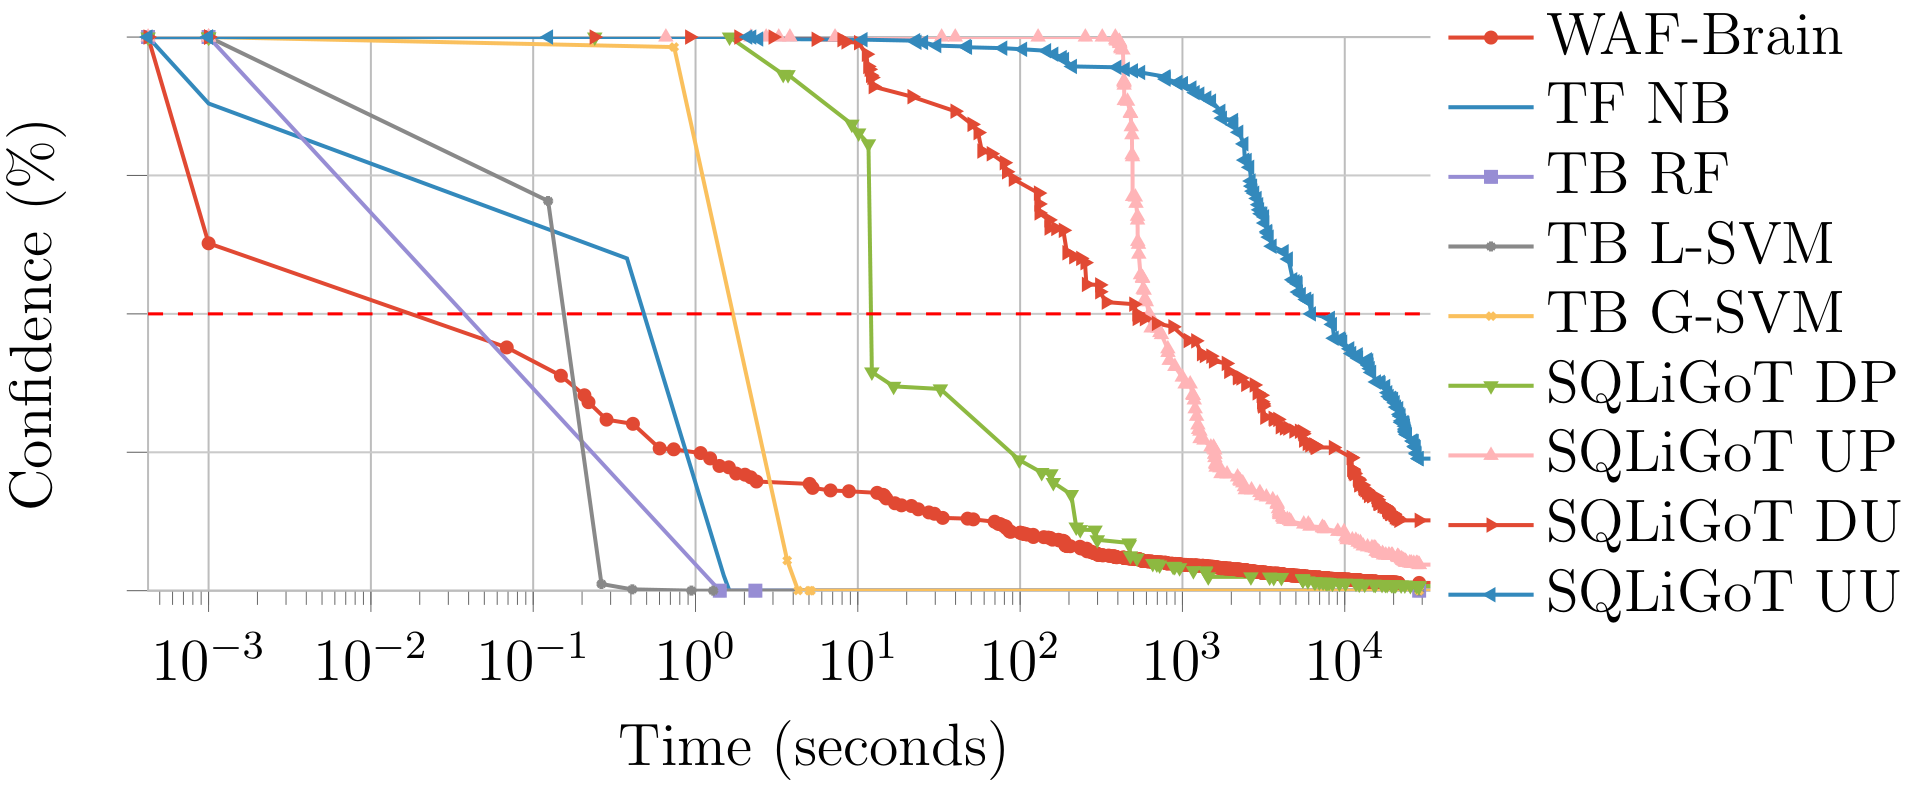
A guided mutation-based fuzzer for ML-based Web Application Firewalls

Multi-domain HTTP 403 bypass scanner that tests header manipulation techniques to discover hidden access paths on web servers, supporting bulk domain…

[漏洞复现] 全球首款利用PHP默认环境(XAMPP)的CVE-2024-4577 PHP-CGI RCE 漏洞 EXP。

Nmap NSE script for detecting Apache Log4j RCE (CVE-2021-44228) by injecting JNDI exploit payloads via HTTP headers or TCP/UDP sockets across…

Enhance your malware detection with WAF + YARA (WAFARAY)

From Dork to Download: Automating Google Dorks with Playwright

Disrupt WAF by abusing SSL/TLS Ciphers

This Log4j RCE exploit originated from https://github.com/tangxiaofeng7/CVE-2021-44228-Apache-Log4j-Rce

Log4Shell / Log4J Payload - CVE-2021-45046 and CVE-2022-42889

[漏洞复现] 全球首款基于RSC特性能绕过WAF检测的CVE-2025-55182 React Server RCE 漏洞 EXP。

Header bypass for CVE-2025-55182 (React Server Components RCE).

🛡️ Explore CVE-2025-55182, a critical RCE vulnerability in React's Flight Protocol, demonstrating exploitation techniques and mitigation strategies.

Reverse Engineer of Trust Decision Chinese Security

Cloudflare Image Resizing <= 1.5.6 | Unauthenticated Remote Code Execution