
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

··Feeds·Contact·Privacy·© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
40 results
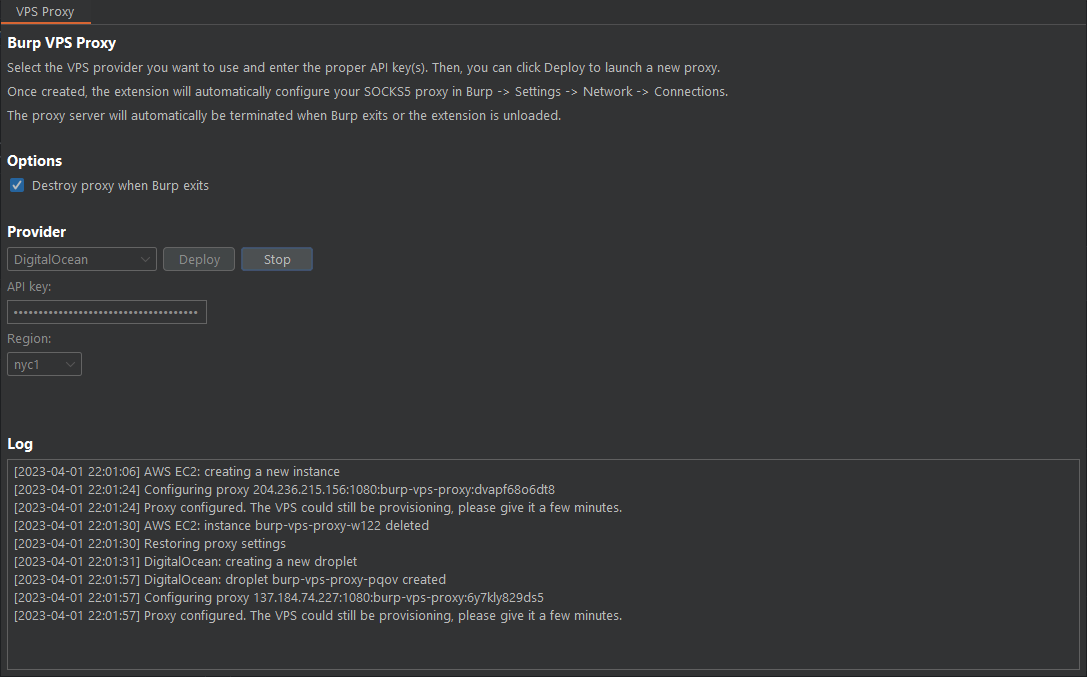
burp-vps-proxy preview

burp-vps-proxy

GitHubd3mondev/burp-vps-proxy

This Burp Suite extension allows for the automatic creation and deletion of an upstream SOCKS5 proxy on popular cloud services.
penetration-testingutilities-frameworkswaf-bypass+1
249
1 year ago
snuck preview

snuck

GitHubmauro-g/snuck

Automatic XSS filter bypass

fuzzingpenetration-testingwaf-bypass+2
9011 years ago
react2shell-scanner preview

react2shell-scanner

GitHuborwagodfather/react2shell-scanner

RSC/Next.js RCE (CVE-2025-55182 & CVE-2025-66478)

exploitationpenetration-testingwaf-bypass+3
189 months ago
coraza preview

coraza

GitHubcorazawaf/coraza

Go-based Web Application Firewall library compatible with ModSecurity SecLang rules and OWASP Core Rule Set v4, providing real-time HTTP traffic…
api-securityapi-security-testingdefensive-tools+7
3.9k4 days ago
pFuzz preview

pFuzz

GitHubredsection/pfuzz

Modular WAF bypass fuzzer with multi-threading, request manipulation, and payload encoding for red team web application testing.

fuzzingpenetration-testingred-teaming+2
1615 years ago
Awesome-WAF preview

Awesome-WAF

GitHub0xinfection/awesome-waf

Everything about Web Application Firewalls (WAFs) from Security Standpoint! 🔥

curated-resourceseducationwaf-bypass+1
7.6k1 month ago
coreruleset preview

coreruleset

GitHubcoreruleset/coreruleset

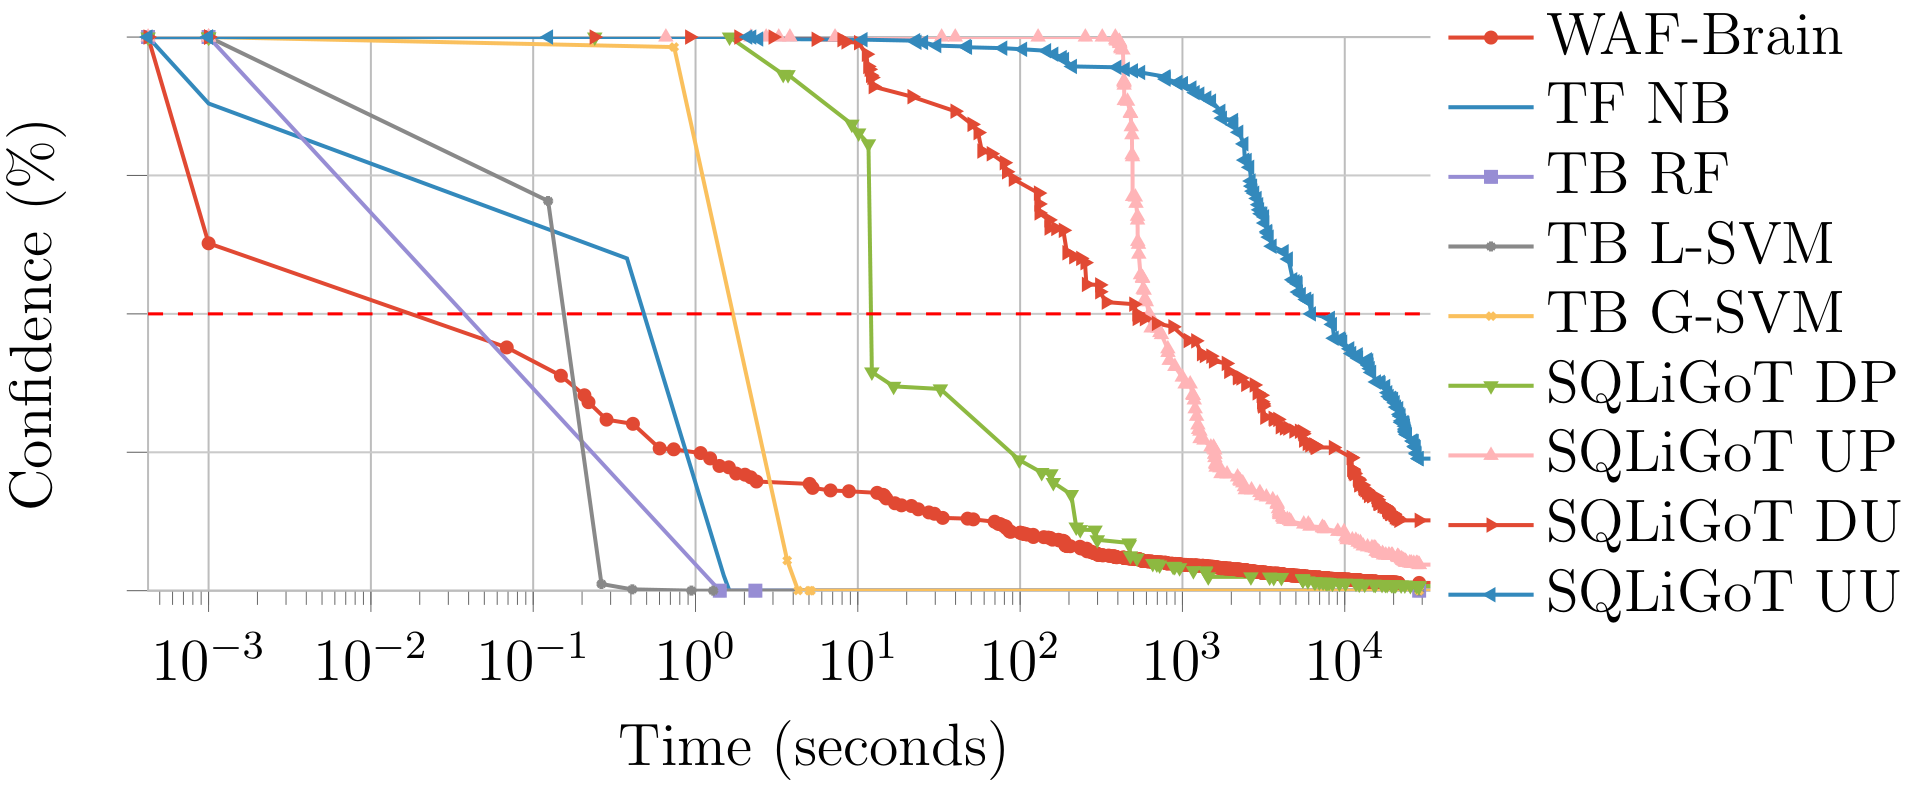
Generic attack detection rule set for web application firewalls, protecting against OWASP Top Ten and common vulnerabilities with minimal false…
anti-botids-ips-evasionmisconfiguration+4
3.3k13 hours ago
WAF-A-MoLE preview

WAF-A-MoLE

GitHubavalz/waf-a-mole

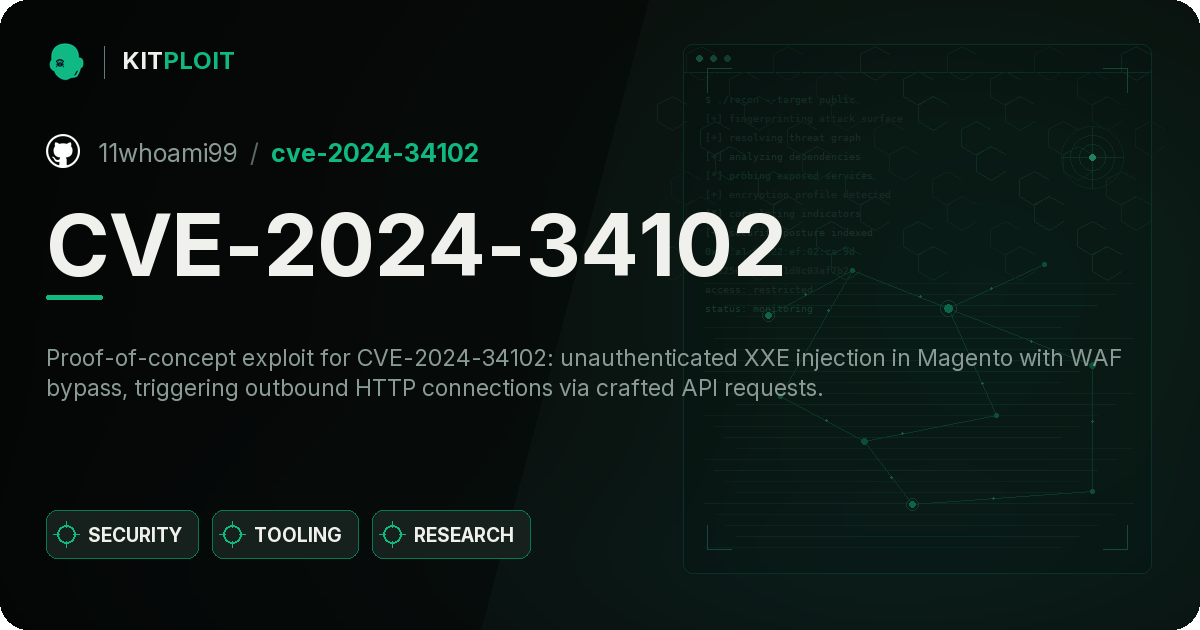
A guided mutation-based fuzzer for ML-based Web Application Firewalls
adversarial-attackfuzzingmachine-learning+2
2082 years ago
CVE-2024-34102 preview

CVE-2024-34102

GitHub11whoami99/cve-2024-34102

Proof-of-concept for CVE-2024-34102 exploiting unauthenticated Magento XXE and WAF bypass by sending a crafted request to the…
exploitationpenetration-testingvulnerability-analysis+2
32 years ago
Bypass-CVE-2025-58360 preview

Bypass-CVE-2025-58360

GitHubquyenheu/bypass-cve-2025-58360

A new way to exploit CVE-2025-58360 bypass WAF
exploitationpenetration-testingvulnerability-analysis+2
19 months ago
CVE-2026-21876 preview

CVE-2026-21876

GitHubmefhika120/cve-2026-21876

Minimal PoC and Docker container demonstrating a WAF bypass in OWASP ModSecurity CRS via multipart charset handling, leading to XSS payload delivery.

exploitationpenetration-testingvulnerability-analysis+2
8 months ago
CVE-2025-59342 preview
Archived

CVE-2025-59342

GitHubbytereaper77/cve-2025-59342

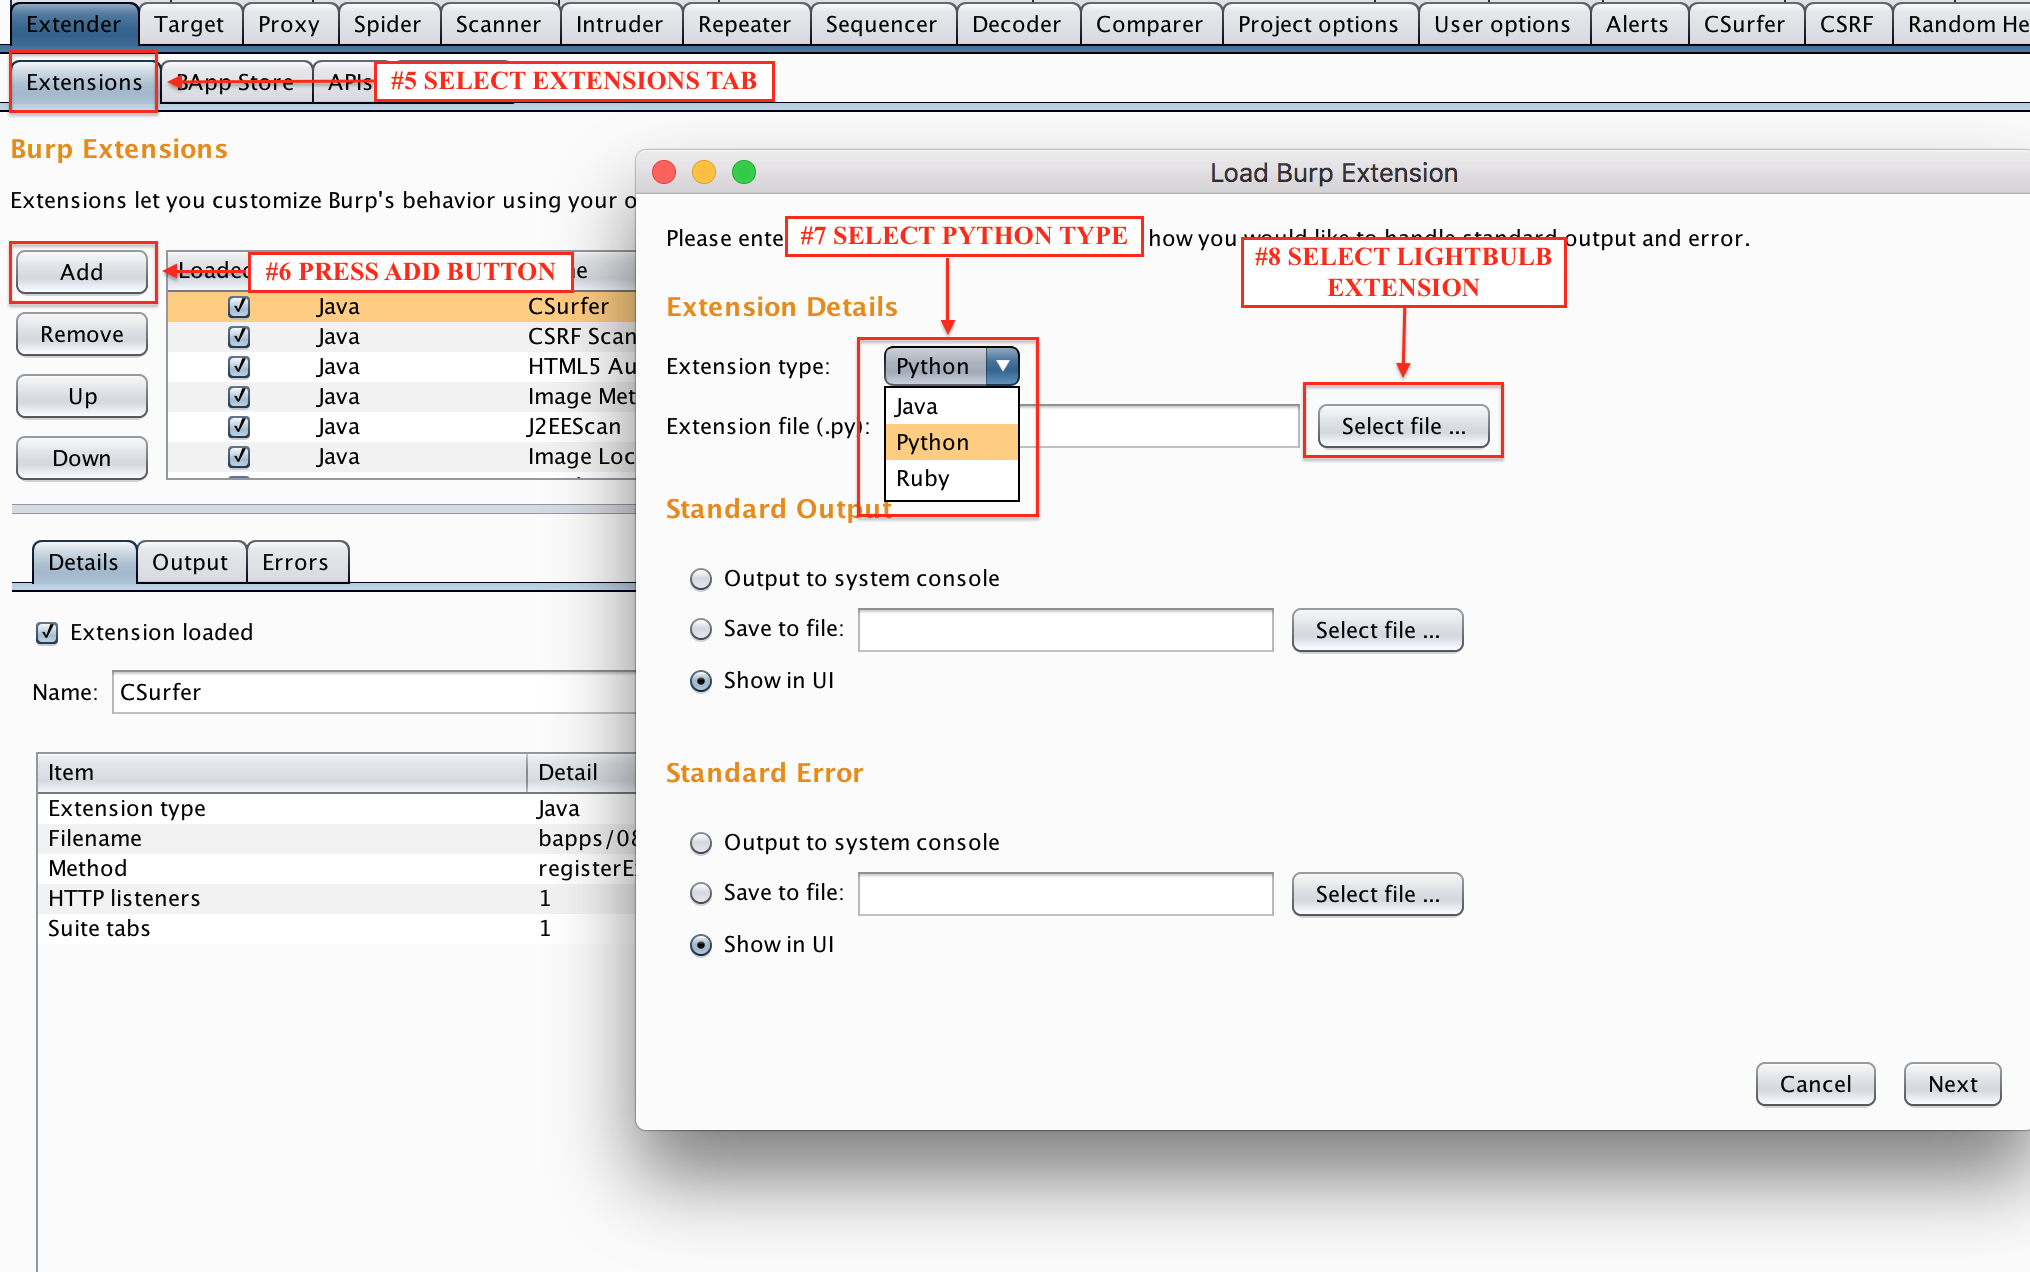
C exploit for CVE-2025-59342 path traversal in esm.sh CDN (v136 and earlier). Injects payloads via X-Zone-Id header with WAF bypass and cookie…
exploitationpenetration-testingvulnerability-analysis+2
11 year ago
lightbulb-framework preview

lightbulb-framework

GitHublightbulb-framework/lightbulb-framework

Tools for auditing WAFS

fuzzingpenetration-testingvulnerability-analysis+2
4665 years ago
watchTowr-vs-Fortiweb-AuthBypass preview

watchTowr-vs-Fortiweb-AuthBypass

GitHubwatchtowrlabs/watchtowr-vs-fortiweb-authbypass

Python-based detector for FortiWeb authentication bypass (CVE-2025-xxxxx). Sends exploit payload to create a test user as proof of exploitation.

exploitationpenetration-testingvulnerability-analysis+2
7610 months ago
CVE-2020-6519 preview

CVE-2020-6519

GitHubperimeterx/cve-2020-6519

Proof-of-concept exploit for CVE-2020-6519, a Content Security Policy bypass vulnerability in Chromium 83, enabling full CSP bypass across platforms.
exploitationpenetration-testingvulnerability-analysis+2
256 years ago
CVE-2025-55182-bypass preview

CVE-2025-55182-bypass

GitHubmomika233/cve-2025-55182-bypass

CVE-2025-55182-bypass-waf
exploitationpenetration-testingvulnerability-analysis+2
318 months ago
CVE-2025-55182-research preview

CVE-2025-55182-research

GitHubfarhan9488/cve-2025-55182-research

🛡️ Explore CVE-2025-55182, a critical RCE vulnerability in React's Flight Protocol, demonstrating exploitation techniques and mitigation strategies.
exploitationpenetration-testingvulnerability-analysis+3
4 days ago
CVE-2022-31813 preview

CVE-2022-31813

GitHubyiliufeng168/cve-2022-31813

Demonstrates CVE-2022-31813 Apache HTTP Server bypass using X-Real-IP header manipulation to evade access controls, with a Docker-based test…

exploitationpenetration-testingvulnerability-analysis+2
7 months ago
Previous123Next