

JShunter
 cc1a2b/jshunter
jshunter is a command-line tool designed for analyzing JavaScript files and extracting endpoints. This tool specializes in identifying sensitive…
api-securitydynamic-code-analysispenetration-testing+6
529
cc1a2b/jshunterjshunter is a command-line tool designed for analyzing JavaScript files and extracting endpoints. This tool specializes in identifying sensitive…
 warflop/cloudbunny
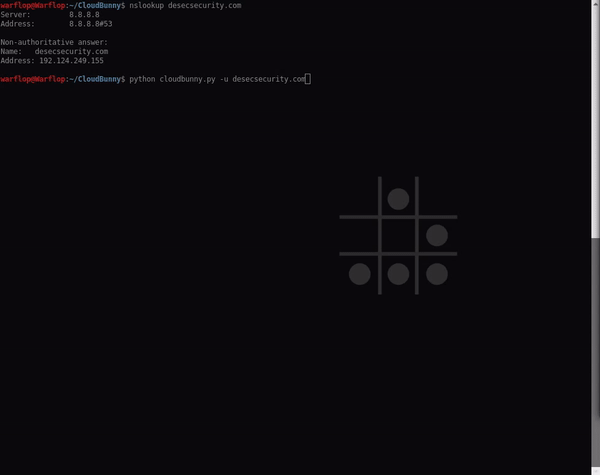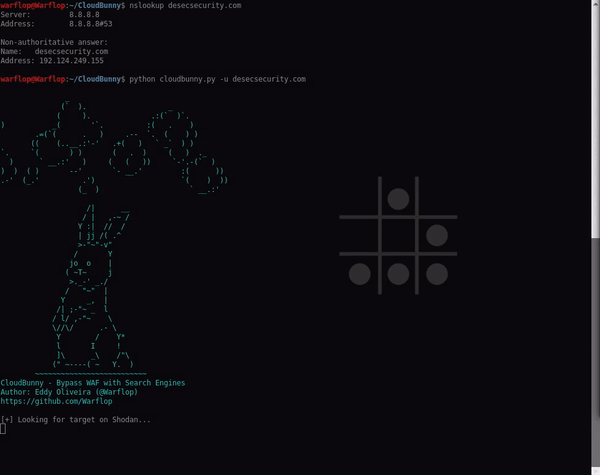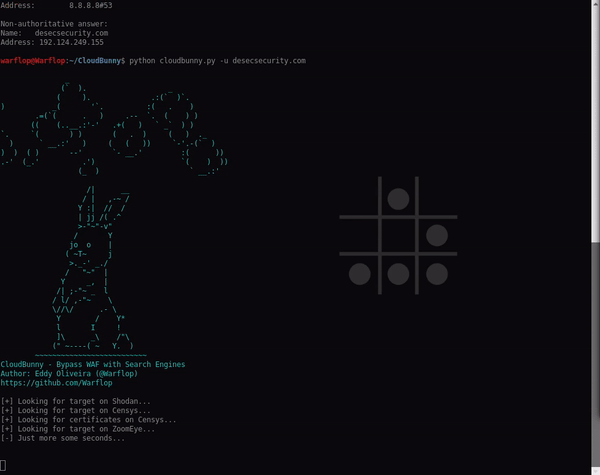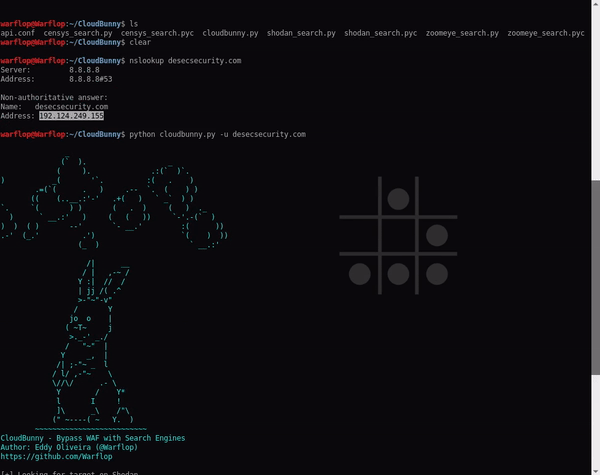
CloudBunny is a tool to capture the real IP of the server that uses a WAF as a proxy or protection. In this tool we used three search engines to…
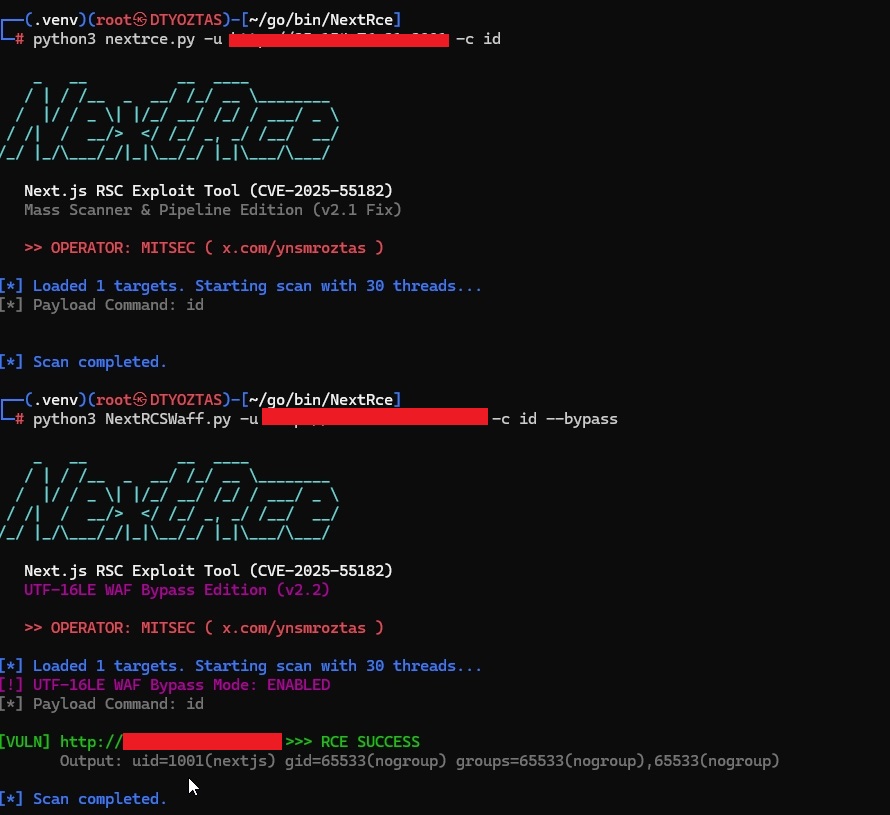 ynsmroztas/nextrce
React Shell & Next.js RSC Exploit Tool (CVE-2025-55182)
 samyk/quickjack
Quickjack is a point-and-click tool for intuitively producing advanced clickjacking and frame slicing attacks.
 mmarting/unwaf
Go tool that passively discovers the real origin IP behind a WAF/CDN using multiple OSINT sources, then verifies candidates via HTML similarity, SSL…
 ammarion/waf-detector
🛡️ High-performance WAF & CDN detection tool. Identify protection layers (Cloudflare, Akamai, AWS, Fastly, and more), run effectiveness and…
 cybertechajju/cve-2026-1357-poc
Automated exploit tool for CVE-2026-1357, an unauthenticated RCE in WPvivid Backup & Migration. Scans WordPress targets, bypasses WAF/403, uploads a…
 se1zer/nextjs_exploit_tool
Next.js RSC RCE Exploit Tool (CVE-2025-55182)
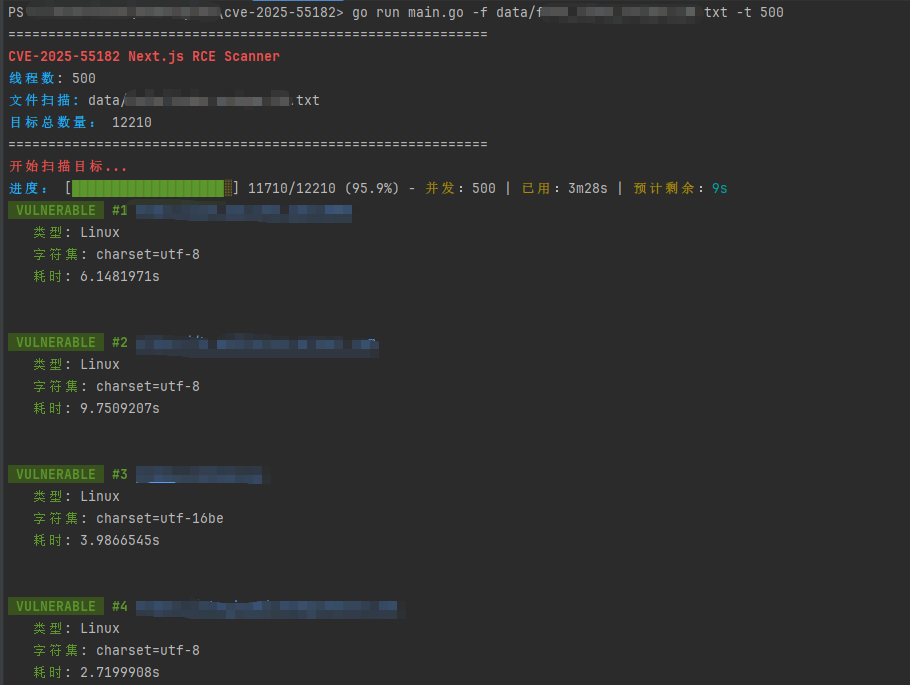 luoqichen/cve-2025-55182-poc
Go-based scanner and exploitation tool for CVE-2025-55182 (Next.js RCE). Supports batch scanning, command execution, Godzilla memory shell injection,…
 getrektboy724/meterpwrshell
Automated Tool That Generates The Perfect Meterpreter Powershell Payload
 zidansec/cloudpeler
PHP CLI tool that resolves the real origin IP behind CloudFlare-protected websites, returning hostname, organization, geolocation, and DNS data for…
 laluka/bypass-url-parser
Tests hundreds of URL bypass techniques against 40X protected pages using raw curl requests, with multi-mode scanning, header spoofing, and JSON/HTML…
 viperbluff/waf_buster
Disrupt WAF by abusing SSL/TLS Ciphers
 sumanrox/rschunter
Mass Hunting & Exploitation PoC for CVE-2025-55182 & CVE-2025-66478
 wi3memake/react2shell-scanner
Command-line security assessment framework for React and Next.js applications, analyzing React Server Components for misconfigurations, with…
 themehackers/cve-2025-55182
a critical Remote Code Execution (RCE) vulnerability in React Server Components (RSC). It also includes a realistic "Lab Environment" to safely test…
 qassam-315/cve-2026-23918-elite-auditor
Elite reconnaissance script for auditing Apache's HTTP/2 stack against memory corruption (CVE-2026-23918). Features ALPN protocol forcing and…
 g0d150ne/wp2shell
Modular WordPress pre-auth exploit framework chaining SQL injection and authentication bypass to deliver remote code execution, interactive shells,…