
JNDI-Exploit-1.2-log4shell
 34zy/jndi-exploit-1.2-log4shell
Details : CVE-2021-44228
command-and-controlexploitationpayload-generation+3
34zy/jndi-exploit-1.2-log4shellDetails : CVE-2021-44228
 h0tak88r/next88
High-performance Go implementation for detecting React Server Components RCE vulnerabilities (CVE-2025-55182 & CVE-2025-66478).
 zxz3650/cve-2025-55182-poc
CVE-2025-55182-POC
 wysiiwyg/log4j_0day_rce
Log4j-RCE (CVE-2021-44228) Proof of Concept
 scheibling/py-log4shellscanner
Scanner for the Log4j vulnerability dubbed Log4Shell (CVE-2021-44228)
 felipe8398/modsec-log4j2
Regra ModSec para proteção log4j2 - CVE-2021-44228
 nbs-system/naxsi
NAXSI is an open-source, high performance, low rules maintenance WAF for NGINX
 bytereaper77/cve-2025-41373
PoC for CVE-2025-41373 Authenticated SQL Injection in Gandia Integra Total v2.1.2217.3–4.4.2236.1
 carlos-mesquita/tpaslog4shellpoc
Proof of Concept for the Log4Shell vulnerability (CVE-2021-44228), developed as part of the coursework for the curricular unit TPAS in the Master's…
 codingo/crithit
Takes a single wordlist item and tests it one by one over a large collection of websites before moving onto the next. Create signatures to…
 yehia-mamdouh/xssya-v-2.0
Python XSS scanner that confirms reflected and encoded-payload injection, executes payloads to capture cookies, detects WAFs, and tests XST with a…
 sc4rfurry/r4venzcl4w
A Modular Framework for Pentesters and Bug Hunters written in python.
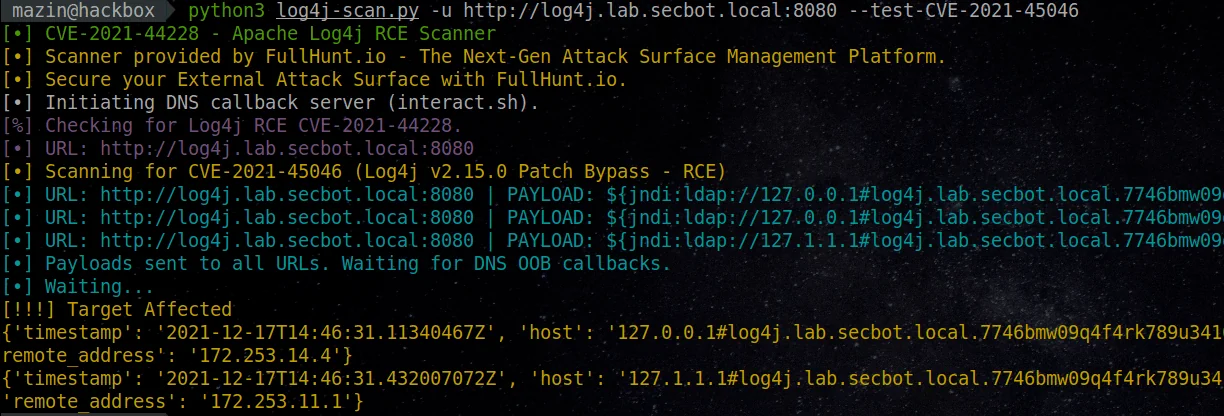 ananya-0306/log-4j-scanner
A fully automated, accurate, and extensive scanner for finding log4j RCE CVE-2021-44228
 cerberusmrxi/cve-2025-55182-advanced-react-server-components-rce-exploit
Advanced React Server Components RCE scanner for CVE-2025-55182. Features: multi-stage fingerprinting, vulnerability verification, DNS exfiltration,…
 cerberusmrxi/wp-contest-gallery-28.1.4-exploit
Complete exploitation toolkit for CVE-2026-3180 - WordPress Contest Gallery SQL Injection vulnerability. Features automated data extraction, WAF…
 iicaicai/cve-2026-5524-poc
Python mass-exploit toolkit for CVE-2026-5524, an unauthenticated file upload RCE in the WordPress Divi Form Builder plugin, with webshell upload and…
 lobuhi/byp4xx
40X/HTTP bypasser in Go. Features: Verb tampering, headers, #bugbountytips, User-Agents, extensions, default credentials...
 zigoo0/webpwn3r
WebPwn3r - Web Applications Security Scanner.