

ModSecurity
 owasp-modsecurity/modsecurity
ModSecurity is an open source, cross platform web application firewall (WAF) engine for Apache, IIS and Nginx. It has a robust event-based…
anti-botapi-securitydefensive-tools+7
9.8k
owasp-modsecurity/modsecurityModSecurity is an open source, cross platform web application firewall (WAF) engine for Apache, IIS and Nginx. It has a robust event-based…
 crowdsecurity/crowdsec
Open-source IDS/IPS and WAF engine that analyzes logs and HTTP requests to detect and block malicious IPs, leveraging a crowdsourced community…
 matrixtm/mhddos
Best DDoS Attack Script Python3, (Cyber / DDos) Attack With 60 Methods
 coreruleset/coreruleset
Generic attack detection rule set for web application firewalls, protecting against OWASP Top Ten and common vulnerabilities with minimal false…
 kaliiiiiiiiii-vinyzu/patchright
Undetected version of the Playwright testing and automation library.
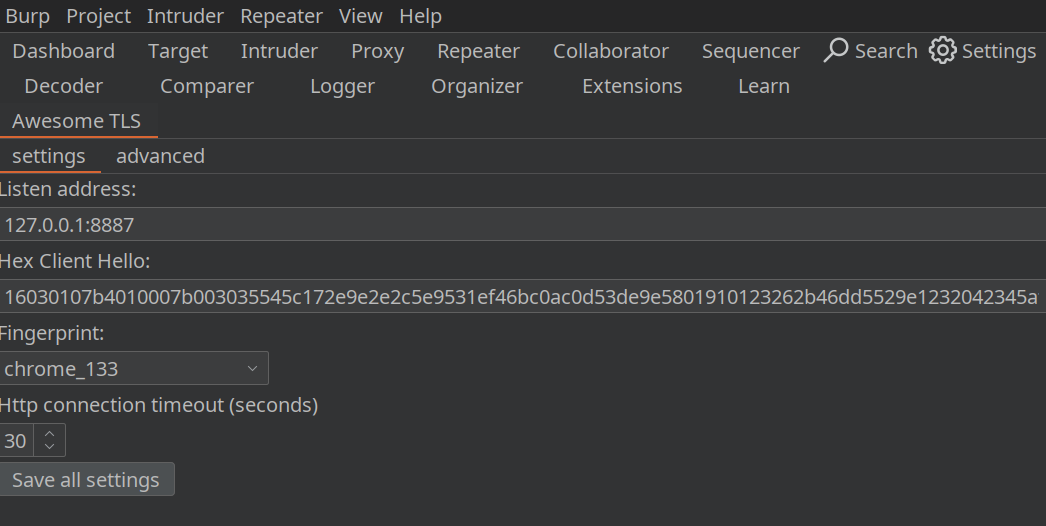 sleeyax/burp-awesome-tls
Burp extension to evade TLS fingerprinting. Bypass WAF, spoof any browser.
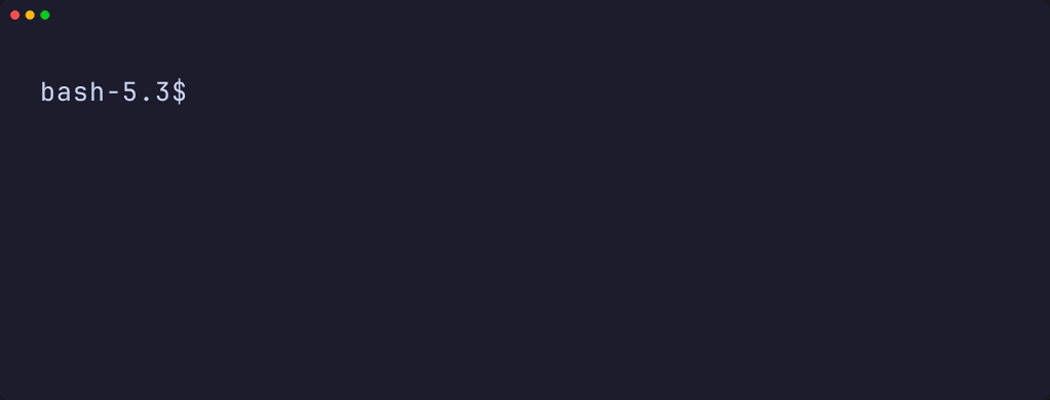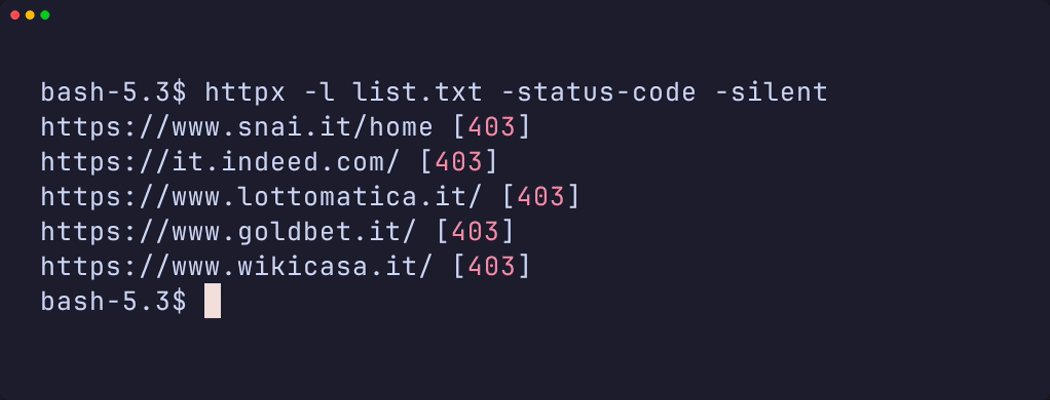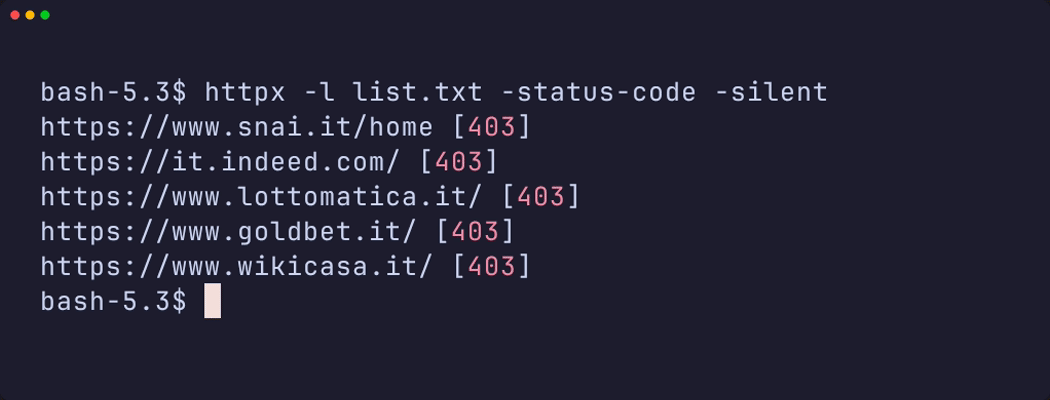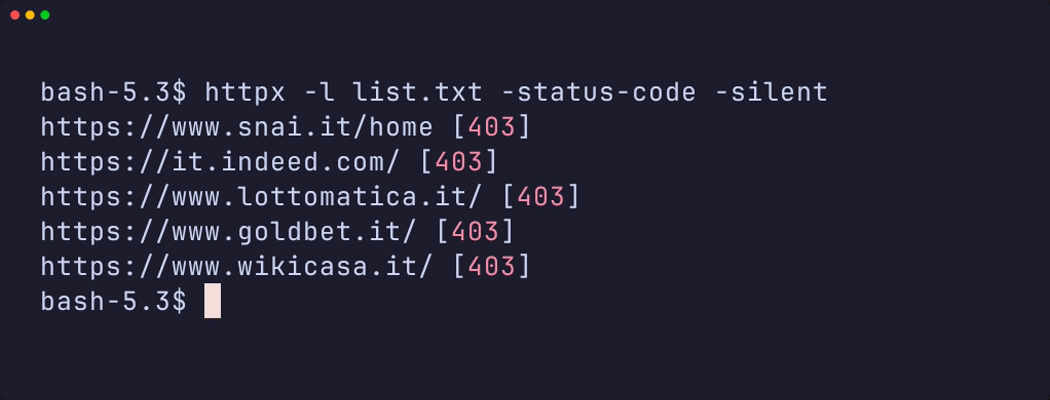 michele0303/undetected-httpx
Stop getting 403 Forbidden. A specialized httpx-like toolkit for WAF evasion.
 d00movenok/bounceback
↕️🤫 Stealth redirector for your red team operation security
 ge0rg3/requests-ip-rotator
A Python library to utilize AWS API Gateway's large IP pool as a proxy to generate pseudo-infinite IPs for web scraping and brute forcing.
 devploit/nomore403
🚫 Advanced tool for security researchers to bypass 403/40X restrictions through smart techniques and adaptive request manipulation. Fast. Precise.…
 daytriftnewgen/cve-2026-21876
Proof-of-concept exploit for CVE-2026-21876 demonstrating multipart charset bypass of OWASP CRS WAF in Flask, ASP.NET, and Spring Boot applications.
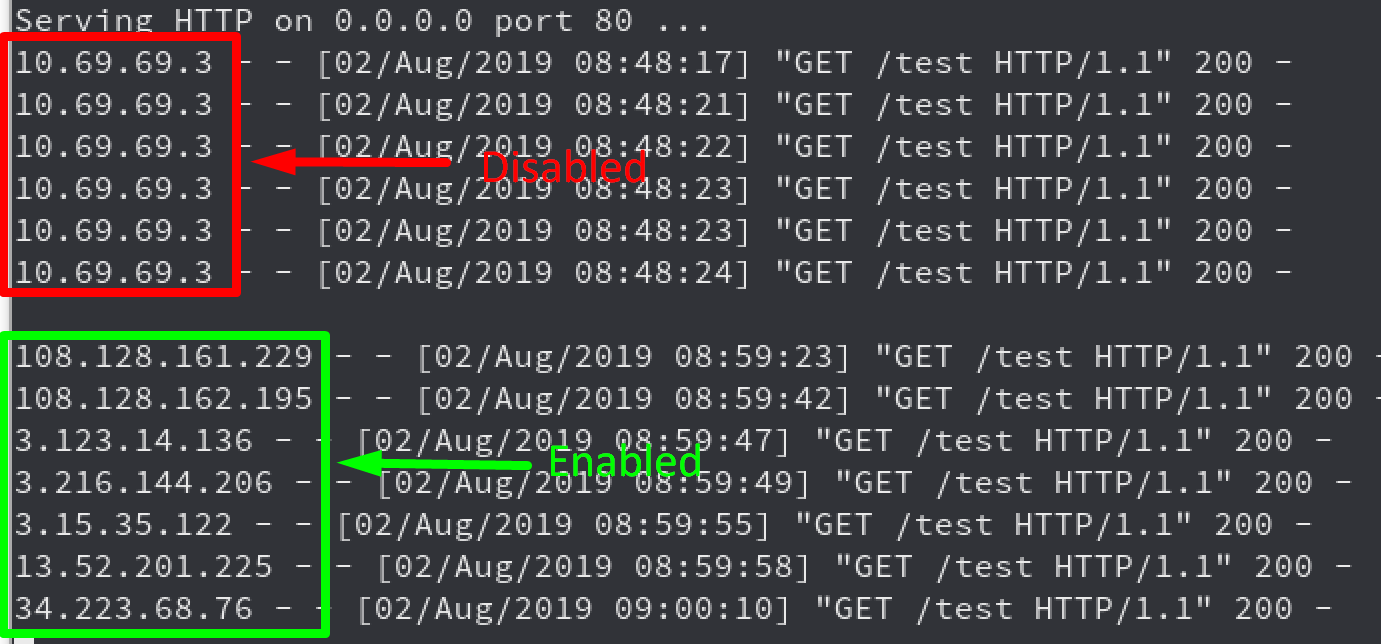 rhinosecuritylabs/iprotate_burp_extension
Extension for Burp Suite which uses AWS API Gateway to rotate your IP on every request.
 ejpir/cve-2025-55182-bypass
Header bypass for CVE-2025-55182 (React Server Components RCE).
 zxz3650/cve-2025-55182-poc
CVE-2025-55182-POC
 aiexz/cve-2025-66478-kinda-waf
Let's help websites stay safe until they are properly patched!
 nxploited/cve-2025-10041
Flex QR Code Generator <= 1.2.5 - Unauthenticated Arbitrary File Upload
 ivan-sincek/forbidden
Bypass 4xx HTTP response status codes and more. The tool is based on Python Requests, PycURL, and HTTP Client.
 realgam3/pymultitor
PyMultitor - Python Multi Threaded Tor Proxy