

Skip to content
KitploitKITPLOIT
ToolsBlog
Log in
Submit
ToolsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems Security
General Purpose Utilities
Indicator of Compromise (IOC) Management
OSINT (Open Source Intelligence)
Packet Sniffing & Analysis
Password Cracking
Penetration Testing Frameworks
Phishing Tools
Privilege Escalation
Reconnaissance
Static Analysis
Vulnerability Scanners
Web Vulnerability Scanners
Wi-Fi Auditing
Bluetooth Security
Container Security
Dynamic Analysis (Sandboxing)
Encryption/Decryption Tools
Exploit Frameworks
Identity Management
iOS Security
IoT Security
Memory Forensics
Network Mapping
OSINT for Social Engineering
Password Attacks
Payload Generation
Persistence Mechanisms
Port Scanning
Static Code Analysis (SAST)
Threat Feeds & Aggregators
Vulnerability Analysis
Web Proxies & Interception
Code Analysis
DNS & Subdomain Enumeration
Dynamic Code Analysis (DAST)
Exploitation
Hash Analysis
IDS/IPS Evasion
Impersonation Tools
Lateral Movement
Mobile App Pentesting
Network Forensics
Reverse Engineering
RFID/NFC Tools
SCADA/ICS Security
Scripting & Automation
Serverless Security
Shellcode
Web Application Exploitation
API Security Testing
Configuration Auditing
Data Exfiltration
Debuggers
Forensics
Information Gathering
Mobile Forensics
Network Access Control
Post-Exploitation
Security Virtualization
Phishing
WAF Bypass
Web Security
Fuzzing
Network Security
Steganography
Wireless Security
Data Recovery
Malware Analysis
Digital Forensics
Hardware Hacking
Cryptography
CTF
Penetration Testing
Cloud Security
DevSecOps
Mobile Security
Privacy
Command and Control
Social Engineering
Hardware Security
Utilities & Frameworks
Hardware & IoT Security
Secret Detection
Binary Analysis
Threat Intelligence
Identity & Access Management (IAM)
Supply Chain Security
Authentication
Machine Learning
Intrusion Detection
Papers & Research
Misconfiguration
Subdomain Enumeration
Email Harvesting
Learning & Education
AI-Assisted Reversing
DNS Fuzzing
Red Teaming
Incident Response
Crawler
Curated Resources
Remote Access Tool
Shellcode Generation
Payload Development
Remote Access Trojan
API Security
Anti-Bot
Fingerprint Spoofing
CAPTCHA Bypass
Email Security
DNS Analysis
Chaos Engineering
Learning Paths & Courses
Container Escape
AI Security
Database Security
Firmware Analysis
Anomaly Detection
Log Analysis
Adversarial Attack
Binary Exploitation
Labs & Practice
NewestRelevanceMost popularRecently updated
34 results
coraza preview

coraza

GitHubcorazawaf/coraza

Go-based Web Application Firewall library compatible with ModSecurity SecLang rules and OWASP Core Rule Set v4, providing real-time HTTP traffic…

api-securityapi-security-testingdefensive-tools+7
3.9k9h 21m ago
httpx preview

httpx

GitHubprojectdiscovery/httpx

Fast, multi-probe HTTP toolkit for reconnaissance and information gathering. Probes TLS, CSP, headers, tech stack, and CDN. Supports matchers,…
api-securityapi-security-testingcrawler+18
10.5k15h 46m ago
crowdsec preview

crowdsec

GitHubcrowdsecurity/crowdsec

Open-source IDS/IPS and WAF engine that analyzes logs and HTTP requests to detect and block malicious IPs, leveraging a crowdsourced community…

anti-botdefensive-toolsids-ips-evasion+6
15.1k1 day ago
mitmproxy preview

mitmproxy

GitHubmitmproxy/mitmproxy

An interactive TLS-capable intercepting HTTP proxy for penetration testers and software developers.
android-securityapi-securityapi-security-testing+12
45.3k3 days ago
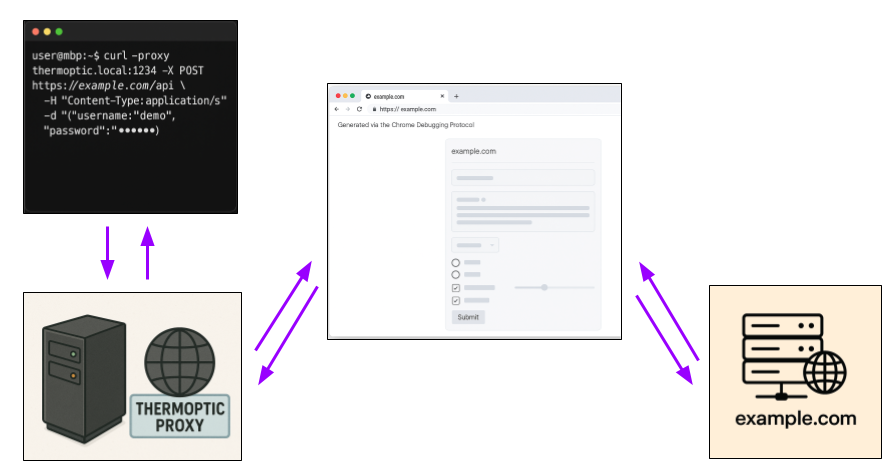
thermoptic preview

thermoptic

GitHubmandatoryprogrammer/thermoptic

A next-generation HTTP stealth proxy which perfectly cloaks requests as the Chrome browser across all layers of the stack.
anti-botcaptcha-bypasscrawler+5
1.0k3 days ago
ModSecurity preview

ModSecurity

GitHubowasp-modsecurity/modsecurity

ModSecurity is an open source, cross platform web application firewall (WAF) engine for Apache, IIS and Nginx. It has a robust event-based…

anti-botapi-securitydefensive-tools+7
9.8k5 days ago
burp-awesome-tls preview

burp-awesome-tls

GitHubsleeyax/burp-awesome-tls

Burp extension to evade TLS fingerprinting. Bypass WAF, spoof any browser.

anti-botfingerprint-spoofingids-ips-evasion+3
1.9k14 days ago
SafeLine preview

SafeLine

GitHubchaitin/safeline

Self-hosted WAF and reverse proxy that filters malicious HTTP traffic, blocks SQL injection, XSS, and bot attacks, with rate limiting and dynamic…
anti-botapi-securityapi-security-testing+8
22.7k16 days ago
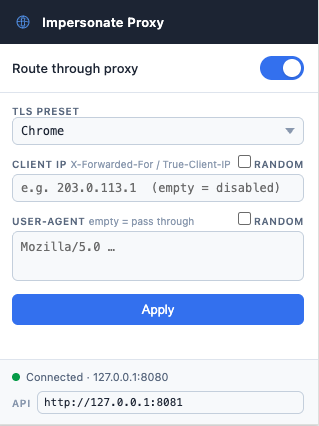
impersonate-proxy preview

impersonate-proxy

GitHubytkoka/impersonate-proxy

A local MITM proxy that lets you control TLS fingerprints (JA3/JA4), HTTP/2 fingerprints, HTTP header order, and User-Agent — all from a single YAML…
fingerprint-spoofingimpersonation-toolspenetration-testing+3
4019 days ago
http-request-smuggler preview

http-request-smuggler

GitHubportswigger/http-request-smuggler

Burp Suite extension for automated detection and exploitation of HTTP request smuggling vulnerabilities, supporting HTTP/1.1 and HTTP/2-downgrade…
dynamic-analysis-sandboxingpenetration-testingvulnerability-scanners+3
1.2k1 month ago
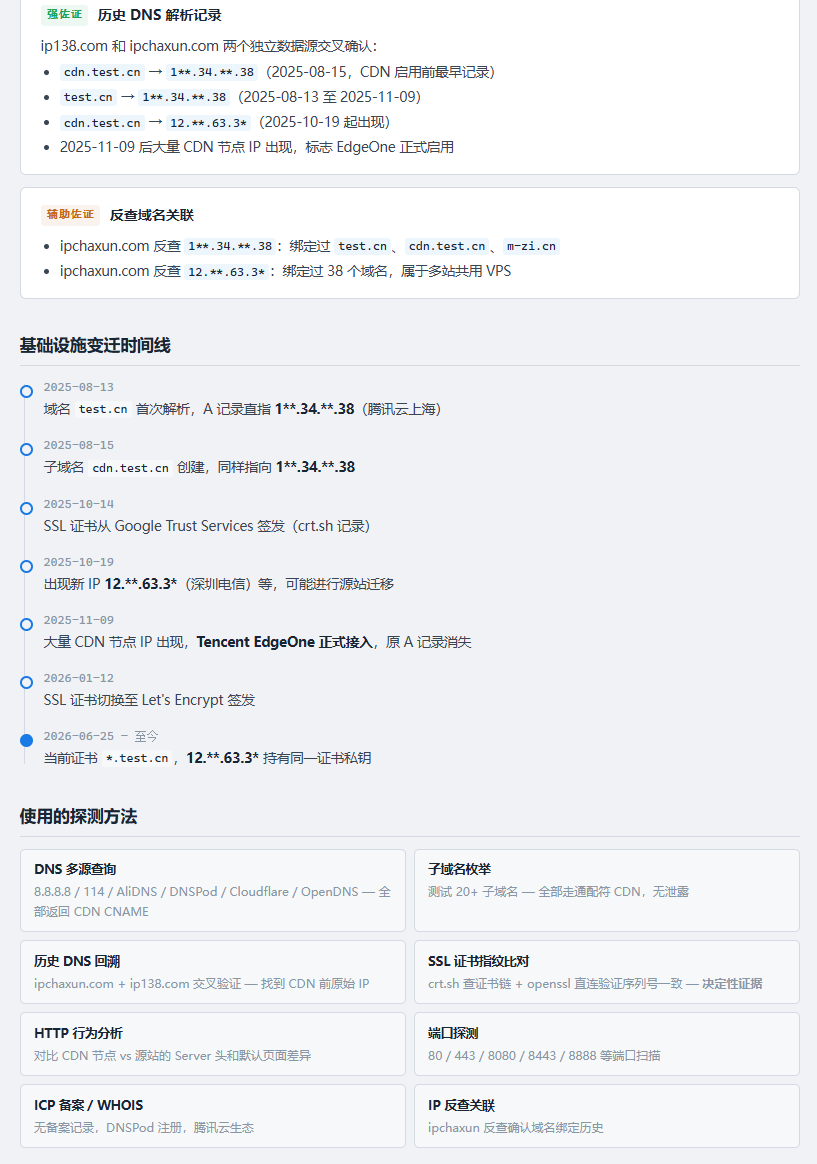
FUCK-CDN preview

FUCK-CDN

GitHub0xshe/fuck-cdn

Automated CDN origin-IP discovery skill for Claude Code that runs 40+ prioritized OSINT methods, cross-validates candidates via SSL and HTTP…
dns-analysisdns-subdomain-enumerationinformation-gathering+9
1512 months ago
nomore403 preview

nomore403

GitHubdevploit/nomore403

🚫 Advanced tool for security researchers to bypass 403/40X restrictions through smart techniques and adaptive request manipulation. Fast. Precise.…
ids-ips-evasionpenetration-testingreconnaissance+3
1.9k3 months ago
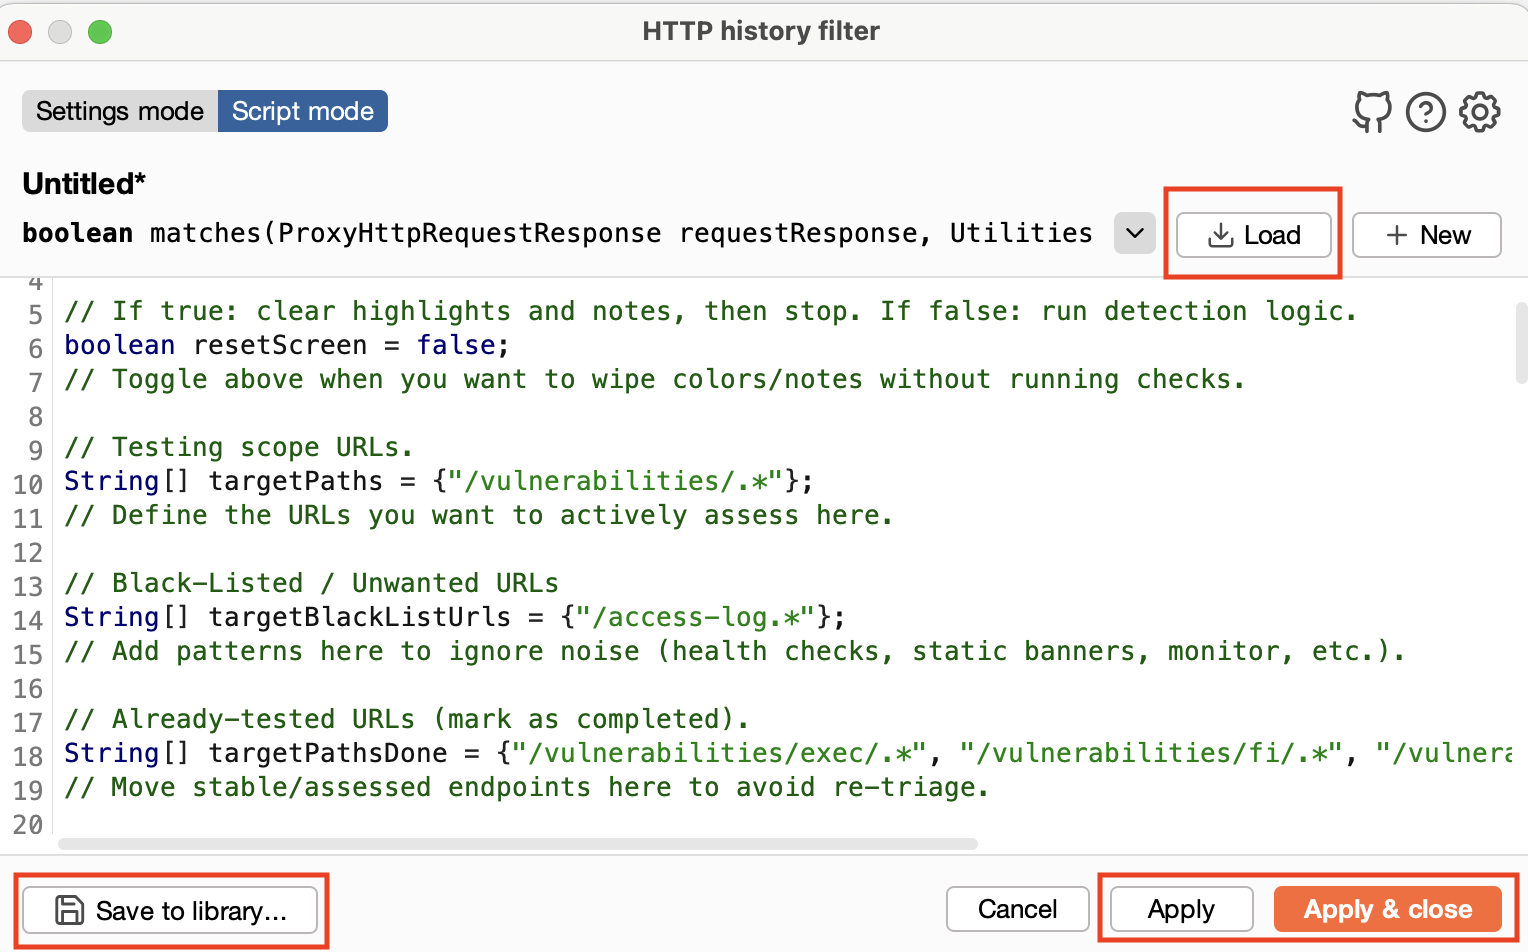
agartha preview

agartha

GitHubvolkandindar/agartha

A Burp Suite extension for identifying injection flaws (LFI, RCE, SQLi), authentication/authorization issues, and HTTP 403 access violations. It…
authentication-authorizationpayload-generationpenetration-testing+4
4134 months ago
wafw00f preview

wafw00f

GitHubenablesecurity/wafw00f

Automated Web Application Firewall fingerprinting tool that identifies and detects over 200 WAF products by analyzing HTTP responses to normal and…
crawlerdynamic-code-analysisinformation-gathering+6
6.6k5 months ago
CVE-2022-31813 preview

CVE-2022-31813

GitHubyiliufeng168/cve-2022-31813

Demonstrates CVE-2022-31813 Apache HTTP Server bypass using X-Real-IP header manipulation to evade access controls, with a Docker-based test…

exploitationpenetration-testingvulnerability-analysis+2
7 months ago
unwaf preview

unwaf

GitHubmmarting/unwaf

Go tool that passively discovers the real origin IP behind a WAF/CDN using multiple OSINT sources, then verifies candidates via HTML similarity, SSL…

dns-subdomain-enumerationinformation-gatheringnetwork-mapping+7
1927 months ago
undetected-httpx preview

undetected-httpx

GitHubmichele0303/undetected-httpx

Stop getting 403 Forbidden. A specialized httpx-like toolkit for WAF evasion.

anti-botfingerprint-spoofingids-ips-evasion+5
228 months ago
CVE-2025-64446-Exploit preview

CVE-2025-64446-Exploit

GitHubsoltanali0/cve-2025-64446-exploit

Python exploit for CVE-2025-64446 targeting FortiWeb WAF, enabling unauthorized user creation and privilege escalation through a crafted HTTP request.

exploitationpenetration-testingred-teaming+3
1310 months ago
Previous12Next