

xss-cheatsheet
 ardakocadoru/xss-cheatsheet
Comprehensive XSS reference covering reflected, stored, DOM and blind payloads, filter bypass, WAF evasion, CSP bypass, mXSS, and real-world CVE case…
curated-resourceseducationpayload-generation+6
2
ardakocadoru/xss-cheatsheetComprehensive XSS reference covering reflected, stored, DOM and blind payloads, filter bypass, WAF evasion, CSP bypass, mXSS, and real-world CVE case…
 yehia-mamdouh/xssya-v-2.0
Python XSS scanner that confirms reflected and encoded-payload injection, executes payloads to capture cookies, detects WAFs, and tests XST with a…
 dinosn/php-cve-2026-10961x-lab-poc
PHP CVE-2026-109618/109619 — self-contained unauthenticated RCE on stock PHP 8.5.11 (in-band PS(id)→cookie memory disclosure + UAF chain), full…
 pennacle-security/summit
Open-source web security testing platform: proxy, scanner and fuzzer in one CLI. By Pennacle Security.
 brutelogic/unkover
Bash 403/401 access bypass tester that probes a URL with header spoofing, method tampering, path normalization, and encoding techniques, returning a…
 affolter-engineering/xssearch
Rust-based XSS scanner with context-aware payload selection, WAF detection and bypass, crawling, blind XSS callbacks, and static DOM sink analysis.
 z3rodayhacks/cve-2026-63030-cve-2026-60137
Pre-auth RCE proof-of-concept chaining a WordPress REST batch API auth bypass with WP_Query SQL injection to dump hashes, add admin users, or plant a…
 kamalx06/xxeripper
Black-box XXE scanner detecting in-band, error-based, and blind out-of-band injection via statistical baselining, parser fingerprinting, and OOB…
 mmarting/unwaf
Go tool that passively discovers the real origin IP behind a WAF/CDN using multiple OSINT sources, then verifies candidates via HTML similarity, SSL…
 ammarion/waf-detector
🛡️ High-performance WAF & CDN detection tool. Identify protection layers (Cloudflare, Akamai, AWS, Fastly, and more), run effectiveness and…
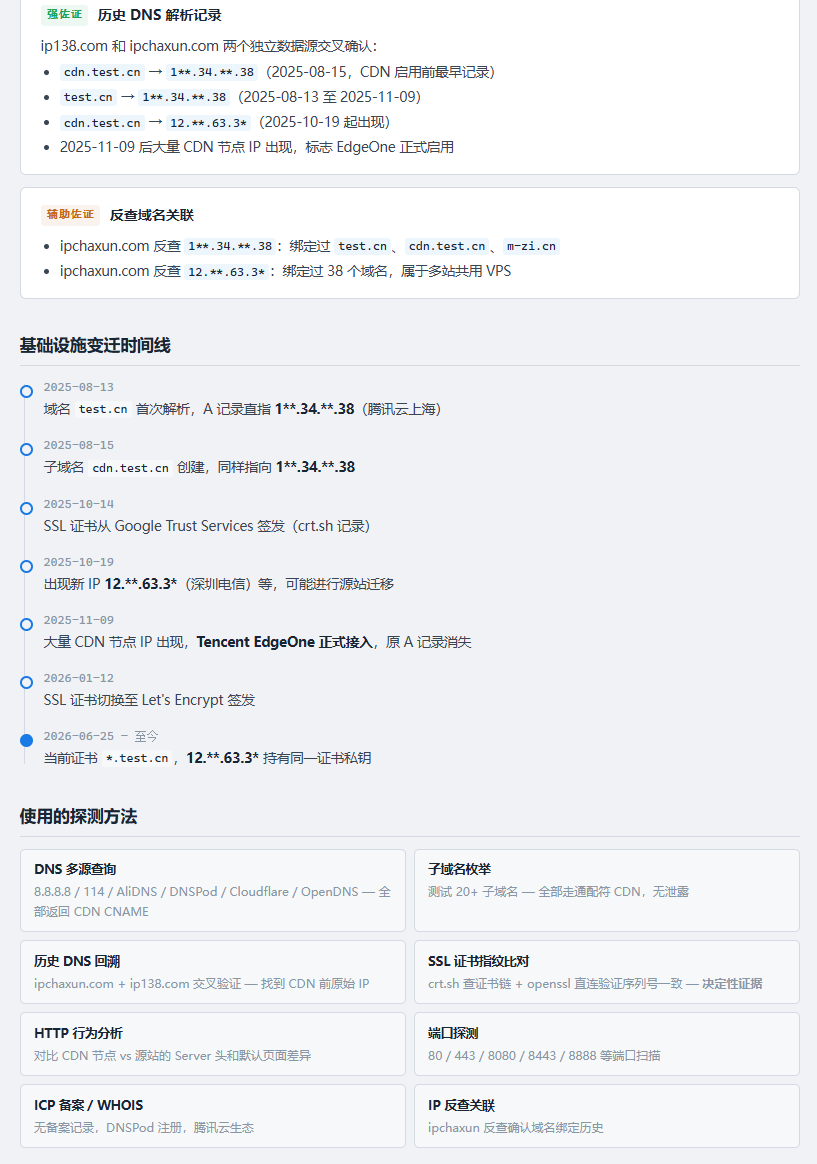 0xshe/fuck-cdn
Automated CDN origin-IP discovery skill for Claude Code that runs 40+ prioritized OSINT methods, cross-validates candidates via SSL and HTTP…
 bhideki/cve-2026-87902
Python PoC and scanner for CVE-2026-87902, a WordPress core path traversal leading to LFI and PEAR-based RCE, with WAF bypass and automated…
 iicaicai/cve-2026-5524-poc
Python mass-exploit toolkit for CVE-2026-5524, an unauthenticated file upload RCE in the WordPress Divi Form Builder plugin, with webshell upload and…
 anonmoty/xxstrike
XSStrike based XSS scanner with custom features. Detects XSS vulnerabilities in web applications.
 wi3memake/react2shell-scanner
Command-line security assessment framework for React and Next.js applications, analyzing React Server Components for misconfigurations, with…
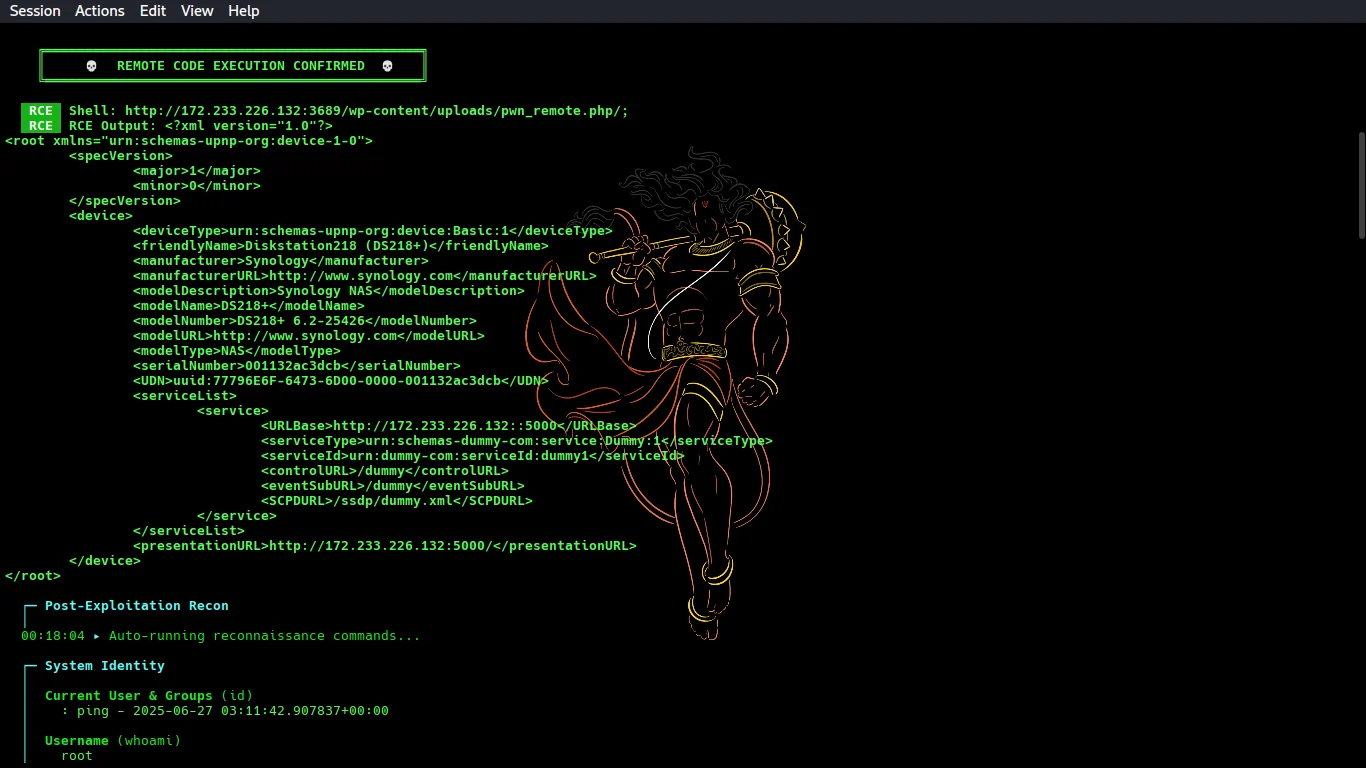 cybertechajju/cve-2026-1357-poc
Automated exploit tool for CVE-2026-1357, an unauthenticated RCE in WPvivid Backup & Migration. Scans WordPress targets, bypasses WAF/403, uploads a…
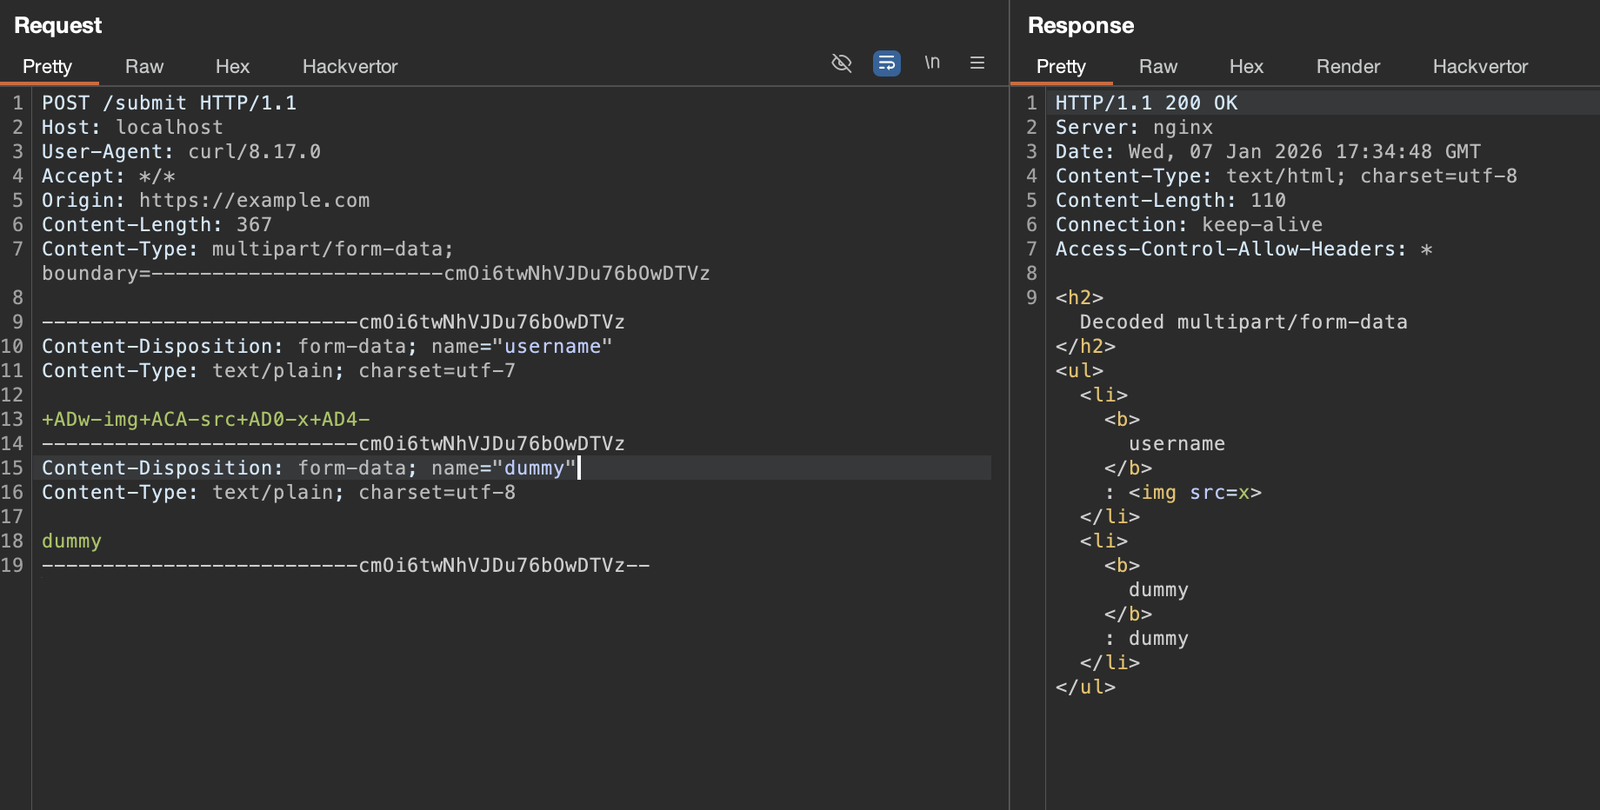 mefhika120/cve-2026-21876
Minimal PoC and Docker container demonstrating a WAF bypass in OWASP ModSecurity CRS via multipart charset handling, leading to XSS payload delivery.
 c00ln3t/log4shellauditor
An autonomous reflective Go agent for full-cycle security auditing, WAF evasion, OOB LDAP verification, self-remediation (auto-patching), and…