
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

··Feeds·Contact·Privacy·© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
66 results
CVE-2026-87902 preview

CVE-2026-87902

GitHubbhideki/cve-2026-87902

Python PoC and scanner for CVE-2026-87902, a WordPress core path traversal leading to LFI and PEAR-based RCE, with WAF bypass and automated…
exploitationpayload-developmentpenetration-testing+6
2 days ago
cve-2021-44228-waf-tests preview

cve-2021-44228-waf-tests

GitHubrobrankin/cve-2021-44228-waf-tests

Testing WAF protection against CVE-2021-44228 Log4Shell
defensive-toolspenetration-testingvulnerability-scanners+2
4 years ago
log4j-scanner preview

log4j-scanner

GitHubmanishkanyal/log4j-scanner

A Log4j vulnerability scanner is used to identify the CVE-2021-44228 and CVE_2021_45046
exploitationfuzzingpenetration-testing+3
14 years ago
CVE-2026-21876 preview

CVE-2026-21876

GitHubmefhika120/cve-2026-21876

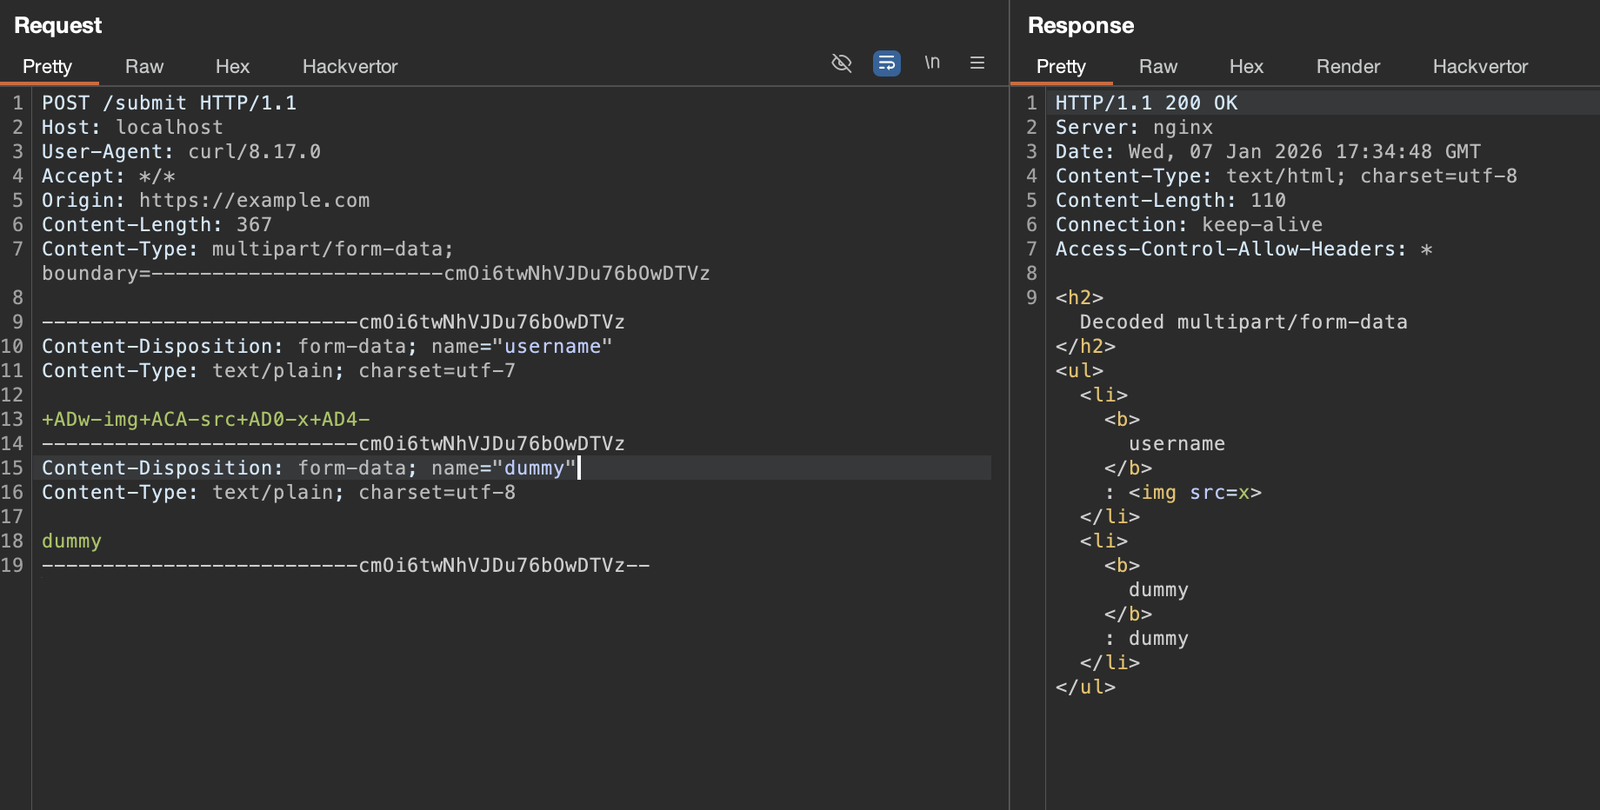
Minimal PoC and Docker container demonstrating a WAF bypass in OWASP ModSecurity CRS via multipart charset handling, leading to XSS payload delivery.
exploitationpenetration-testingvulnerability-analysis+2
8 months ago
Log4ShellAuditor preview

Log4ShellAuditor

GitHubc00ln3t/log4shellauditor

An autonomous reflective Go agent for full-cycle security auditing, WAF evasion, OOB LDAP verification, self-remediation (auto-patching), and…
devsecopsexploitationlabs-practice+6
11 month ago
burp-vps-proxy preview

burp-vps-proxy

GitHubd3mondev/burp-vps-proxy

This Burp Suite extension allows for the automatic creation and deletion of an upstream SOCKS5 proxy on popular cloud services.
penetration-testingutilities-frameworkswaf-bypass+1
2491 year ago
CVE-2025-55182-Advanced-React-Server-Components-RCE-Exploit preview

CVE-2025-55182-Advanced-React-Server-Components-RCE-Exploit

GitHubcerberusmrxi/cve-2025-55182-advanced-react-server-components-rce-exploit

Advanced React Server Components RCE scanner for CVE-2025-55182. Features: multi-stage fingerprinting, vulnerability verification, DNS exfiltration,…
data-exfiltrationexploitationpayload-development+6
11 month ago
react2shell-scanner preview

react2shell-scanner

GitHuborwagodfather/react2shell-scanner

RSC/Next.js RCE (CVE-2025-55182 & CVE-2025-66478)

exploitationpenetration-testingwaf-bypass+3
189 months ago
CVE-2020-6519 preview

CVE-2020-6519

GitHubweizman/cve-2020-6519

Proof-of-concept exploit for CVE-2020-6519 - a Chromium zero-day that fully bypasses Content Security Policy (CSP) across platforms, enabling script…

exploitationpenetration-testingred-teaming+4
66 years ago
watchTowr-vs-Fortiweb-AuthBypass preview

watchTowr-vs-Fortiweb-AuthBypass

GitHubwatchtowrlabs/watchtowr-vs-fortiweb-authbypass

Python-based detector for FortiWeb authentication bypass (CVE-2025-xxxxx). Sends exploit payload to create a test user as proof of exploitation.
exploitationpenetration-testingvulnerability-analysis+2
7610 months ago
CVE-2025-48148 preview

CVE-2025-48148

GitHubnxploited/cve-2025-48148

StoreKeeper for WooCommerce <= 14.4.4 - Unauthenticated Arbitrary File Upload
exploitationpayload-developmentpenetration-testing+3
11 months ago
CVE-2025-55182-React-RCE preview

CVE-2025-55182-React-RCE

GitHubxcanwin/cve-2025-55182-react-rce

[漏洞复现] 全球首款基于RSC特性能绕过WAF检测的CVE-2025-55182 React Server RCE 漏洞 EXP。
exploitationpayload-developmentpenetration-testing+3
159 months ago
CVE-2022-31813 preview

CVE-2022-31813

GitHubyiliufeng168/cve-2022-31813

Demonstrates CVE-2022-31813 Apache HTTP Server bypass using X-Real-IP header manipulation to evade access controls, with a Docker-based test…

exploitationpenetration-testingvulnerability-analysis+2
6 months ago
CVE-2025-25369 preview

CVE-2025-25369

GitHublkasjkasj/cve-2025-25369

Documented XSS exploit for ZKBio CVSecurity v.6.4.1 with WAF bypass, enabling privilege escalation from Template Editor to administrator via crafted…
exploitationpenetration-testingprivilege-escalation+3
1 year ago
Bypass-CVE-2025-58360 preview

Bypass-CVE-2025-58360

GitHubquyenheu/bypass-cve-2025-58360

A new way to exploit CVE-2025-58360 bypass WAF
exploitationpenetration-testingvulnerability-analysis+2
18 months ago
NextRce preview

NextRce

GitHubynsmroztas/nextrce

React Shell & Next.js RSC Exploit Tool (CVE-2025-55182)
command-and-controlexploitationpayload-development+5
2659 months ago
r2s preview

r2s

GitHubzamdevio/r2s

Advanced security testing tool for CVE-2025-55182 vulnerability assessment in Next.js applications. Features interactive shell, batch scanning, WAF…
command-and-controlexploitationinformation-gathering+5
29 months ago
CVE-2025-55182-poc-tool preview

CVE-2025-55182-poc-tool

GitHubdh4v4l8/cve-2025-55182-poc-tool

Automated exploit tool for CVE-2025-55182 in Next.js React Server Components. Enables remote command execution with built-in WAF bypass, custom…

exploitationpenetration-testingremote-access-tool+3
39 months ago
Previous1234Next