
aethel_core
 lokinpendawa/aethel_core
Next-gen logical WAF engine built in SWI-Prolog. Features an inductive learning brain running at 2M+ LIPS with an integrated recursive decoder to…
ai-securityanomaly-detectionthreat-intelligence+3
5
lokinpendawa/aethel_coreNext-gen logical WAF engine built in SWI-Prolog. Features an inductive learning brain running at 2M+ LIPS with an integrated recursive decoder to…
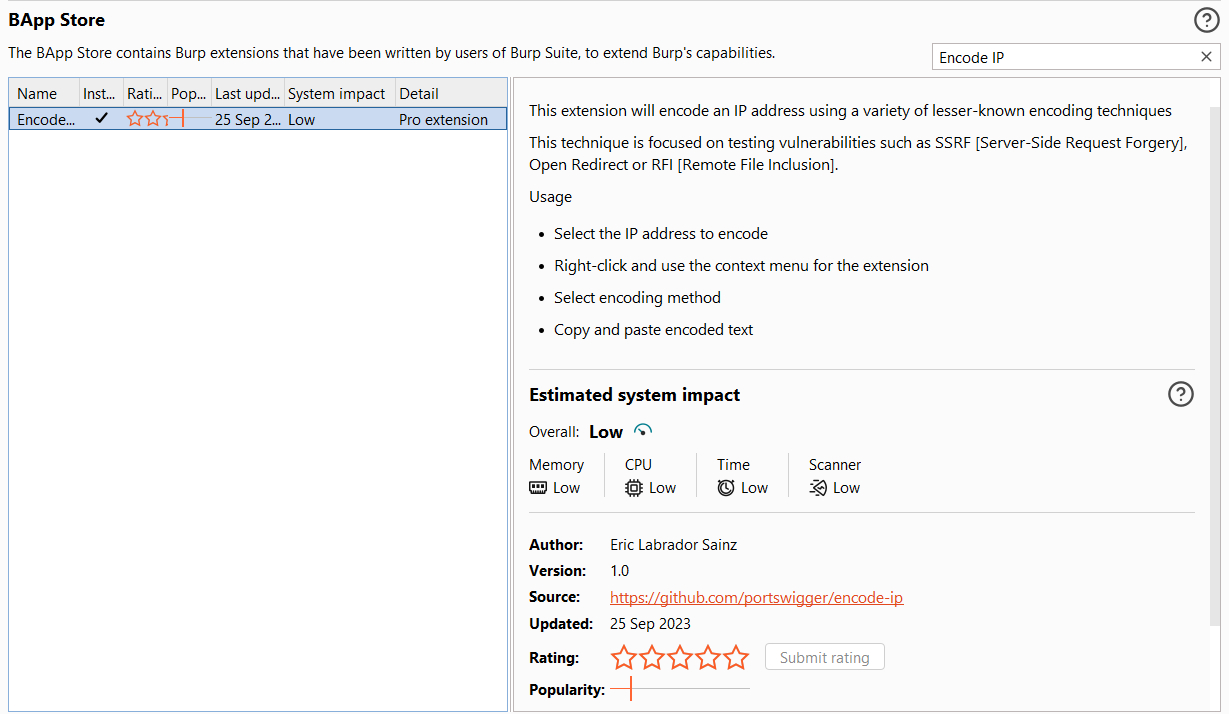 e1abrador/burp-encode-ip
Burp Suite extension to encode an IP address focused to bypass application IP / domain blacklist.
 redsection/pfuzz
Modular WAF bypass fuzzer with multi-threading, request manipulation, and payload encoding for red team web application testing.
 d00movenok/bounceback
↕️🤫 Stealth redirector for your red team operation security
 fatguru/cve-2025-55182-scanner
A non-intrusive surface scanner for CVE-2025-55182 (React Server Components RCE). Detects exposed RSC endpoints in React 19 and Next.js applications
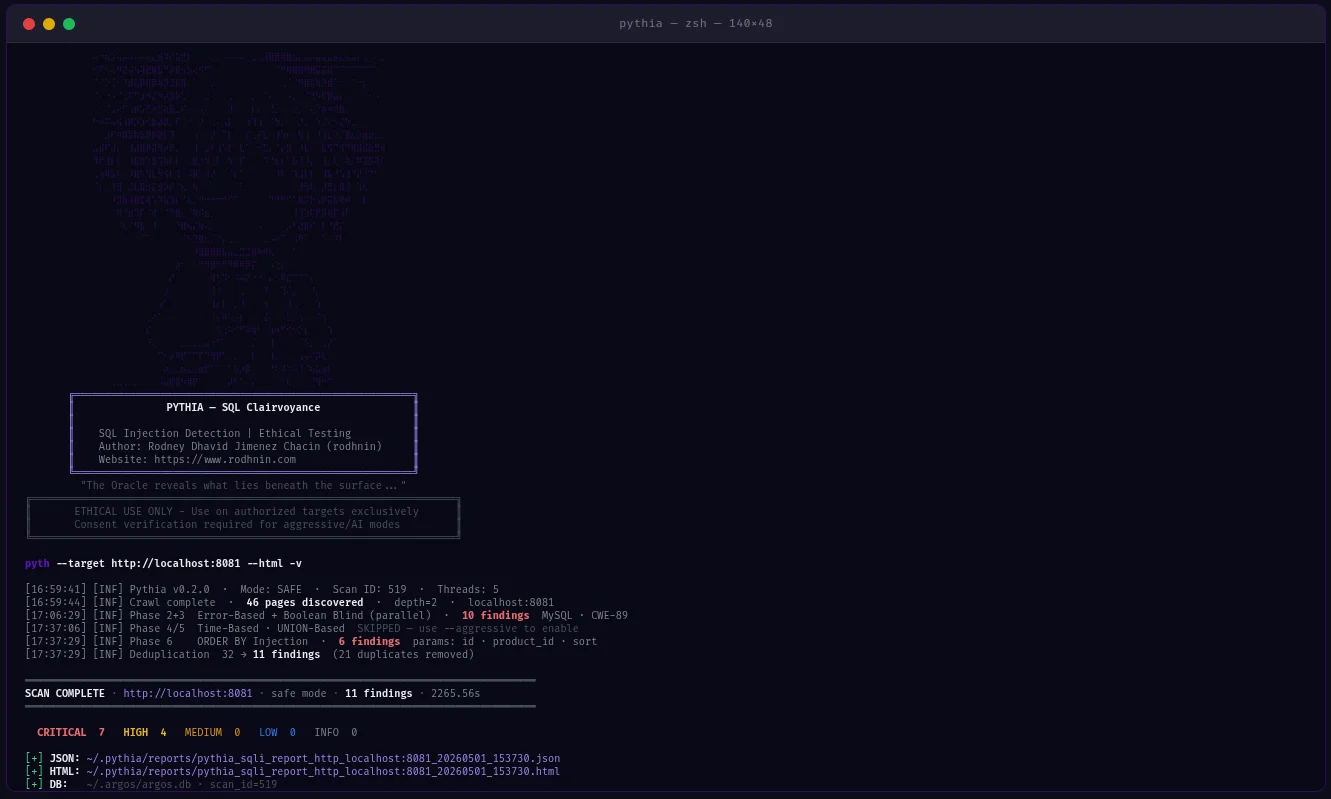 rodhnin/pythia-sql-clairvoyance
Advanced SQL Injection Scanner with AI-powered analysis, ethical compliance framework, and professional reporting.
 weizman/cve-2020-6519
Proof-of-concept exploit for CVE-2020-6519 - a Chromium zero-day that fully bypasses Content Security Policy (CSP) across platforms, enabling script…
 ghostn4444/cve-2025-55182
Next.js RSC RCE vulnerability scanner with multiple scan modes, WAF bypass, interactive shell, and batch scanning for authorized penetration testing.
 h0tak88r/next88
High-performance Go implementation for detecting React Server Components RCE vulnerabilities (CVE-2025-55182 & CVE-2025-66478).
 soltanali0/cve-2025-64446-exploit
Python exploit for CVE-2025-64446 targeting FortiWeb WAF, enabling unauthorized user creation and privilege escalation through a crafted HTTP request.