
api-scanner-docker
Automated API security testing tool that scans REST and SOAP APIs for vulnerabilities using OpenAPI/Swagger specs and WSDL files. Deploys a full …

Automated API security testing tool that scans REST and SOAP APIs for vulnerabilities using OpenAPI/Swagger specs and WSDL files. Deploys a full …

Automated REST API fuzzer and negative testing tool for OpenAPI endpoints. Generates, runs, and reports thousands of self-healing tests with no…

Validates Google Maps API keys against 21 endpoints, revealing exposed services with PoC URLs, proxy support, and quiet mode for focused auditing.

RESTler is the first stateful REST API fuzzing tool for automatically testing cloud services through their REST APIs and finding security and…

Multi-threaded scanner for detecting exposed Swagger/OpenAPI endpoints across web domains and subdomains, with automatic XSS detection, PoC…

A comprehensive web application security testing toolkit that combines 10 powerful penetration testing features into one tool.

Command-line security assessment framework for React and Next.js applications, analyzing React Server Components for misconfigurations, with…

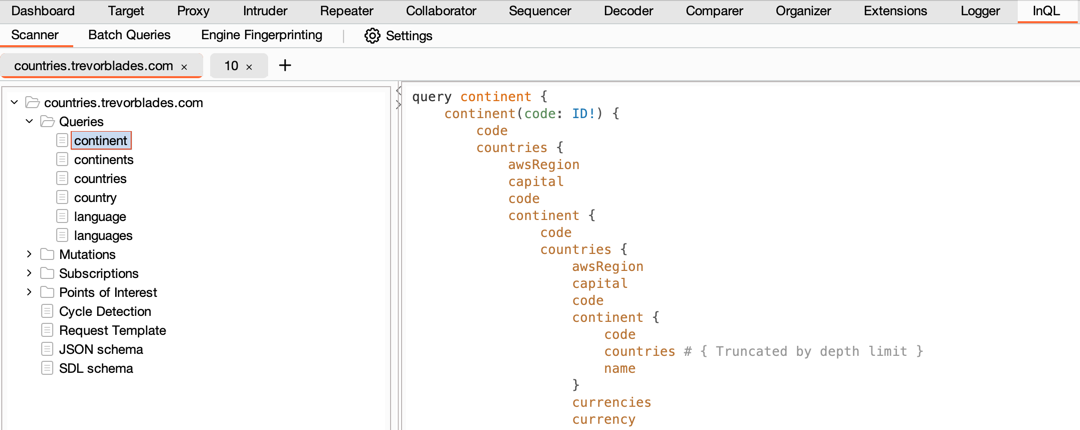
InQL is a robust, open-source Burp Suite extension for advanced GraphQL testing, offering intuitive vulnerability detection, customizable scans, and…

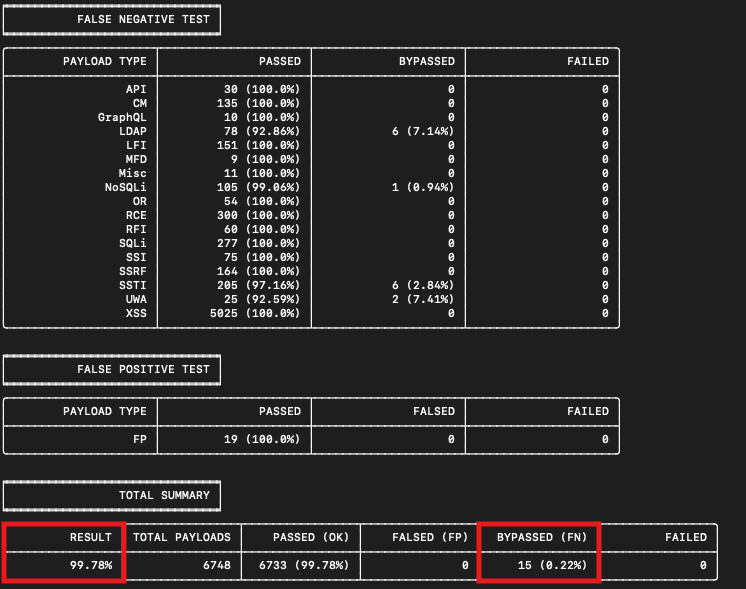
Automated WAF security testing tool that detects false positives and false negatives using 15+ payload categories including SQLi, XSS, RCE, and…

A tool for auditing endpoints defined in exposed (Swagger/OpenAPI) definition files.

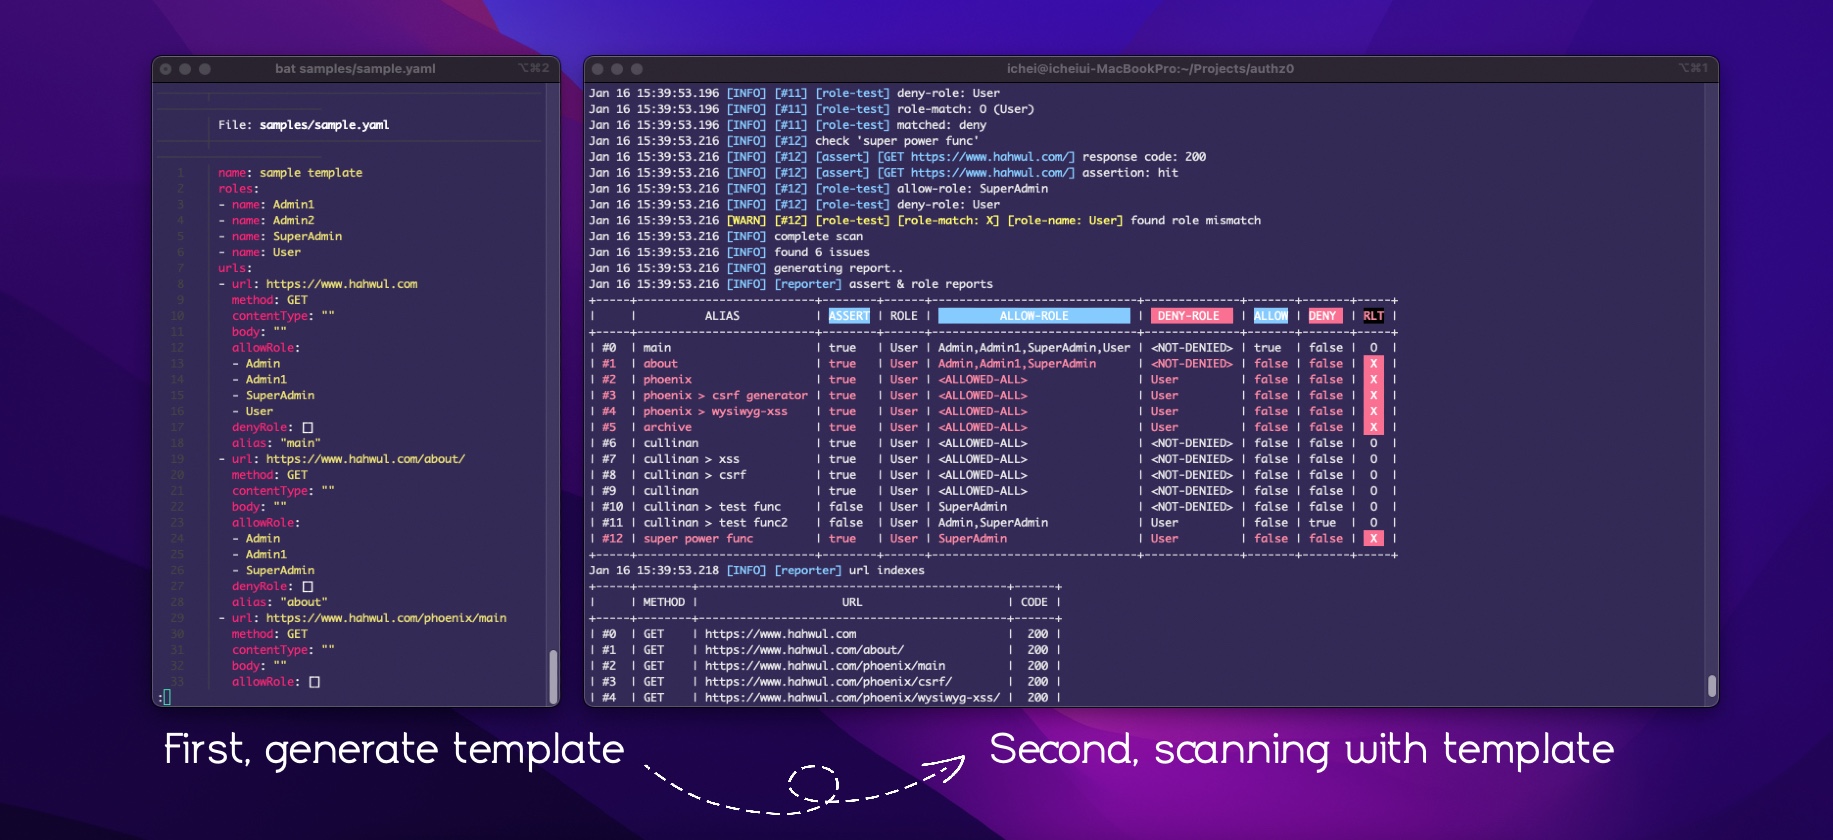
Automated authorization testing tool that detects unauthorized access by scanning URLs with role-based credentials using YAML templates.

Unofficial Acunetix CLI tool for automated pentesting and bug hunting across large scopes.

A lightweight CLI tool for systematically detecting and exploiting race conditions in web applications, APIs, and modern services.

Comprehensive vulnerability detection tool for n8n workflow automation instances. Detects the critical CVE-2026-21858 vulnerability (CVSS 10.0)…

A lightweight Python-based security assessment tool for detecting dangerous Cross-Origin Resource Sharing (CORS) misconfigurations - CVE-2025-34291.

Python API security testing tool from OpenStack Security Group

An on-path blackbox network traffic security testing tool

Rust-powered HTTP Request Smuggling Scanner.