

trivy
 aquasecurity/trivy
Find vulnerabilities, misconfigurations, secrets, SBOM in containers, Kubernetes, code repositories, clouds and more
cloud-infrastructure-securitycloud-securitycode-analysis+14
38.3k
aquasecurity/trivyFind vulnerabilities, misconfigurations, secrets, SBOM in containers, Kubernetes, code repositories, clouds and more
 hackmanit/web-cache-vulnerability-scanner
Go-based CLI scanner for web cache poisoning and deception. Supports 10 poisoning techniques, multiple deception methods, built-in crawler, JSON…
 purpleteam-labs/purpleteam-s2-containers
Stage two containers
 purpleteam-labs/purpleteam-tls-checker
TLS checking component of purpleteam
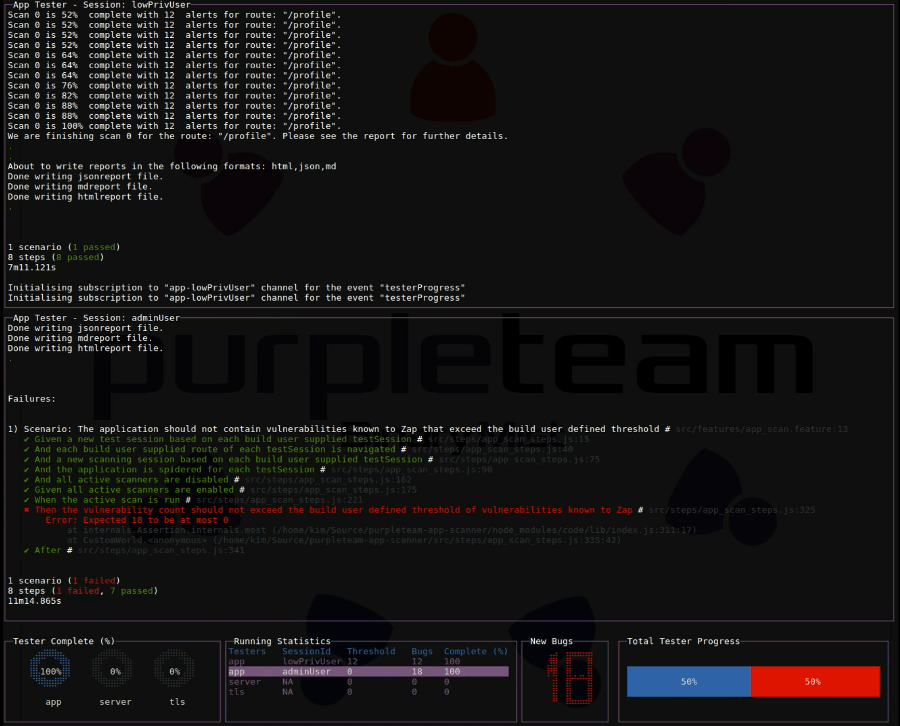 purpleteam-labs/purpleteam
CLI component of purpleteam
 purpleteam-labs/purpleteam-app-scanner
Application scanning component of purpleteam
 purpleteam-labs/purpleteam-server-scanner
Server scanning component of purpleteam
 purpleteam-labs/purpleteam-orchestrator
Orchestration component of purpleteam
 tombstoneghost/tiwap
Deliberately vulnerable Flask web application with 22 security flaws across 3 difficulty levels for hands-on penetration testing and web security…
 psiinon/open-source-web-scanners
Curated list of open-source web security scanners, including general-purpose scanners, infrastructure scanners, and fuzzers, ordered by GitHub stars.
 owasp/asst
OWASP ASST (Automated Software Security Toolkit) | A Novel Open Source Web Security Scanner.
 mohshomis/modo
Curated collection of cybersecurity learning resources, CTF writeups, research papers, and practical labs for hands-on skill development across web…
 0xdevrel/easyscan
Python-based web security scanner that analyzes HTTP headers, SSL/TLS, DNS records, and common misconfigurations to generate a scored security report…
 duriantaco/ravage
Evidence first autonomous web security testing for controlled, authorized targets. With reproducible labs, audit trails, reports, and XBEN…
 rawsec/rawsec-cybersecurity-list
Curated inventory of cybersecurity tools and resources covering penetration testing, forensics, OSINT, web security, malware analysis, cryptography,…
 yahoo/gryffin
Gryffin is a large scale web security scanning platform.
 owtf/owtf
Modular penetration testing framework integrating multiple tools for automated web application security assessment, aligned with OWASP Testing Guide,…
 quarantyne/quarantyne
Modern Web Firewall: stop account takeovers, weak passwords, cloud IPs, DoS attacks, disposable emails