
apicheck
 owasp/apicheck
Modular DevSecOps toolset for REST API security testing, designed for developers, sysadmins, and penetration testers to automate security checks…
api-securityapi-security-testingdevsecops+3
37
owasp/apicheckModular DevSecOps toolset for REST API security testing, designed for developers, sysadmins, and penetration testers to automate security checks…
 brinhosa/apidetector
Multi-threaded scanner for detecting exposed Swagger/OpenAPI endpoints across web domains and subdomains, with automatic XSS detection, PoC…
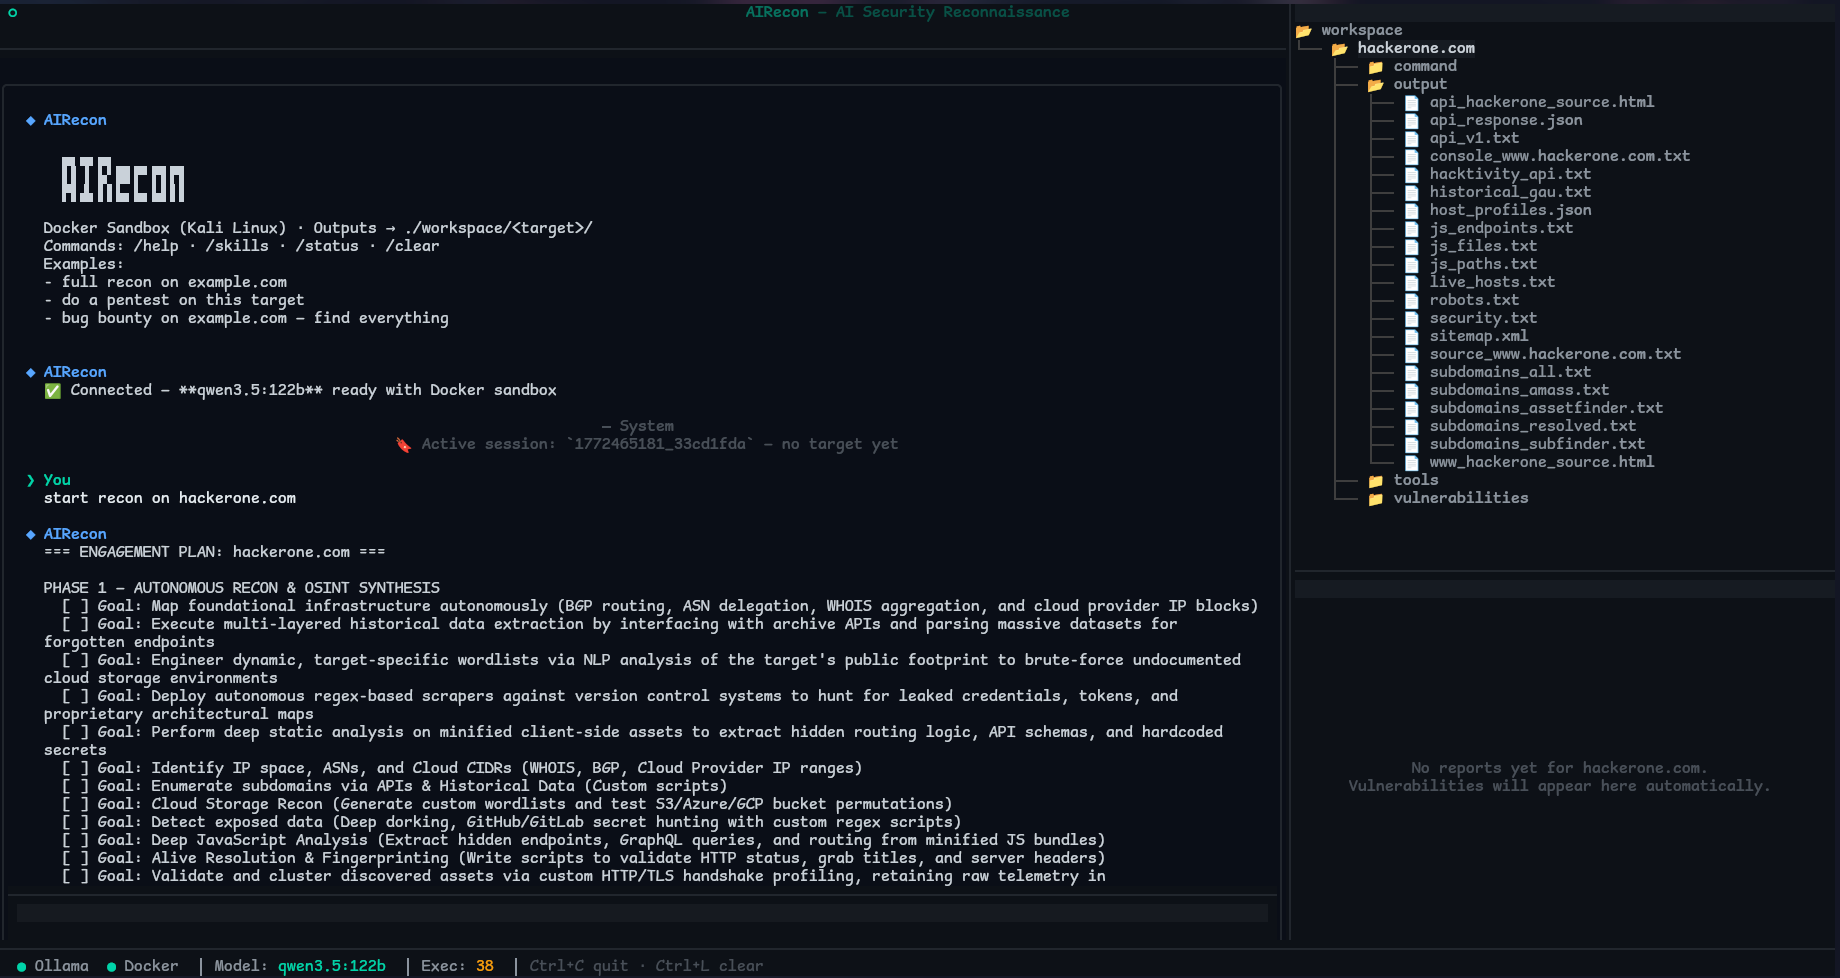 pikpikcu/airecon
AIRecon is an autonomous cybersecurity agent that combines a self-hosted Large Language Model (Ollama) with a Kali Linux Docker sandbox and a Textual…
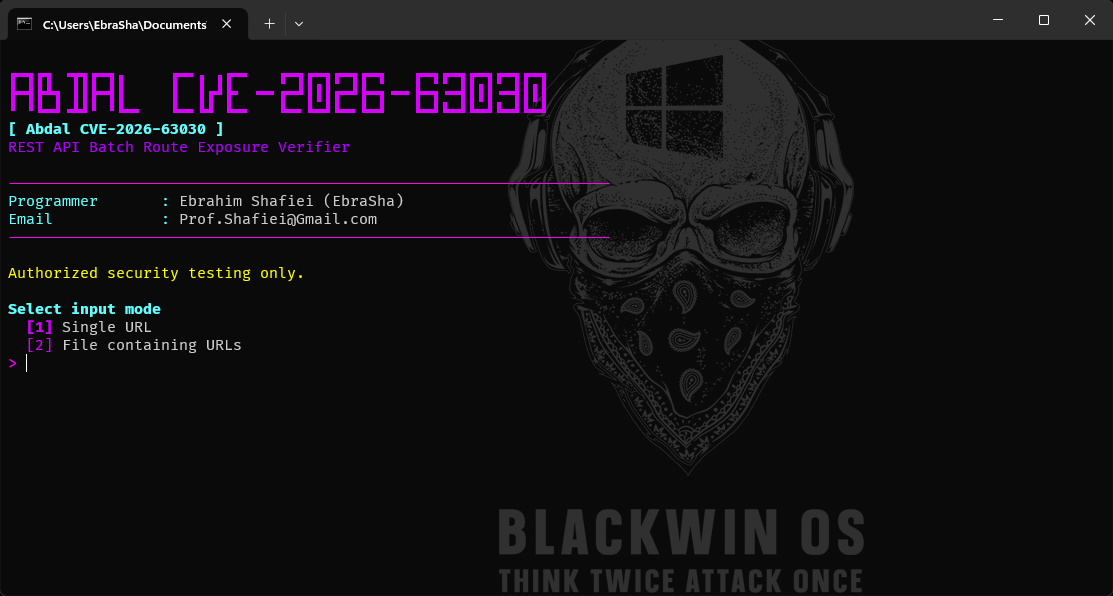 ebrasha/abdal-cve-2026-63030
Abdal CVE-2026-63030 is a professional WordPress vulnerability scanner designed to detect exposure to CVE-2026-63030 through version analysis and…
 microsoft/restler-fuzzer
RESTler is the first stateful REST API fuzzing tool for automatically testing cloud services through their REST APIs and finding security and…
 eilonh/s3crets_scanner
Automated scanner that hunts for secrets (API keys, credentials) accidentally uploaded to public S3 buckets, using truffleHog3 for detection and…
 sohelyousef/js-secret-hunter
Automated Python scanner to detect hardcoded secrets (Private Keys, API Tokens) in client-side JavaScript files.
 bishopfox/sj
A tool for auditing endpoints defined in exposed (Swagger/OpenAPI) definition files.
 ap0dexme0/cve-2023-2732
Perform With Massive Authentication Bypass (Wordpress Mstore-API)
 six2dez/reconftw
reconFTW is a tool designed to perform automated recon on a target domain by running the best set of tools to perform scanning and finding out…
 andresriancho/w3af
Open-source web application security scanner that identifies and exploits 200+ vulnerabilities including XSS, SQL injection, and OS commanding.…
 mindpatch/scant3r
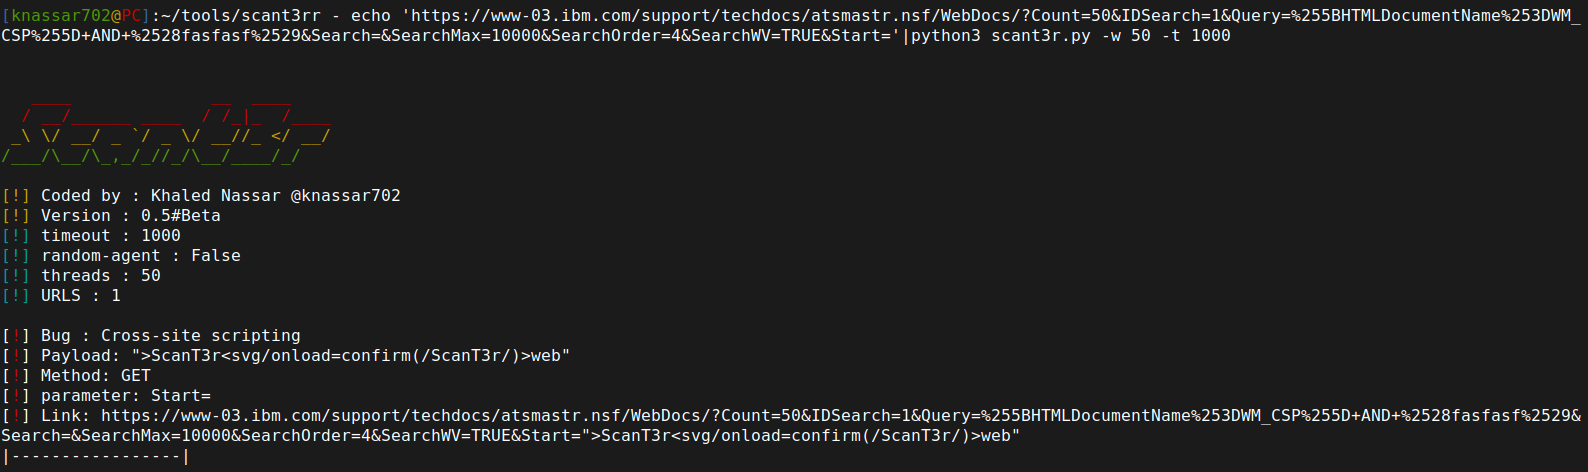
Module-based web vulnerability scanner and bug bounty automation framework with built-in XSS, SSTI, SSRF, and Firebase detection engines. Designed to…
 tamim1089/hikvisionexploiter
HikvisionExploiter is a Python-based utility designed to automate exploitation and directory accessibility checks on Hikvision network cameras…
 dragonked2/egyscan
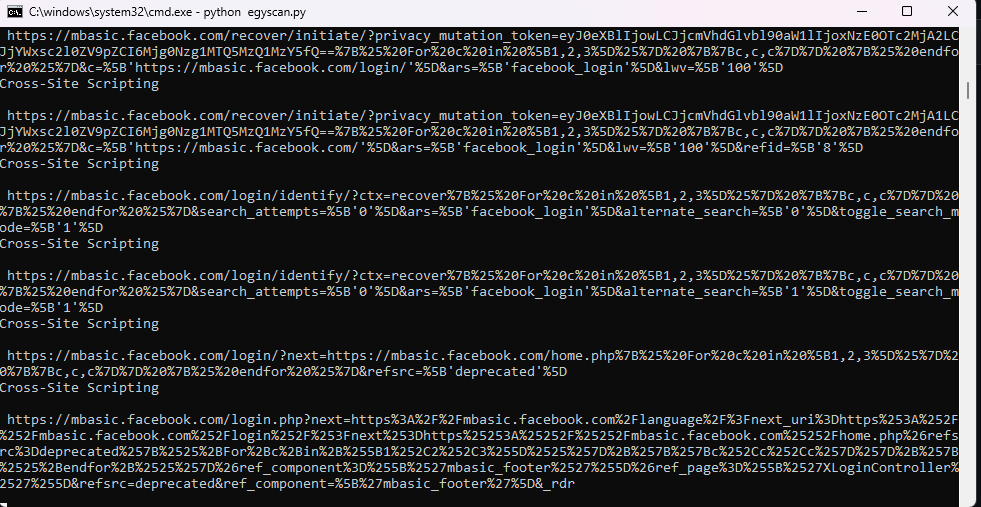
Egyscan The Best web vulnerability scanner; it's a multifaceted security powerhouse designed to fortify your web applications against malicious…
 softrams/bulwark
An organizational asset and vulnerability management tool, with Jira integration, designed for generating application security reports.
 d4vinci/clickjacking-tester
A python script designed to check if the website if vulnerable of clickjacking and create a poc
 nccgroup/argumentinjectionhammer
A Burp Extension designed to identify argument injection vulnerabilities.
 nccgroup/ccs
Regex-based scanner for detecting hard-coded credentials in codebases, designed for CI/CD integration with suppression comment support and low…