
PSO - Printer Security Offensive
 hivesecurity/pso-printer-security-offensive
Offensive security tool for printer pentesting
exploitationhardware-securityinformation-gathering+4
hivesecurity/pso-printer-security-offensiveOffensive security tool for printer pentesting
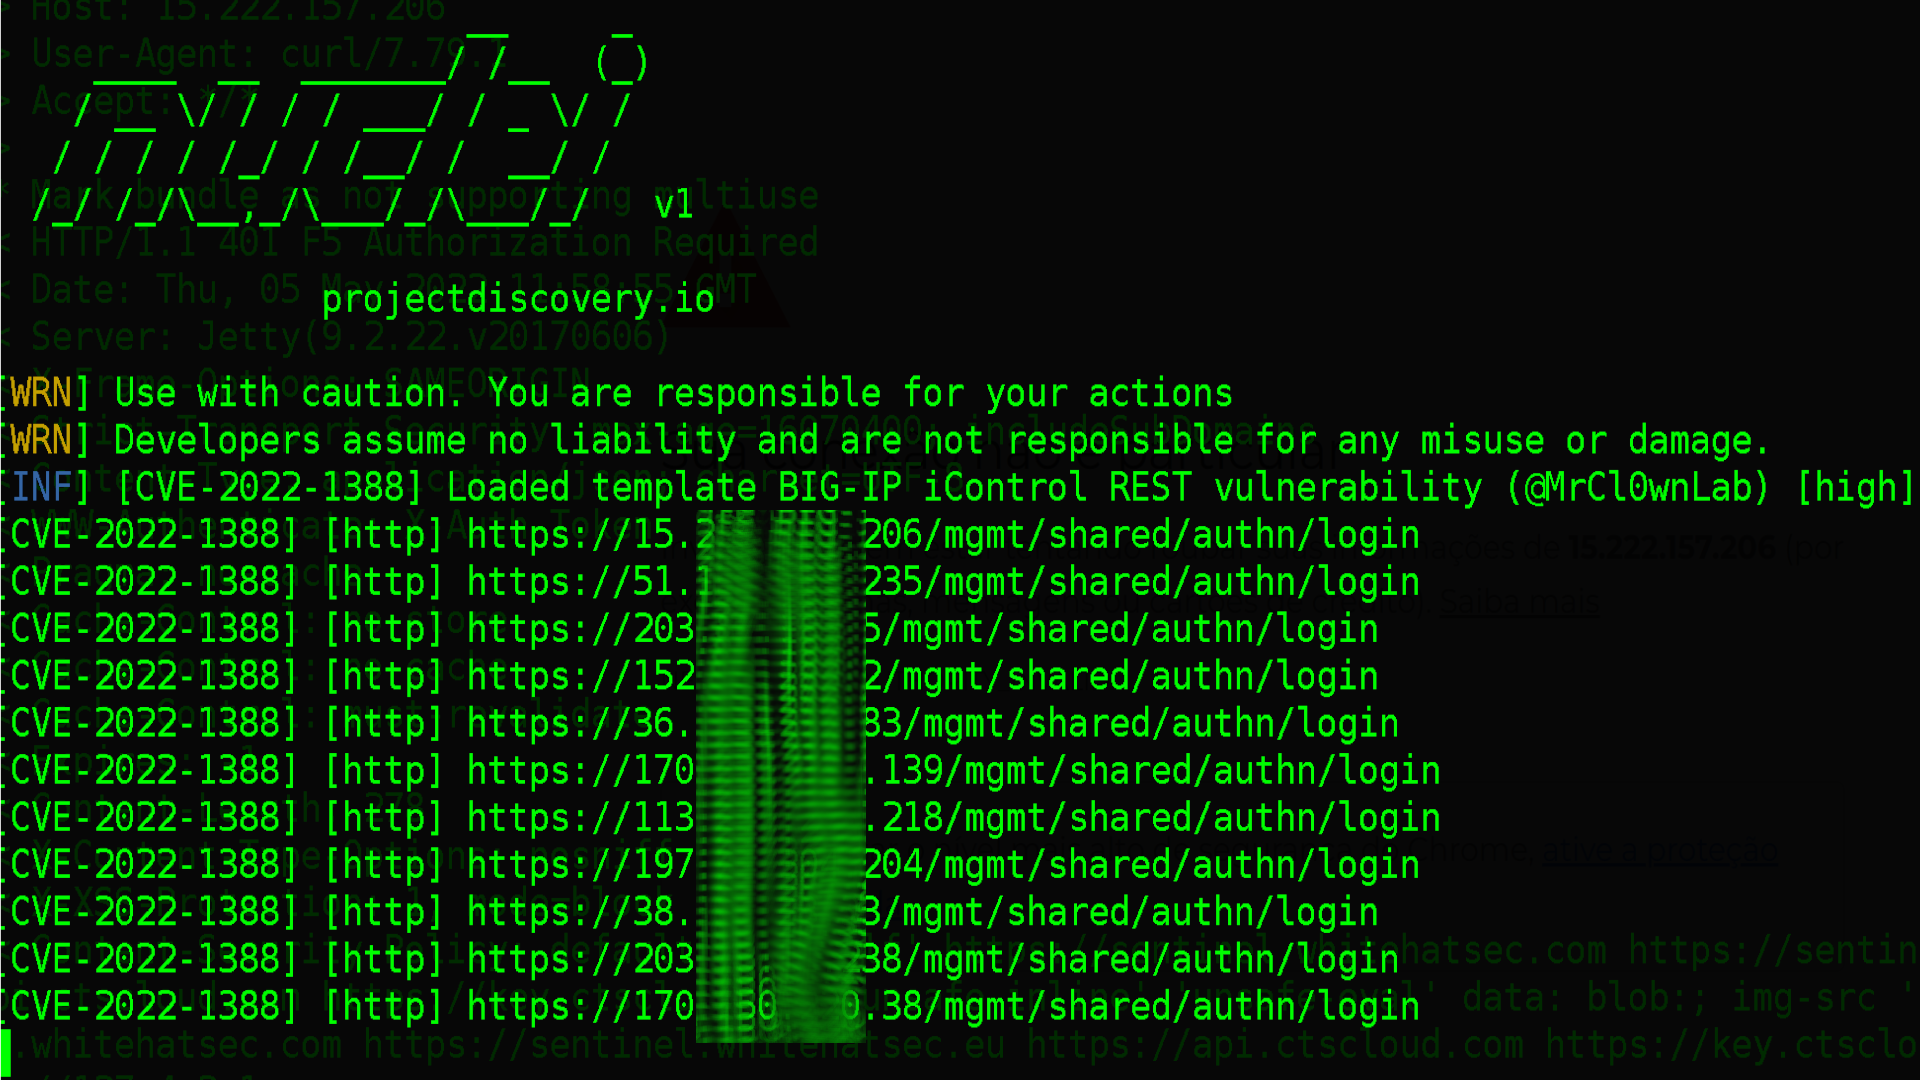
 mrcl0wnlab/nuclei-template-cve-2022-1388-big-ip-icontrol-rest-exposed
This vulnerability may allow an unauthenticated attacker with network access to the BIG-IP system through the management port and/or self IP…
 al1ex/cve-2022-1388
CVE-2022-1388 F5 BIG-IP iControl REST RCE
 yukar1z0e/cve-2022-1388
batch scan CVE-2022-1388
 google/tsunami-security-scanner
Tsunami is a general purpose network security scanner with an extensible plugin system for detecting high severity vulnerabilities with high…
 zcyberseclab/zscan
A fast, customizable service detection tool powered by a flexible fingerprint system. It helps you identify services, APIs, and network…
 imthenachoman/how-to-secure-a-linux-server
Step-by-step guide for hardening a Linux server, covering SSH security, firewalls, intrusion detection, auditing, and system configuration to reduce…
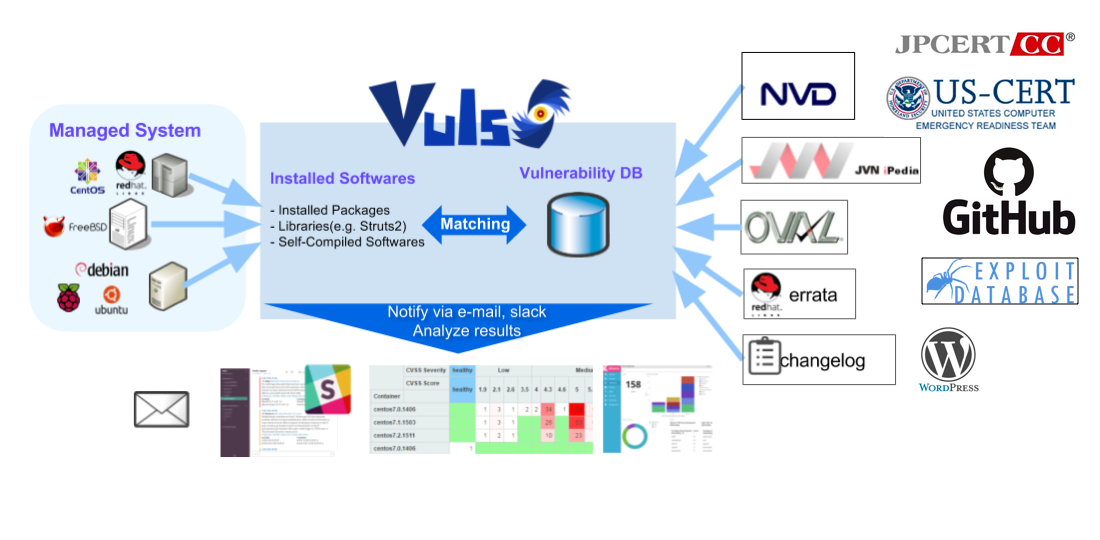 future-architect/vuls
Agent-less vulnerability scanner for Linux, FreeBSD, Container, WordPress, Programming language libraries, Network devices
 ssc-ict-innovatie/nl-kat-coordination
Modular network scanning framework that integrates diverse tools and external databases to detect vulnerabilities and configuration errors, producing…
 usdag/sncscan
Tool for analyzing SAP Secure Network Communications (SNC).
 yojiwatanabe/networkalarm
A tool to monitor local network traffic for possible security vulnerabilities. Warns user against possible nmap scans, Nikto scans, credentials sent…
 hwdsl2/setup-ipsec-vpn
Automated IPsec VPN server setup with IPsec/L2TP, Cisco IPsec, and IKEv2 support. Includes helper scripts for user and certificate management, and…
 gagaltotal/cve-2026-42945-nginx-rift-toolkit
Automated toolkit for scanning, exploiting, and patching CVE-2026-42945 (critical RCE in nginx). Includes network scanner, heap spray exploit, and…
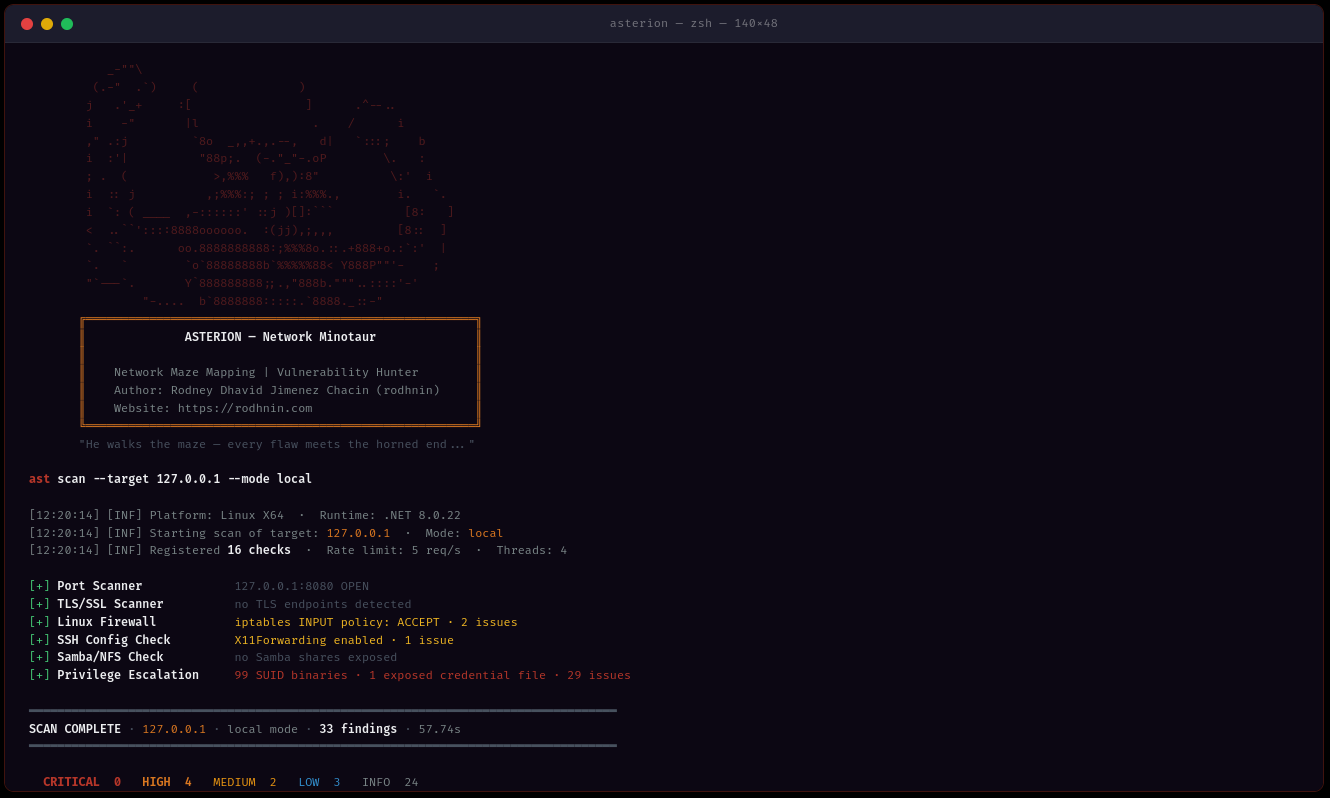 rodhnin/asterion-network-minotaur
Network and domain security auditor scanning Windows Active Directory, Linux systems, and network infrastructure with AI-powered hardening guides…
 soemoescode/guardskill
Read-only scanner for what lets a repository run code in a coding agent (Claude Code, Codex, Cursor, Copilot): git settings, hooks, and committed MCP…
 hargabyte/cve-scanner
Local CVE scanner for OpenClaw that checks versions against 522+ known vulnerabilities, displays recent HIGH-severity CVEs, and recommends upgrades.…
 hackervlogofficial/cve-2026-23918
This is a proactive tool for security auditing. For your GitHub repository, you’ll want a description that highlights its safety (non-intrusive) and…
 raptoratack/copyfail-scanner-cve-2026-31431
Scans systems for CVE-2026-31431 (CopyFile vulnerability), enumerates system details, evaluates exposure, reports vulnerable status, and optionally…