npm-incident-response

Scanner for the keyv/cacheable supply-chain attack: detects compromised npm packages, verifies payload hashes, and finds persistence implants in repo…

Scanner for the keyv/cacheable supply-chain attack: detects compromised npm packages, verifies payload hashes, and finds persistence implants in repo…

Windows 10 patch level scanner that detects missing patches, identifies associated CVEs, and links to public exploit code for vulnerability…

Wicked sick v2.0 script is intended to automate your reconnaissance process in an organized fashion.

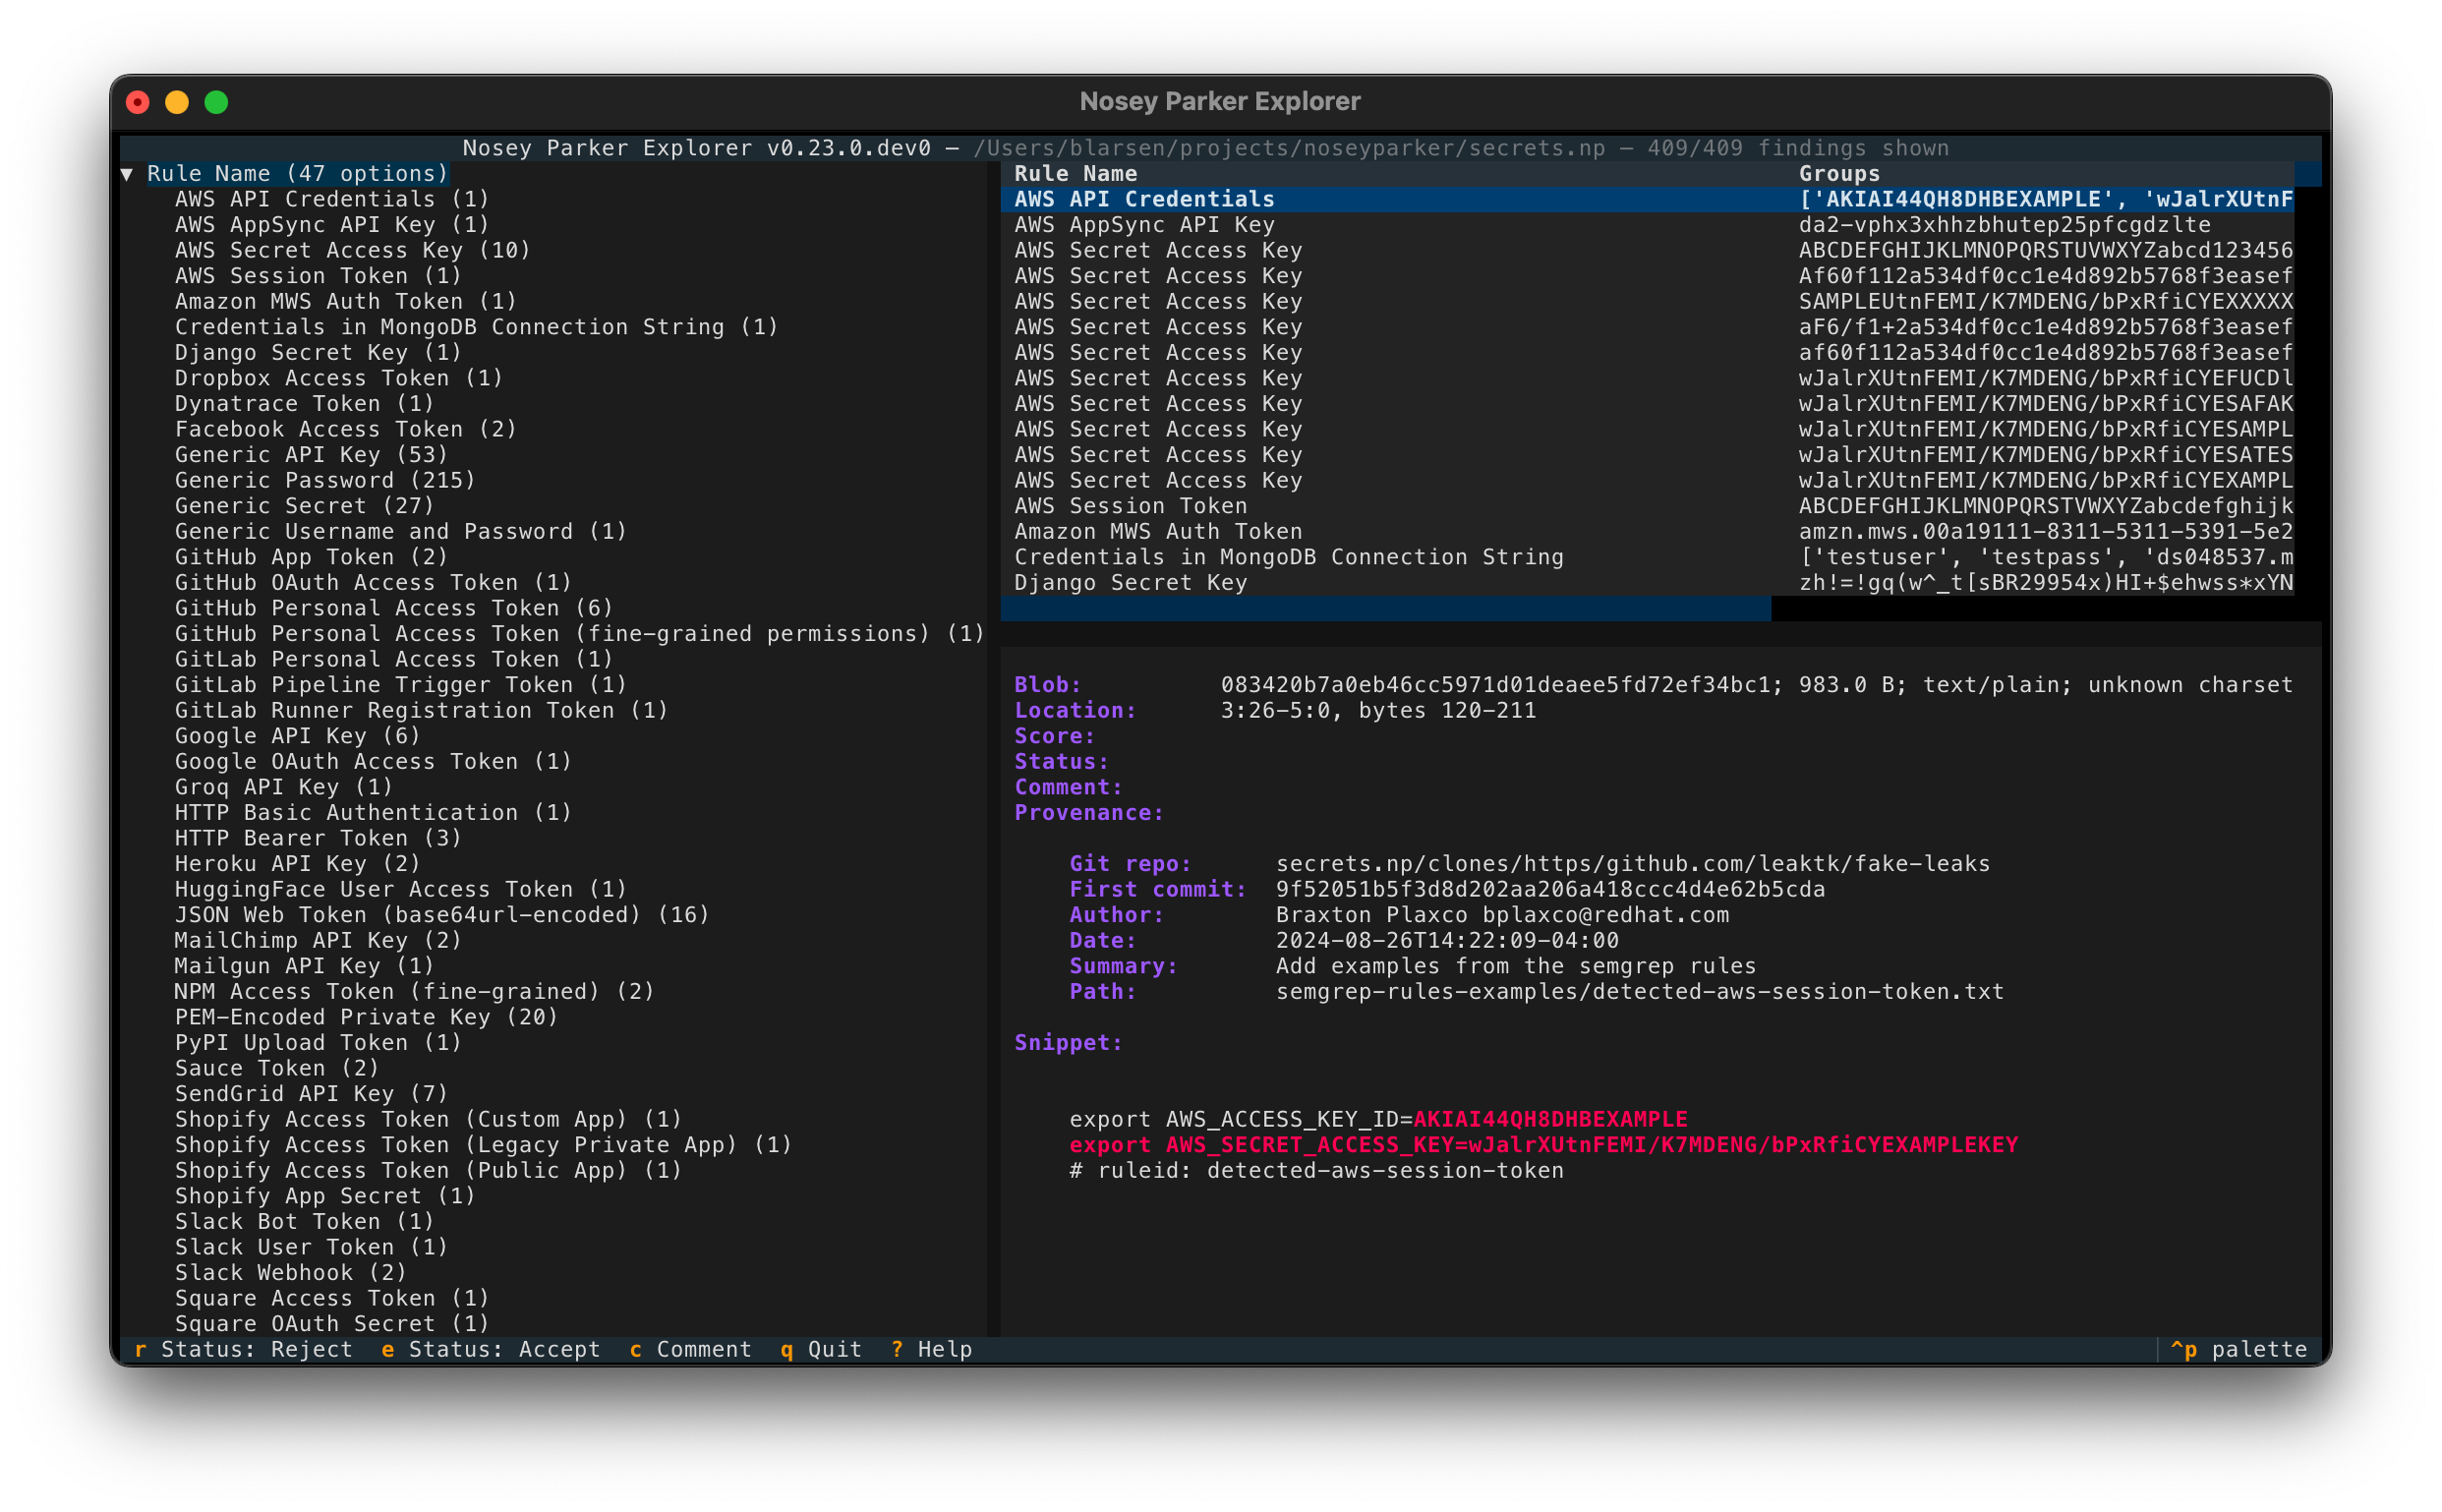
Nosey Parker is a command-line tool that finds secrets and sensitive information in textual data and Git history.

Full automation check for CVE-2025-14847 MonogBleed- Finds origin IP and tests for exploit.

AI-powered SAST scanner that finds auth bypass, IDOR, and logic bugs Semgrep/CodeQL miss. Free GitHub Action. Supports Python, JS/TS, Go, PHP, Ruby.

Tool to scan for secret files on HTTP servers

Open-source security audits for Supabase: a read-only MCP server, a CLI agent and a Claude Skill. Finds RLS misconfigurations, exposed keys and risky…

Zero-dependency, offline CLI scanner that finds fastjson inside JARs and Spring Boot fat-JARs, flags CVE-2026-16723 exposure, and detects shaded…

Automates SQL injection exploitation with SQLMAP, crawls for vulnerabilities, extracts database credentials, finds admin login pages, and cracks…

Burp Suite extension that finds exposed admin panels and login pages of web applications and infrastructure. 1,000+ payloads, OWASP WSTG-CONF-05.

Finds CSP report urls and tests to see if they are vulnerable to log4j

Shodan-powered vulnerability scanner that discovers exposed devices and scans targets for known CVEs and vulnerabilities using dork queries and IP…

Lightweight scanner that detects vulnerable Log4j versions and Log4Shell (CVE-2021-44228) indicators in a filesystem tree.

Claude Code and Codex skill for finding potentially vulnerable Brotli copies and guiding updates for CVE-2026-111497.

403/401 bypass tool: finds HTTP access-control bypasses via path, method, header and raw-request mutations. Baseline diff, auto-calibration,…

find sensitive data leaking from ServiceNow instances.

Runtime vulnerability scanner: finds CVEs in the services actually running on a host and ranks them by network exposure.