
enumy
 luke-goddard/enumy
Linux post exploitation privilege escalation enumeration
penetration-testingpost-exploitationprivilege-escalation+1
luke-goddard/enumyLinux post exploitation privilege escalation enumeration
 im-hanzou/msaper
Automatic Mass Tool for check and exploiting vulnerability in CVE-2023-3076 - MStore API < 3.9.9 - Unauthenticated Privilege Escalation (Mass Add…
 murrez/cve-2026-14281
Unauthenticated privilege escalation in WordPress WAWP (Automation Web Platform) ≤ 4.8.6 via public REST signup and unsanitized wawp_custom_fields →…
 penteraio/vscalation-cve-2021-22015
Scanner for vScalation (CVE-2021-22015) a Local Privilege Escalation in VMWare vCenter
 johenlastgen-jlg/cve-2025-6325_cve-2025-6327
Python PoC validating CVE-2025-6325 unauthenticated privilege escalation and CVE-2025-6327 arbitrary file upload RCE in King Addons for Elementor <=…
 codiobert/pwnkit-scanner
Scans Linux systems for the Polkit privilege escalation vulnerability (CVE-2021-4034) and provides mitigation guidance.
 rxerium/cve-2024-32444
An unauthenticated privilege escalation problem tracked as CVE-2024-32444 (CVSS score: 9.8).
 rootharpy/cve-2025-39459-nuclei-template
The Real Estate 7 WordPress theme is vulnerable to Privilege Escalation in all versions up to, and including, 3.5.2. This makes it possible for…
 thelsa/harbor-give-me-admin
harbor(<1.7.6/1.8.3) privilege escalation (CVE-2019-16097)
 mbadanoiu/cve-2020-8248
CVE-2020-8248: Privilege Escalation via Zip Wildcard Exploit in Pulse Secure VPN Linux Client
 langz337/cve-2026-14281
Mass scanner and single-target exploit for CVE-2026-14281, an unauthenticated privilege escalation in the WordPress Automation Web Platform plugin…
 nxploited/cve-2026-96451
WordPress Ultimate Member plugin <= 2.13.1 - Privilege Escalation vulnerability
 0xcyp1337/cve-2026-19598-
Exploits CVE-2026-19598 in WordPress Pods plugin to create admin accounts or overwrite passwords via unauthenticated AJAX request, with mass scanning…
 rxerium/cve-2025-41244
Detection for CVE-2025-41244
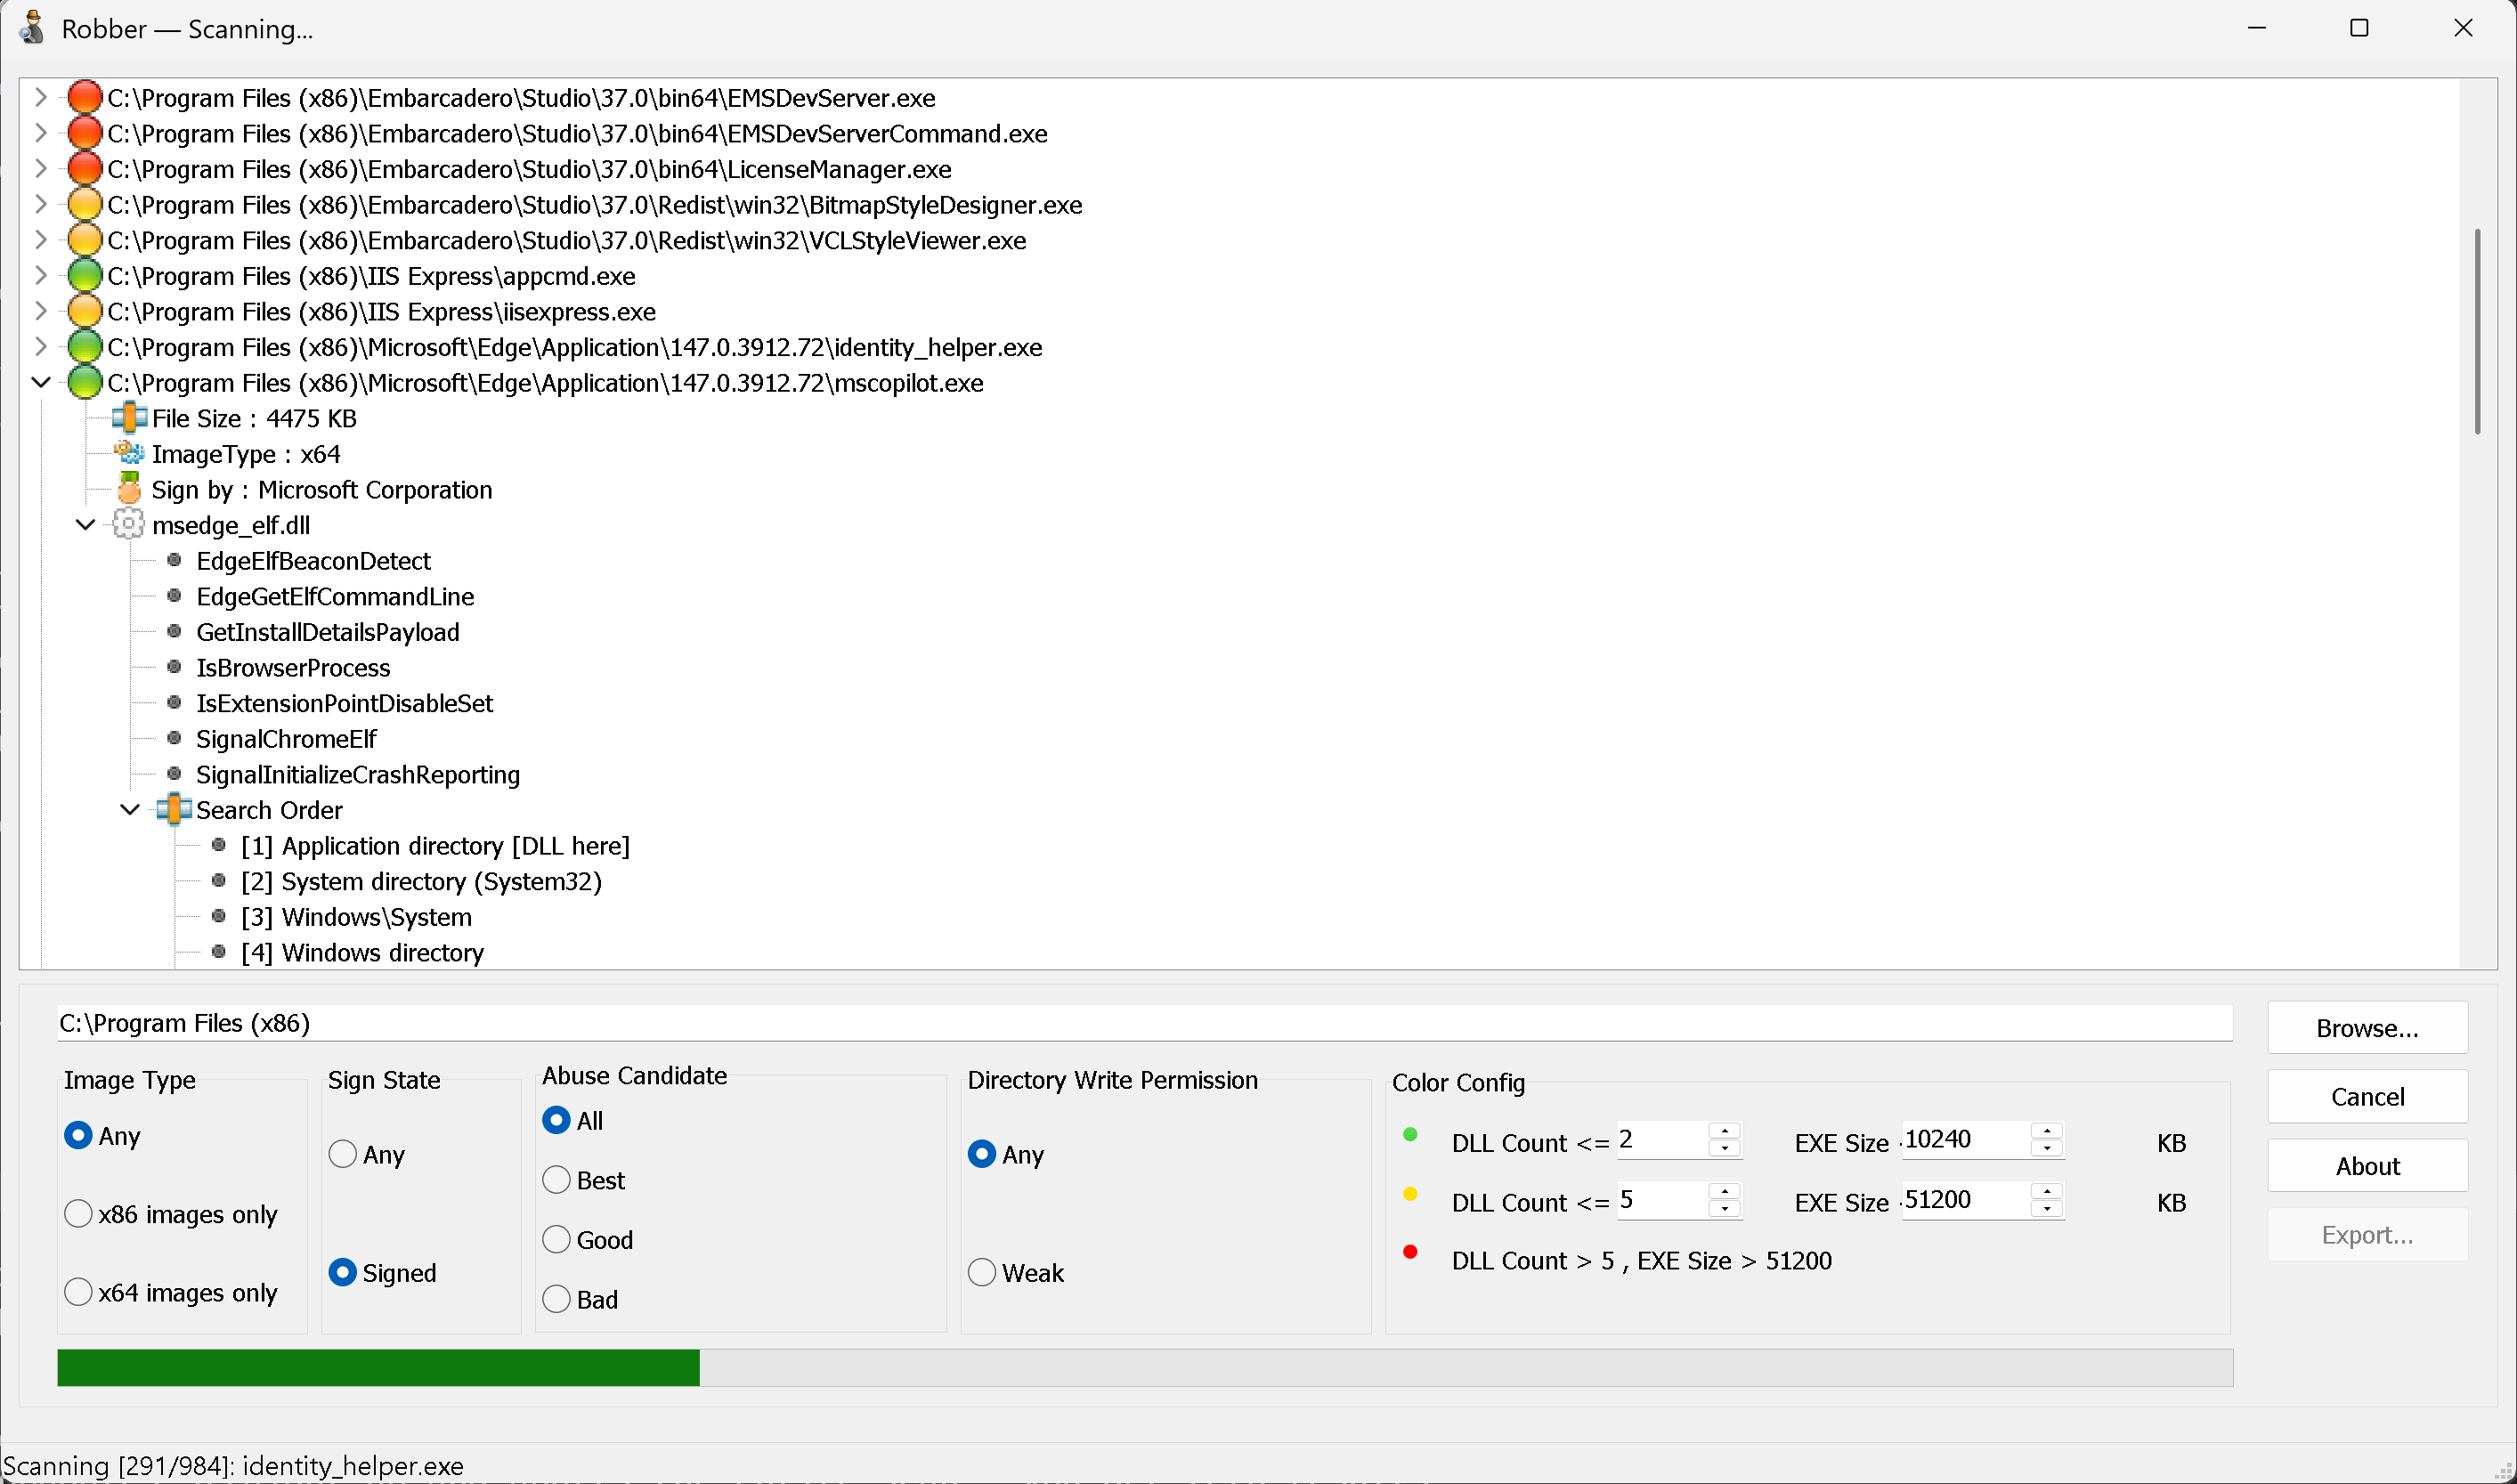 mojtabatajik/robber
Robber is open source tool for finding executables prone to DLL hijacking
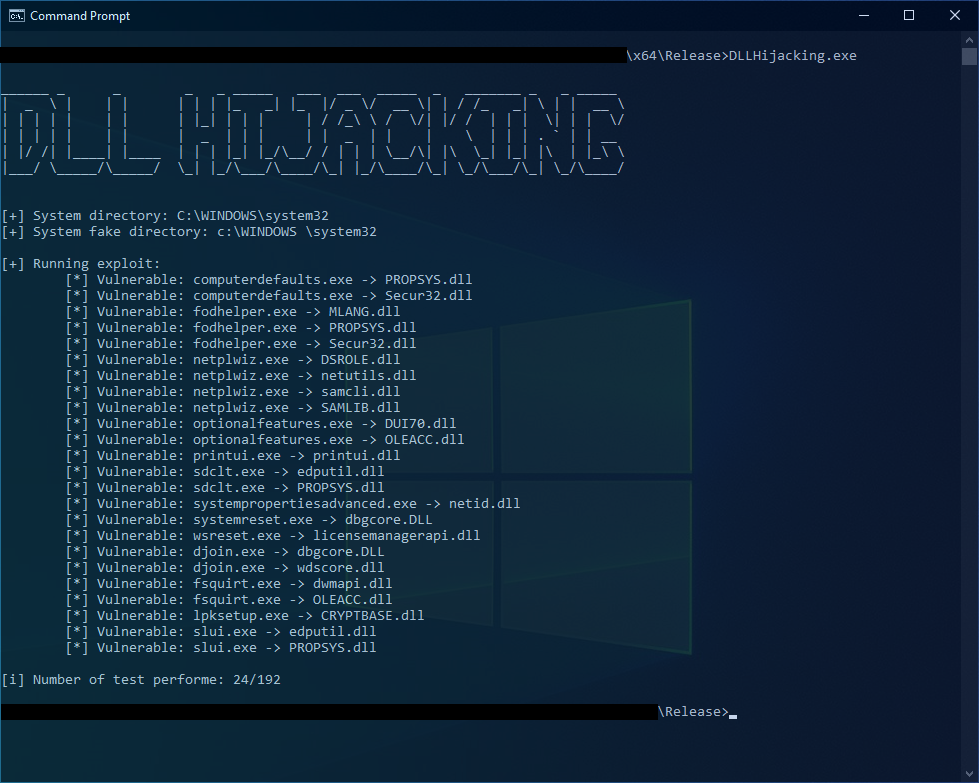 secuproject/dllhijackingscanner
This is a PoC for bypassing UAC using DLL hijacking and abusing the "Trusted Directories" verification.
 evilashz/pigadvulnscanner
检测域内常见一把梭漏洞,包括:NoPac、ZeroLogon、CVE-2022-26923、PrintNightMare
 joaovarelas/cve-2021-30357_checkpoint_snx_vpn_poc
Proof-of-Concept for privileged file read through CheckPoint SNX VPN Linux Client