
Pegasus-Pentest-Arsenal
 sobri3195/pegasus-pentest-arsenal
A comprehensive web application security testing toolkit that combines 10 powerful penetration testing features into one tool.
api-security-testingctfeducation+9
sobri3195/pegasus-pentest-arsenalA comprehensive web application security testing toolkit that combines 10 powerful penetration testing features into one tool.
 cspf-founder/api-scanner-docker
Automated API security testing tool that scans REST and SOAP APIs for vulnerabilities using OpenAPI/Swagger specs and WSDL files. Deploys a full …
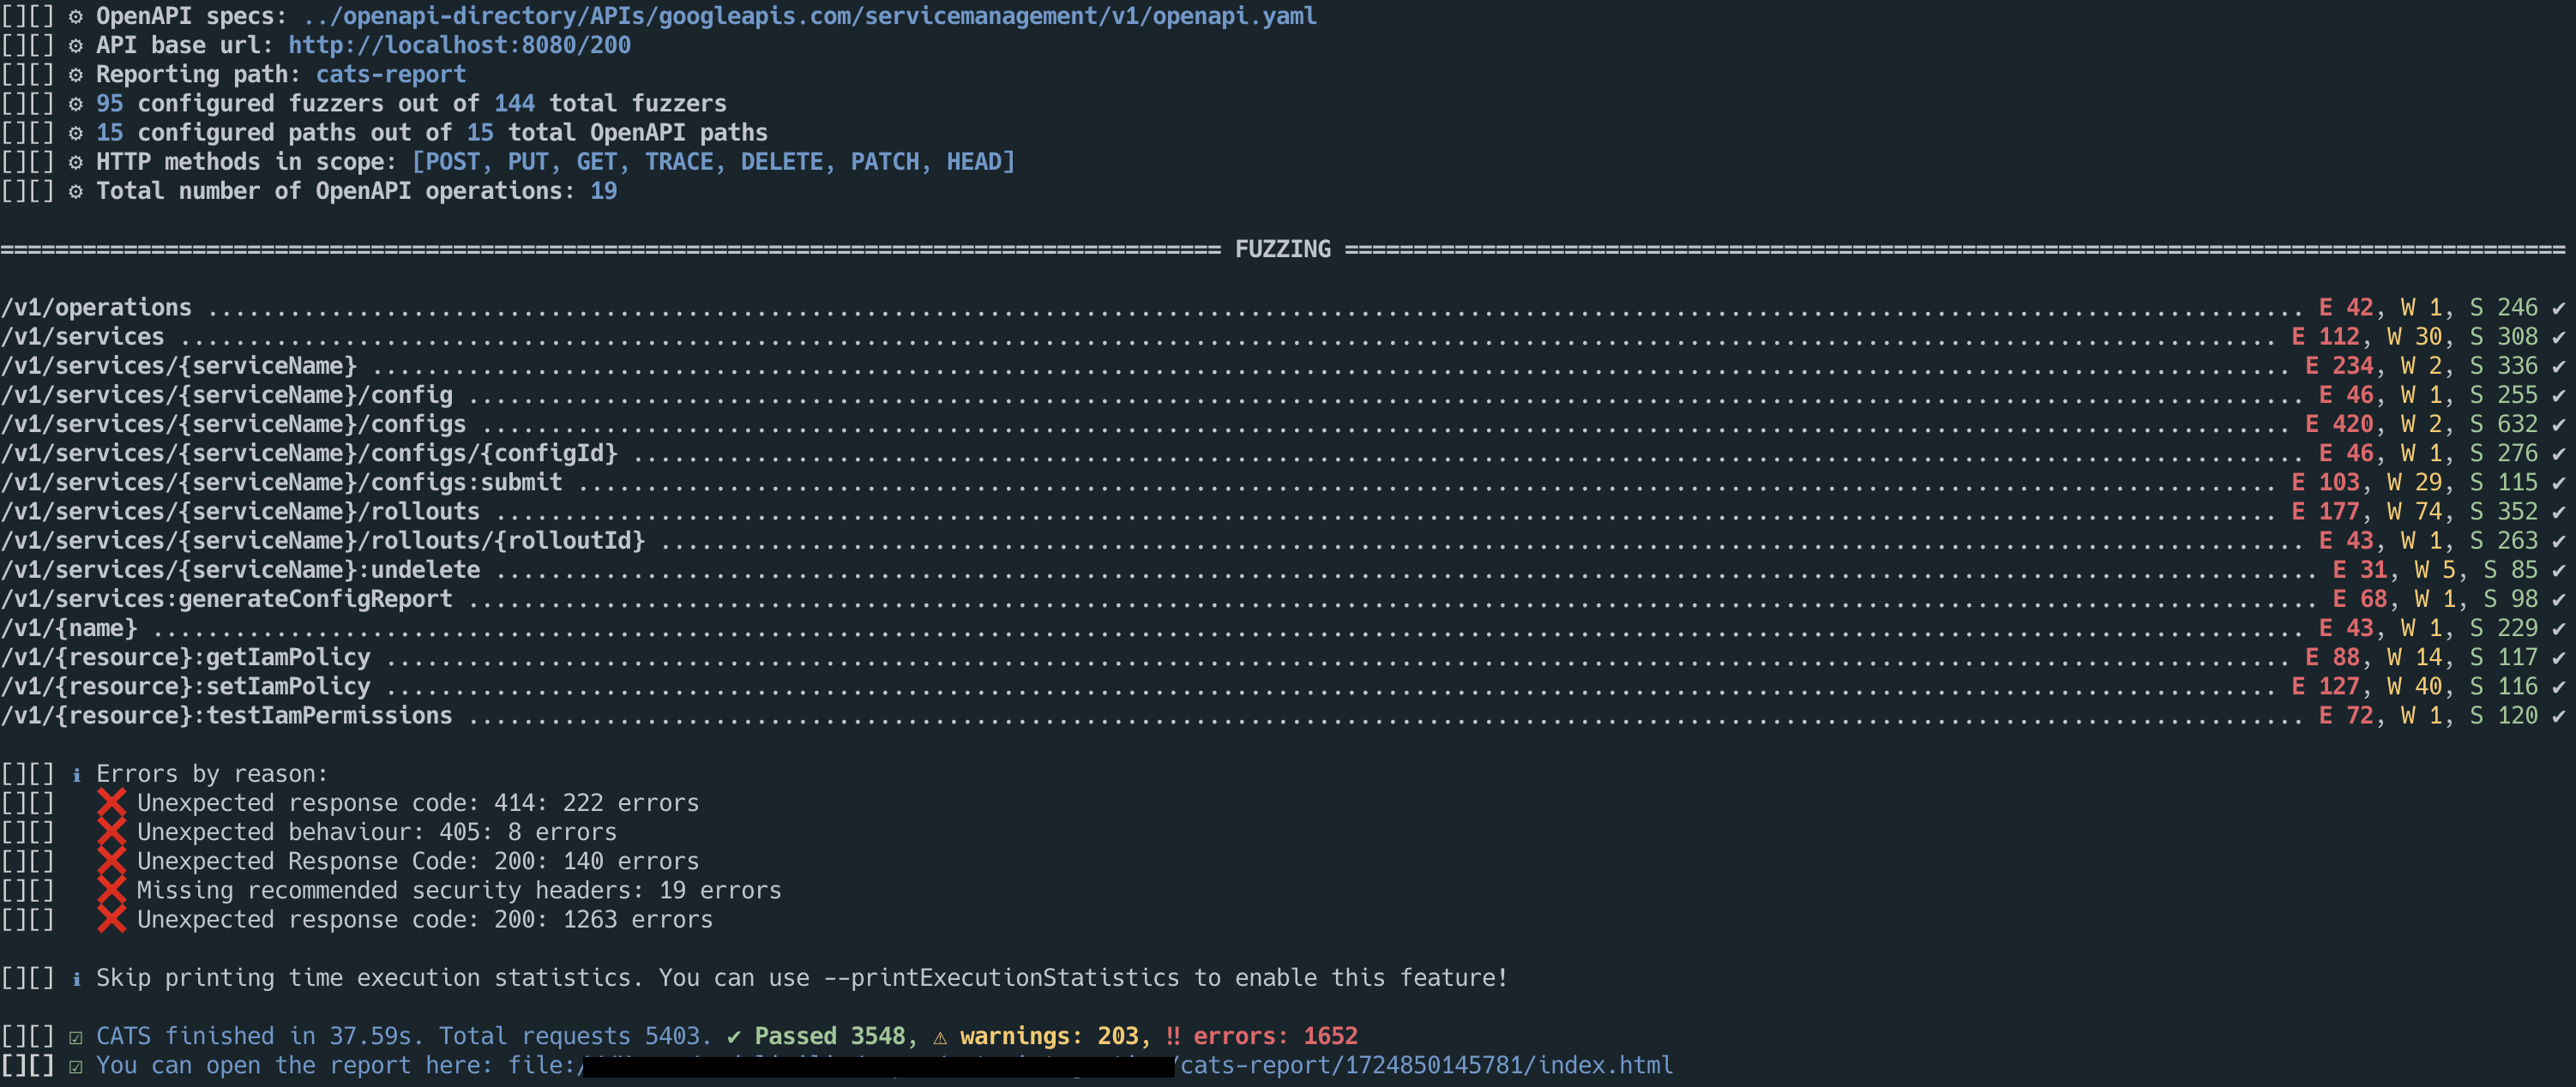 endava/cats
Automated REST API fuzzer and negative testing tool for OpenAPI endpoints. Generates, runs, and reports thousands of self-healing tests with no…
 microsoft/restler-fuzzer
RESTler is the first stateful REST API fuzzing tool for automatically testing cloud services through their REST APIs and finding security and…
 nemesida-waf/waf-bypass
Automated WAF security testing tool that detects false positives and false negatives using 15+ payload categories including SQLi, XSS, RCE, and…
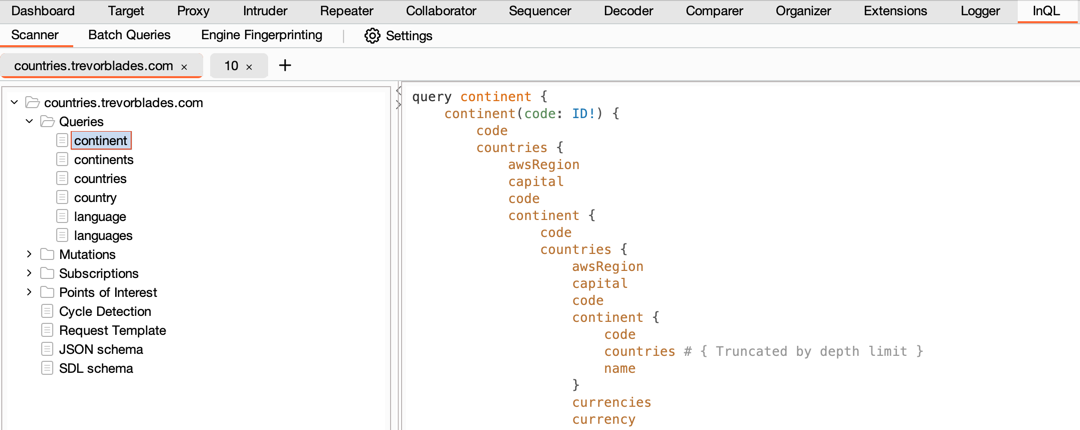 doyensec/inql
InQL is a robust, open-source Burp Suite extension for advanced GraphQL testing, offering intuitive vulnerability detection, customizable scans, and…
 bishopfox/sj
A tool for auditing endpoints defined in exposed (Swagger/OpenAPI) definition files.
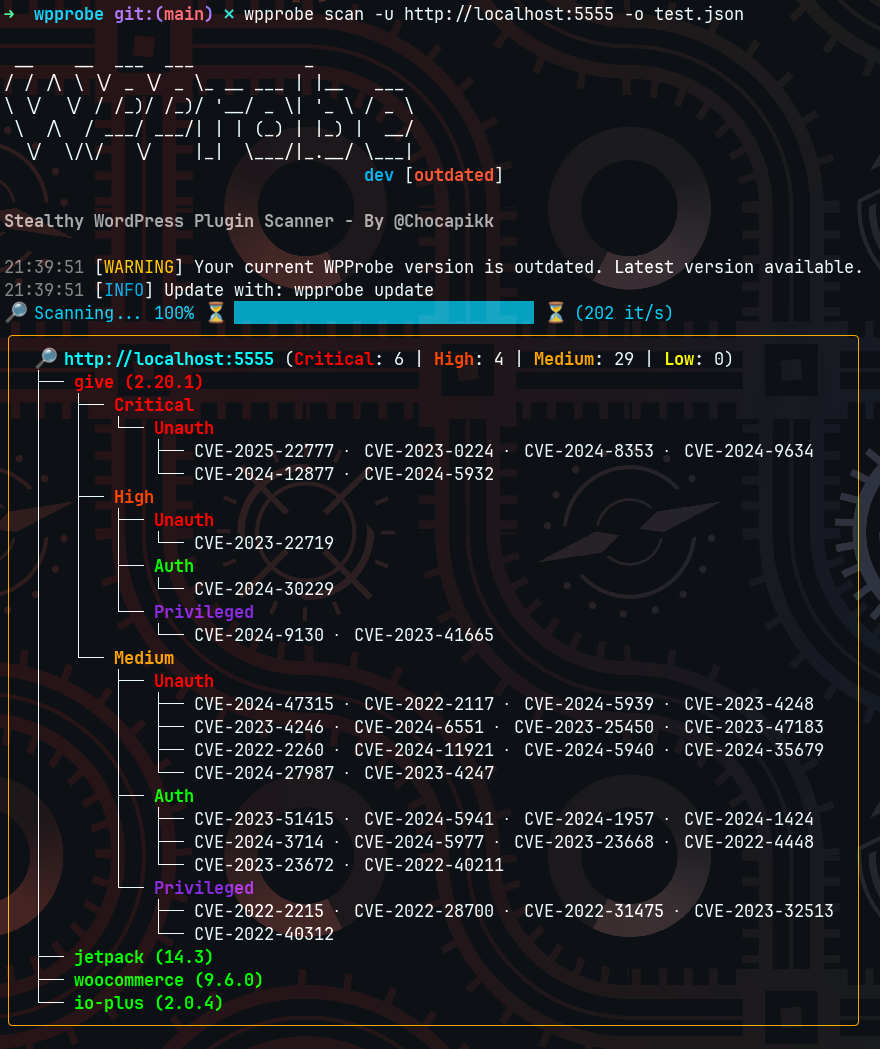 chocapikk/wpprobe
A fast WordPress plugin enumeration tool
 0x4d31/burpa
Burp-Automator: A Burp Suite Automation Tool with Slack Integration. It can be used with Jenkins and Selenium to automate Dynamic Application…
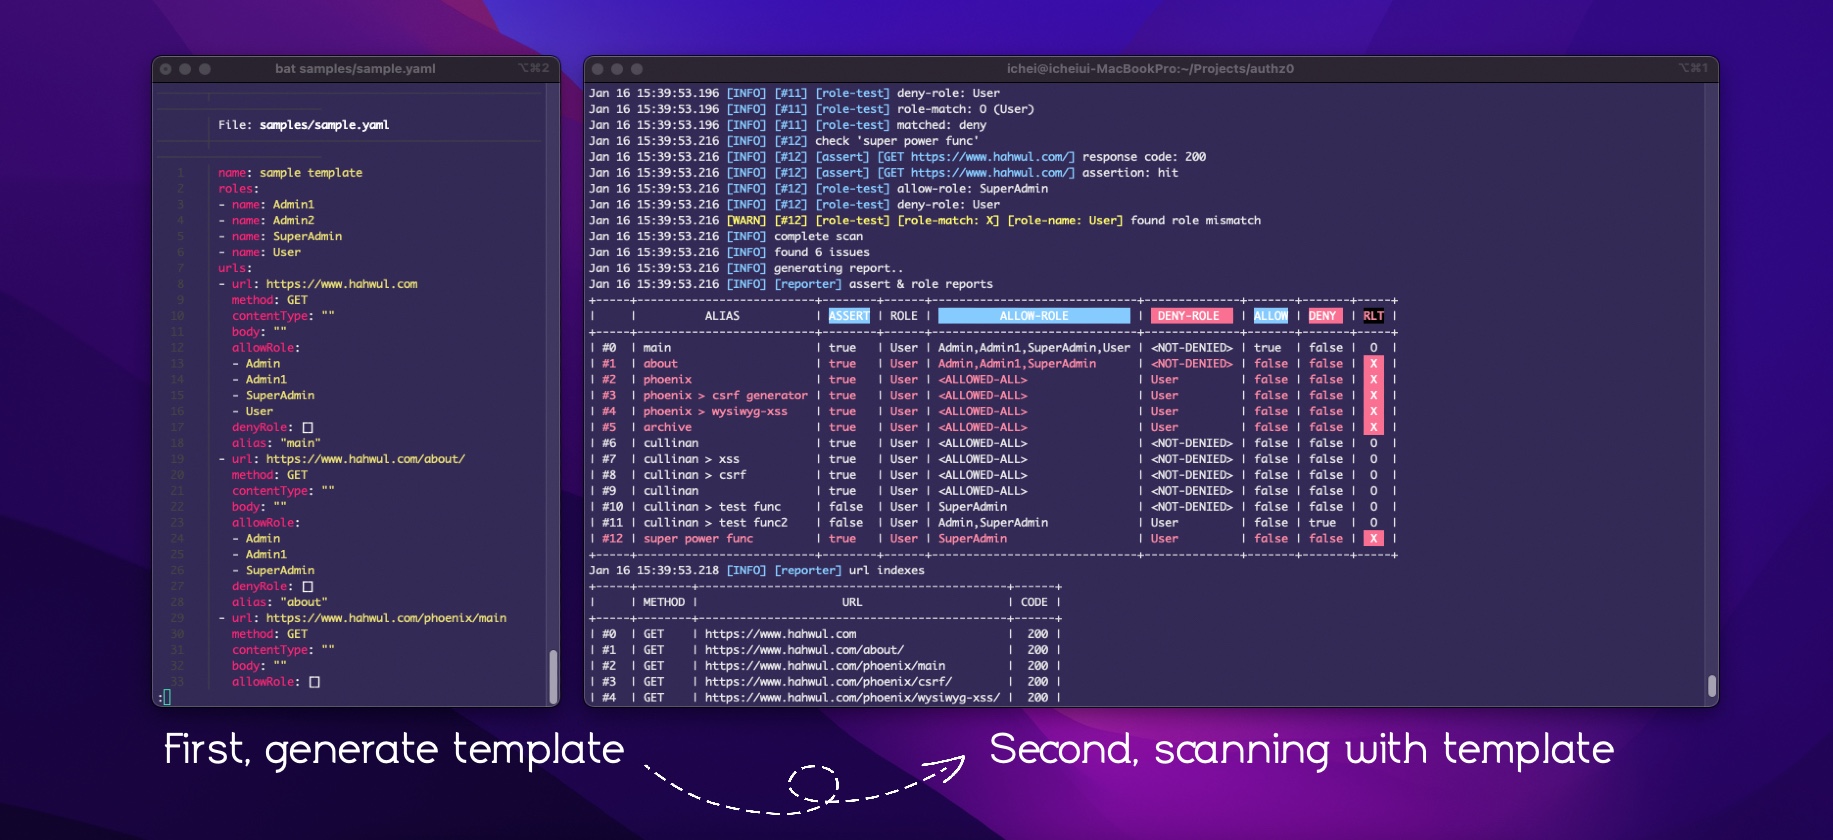 hahwul/authz0
Automated authorization testing tool that detects unauthorized access by scanning URLs with role-based credentials using YAML templates.
 yalcinyolalan/wssat
WEB SERVICE SECURITY ASSESSMENT TOOL
 sech0us3/waf-checker
Automated WAF assessment tool that detects firewall vendors, tests 19 attack categories with advanced evasion payloads, and provides color-coded…
 danialhalo/acuautomate
Unofficial Acunetix CLI tool for automated pentesting and bug hunting across large scopes.
 bogdanticu88/ratrace
A lightweight CLI tool for systematically detecting and exploiting race conditions in web applications, APIs, and modern services.
 marcin-wolak/simplermidiscoverer
Simple JMX RMI scanning tool
 cropnet/ni8mare
Comprehensive vulnerability detection tool for n8n workflow automation instances. Detects the critical CVE-2026-21858 vulnerability (CVSS 10.0)…
 amnnrth/cve-2025-34291_cors_security_scanner
A lightweight Python-based security assessment tool for detecting dangerous Cross-Origin Resource Sharing (CORS) misconfigurations - CVE-2025-34291.
 vmware-archive/burp-rest-api
REST/JSON API to the Burp Suite security tool.