

dawnscanner
 thesp0nge/dawnscanner
Dawn is a static analysis security scanner for ruby written web applications. It supports Sinatra, Padrino and Ruby on Rails frameworks.
code-analysisstatic-analysisvulnerability-scanners+1
749
thesp0nge/dawnscannerDawn is a static analysis security scanner for ruby written web applications. It supports Sinatra, Padrino and Ruby on Rails frameworks.
 tstillz/webshell-analyzer
Web shell scanner and analyzer.
 hristiy4n/bom-view
Static web application for viewing SBOMs and performing on-demand vulnerability scanning with osv.dev. Easily deployable to GitHub/GitLab Pages.
 honeyb33z/cve-2020-11023-scanner
Static analysis scanner for CVE-2020-11023 XSS vulnerabilities in JavaScript. Detects vulnerable jQuery versions and dangerous DOM manipulation…
 retirejs/retire.js
scanner detecting the use of JavaScript libraries with known vulnerabilities. Can also generate an SBOM of the libraries it finds.
 sudo-wp/sudowp-dropzone-elementor
Secure fork of Startklar Elementor Addons. Patched CVE-2024-5153 & File Upload vulnerabilities.
 hillu/local-log4j-vuln-scanner
[Moved to Codeberg] Simple local scanner for vulnerable log4j instances
 presidentbeef/brakeman
A static analysis security vulnerability scanner for Ruby on Rails applications
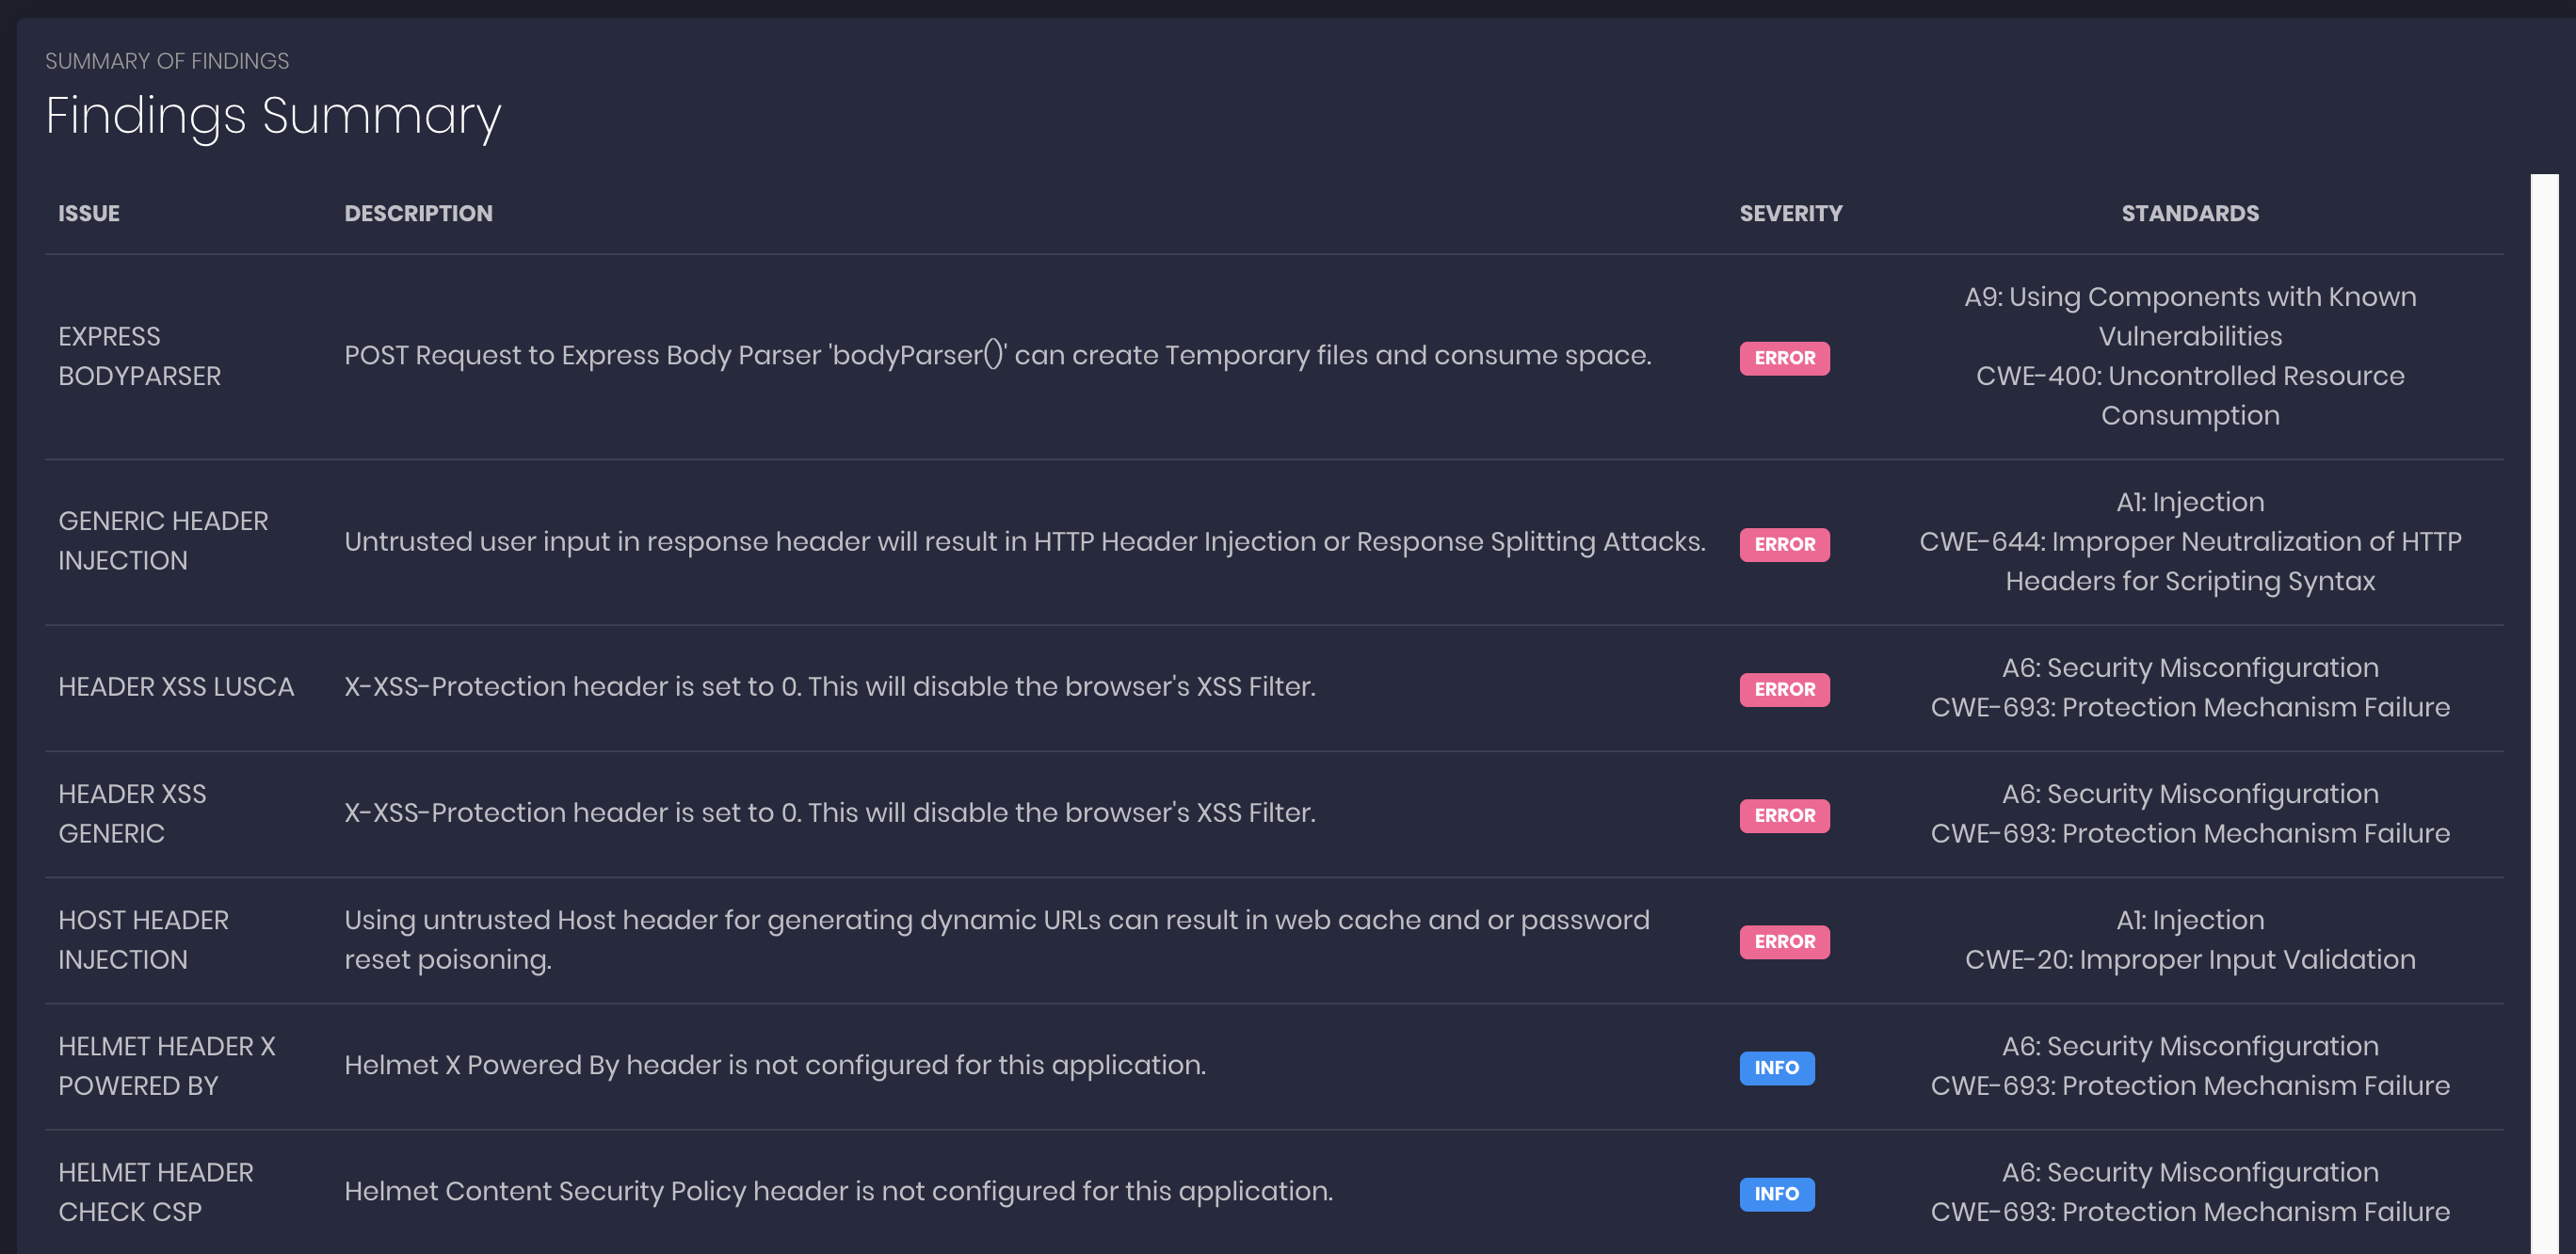 ajinabraham/nodejsscan
nodejsscan is a static security code scanner for Node.js applications.
 nccgroup/sobelow
Security-focused static analysis for the Phoenix Framework
 ajinabraham/njsscan
Semantic-aware SAST scanner for Node.js applications that detects insecure code patterns using libsast pattern matching and semgrep syntax-aware…
 nbs-system/php-malware-finder
YARA-based scanner that detects obfuscated PHP malware and webshells using semantic pattern matching instead of file hashes, with a whitelist system…
 fox-it/log4j-finder
Find vulnerable Log4j2 versions on disk and also inside Java Archive Files (Log4Shell CVE-2021-44228, CVE-2021-45046, CVE-2021-45105)
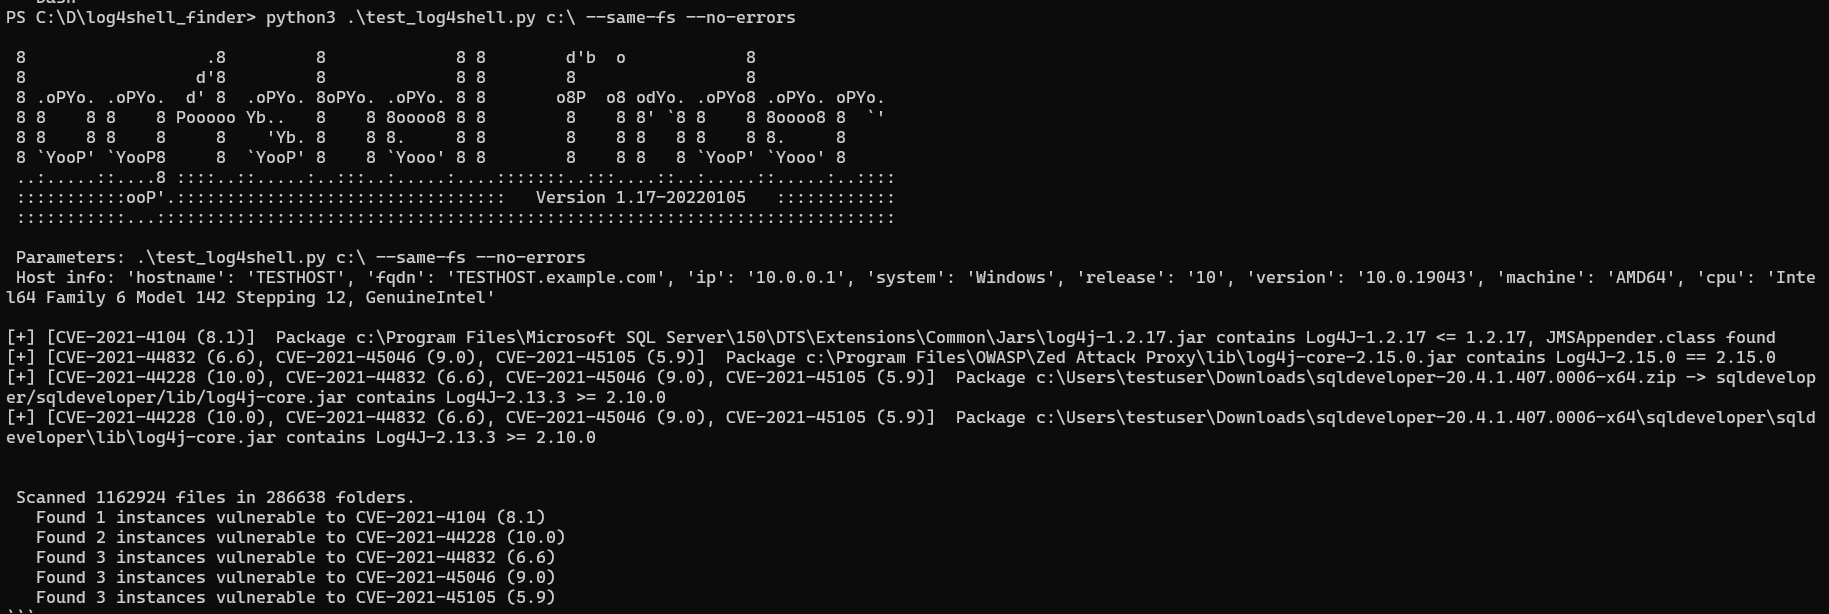 hynekpetrak/log4shell-finder
Fastest filesystem scanner for log4shell (CVE-2021-44228, CVE-2021-45046) and other vulnerable (CVE-2017-5645, CVE-2019-17571, CVE-2022-23305,…
 coinbase/salus
We would like to request that all contributors please clone a *fresh copy* of this repository since the September 21st maintenance.
 theori-io/reactguard
ReactGuard provides framework- and vulnerability-detection tooling for CVE-2025-55182 (React2Shell)
 abtonc/next-cve-2025-66478
Scans local projects for CVE-2025-66478 vulnerability and reports affected instances without fixing them.