
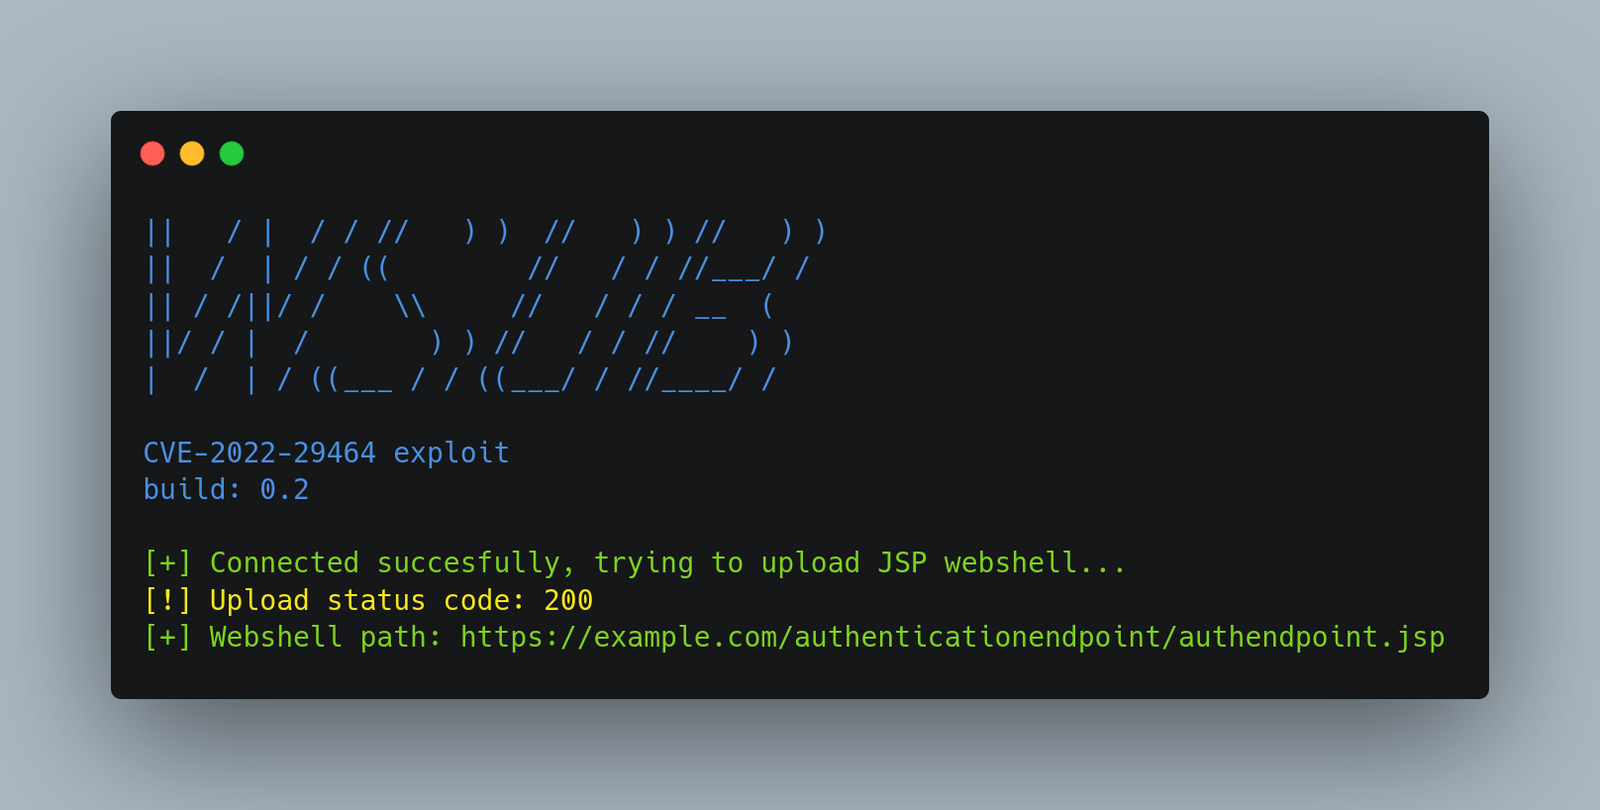
WSOB
 dsssssssm/wsob
Python exploit tool for CVE-2022-29464, enabling unrestricted file upload and remote code execution on vulnerable WSO2 products via directory…
exploitationpenetration-testingred-teaming+2
26
dsssssssm/wsobPython exploit tool for CVE-2022-29464, enabling unrestricted file upload and remote code execution on vulnerable WSO2 products via directory…
 mauricelambert/cve-2021-41773
Multi-language exploit and detection scripts for CVE-2021-41773, enabling remote code execution and local file disclosure on vulnerable Apache…
 kulik-labs-development/ghost-cms-code-injection-audit-cve-2026-26980
Outdated Ghost CMS websites that have fallen become compromised from CVE-2026-26980 can suffer from spam code injection to pages. Use this to mass…
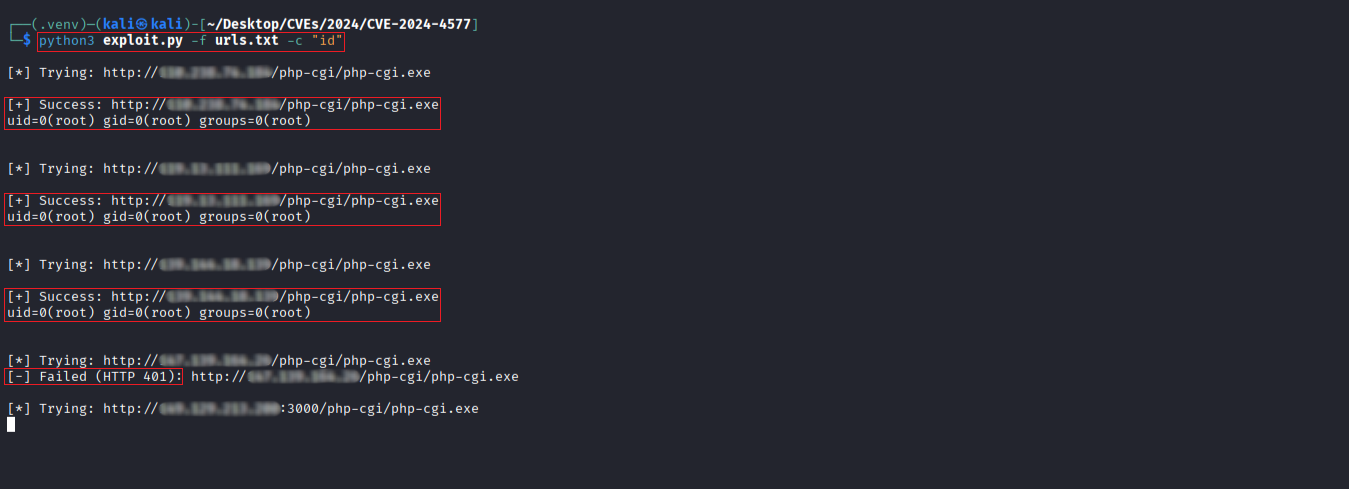 r0otk3r/cve-2024-4577
Scanner and exploit tool for CVE-2024-4577, a PHP CGI argument injection vulnerability enabling remote code execution on Windows systems. Includes…
 zwxxb/cve-2023-21887
Scans a list of URLs for CVE-2023-46805 and exploits CVE-2023-21887 to achieve remote code execution on Ivanti products.
 bimboxh4/cve-2025-66039_cve-2025-61675_cve-2025-61678_reepbx
This vulnerability allows both authenticated and unauthenticated remote attackers to execute remote code on vulnerable FreePBX instances. These…
 thesp0nge/dawnscanner
Dawn is a static analysis security scanner for ruby written web applications. It supports Sinatra, Padrino and Ruby on Rails frameworks.
 shirkdog/pulledpork
Pulled Pork for Snort and Suricata rule management (from Google code)
 mhaskar/bughound
Static code analysis tool based on Elasticsearch
 adityaks/melee
Python-based tool to detect ransomware infections and malicious code in MySQL instances. Performs reconnaissance, user enumeration, and deep scans…
 wgetnz/cve-2024-3094-check
Shell script to detect CVE-2024-3094 (xz-utils backdoor) on Linux and macOS systems, with automated check and fix instructions.
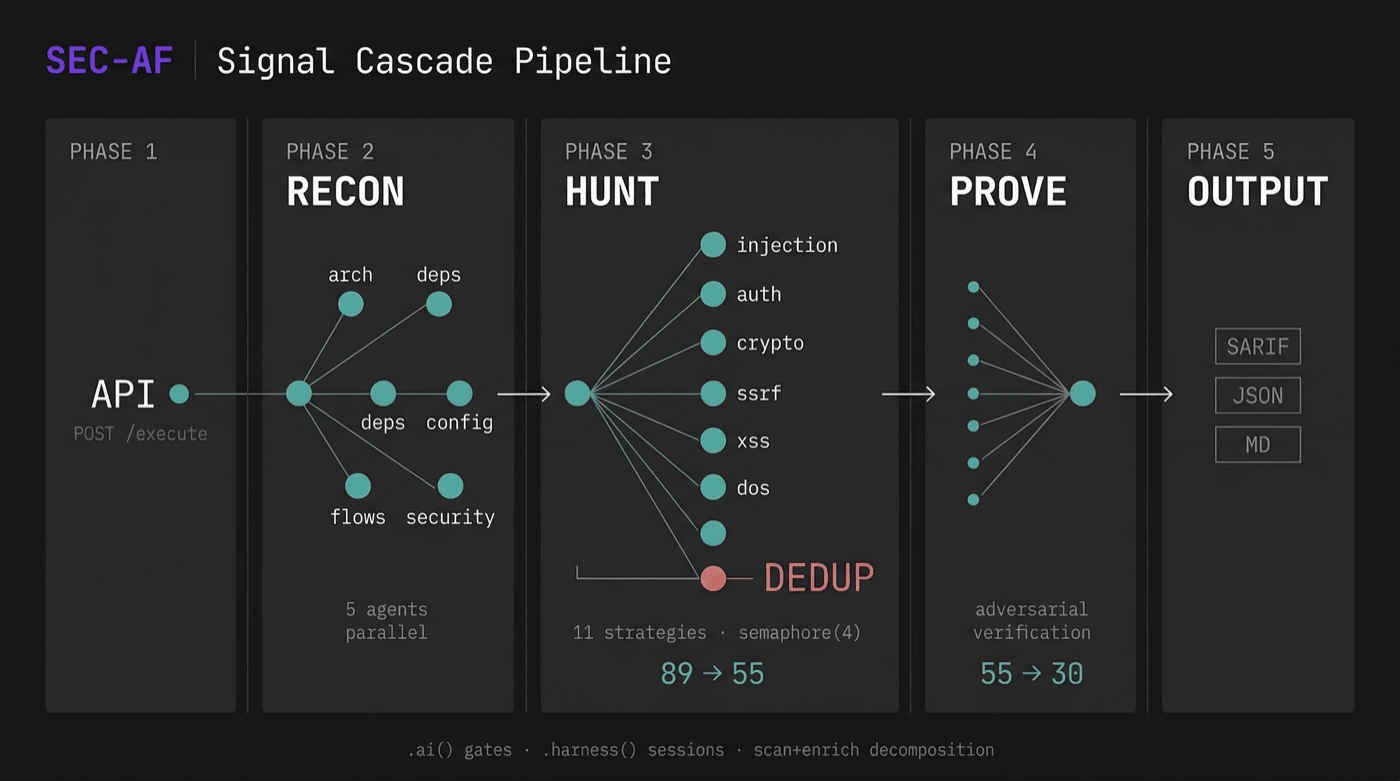 agent-field/sec-af
AI-native code security auditor on AgentField that proves exploitability with verdicts, traces, and actionable evidence.
 mantvmass/react2shell
A CLI tool that exploits vulnerabilities in React Server Components and Server Actions (CVE-2025-55182, CVE-2025-66478) to achieve remote code…
 e11i0t4lders0n/cve-2023-36845
Shell-based scanner for CVE-2023-36845, an unauthenticated remote code execution vulnerability in Juniper J-Web, enabling environment variable…
 chenqin231/cve-2026-42945
Local risk assessment script for CVE-2026-42945 (nginx-rift). Checks version, vulnerable rewrite+set config, ASLR status, and compile hardening to…
 0xsj/cve-2025-55182
Proof-of-concept scanner for CVE-2025-55182, an unauthenticated RCE in React Server Components. Supports batch scanning, JSON/CSV export, and…
 shield-cyber/react2shell-scanner
Scanner to detect the presence of CVE-2025-55182 & CVE-2025-66478 on targeted web services.
 node9-ai/node9-proxy
Access control for AI agents. Set what Claude Code, Codex, Gemini, Cursor and any MCP server are allowed to do, review risky actions before they run,…