
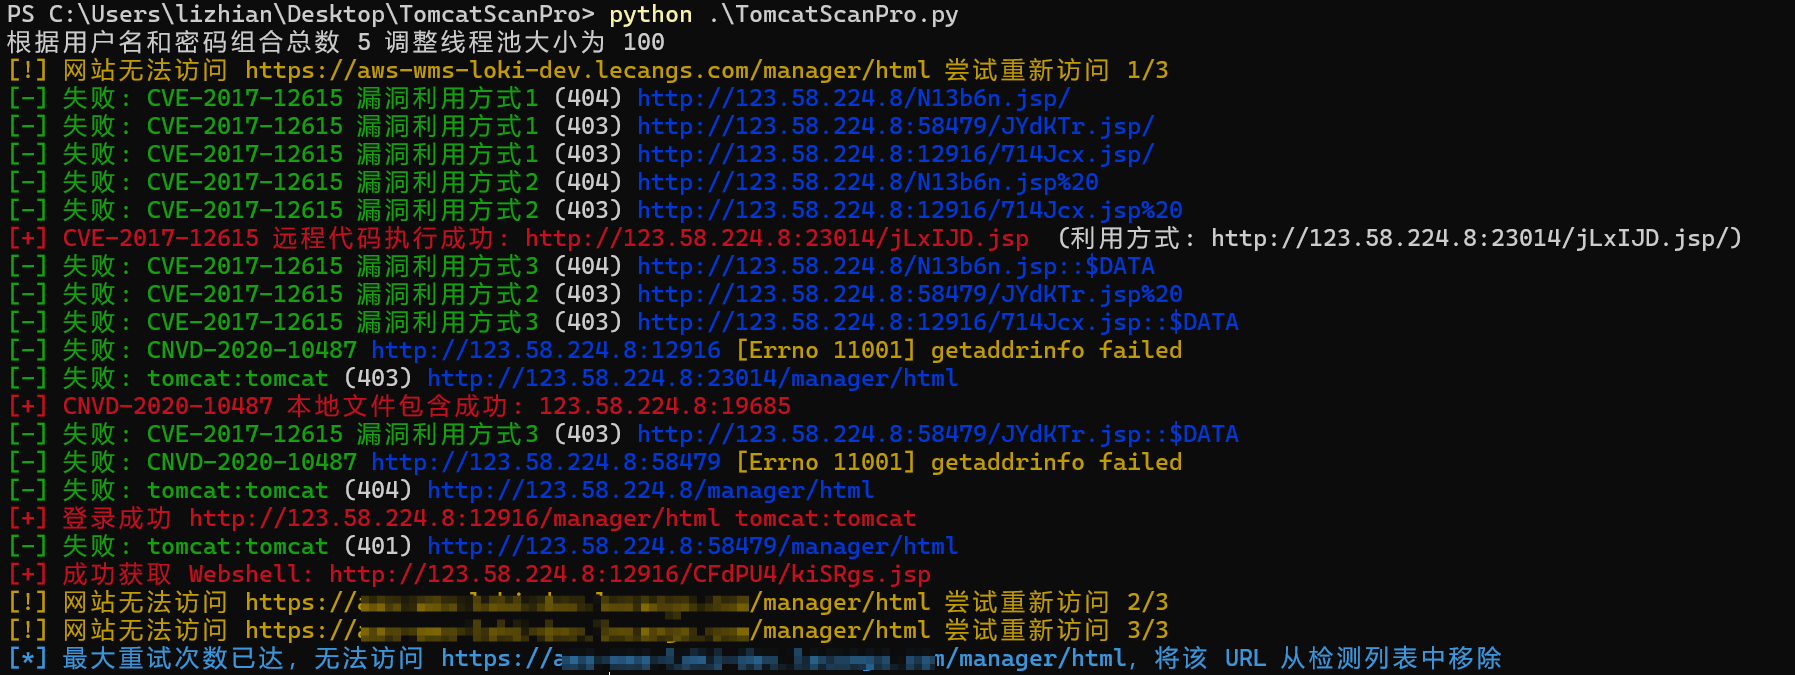
TomcatScanPro
 lizhianyuguangming/tomcatscanpro
tomcat自动化漏洞扫描利用工具,支持批量弱口令检测、后台部署war包getshell、CVE-2017-12615 文件上传、CVE-2020-1938/CNVD-2020-10487 文件包含
exploitationpassword-attackspayload-generation+3
295
lizhianyuguangming/tomcatscanprotomcat自动化漏洞扫描利用工具,支持批量弱口令检测、后台部署war包getshell、CVE-2017-12615 文件上传、CVE-2020-1938/CNVD-2020-10487 文件包含

 esmog/nodexp
NodeXP - A Server Side Javascript Injection tool capable of detecting and exploiting Node.js vulnerabilities
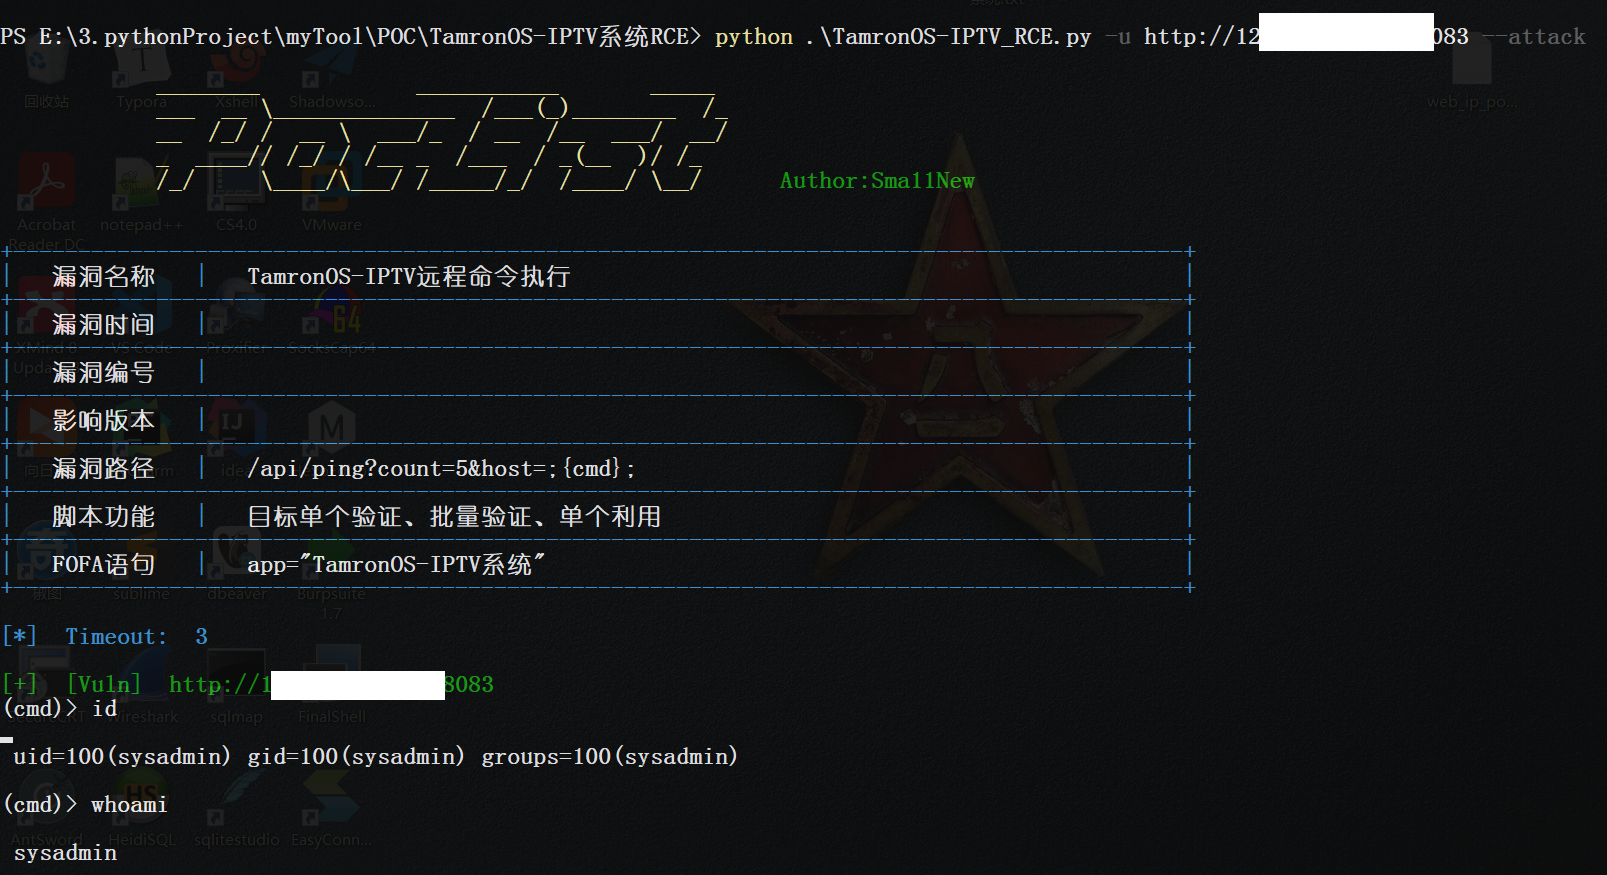 sma11new/poclist
漏洞POC、EXP合集,持续更新。Apache Druid-任意文件读取(CVE-2021-36749)、ConfluenceRCE(CVE-2021-26084)、ZeroShell防火墙RCE(CVE-2019-12725)、ApacheSolr任意文件读取、蓝凌OA任意文件读取、phpStud…
 giterlizzi/nmap-log4shell
Nmap NSE script for detecting Apache Log4j RCE (CVE-2021-44228) by injecting JNDI exploit payloads via HTTP headers or TCP/UDP sockets across…
 assetnote/cpanel2shell-scanner
High fidelity scanner for CVE-2026-41940 (cPanel & WHM authentication bypass)
 hackersatyamrastogi/react2shell-ultimate
React2Shell Ultimate - The most comprehensive CVE-2025-66478 Scanner for Next.js RSC RCE vulnerability. Multi-mode detection, WAF bypass, local…
 bigsizeme/log4j-check
log4J burp被扫插件、CVE-2021-44228、支持dnclog.cn和burp内置DNS、可配合JNDIExploit生成payload
 puzzlepeaches/log4jhorizon
Exploiting CVE-2021-44228 in VMWare Horizon for remote code execution and more.
 watchtowrlabs/watchtowr-vs-fortiweb-cve-2025-25257
Detection artifact generator for FortiWeb CVE-2025-25257, exploiting unauthenticated SQL injection to achieve remote code execution via hex-encoded…
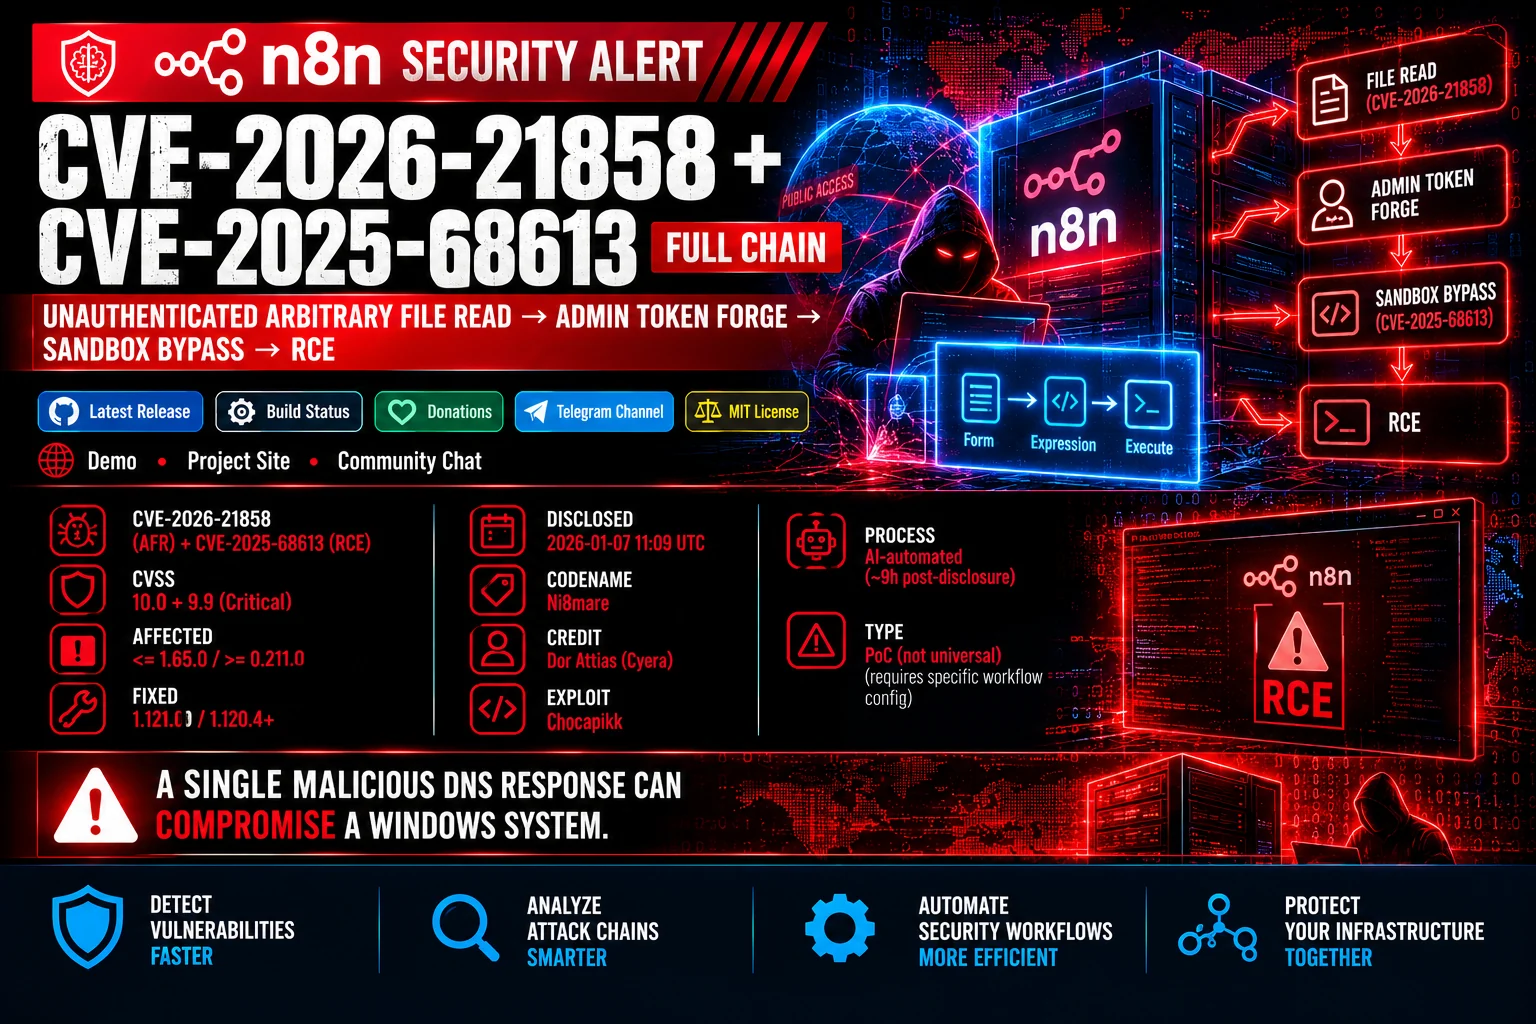 zerodayevil/cve-2026-21858-n8n-fullchain
🛡️ Official AI Security Tool module for CVE-2026-21858 + CVE-2025-68613 (n8n "Ni8mare" Unauthenticated Arbitrary File Read & Expression Injection…
 rsatan/next.js-exploit-tool
Next.js-Exploit-Tool 图形化综合利用工具,基于 Go 开发,一款针对 CVE-2025-55182 的独立安全评估工具。
 gh1mau/masta-cve-2026-48907
Single-file Python scanner for CVE-2026-48907 (Joomla JCE Editor RCE). Detects Joomla/JCE, performs intrusive math-verified payload test, supports…
 christbowel/cve-2024-25600_nuclei-template
Nuclei template and information about the POC for CVE-2024-25600
 hazcod/cve-2025-53770
Go-based scanner that detects SharePoint CVE-2025-53770 RCE vulnerability by injecting a harmless marker into the ToolBox widget and verifying its…
 gensecaihq/cve-2024-3094-vulnerability-checker-fixer
Shell script and Ansible playbook to detect and remediate CVE-2024-3094 in xz-utils by checking package versions, upgrading or downgrading to a…
 watchtowrlabs/watchtowr-vs-freepbx-cve-2025-57819
Python-based detection artifact generator for CVE-2025-57819, exploiting FreePBX pre-auth RCE via SQL injection and auth bypass to deploy webshells…
 turtlesec-software/crlf-desyncs
Nuclei templates and exploit resources for CRLF based desync attacks