owtf
 owtf/owtf
Modular penetration testing framework integrating multiple tools for automated web application security assessment, aligned with OWASP Testing Guide,…
exploit-frameworkspenetration-testingpenetration-testing-frameworks+2
1.9k
owtf/owtfModular penetration testing framework integrating multiple tools for automated web application security assessment, aligned with OWASP Testing Guide,…
 01rabbit/pakuri
Semi-automated penetration testing framework with TUI, integrating Nmap, OpenVAS, Metasploit, and Faraday for streamlined information gathering,…
 abdirisaq-ali-aynab/vulnerability-assessment
Professional cybersecurity assessment demonstrating vulnerability identification, CVSS severity scoring, MITRE ATT&CK framework application, and…
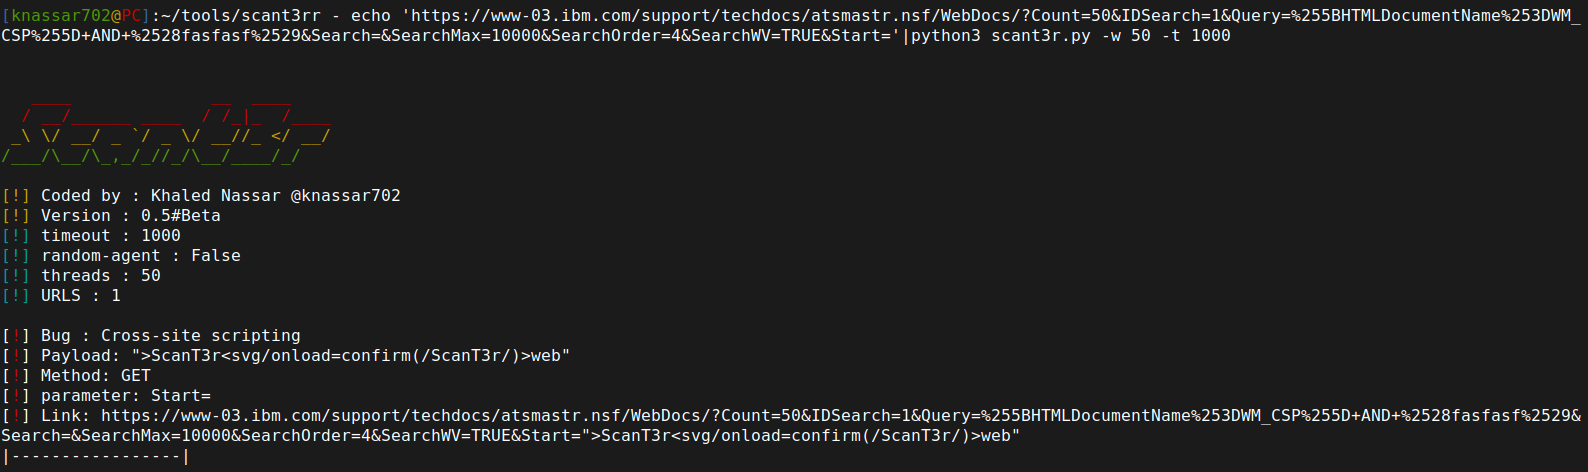 mindpatch/scant3r
Module-based web vulnerability scanner and bug bounty automation framework with built-in XSS, SSTI, SSRF, and Firebase detection engines. Designed to…
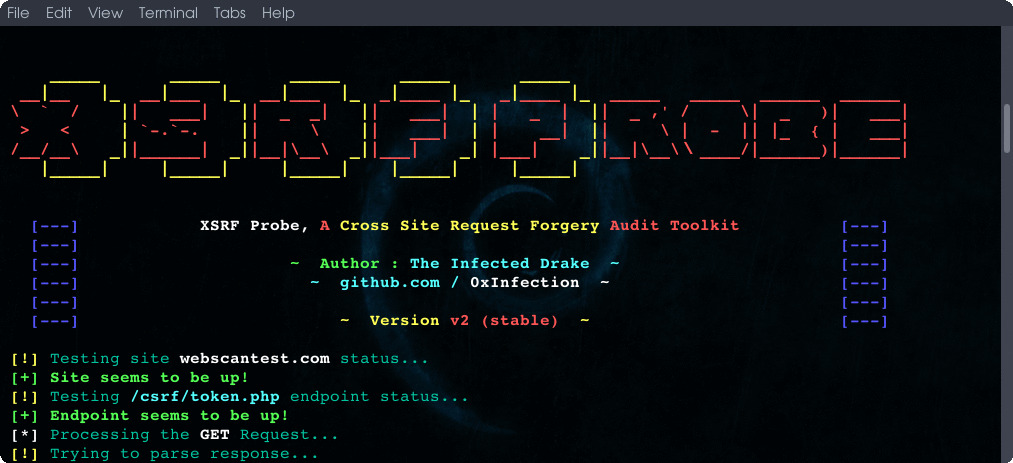 0xinfection/xsrfprobe
The Prime Cross Site Request Forgery (CSRF) Audit and Exploitation Toolkit.
 gokulapap/reconator
Automated reconnaissance framework with 17+ modules for subdomain enumeration, directory brute-forcing, JS/link mining, WAF fingerprinting, and…
 ssc-ict-innovatie/nl-kat-coordination
Modular network scanning framework that integrates diverse tools and external databases to detect vulnerabilities and configuration errors, producing…
 githubsecuritylab/seclab-taskflow-agent
MCP-enabled multi-agent framework for declarative YAML-driven agentic workflows, used for AI-assisted code auditing, vulnerability triage, and…
 dipjyotimetia/hybridtestframework
End to End testing of Web, API, Cloud, Events and Security
 hhhrrrttt222111/dorkify
Automated Google Dorking tool for OSINT reconnaissance, vulnerability discovery, and information gathering via advanced search operators and targeted…
 ociredefz/vsaudit
VOIP Security Audit Framework
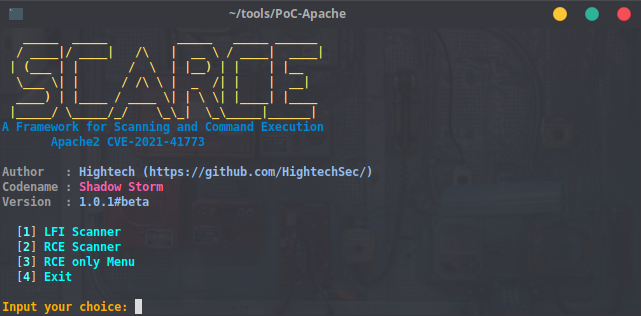 hightechsec/scarce-apache2
A framework for bug hunting or pentesting targeting websites that have CVE-2021-41773 Vulnerability in public
 sdnewhop/sdwan-harvester
:globe_with_meridians: Automatically enumerate and fingerprint SD-WAN nodes on the internet
 elevenpaths/atomshields
Security testing framework for repositories and source code
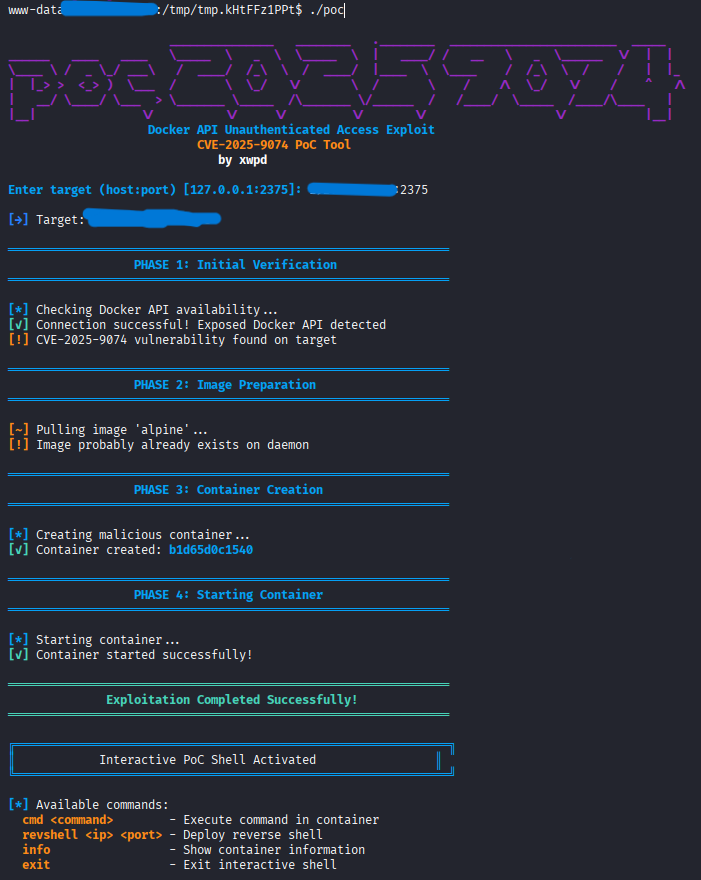 xwpdx0/poc-2025-9074
Docker API CVE-2025-9074 PoC (Proof-Of-Concept). A sophisticated exploitation framework for CVE-2025-9074, targeting unauthenticated Docker API…
 marklindsey11/gh-repo-clone-marklindsey11--cve-2021-44228_scanner-applications-that-are-vulnerable-to-the-log4j-cv
Scans applications for the Log4Shell vulnerability (CVE-2021-44228) to identify systems at risk of remote code execution.