
openrisk
 projectdiscovery/openrisk
openrisk is a tool that generates a risk score based on the results of a Nuclei scan.
ai-securitypenetration-testingutilities-frameworks+2
181
projectdiscovery/openriskopenrisk is a tool that generates a risk score based on the results of a Nuclei scan.
 videns/vulners-scanner
Vulnerability scanner based on vulners.com audit API
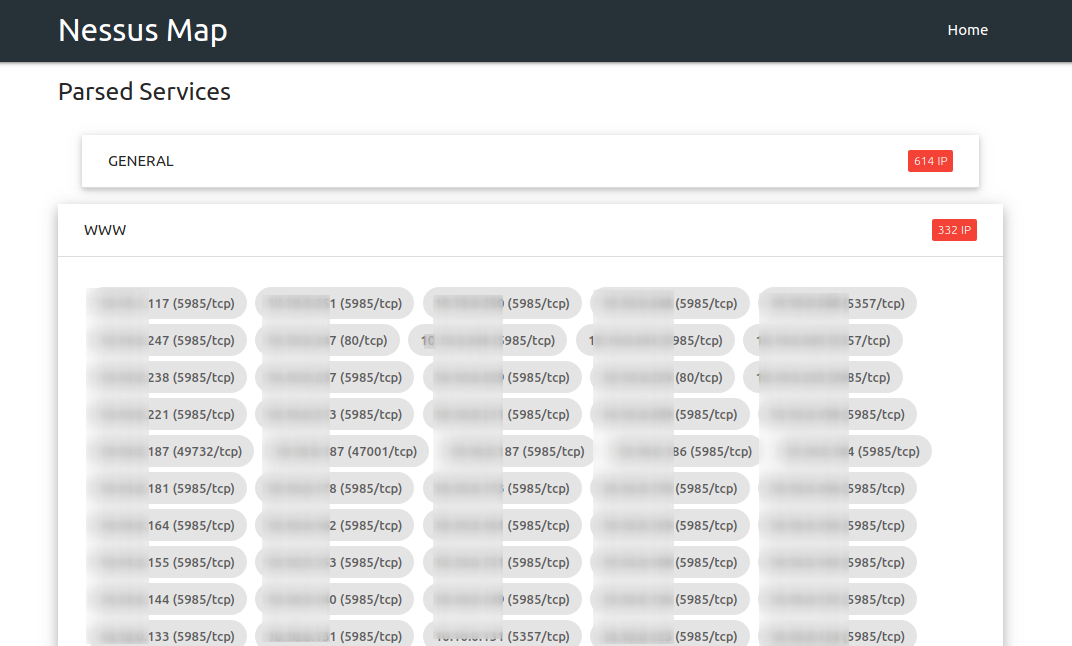 ebryx/nessus_map
Parse .nessus file(s) and shows output in interactive UI
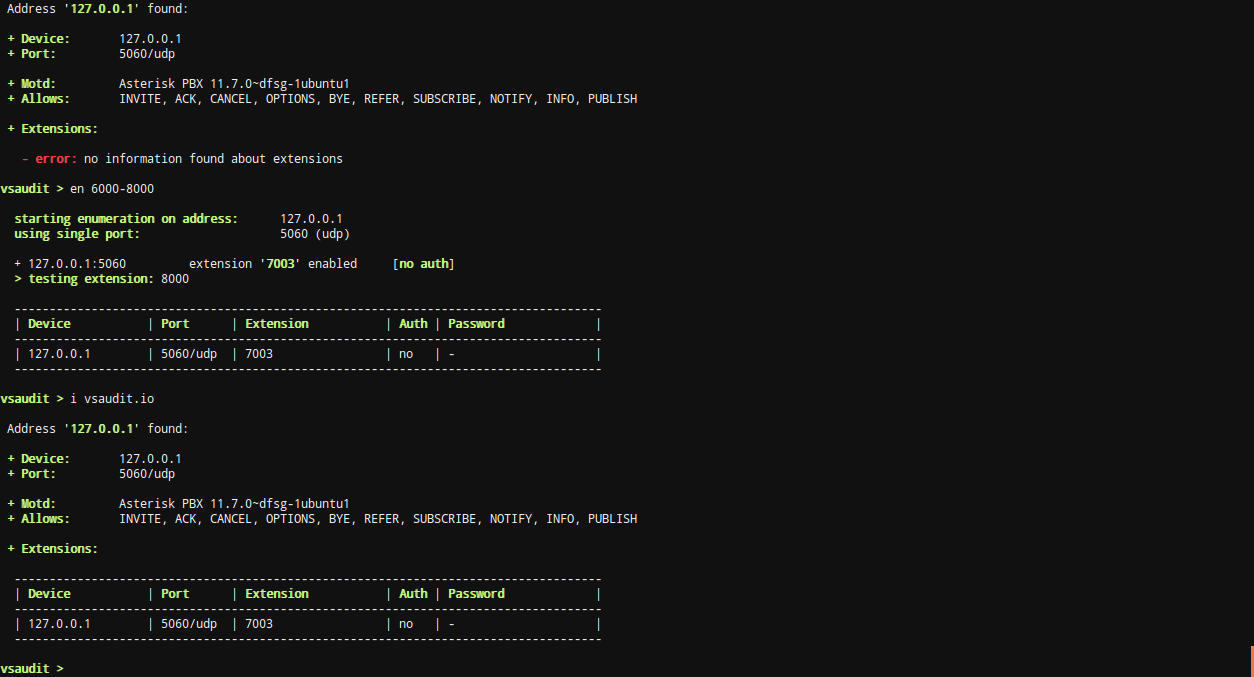 ociredefz/vsaudit
VOIP Security Audit Framework
 zephrfish/cve-2023-20198-checker
CVE-2023-20198 & 0Day Implant Scanner
 zephrfish/cve-2021-41773-poc
Proof-of-concept scanner that checks hosts for CVE-2021-41773 Apache path traversal vulnerability, reporting vulnerable or not vulnerable status.
 m3ssap0/springbreakvulnerableapp
WARNING: This is a vulnerable application to test the exploit for the Spring Break vulnerability (CVE-2017-8046). Run it at your own risk!
 h0ffayyy/jira-cve-2019-8451
POC to check for Jira instances vulnerable to CVE-2019-8451
 abrewer251/cve-2025-6543_citrixnetscaler_poc
Multi-host, multi-port scanner and auditor for CVE-2025-6543-affected NetScaler devices. Supports SNMP and SSH enumeration with optional CSV…
 krisiasty/vcheck
Vulnerability detection and mitigation tool for Copy Fail and Dirty Frag bugs (CVE-2026-31431, CVE-2026-43284, CVE-2026-43500)
 1n3/sn1per-mcp
MCP server that lets AI assistants drive a self-hosted Sn1per install, running scoped, audited scans and returning findings, ports, subdomains and…
 hidden-investigations/react2shell-scanner
Precision-Based Detection of RSC/Next.js Remote Code Execution Vulnerabilities (CVE-2025-55182, CVE-2025-66478)
 rxerium/cve-2025-26466
The OpenSSH client and server are vulnerable to a pre-authentication DoS attack between versions 9.5p1 to 9.9p1 (inclusive) that causes memory and…
 alexojocyber/cve-2011-2523-vsftpd-validation-lab
Authorized Kali–Metasploitable2 lab using Python and Nmap NSE to validate CVE-2011-2523 in vsFTPd 2.3.4.
 webhosting4u/copy-fail_detect_and_mitigate_cve-2026-31431
Detects exposure to CVE-2026-31431 (Copy Fail) and optionally mitigates by disabling the vulnerable algif_aead kernel module, providing verdicts and…
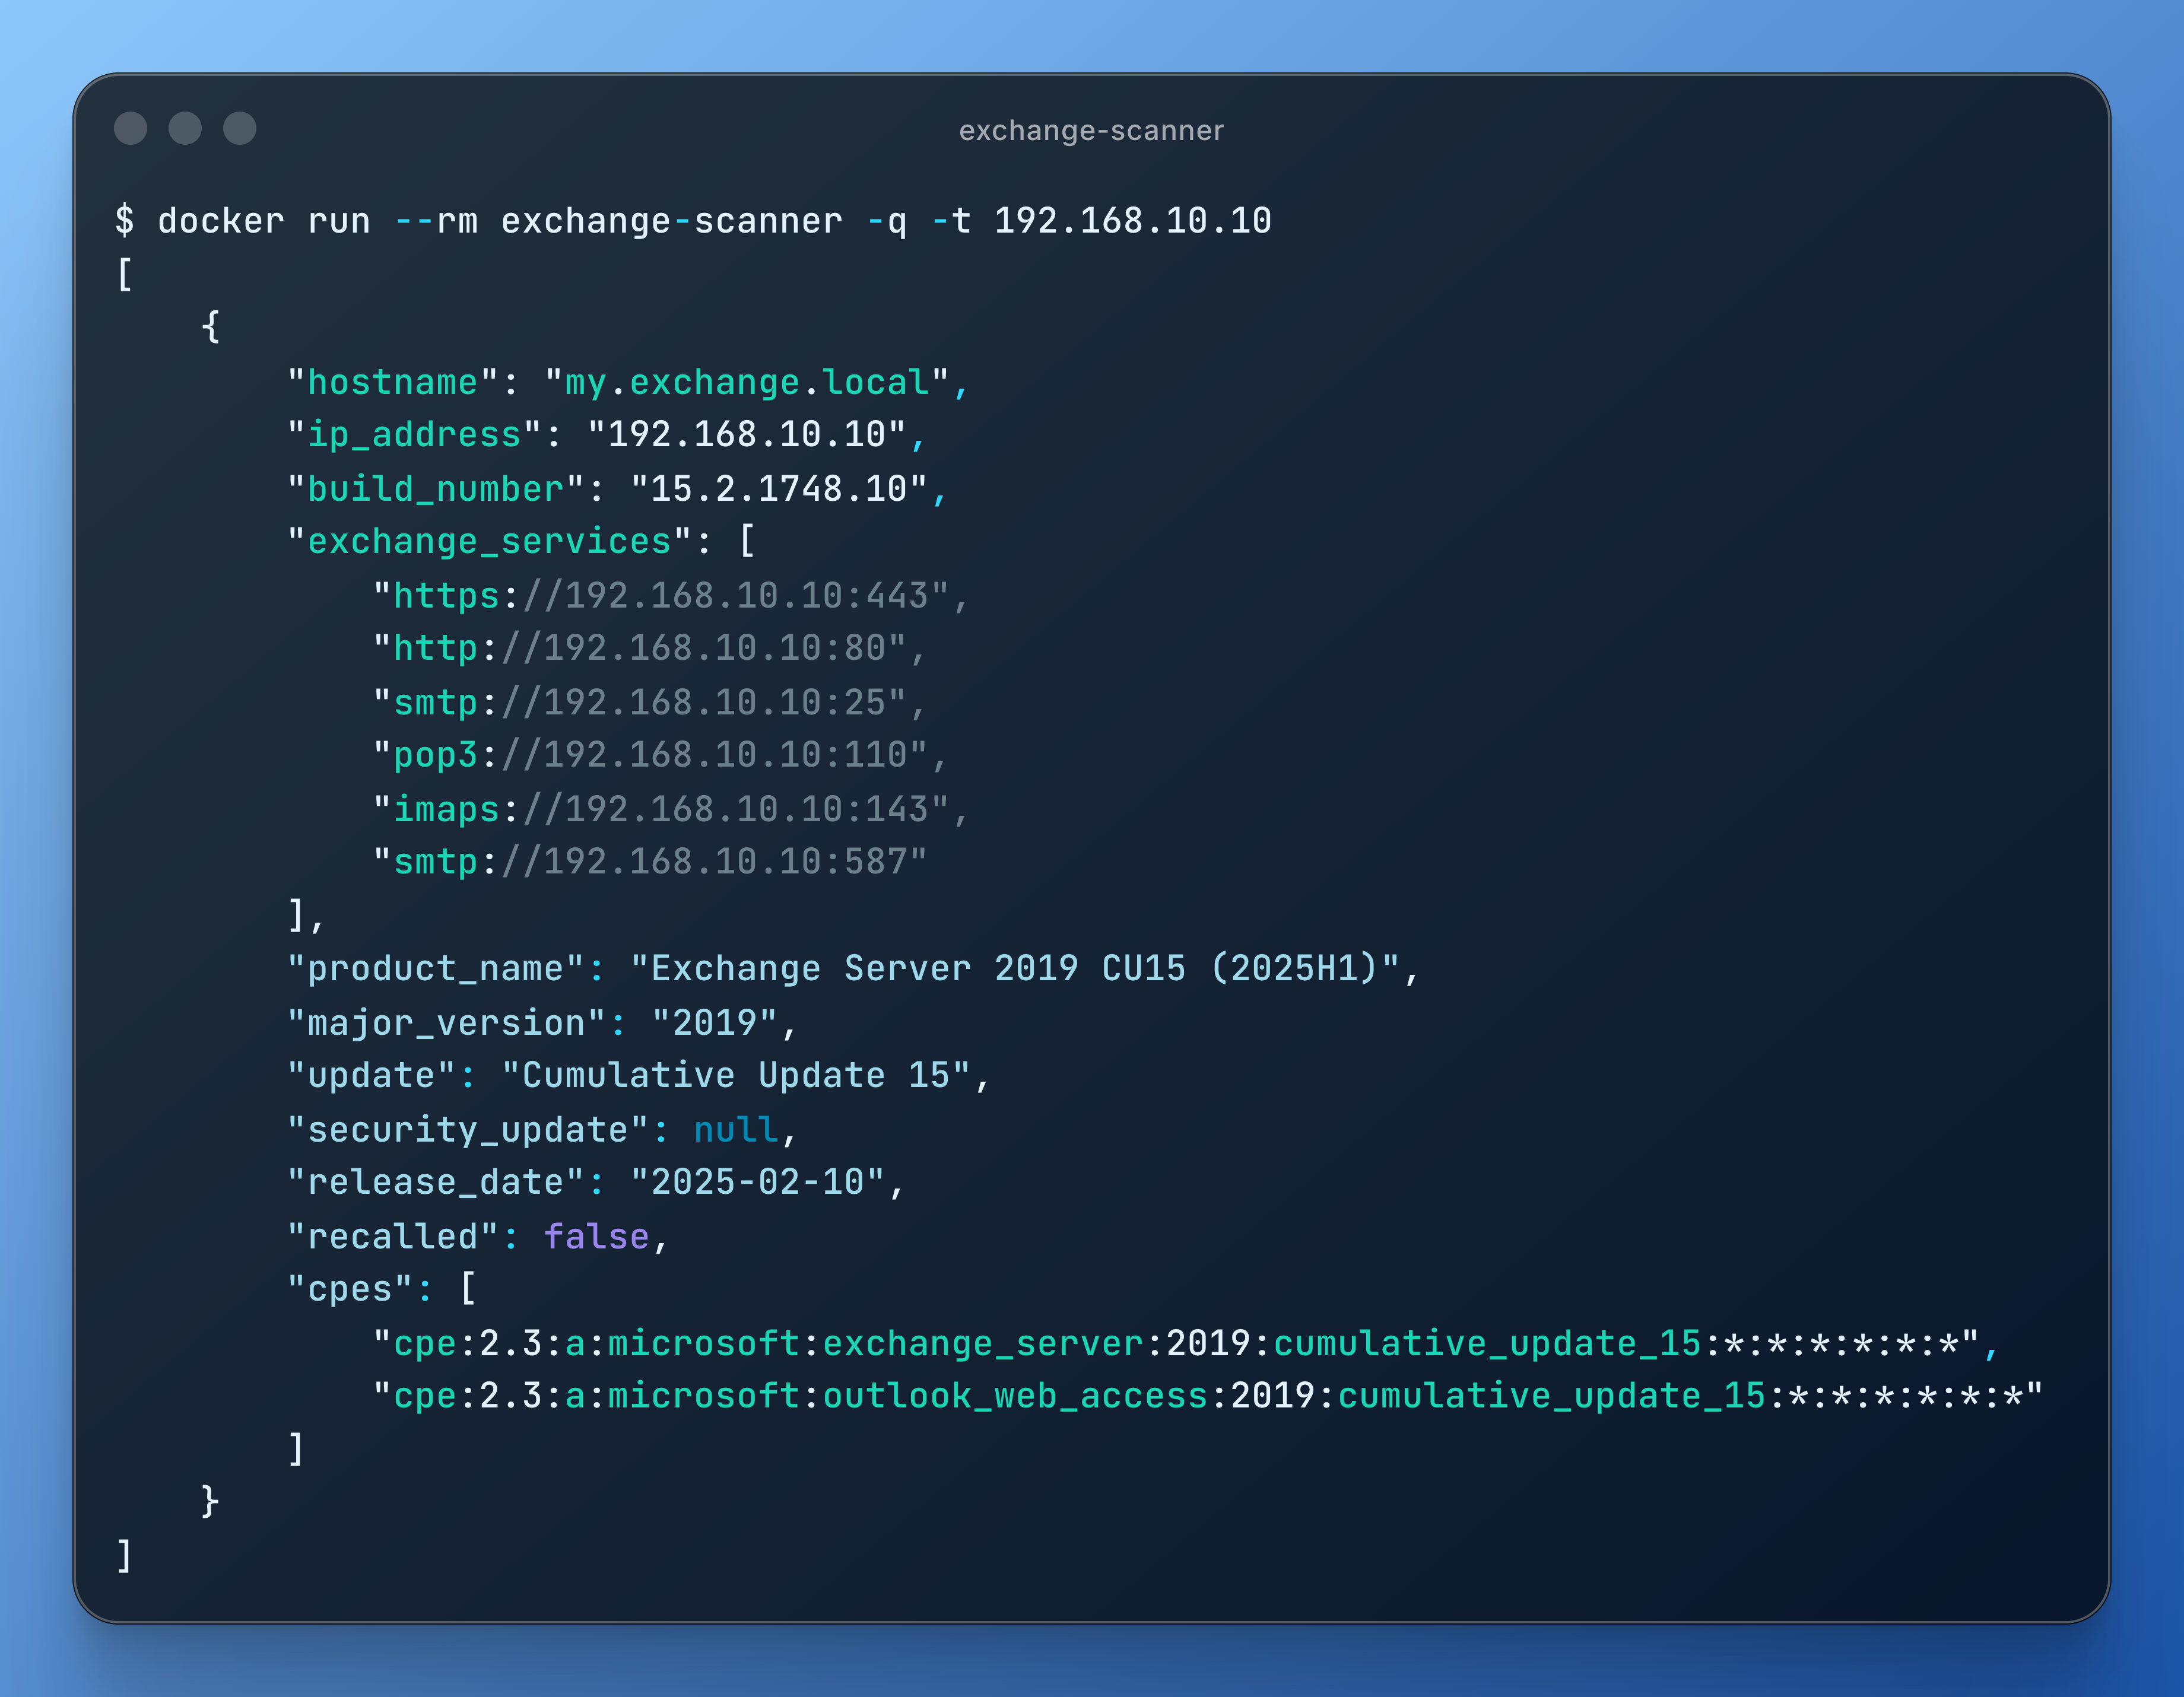 bishopfox/exchange-scanner
Identify public-facing Microsoft Exchange servers and determine their software versions
 ctzisme/copyfail-guard
Detect and mitigate CVE-2026-31431 (Copy Fail) on Linux systems.
 0dev1337/cpanelscanner
Scans internet-exposed cPanel/WHM instances for CVE-2026-41940 authentication bypass, probing HTTPS on port 2087 and matching response markers to…