
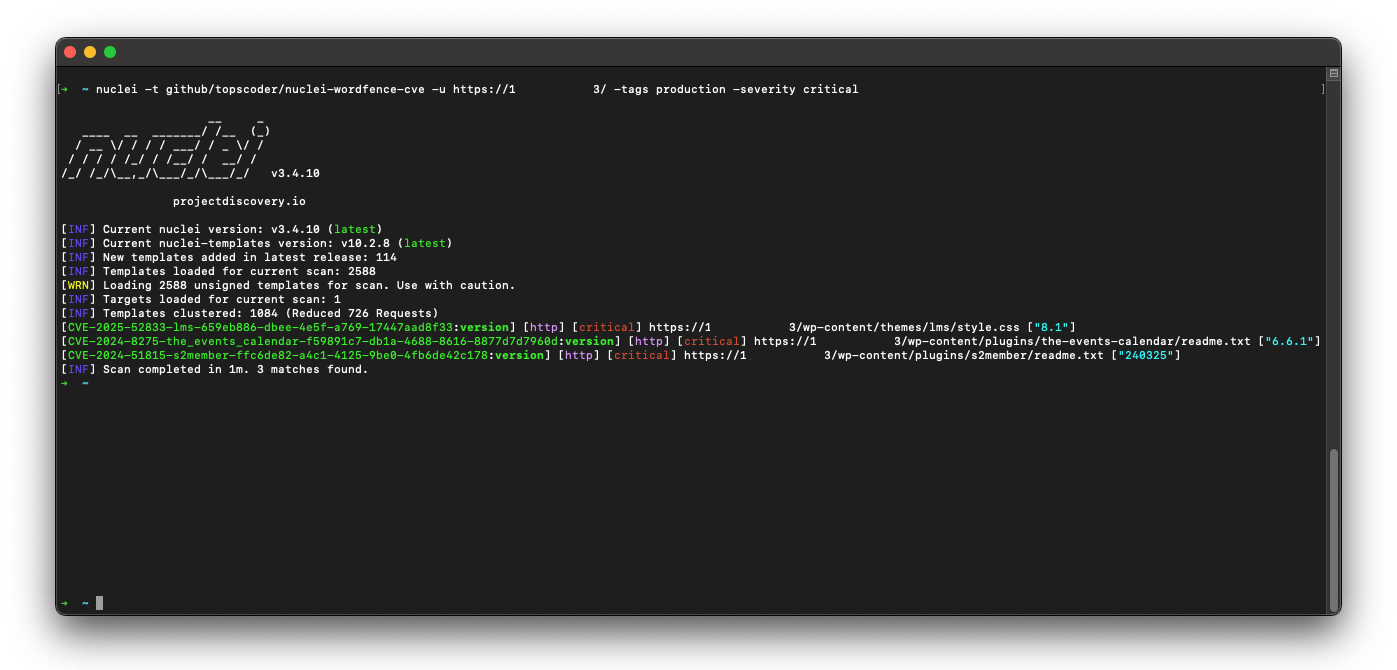
nuclei-wordfence-cve
 topscoder/nuclei-wordfence-cve
80k+ WordPress Nuclei templates, updated daily from Wordfence intel—filter by severity/tags/CVE and scan in one line. 🚀🔒
crawlerexploitationinformation-gathering+3
1.3k
topscoder/nuclei-wordfence-cve80k+ WordPress Nuclei templates, updated daily from Wordfence intel—filter by severity/tags/CVE and scan in one line. 🚀🔒
 future-architect/vuls
Agent-less vulnerability scanner for Linux, FreeBSD, Container, WordPress, Programming language libraries, Network devices
 wpscanteam/wpscan
WordPress security scanner that detects vulnerabilities, enumerates plugins/themes/users, and checks for weak passwords. Integrates with the WPScan…
 bhanunamikaze/wp2shell-cve-2026-63030-poc
PoC detector & safe validator for the WP2Shell WordPress vulnerability chain: CVE-2026-63030 (REST batch-route confusion) + CVE-2026-60137…
 tc4dy/cve-2026-87902-toolkit
WordPress CVE-2026-87902 LFI-to-RCE toolkit with a weaponized exploit chain (PEAR RCE, webshell, admin creation, loot) and a non-intrusive…
 tc4dy/cve-2026-64638-poc-exploit
🛡️ CVE-2026-64638 - WordPress Security Assessment Suite (CVSS 8.9) | WordPress 4.7.0-7.0.2 pentest toolkit. Includes vulnerability assessment &…
 nxploited/cve-2026-96451
WordPress Ultimate Member plugin <= 2.13.1 - Privilege Escalation vulnerability
 anoxhunterdump-ctrl/cve-2026-14378-devkit-pro-auth-bypass
Defensive analysis, patch breakdown, and detection scanner for CVE-2026-14378 (WordPress DevKit Pro Plugin <= 2.3.0).
 anoxhunterdump-ctrl/cve-2026-103752-authorizer-privilege-escalation
Defensive analysis, patch breakdown, and passive detection scanner for CVE-2026-103752 (WordPress Authorizer Plugin <= 3.15.3).
 zer0dayf/cve-2026-87902
Python PoC script for CVE-2026-87902 that performs basic checks against a target WordPress URL with configurable page, depth, prefix, and timeout…
 sangsenimanwartefak/cve-2026-5118
Detection tooling for CVE-2026-5118, an unauthenticated privilege escalation in Divi Form Builder <= 5.1.2, identifying affected WordPress…
 pwnvader/cve-2026-87915-poc-pwnvader
Shell PoC for CVE-2026-87915, an unauthenticated stored XSS in the Popup Maker WordPress plugin (<=1.24.0). Fingerprints the plugin and demonstrates…
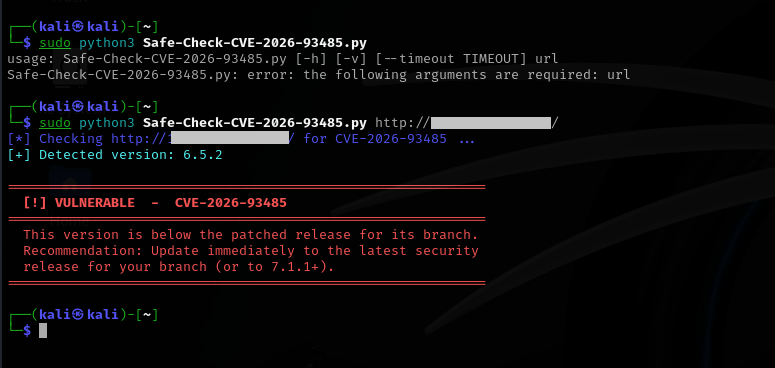 0xblackash/cve-2026-93485
Defensive research repository for CVE-2026-93485, a WordPress core stored XSS flaw, with version-check scanner, technical analysis, and patch…
 polosss/by-poloss..-.cve-2026-89274
Python PoC exploit for CVE-2026-89274, an unauthenticated arbitrary shortcode execution vulnerability in WordPress WP Recipe Maker <= 10.8.1 via…
 sangsenimanwartefak/cve-2026-80467
Python detection tool that fingerprints ACF Extended forms on WordPress and checks for publicly exposed role fields indicating CVE-2026-80467…
 0xcyp1337/cve-2026-57811
Exploits CVE-2026-57811, an unauthenticated RCE in Realtyna Organic IDX + WPL Real Estate WordPress plugin, enabling shell upload and command…
 fientix/cve-2026-8732-poc
CVE-2026-8732 | WP Maps Pro <= 6.1.0 Unauth Admin Creation
 0xcyp1337/cve-2026-82222-massexploit
Exploit tool for CVE-2026-82222, an unauthenticated RCE in GiveWP WordPress plugin. Supports single-target and batch exploitation with…