

 praetorian-inc/brutus
Fast, zero-dependency credential testing tool in Go. Brute force SSH, MySQL, PostgreSQL, Redis, MongoDB, SMB, and 20+ protocols. Hydra alternative…
 mycode83/godirb
Fast and easy-to-use directory brute-forcer written in Go.
 zhairiazzeddine/exploit-cve-2023-6063-poc-vuln
Python PoC for CVE-2023-6063, an unauthenticated time-based blind SQL injection in WP Fastest Cache <=1.2.2, extracting WordPress password hashes and…
 cerberusmrxi/wp-contest-gallery-28.1.4-exploit
Complete exploitation toolkit for CVE-2026-3180 - WordPress Contest Gallery SQL Injection vulnerability. Features automated data extraction, WAF…
 anonymous121029034720384234234/py-network-scanner
Advanced network penetration testing toolkit with SSH vulnerability assessment, CVE-2018-15473 exploitation, stealth brute force capabilities, and…
 password123456/malwarescanner
Hash-based malware scanner for incident response. Scans files recursively using known malware hashes, supports multithreading, extension filtering,…
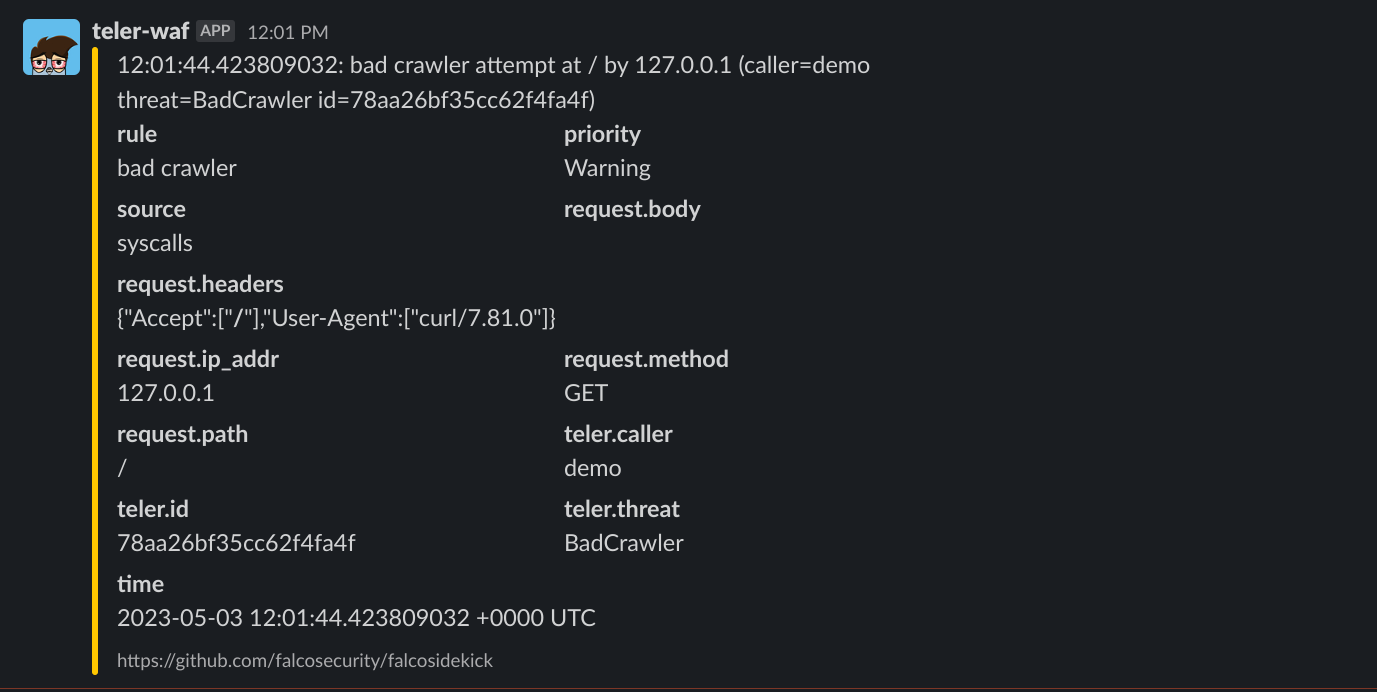 teler-sh/teler-waf
teler-waf is a Go HTTP middleware that protects local web services from OWASP Top 10 threats, known vulnerabilities, malicious actors, botnets,…
 dave_m/clamtk
An easy to use, light-weight, on-demand virus scanner for Linux systems. For additional help, see the <a…
 m4dm0e/dirdar
DirDar is a tool that searches for (403-Forbidden) directories to break it and get dir listing on it
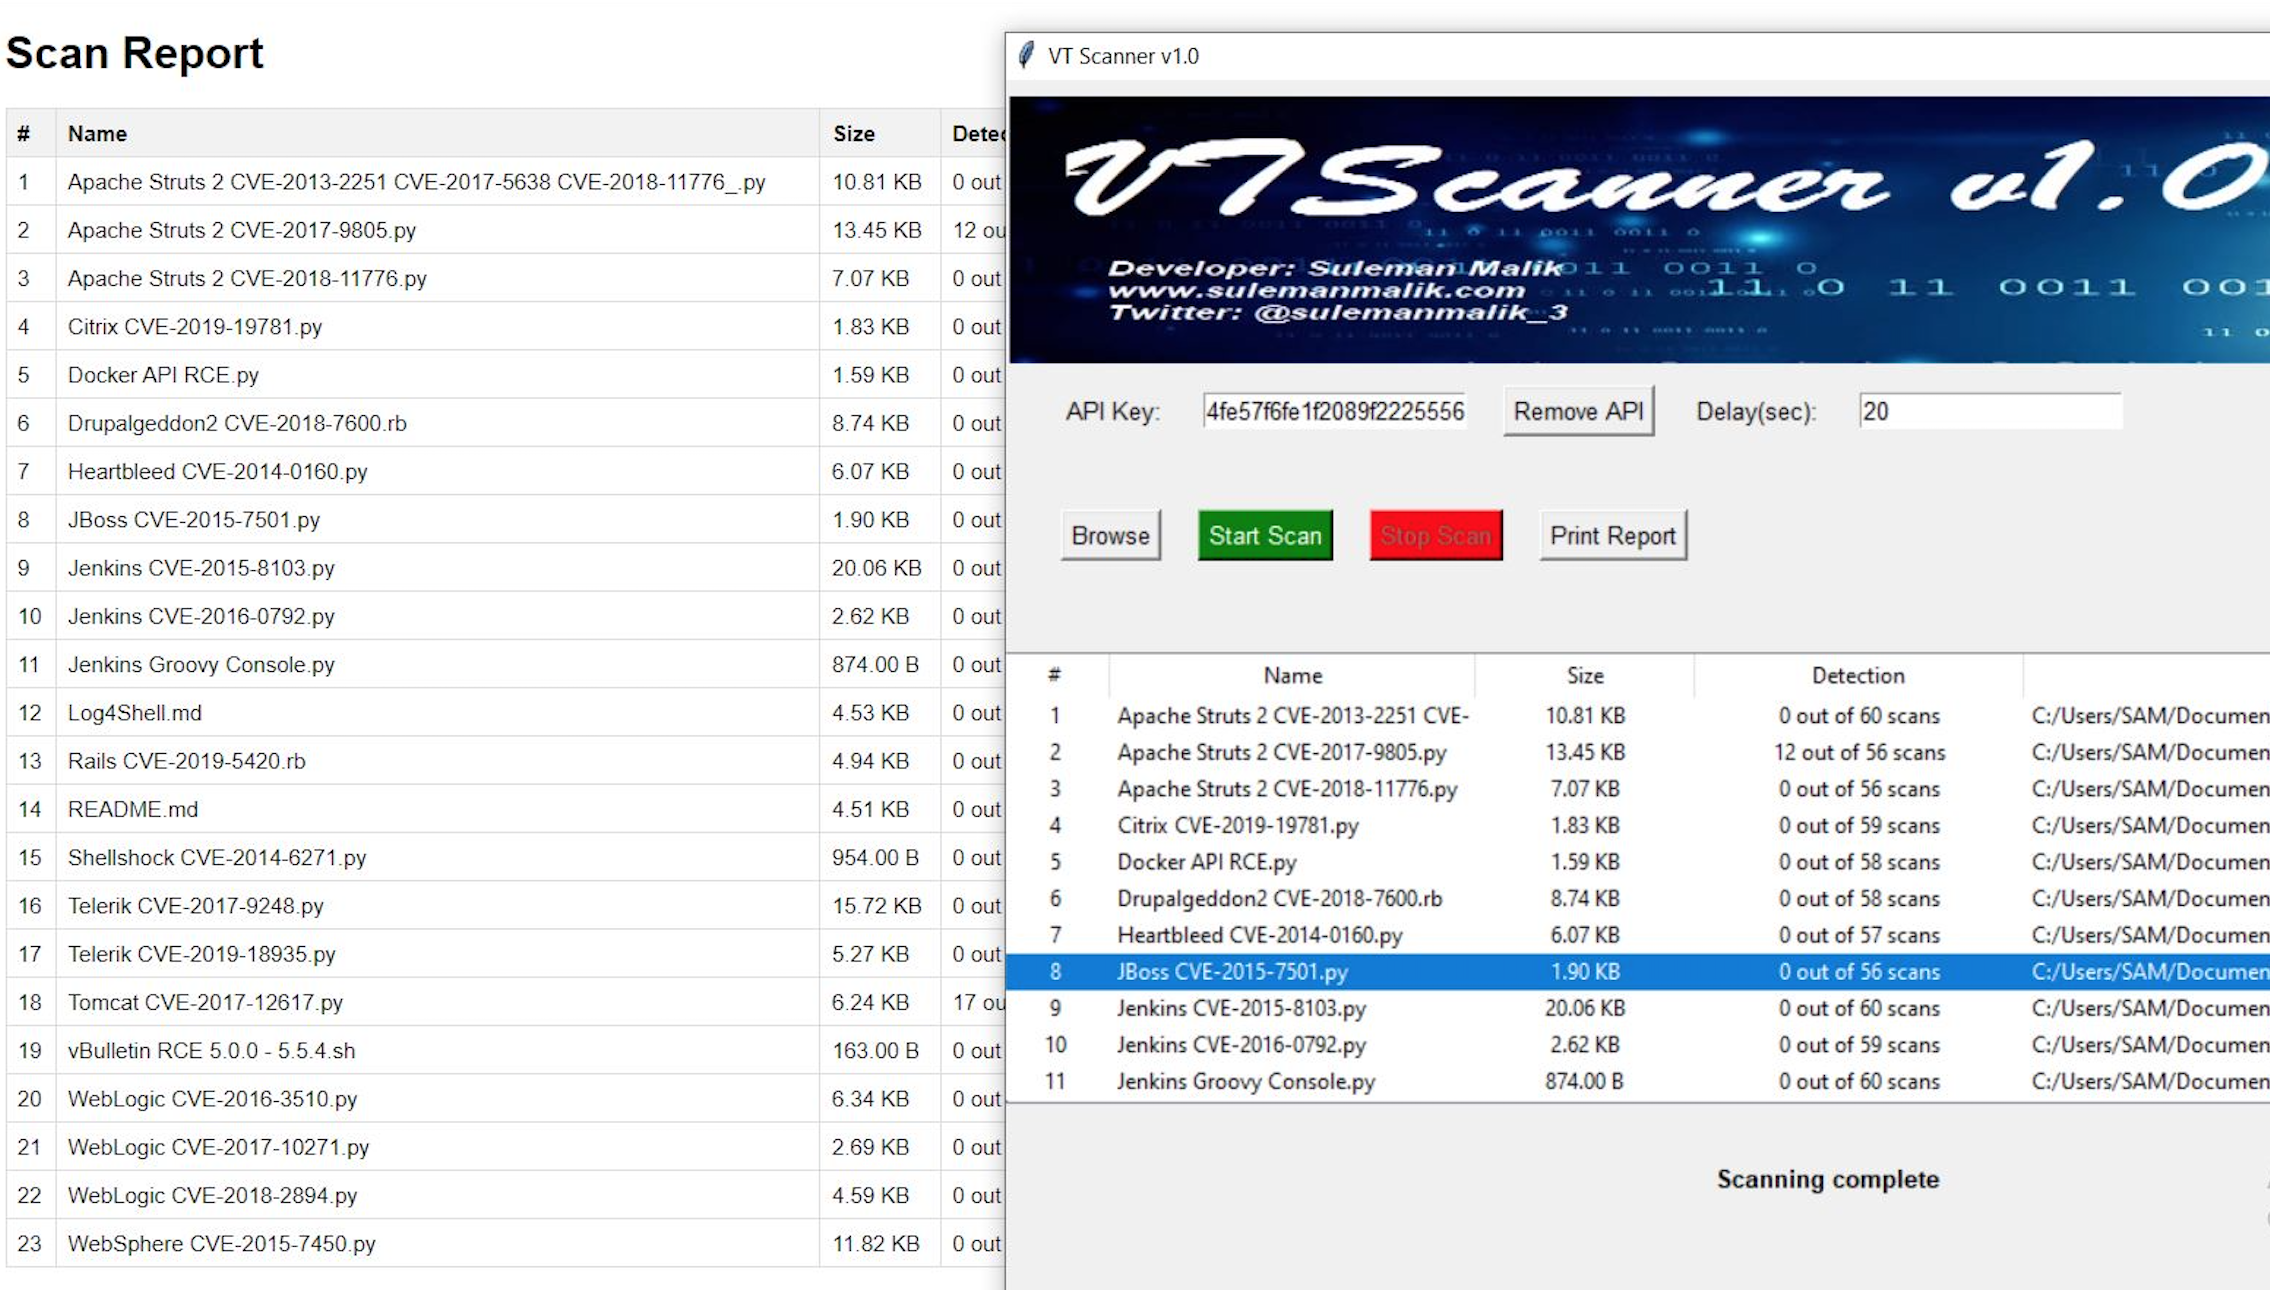 samhaxr/vtscanner
A comprehensive Python-based security tool for file scanning, malware detection, and analysis in an ever-evolving cyber landscape.
 nanotrash/hikvision_brute
Brute Hikvision CAMS with CVE-2021-36260 Exploit
 nu11secur1ty/insect
High-performance web path discovery and directory brute-forcing tool. Discovers hidden files, directories, and endpoints using customizable…
 1n3/brutex
Automatically brute force all services running on a target.
 storenth/lazyrecon
Wicked sick v2.0 script is intended to automate your reconnaissance process in an organized fashion.
 occamsec/log4j-checker
Bash and PowerShell scripts to scan a local filesystem for Log4j .jar files which could be vulnerable to CVE-2021-44228 aka Log4Shell.
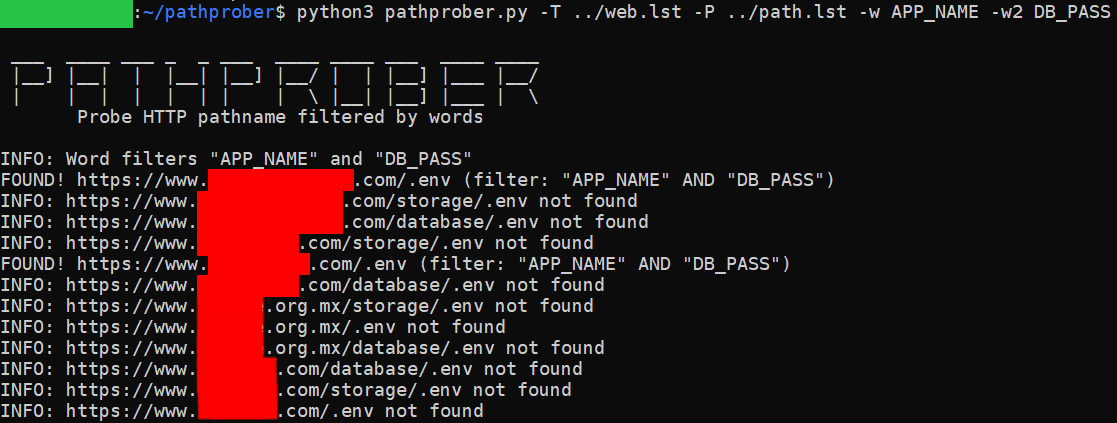 xchopath/pathprober
Probe and discover HTTP pathname using brute-force methodology and filtered by specific word or 2 words at once
 damian89/extended-ssrf-search
Smart ssrf scanner using different methods like parameter brute forcing in post and get...