
CVE-2026-55781-poc
 g17hubh4ck/cve-2026-55781-poc
Unbounded memory allocation in NanaZip's UFS handler via an attacker-controlled `fs_bsize` field.
exploitationpapers-researchvulnerability-analysis+1
3
g17hubh4ck/cve-2026-55781-pocUnbounded memory allocation in NanaZip's UFS handler via an attacker-controlled `fs_bsize` field.
 aipentest/cyberstrikeai
The system of action for AI-native cybersecurity—where intent becomes governed execution, evidence becomes operational memory, and every operation…
 luel-4013/misfortune-cookie
Interactive PoC suite for CVE-2014-9222 (Misfortune Cookie) and related router exploits, featuring detection, auth bypass, DoS, and RCE modules with…
 qassam-315/cve-2026-23918-elite-auditor
Elite reconnaissance script for auditing Apache's HTTP/2 stack against memory corruption (CVE-2026-23918). Features ALPN protocol forcing and…
 bishopfox/cve-2026-8452-check
Behavioral patch-state detector for Citrix NetScaler CVE-2026-8452. Sends crafted SAML requests to determine whether the PrefixList size check is…
 hackspeak/cve-2026-23479
Redis UAF RCE PoC collection for CVE-2026-23479: safe version checker, exploit module, GDB-assisted PoC, and Sigma detection rules for authorized…
 cybereason/siofra
Simulates the Windows PE loader to identify DLL hijacking vulnerabilities, generates weaponized DLLs with shellcode payloads, and detects UAC…
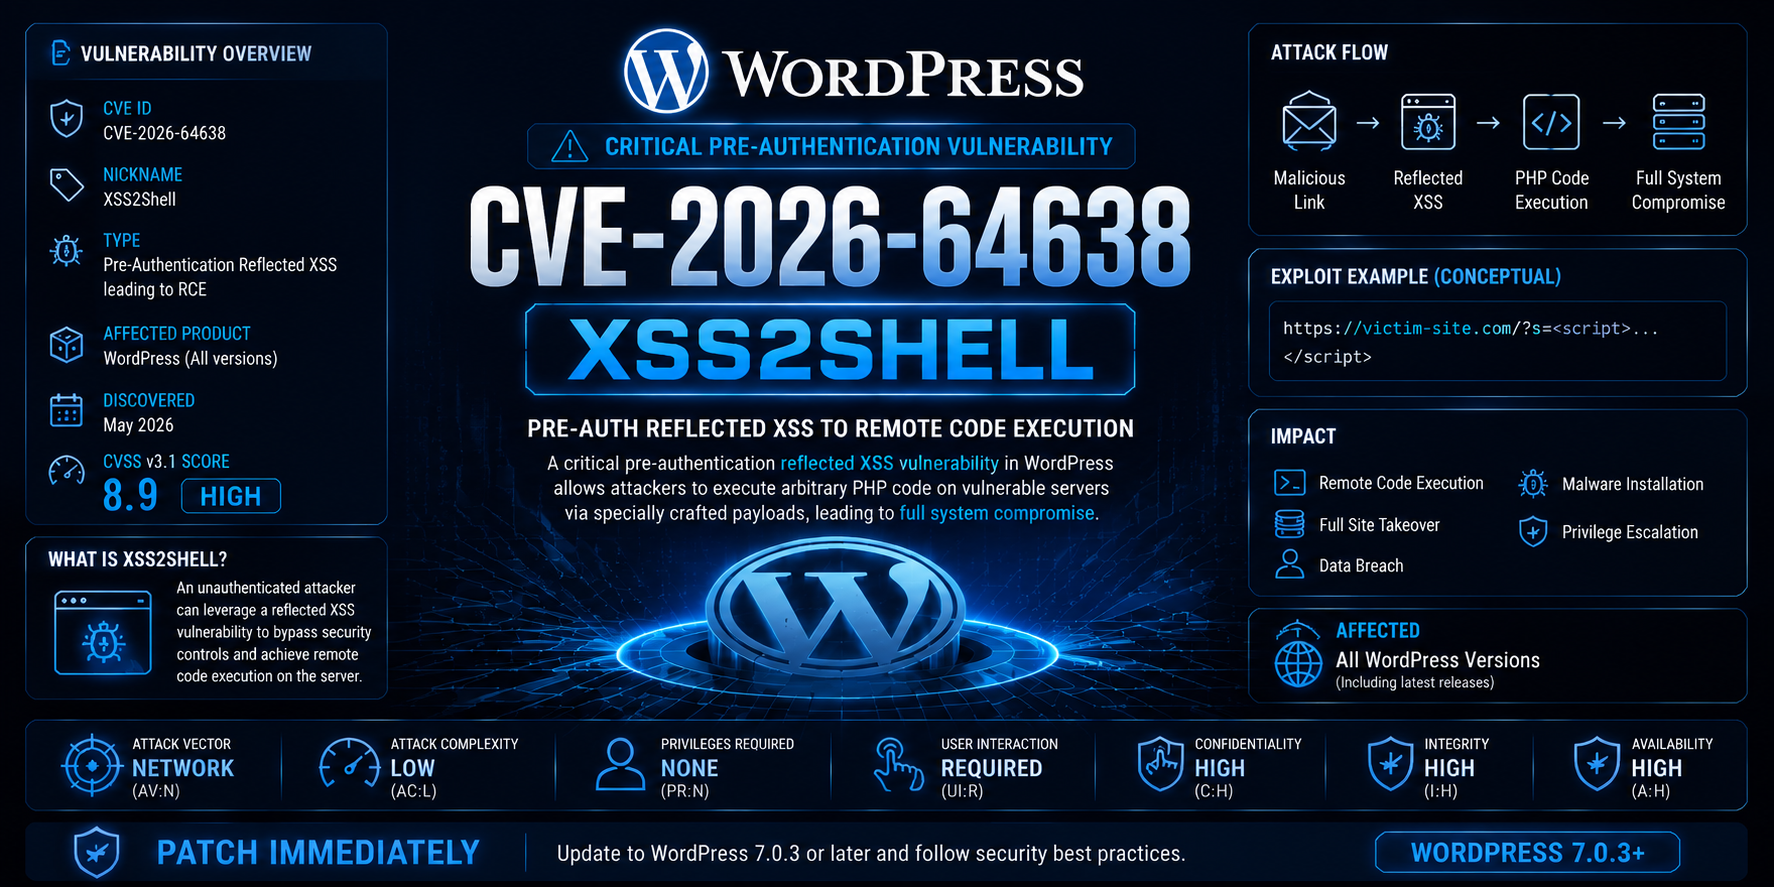 tc4dy/cve-2026-64638-poc-exploit
🛡️ CVE-2026-64638 - WordPress Security Assessment Suite (CVSS 8.9) | WordPress 4.7.0-7.0.2 pentest toolkit. Includes vulnerability assessment &…
 0init/cve-2026-45185
Exploits a critical pre-auth heap use-after-free in Exim via TLS close_notify to gain remote root; includes a GDB lab harness and Nuclei detection…
 sam00/poc-cve-2026-0300-exploit
Palo Alto - CVE-2026-0300 exploit
 amnsecurity/netscaler-saml-memory-disclosure-security-assessment
Professional vulnerability assessment report for NetScaler SAML memory disclosure risk, including technical impact, remediation, and mitigation…
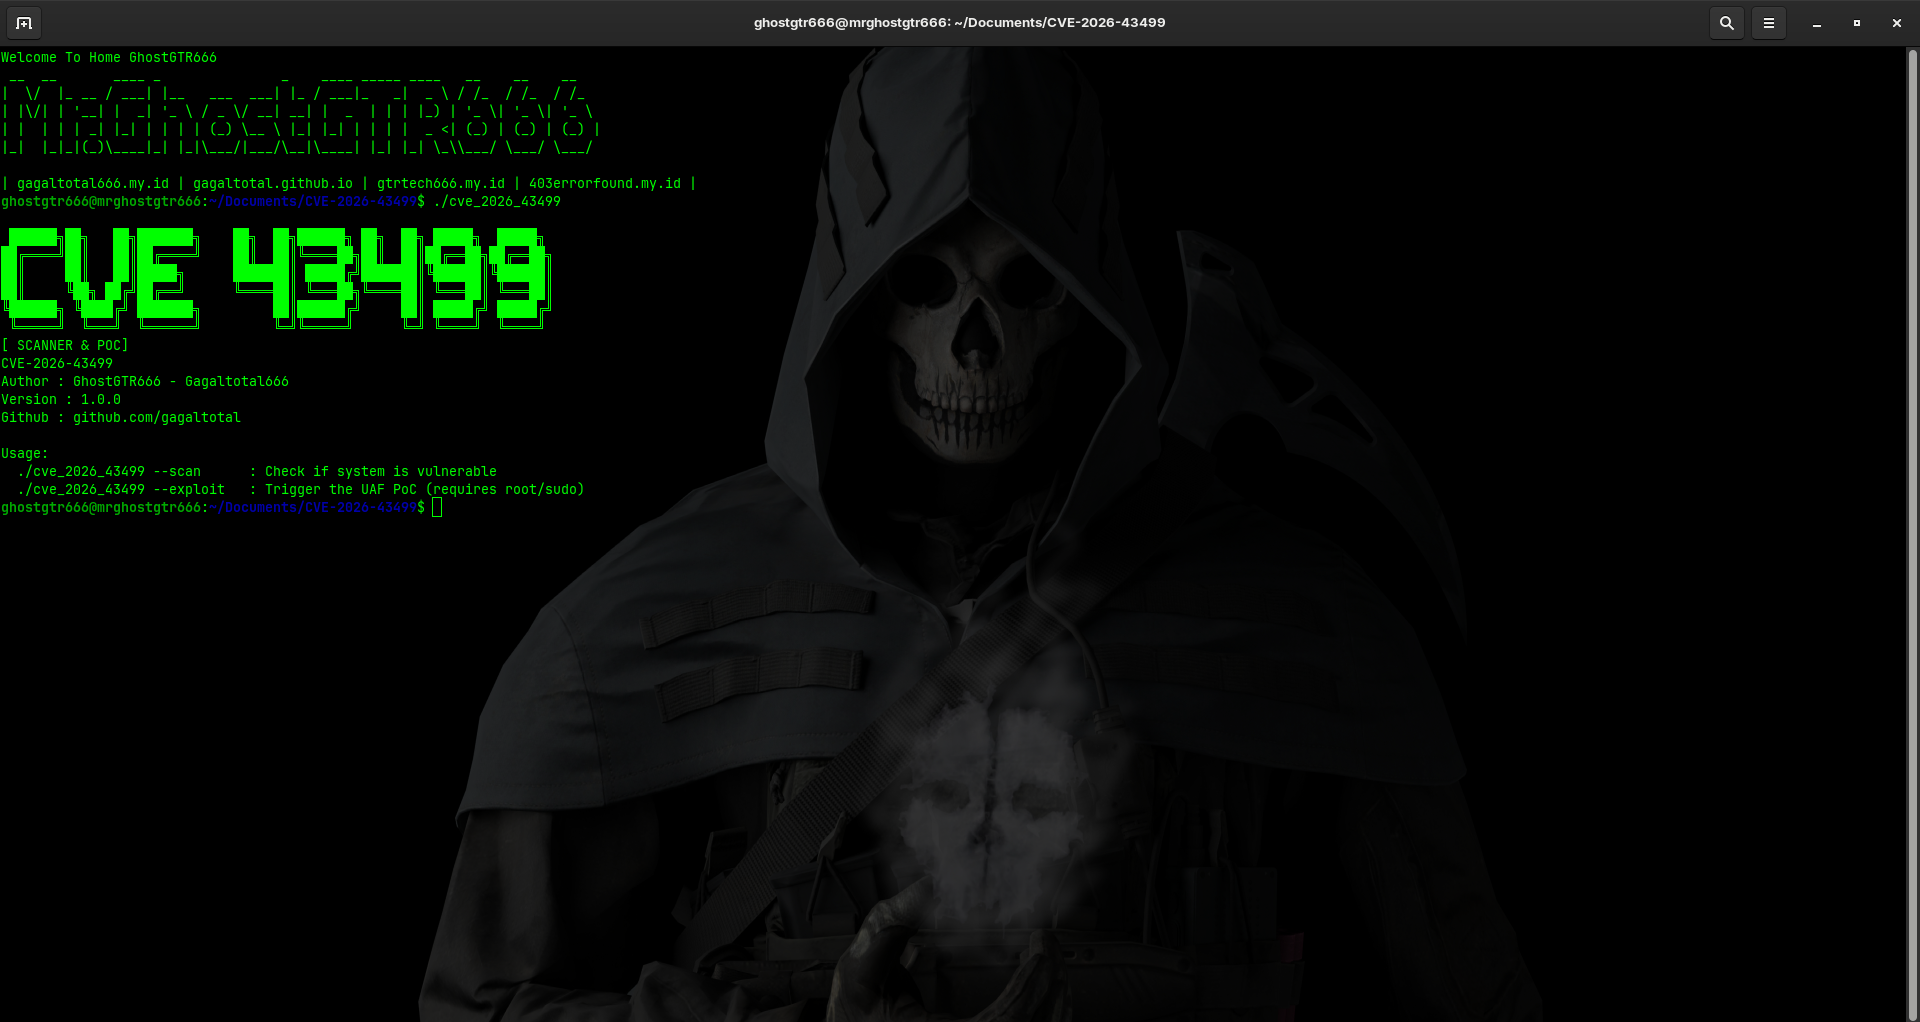 gagaltotal/cve-2026-43499-poc-scanner
CVE-2026-43499 PoC Scanner
 rvzsec/cve-2024-2961
CVE-2024–2961 Security Issue Mitigation Script
 ruppde/rdg_scanner_cve-2020-0609
Scanning for Remote Desktop Gateways (Potentially unpatched CVE-2020-0609 and CVE-2020-0610)
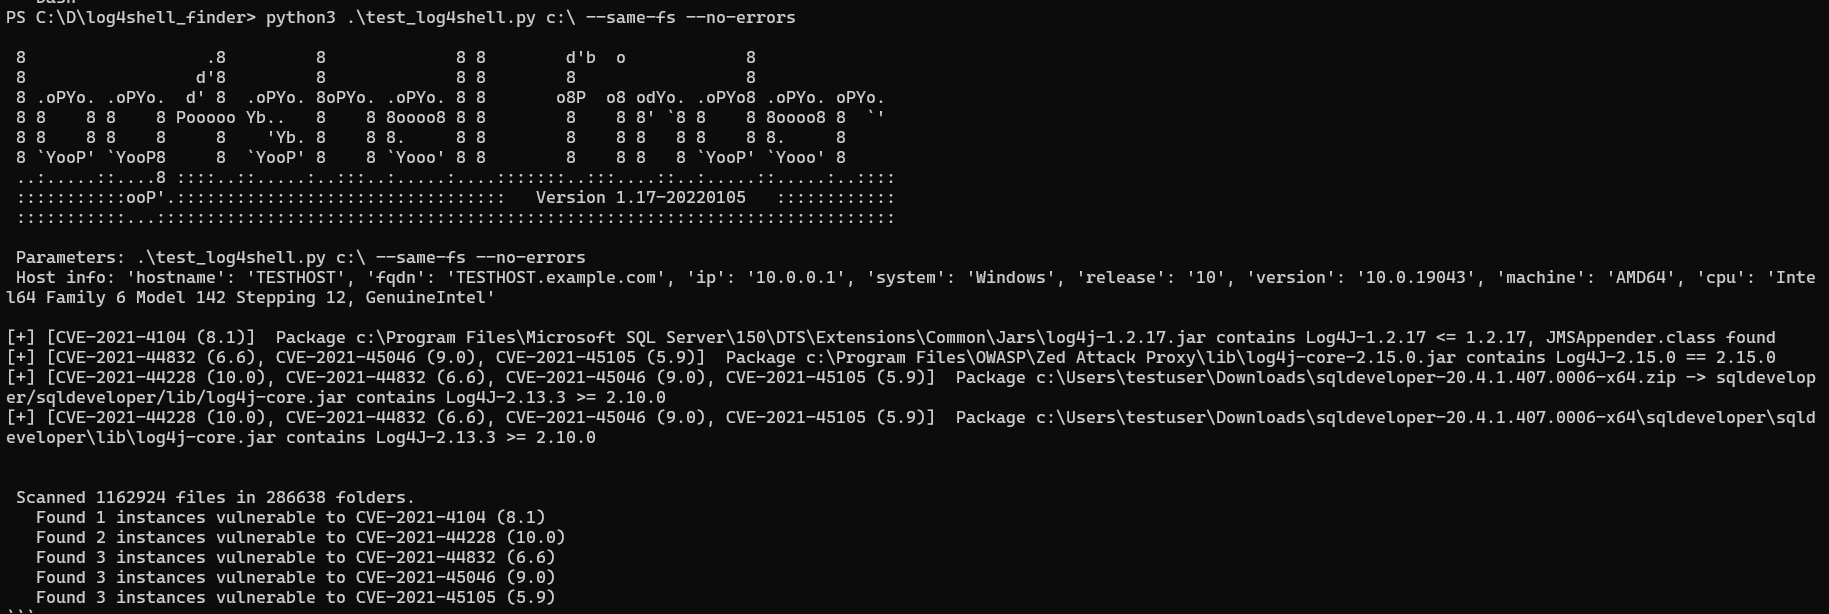 hynekpetrak/log4shell-finder
Fastest filesystem scanner for log4shell (CVE-2021-44228, CVE-2021-45046) and other vulnerable (CVE-2017-5645, CVE-2019-17571, CVE-2022-23305,…
 sho-luv/mongobleed
CVE-2025-14847 (MongoBleed) scanner and exploit tool. Unauthenticated MongoDB heap memory leak via zlib decompression. Detection, memory extraction,…
 renzi25031469/cve-2026-49975-http-2-bomb
Disclosed on June 3, 2026, the "HTTP/2 Bomb" is an unauthenticated remote DoS that combines an HPACK compression bomb with a Slowloris-style hold to…