

CVE-2026-114509
 nxploited/cve-2026-114509
Laravel TokenGuard authentication bypass through non-string API credentials
authenticationexploitationinformation-gathering+6
nxploited/cve-2026-114509Laravel TokenGuard authentication bypass through non-string API credentials
 naimkowshik/lbfh
About All in one tool for Information Gathering, Vulnerability Scanning and Crawling. A must have tool for all penetration testers
 hevnsnt/cvengine
AI-first external attack surface assessment with continuous discovery, evidence-based vulnerability validation, and developer-agent MCP integration.
 0xblackash/cve-2026-111497
Advisory and proof-of-concept toolkit for CVE-2026-111497 (Node2Shell), a Brotli heap overflow in Node.js, with trigger scripts, version checker, and…
 openai/php2shell-checker
CLI that checks a website's PHP version or a local PHP binary against embedded patch cutoffs to determine php2shell vulnerability status, with JSON…
 tridents10/vader-pro-vdr
AI-assisted Vulnerability Detection & Remediation platform featuring a Go endpoint agent, centralized dashboard, and vulnerability intelligence…
 m14r41/scan4secrets
Find credentials and secret with 170+ rules covering across source code, Web URL, and CI/CD, verifies them against vendor APIs, and generates SARIF,…
 sleepingbag945/dddd
Batch asset collection and vulnerability scanning tool for red teams. Pulls targets from Hunter, Fofa, and Quake, performs fingerprinting, subdomain…
 0xblackash/cve-2026-21589
Technical analysis and detection guidance for CVE-2026-21589, a pre-auth path traversal arbitrary file access flaw in Atlassian Data Center products.
 watchtowrlabs/watchtowr-vs-atlassian-cve-2026-21589
Python detection artifact that checks Atlassian Jira, Confluence, and Bitbucket instances for the CVE-2026-21589 arbitrary file read vulnerability.
 trustedsec/spoonmap
Python wrapper around masscan and nmap for large-scale port discovery, host discovery, banner grabbing, and NSE-based vulnerability scanning across…
 dmdhrumilmistry/security-harness
Multi-agent static application-security review harness for AI coding agents: maps codebases, hunts vulnerability classes, chains and verifies…
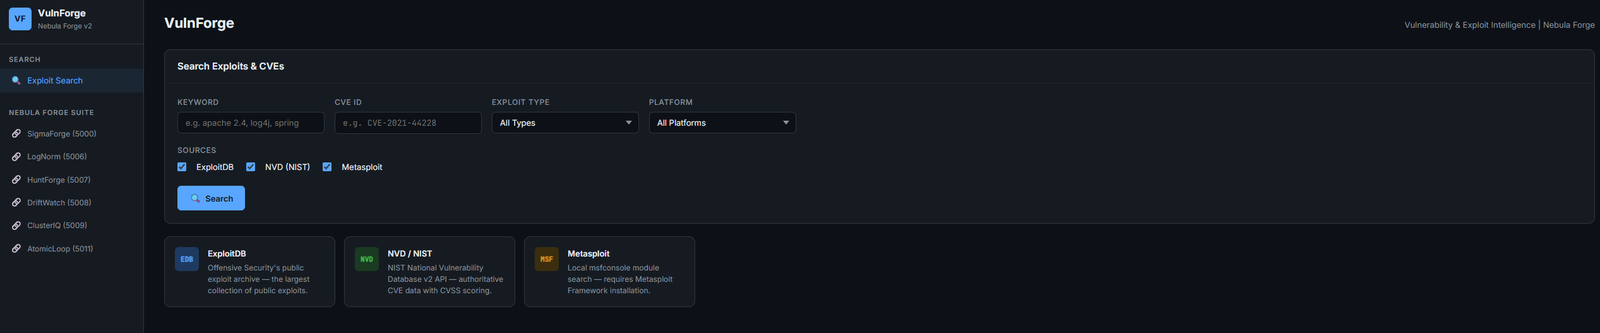 rootless-ghost/vulnforge
Vulnerability & exploit intelligence — ExploitDB, NVD, Metasploit search with CVE→ATT&CK mapping and LogNorm/HuntForge integration | Part of Nebula…
 akha-security/akca
Evidence-oriented DAST scanner in Go that crawls web apps and APIs, then runs adaptive SQLi, XSS, RCE, SSRF, and auth checks with replayable proof.
 sangsenimanwartefak/cve-2026-5118
Detection tooling for CVE-2026-5118, an unauthenticated privilege escalation in Divi Form Builder <= 5.1.2, identifying affected WordPress…
 nxploited/cve-2026-91097-cve-2026-91106
HPLIP < 3.26.6 — Full admin takeover via PAPPL web interface (no auth). Related to CVE-2026-91097 through CVE-2026-91106 (CVSS 9.3)
 babydessy/cve-2024-27954
Nuclei template and detection queries for CVE-2024-27954, a path traversal and SSRF vulnerability in the WP Automatic WordPress plugin up to version…
 iicaicai/cve-2026-5524-poc
Python mass-exploit toolkit for CVE-2026-5524, an unauthenticated file upload RCE in the WordPress Divi Form Builder plugin, with webshell upload and…