
thc-BloodMiami
 foxcornlab/thc-bloodmiami
AI chat-box pentesting tool in C: fires language (SQLi/NoSQL/XSS/SSTI) and prompt injection payloads at chat interfaces and flags the ones that bite
ai-securityapi-security-testingfuzzing+5
foxcornlab/thc-bloodmiamiAI chat-box pentesting tool in C: fires language (SQLi/NoSQL/XSS/SSTI) and prompt injection payloads at chat interfaces and flags the ones that bite
 owasp/agentic-vulnerability-discovery-and-validation-harness
Agentic harness that automates vulnerability discovery and validation, orchestrating AI-driven analysis workflows to confirm exploitable findings.
 piratesshield/apiharvester
The one shot API attacker tool - finds the API url from the given root simulate the automated attacks
 watchtowrlabs/watchtowr-vs-citrix-netscaler-cve-2026-88772
Detection artifact generator for Citrix NetScaler CVE-2026-88772 that builds a DTLS pre-auth buffer overflow payload to verify remote code execution.
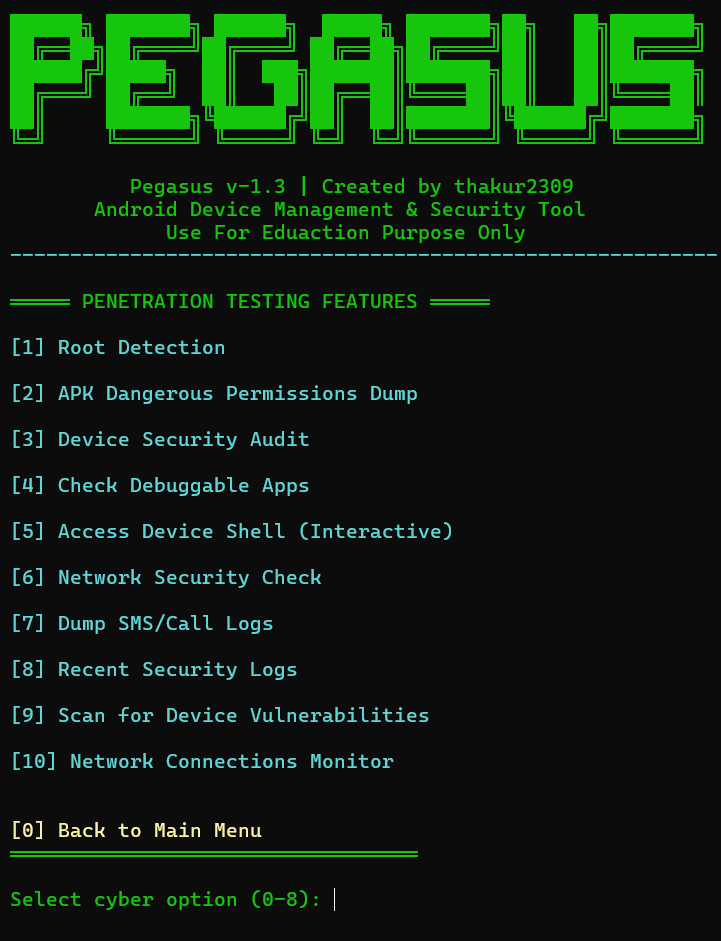 thakur2309/pagasus-pro
Python ADB-based Android device management and security audit toolkit with an interactive menu for root detection, permission dumps, debuggable app…
 langz337/cve-2026-63030
Python exploit tool chaining CVE-2026-63030 REST batch-route confusion with CVE-2026-60137 SQL injection to achieve unauthenticated WordPress RCE,…
 hitechcloud-vietnam/cve-2026-41940-poc
Exploits CVE-2026-41940, a cPanel & WHM authentication bypass, to gain root WHM access and run post-exploitation commands, file reads, and account…
 bhideki/cve-2026-87902
Python PoC and scanner for CVE-2026-87902, a WordPress core path traversal leading to LFI and PEAR-based RCE, with WAF bypass and automated…
 6ickzone/helix3-mass-exploiter
Mass scanner and auto-write tool for CVE-2026-49049, detecting exposed Joomla Helix3 onAjaxHelix3 handlers and verifying unauthenticated file-upload…
 johenlastgen-jlg/cve-2025-6325_cve-2025-6327
Python PoC validating CVE-2025-6325 unauthenticated privilege escalation and CVE-2025-6327 arbitrary file upload RCE in King Addons for Elementor <=…
 murrez/cve-2026-89274
Python PoC scanner and exploit for CVE-2026-89274, an unauthenticated arbitrary shortcode execution flaw in WP Recipe Maker <=10.8.1 via recipe…
 murrez/cve-2026-92229
Python 3 PoC scanner and exploit for CVE-2026-92229, an unauthenticated arbitrary shortcode execution flaw in Forminator WordPress plugin versions…
 talha1112/fyp
Desktop-based vulnerability assessment tool for security teams — scan web apps & networks, detect CVEs, map exploits, auto-score risk, and generate…
 matakucing-ofc/cve-2026-49049
Python scanner and proof-of-concept for CVE-2026-49049, an arbitrary file write in Joomla Helix3 that enables PHP web shell upload and remote code…
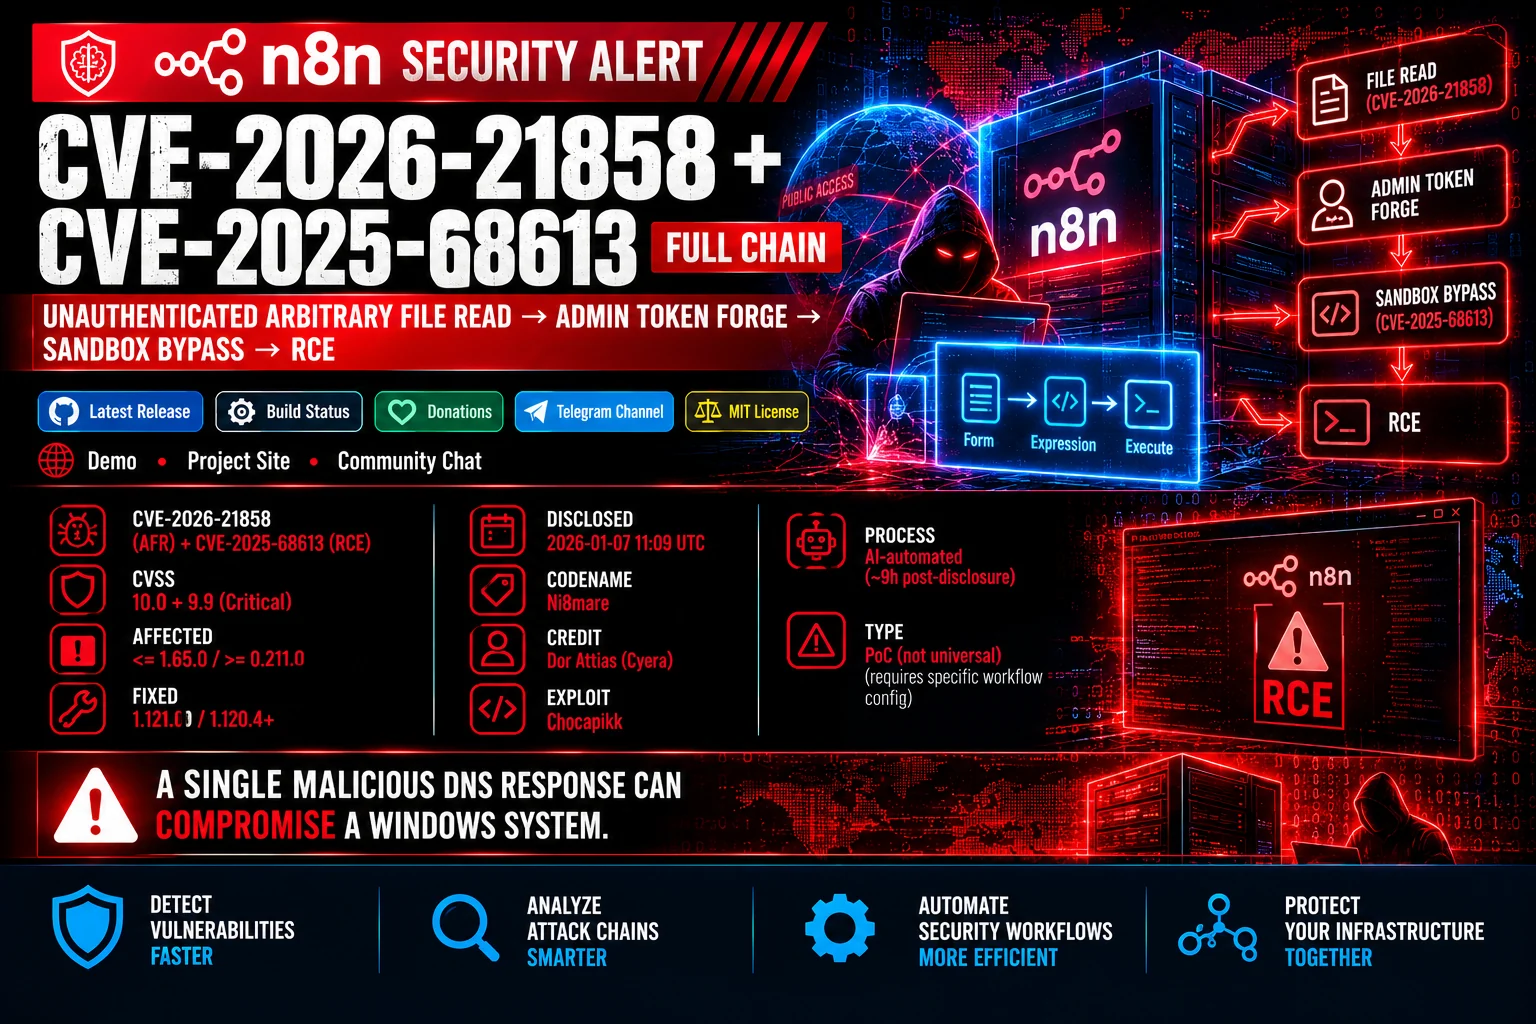 zerodayevil/cve-2026-21858-n8n-fullchain
🛡️ Official AI Security Tool module for CVE-2026-21858 + CVE-2025-68613 (n8n "Ni8mare" Unauthenticated Arbitrary File Read & Expression Injection…
 johenlastgen-jlg/cve-2026-18351
Mass exploit tool for CVE-2026-18351, an unauthenticated arbitrary file upload to RCE in Elementor Forms <= 1.6.0, with passive probing, shell…
 4rt-net/mikrotrick_poc
Testing tool for the Mikrotrick exploit (CVE-2026-67276)
 gmh5225/cve_2023_44487-rapid_reset
Python-based testing tool for CVE-2023-44487 (HTTP/2 Rapid Reset) with multiple attack patterns, granular configuration, and monitoring for…