
netprobe-cve-2026-98432
 xen0bit/netprobe-cve-2026-98432
Black-box remote probe that detects CVE-2026-98432, a Linux IPv4 TCP ireq_opt use-after-free, via differential SYN-ACK option echo, plus static…
binary-analysisexploitationfuzzing+4
6
xen0bit/netprobe-cve-2026-98432Black-box remote probe that detects CVE-2026-98432, a Linux IPv4 TCP ireq_opt use-after-free, via differential SYN-ACK option echo, plus static…
 lu1sdv/wafmeow
wafw00f's fingerprints. Go speed. Pipeline-native. WAF detection from live HTTP and offline captures.
 gmh5225/ollama-hunter
Scans Shodan for publicly exposed Ollama and llama.cpp servers, enumerating hosts, locations, and available models for security research.
 2t8a/cve-2025-49132
Python scanner for CVE-2025-49132 that exploits a path traversal in Pterodactyl Panel's locale endpoint to extract exposed database configuration…
 yasindce1998/barzakh
Ring -4 to Ring 0: offense-defense firmware research platform. We build the bootkits, then we catch them. Closed-loop. Zero trust in silicon.
 sleepingbag945/dddd
Batch asset collection and vulnerability scanning tool for red teams. Pulls targets from Hunter, Fofa, and Quake, performs fingerprinting, subdomain…
 bsysop/servicenow
Scans ServiceNow instances for widget-simple-list plugin misconfigurations that expose data via the API, supporting single URLs, URL lists,…
 nxploited/cve-2026-96451
WordPress Ultimate Member plugin <= 2.13.1 - Privilege Escalation vulnerability
 securewithumer/exploit-index
Zero-API aggregator indexing 150k+ CVE exploits and PoCs from Exploit-DB, Nuclei, Metasploit, and CISA KEV, with EPSS/CVSS risk scoring for threat…
 piratesshield/apiharvester
The one shot API attacker tool - finds the API url from the given root simulate the automated attacks
 rootless-ghost/vulnforge
Vulnerability & exploit intelligence — ExploitDB, NVD, Metasploit search with CVE→ATT&CK mapping and LogNorm/HuntForge integration | Part of Nebula…
 valtersit/wordpress-cve-scanner
Scan your WordPress core, themes and plugins for known CVEs from the command line. Open source, auditable, privacy-first — powered by the ValtersIT…
 mondoohq/cnspec
An open source, cloud-native security to protect everything from build to runtime
 karim852/kumo-domain-recon-tool
Domain OSINT and security reconnaissance framework running 26 parallel modules for DNS, ports, subdomains, leaked credentials, exposed endpoints,…
 gabrielunknown/cve-2026-85706
Perl PoC exploiting CVE-2026-85706, an unauthenticated GitLab path traversal enabling arbitrary file read, with bulk scanning and credential…
 solivaquaant/cve-2026-85706
Proof-of-concept and reproduction lab for CVE-2026-85706, an unauthenticated path-traversal file read in GitLab CE/EE repository commits and files…
 syntaxmethod/cve-2026-42978-poc-research
CVE-2026-42978 Windows Push Notifications (WpnService) Use-After-Free & Race Condition PoC research, diagnostic scanner, and security audit module…
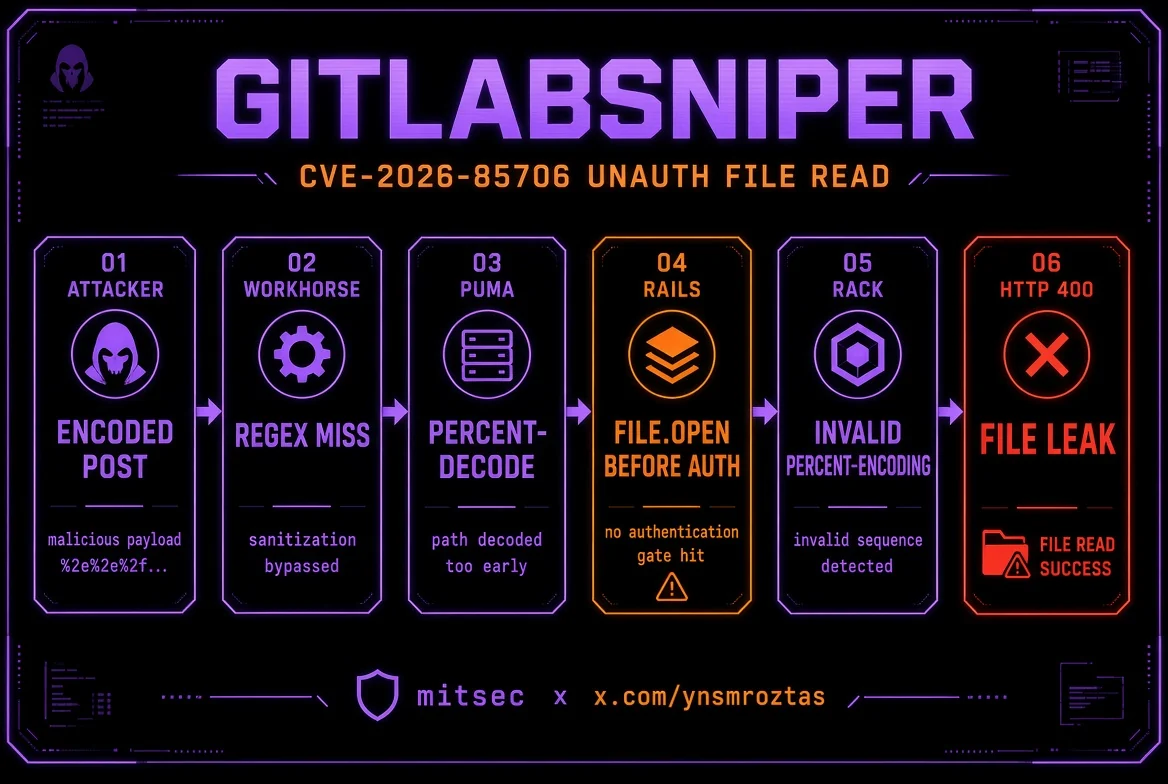 ynsmroztas/gitlabsniper
Single-file Python scanner and exploit for CVE-2026-85706, an unauthenticated arbitrary file read in self-managed GitLab CE/EE, with project…