Apache-OFBiz-Auth-Bypass-and-RCE-Exploit-CVE-2023-49070-CVE-2023-51467

This exploit scans whether the provided target is vulnerable to CVE-2023-49070/CVE-2023-51467 and also exploits it depending on the choice of the…

This exploit scans whether the provided target is vulnerable to CVE-2023-49070/CVE-2023-51467 and also exploits it depending on the choice of the…

[EXPERIMENTAL] Kubernetes Operator for Image Assurance

A Trivy plugin that scans the images of a kubernetes resource

Nmap NSE script to detect Pulse Secure SSL VPN file disclosure CVE-2019-11510

Explore RootSec's DDOS Archive, featuring top-tier scanners, powerful botnets (Mirai & QBot) and other variants, high-impact exploits, advanced…

A lightweight Python-based security assessment tool for detecting dangerous Cross-Origin Resource Sharing (CORS) misconfigurations - CVE-2025-34291.

A collection of awesome resources related AI security

A simple CORS misconfiguration scanner

TheftFuzzer is a tool that fuzzes Cross-Origin Resource Sharing implementations for common misconfigurations.

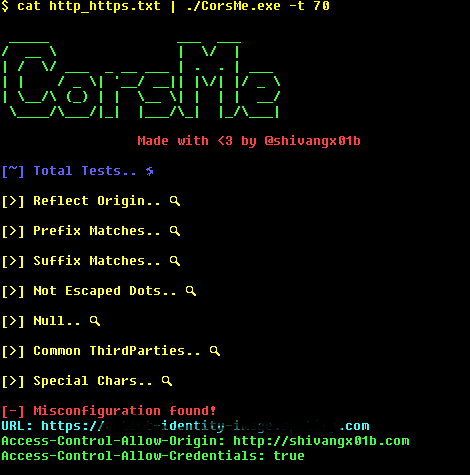
Cross Origin Resource Sharing MisConfiguration Scanner

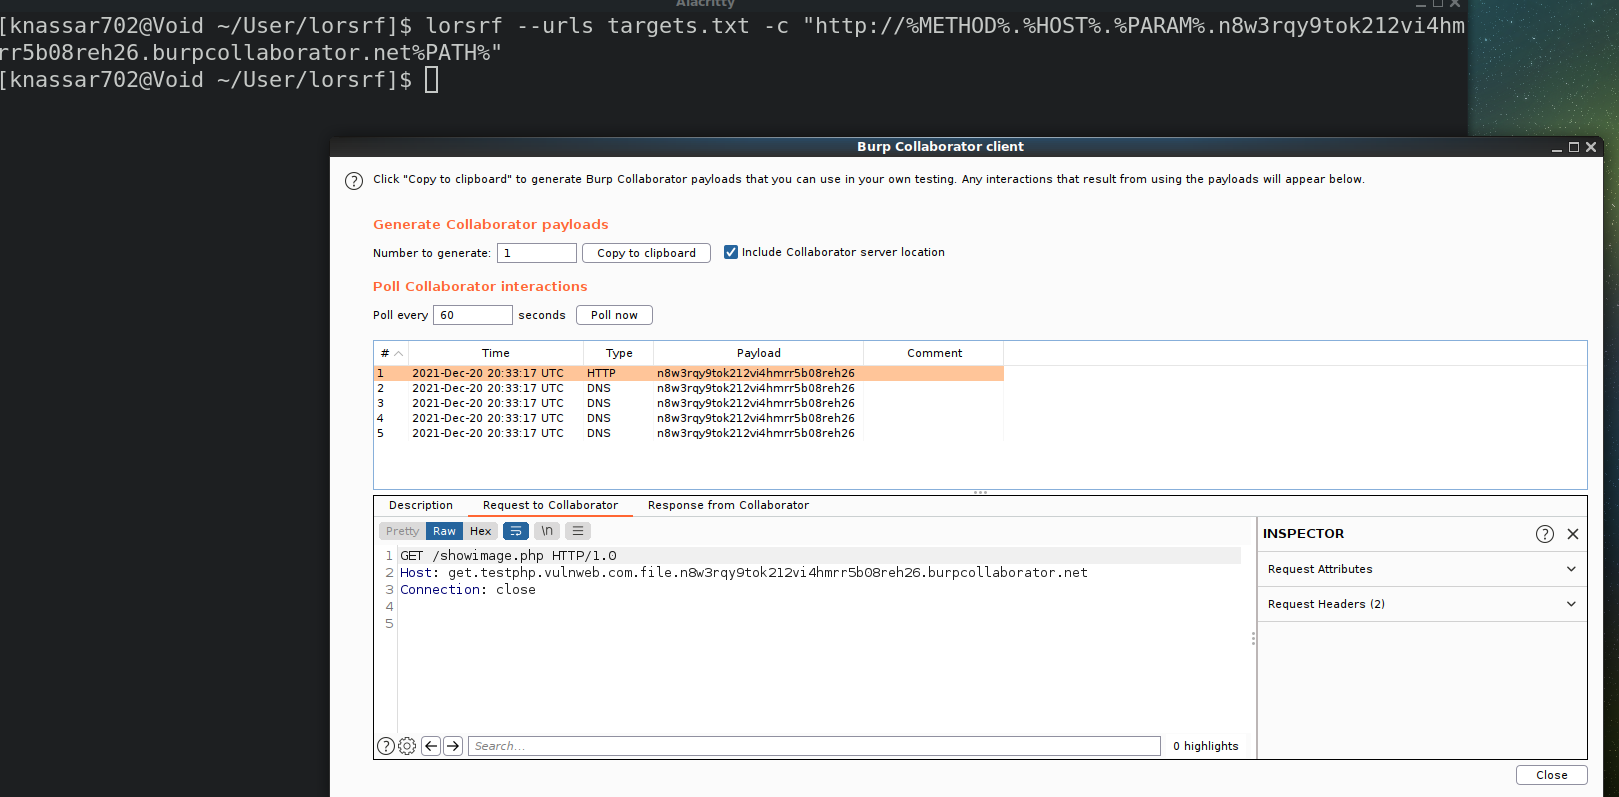
Fast CLI tool to find the parameters that can be used to find SSRF or Out-of-band resource load :artificial_satellite: :crab:

Perform file-based malware scan on your on-prem servers with AWS

GCP resource scanner that evaluates access levels of compromised credentials by enumerating cloud services, projects, and IAM permissions across…

Automated security findings enrichment and impact evaluation tool for AWS. Enriches vulnerability data with resource context, associations, and tags…

Validation of best practices in your Kubernetes clusters

Automated CORS misconfiguration scanner that tests Origin header injection, wildcard reflection, and credential leakage across web applications and…