
v1ew-s0urce
 cro-thehacker/v1ew-s0urce
Python-based penetration testing framework and reconnaissance toolkit offering port scanning, information gathering, and network scanning modules for…
information-gatheringnetwork-mappingpenetration-testing+5
91
cro-thehacker/v1ew-s0urcePython-based penetration testing framework and reconnaissance toolkit offering port scanning, information gathering, and network scanning modules for…
 qyvora/qyvora-anansi
Terminal-first attack surface intelligence engine. Built for speed, portability, and raw technical signal.
 karim852/kumo-domain-recon-tool
Domain OSINT and security reconnaissance framework running 26 parallel modules for DNS, ports, subdomains, leaked credentials, exposed endpoints,…
 ghostlyrootb2h/cve-2026-82222
Exploit framework for CVE-2026-82222, an unauthenticated RCE in GiveWP WordPress plugin. Supports mass scanning, auto-detection, multi-threading,…
 dmonst3r/wordpressmassexploiter
[discontinued] Mass exploiter of CVE-2015-1579 for WordPress CMS
 ridpath/terrminus-cve-2026-2406
AsyncIO Scanner & Exploitation Framework for CVE-2026-24061 (Telnet NEW_ENVIRON Auth Bypass). Features high-concurrency discovery, passive…
 marklindsey11/gh-repo-clone-marklindsey11--cve-2021-44228_scanner-applications-that-are-vulnerable-to-the-log4j-cv
Scans applications for the Log4Shell vulnerability (CVE-2021-44228) to identify systems at risk of remote code execution.
 fckoo/nanwinata-cve-2024-52301
Scans for CVE-2024-52301, an argument injection vulnerability in Laravel, using subfinder and httpx to identify affected web applications.
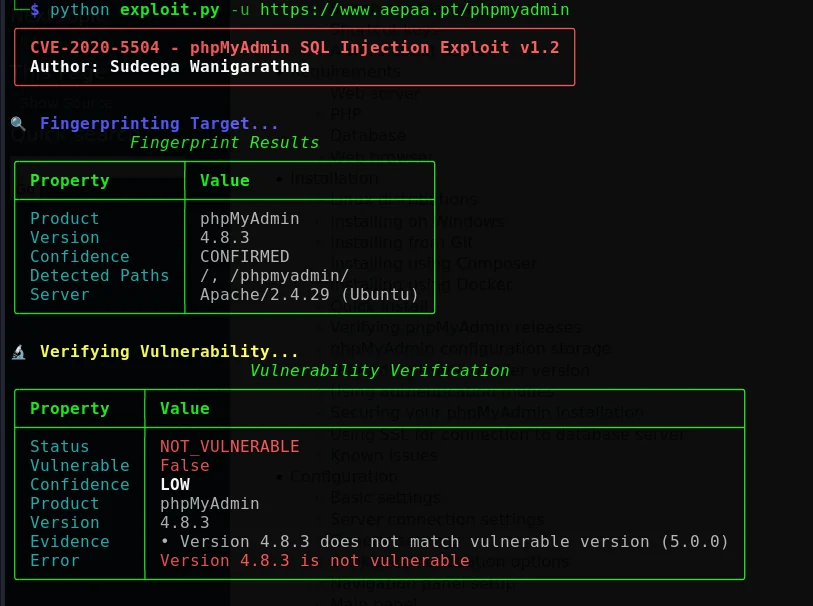 cerberusmrxi/phpmyadmin-cve-2020-5504-exploit
Authorized SQL injection exploitation framework for CVE-2020-5504 in phpMyAdmin, featuring automated database enumeration, blind injection, proxy…
 sdnewhop/sdwan-harvester
:globe_with_meridians: Automatically enumerate and fingerprint SD-WAN nodes on the internet
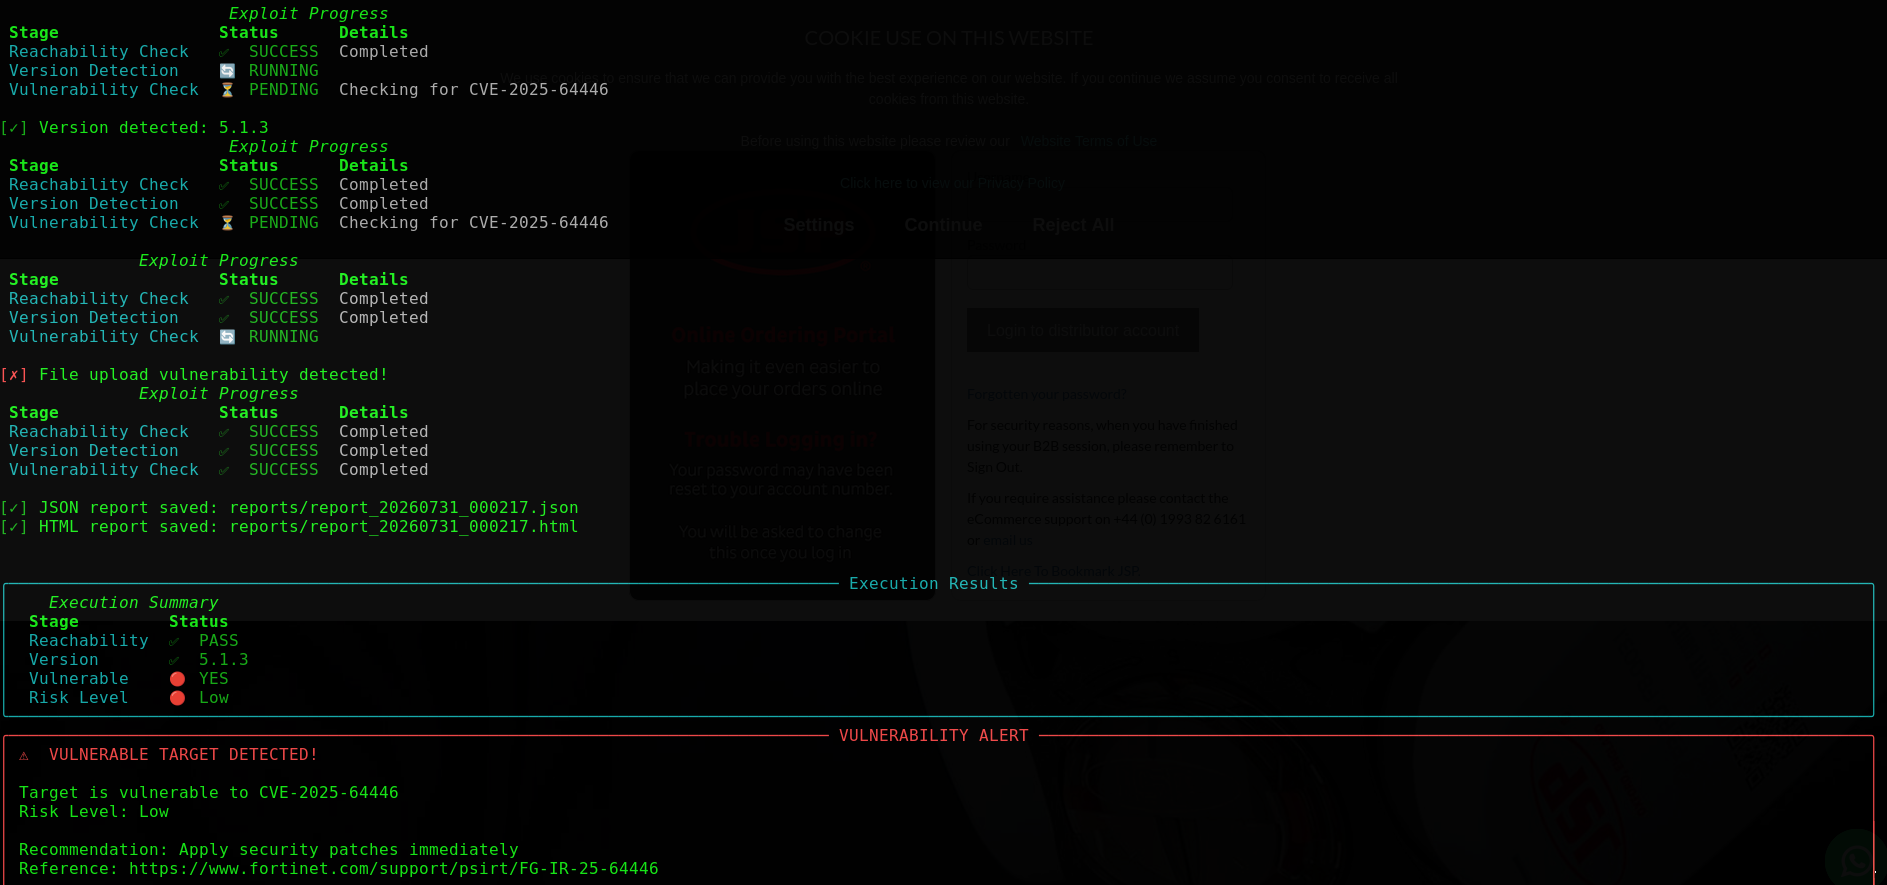 cerberusmrxi/fortiweb-cve-2025-64446-rce-exploit
Security research tool for FortiWeb CVE-2025-64446 vulnerability. Automated exploitation framework with advanced logging, real-time metrics, proxy…
 xkillbit/cve-2025-55182-scanner
Passive vulnerability scanner for CVE-2025-55182 and CVE-2025-66478, detecting unauthenticated RCE in React Server Components via framework…
 shinthink/solrradar
☄️ Mass reconnaissance & exploitation framework for Apache Solr CVE-2026-44825 — Velocity template injection to RCE
 nyakki-labs-0x420/myesve
CVE-2024-38475 exploitation & scanning tool with Mullvad VPN rotation
 owasp/nettacker
Automated Penetration Testing Framework - Open-Source Vulnerability Scanner - Vulnerability Management
 vulnquest58/pressvector
PressVector - Advanced WordPress Vulnerability Scanner CVE-2026-63030 (REST batch route confusion) / CVE-2026-60137 (SQLi) Developer: Vulnquest
 tjnull/cygor
An modular asset discovery framework written in python to automate the repeating manual work
 gobysec/cve-2019-0708
BlueKeep (CVE-2019-0708) vulnerability checker integrated with Goby's network asset discovery and scanning framework for rapid security assessment.