watchTowr-vs-Citrix-Netscaler-CVE-2026-88772

Detection artifact generator for Citrix NetScaler CVE-2026-88772 that builds a DTLS pre-auth buffer overflow payload to verify remote code execution.

Detection artifact generator for Citrix NetScaler CVE-2026-88772 that builds a DTLS pre-auth buffer overflow payload to verify remote code execution.

CVE-2026-60004 — Gitea/Forgejo Diffpatch Git Hook RCE. Bare clone → post-index-change hook injection. CVSS 9.8 | CWE-94 | Gitea < 1.27.1

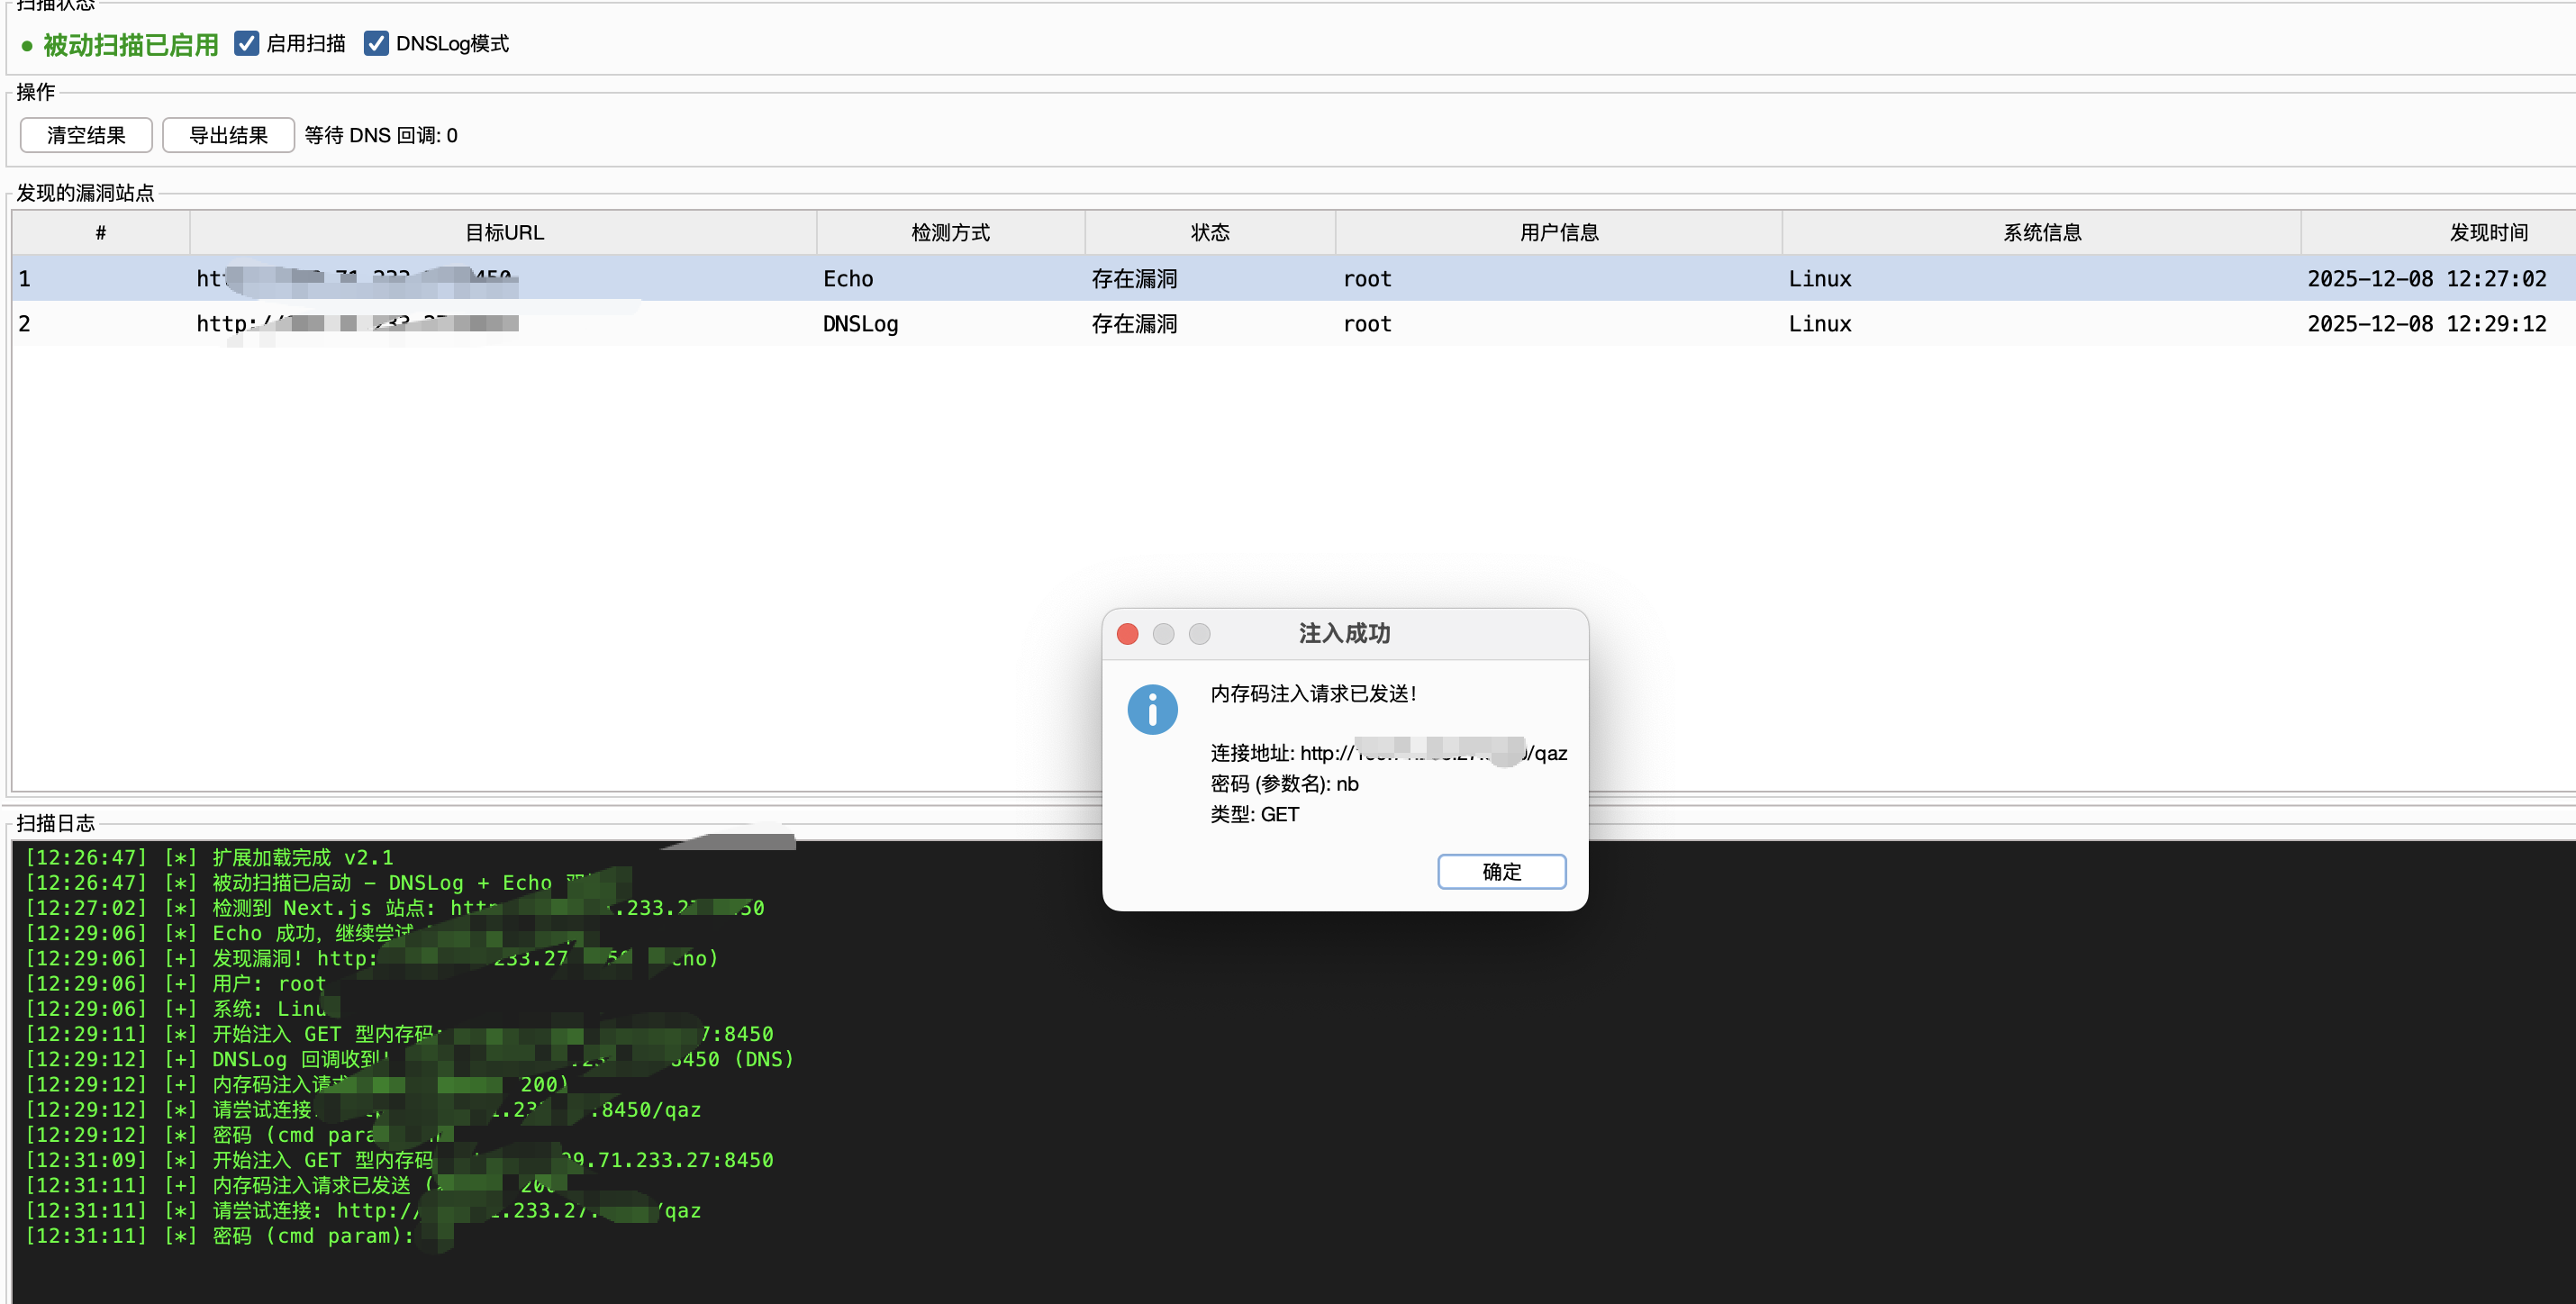
使用burp自动检测CVE-2025-55182 Next.js RCE 漏洞

Detection artifact generator for FortiWeb CVE-2025-25257, exploiting unauthenticated SQL injection to achieve remote code execution via hex-encoded…

Controlled penetration testing lab demonstrating CVE-2011-2523 exploitation and mitigation techniques.

💉 Blind SQL Injection → RCE exploit for Control Web Panel (CWP) ≤ 0.9.8.1224 — userRes POST → INTO DUMPFILE → cwpsvc shell

REC Exploit is a Python-based security testing tool that automates detection of potential RCE conditions in web applications under authorized…

Check list of URLs against Log4j vulnerability CVE-2021-44228

Automated scanner & post-exploitation toolkit for CVE-2026-41940 — cPanel & WHM root authentication bypass via session-file CRLF injection

Automatic Mass Tool for checking vulnerability in CVE-2022-4060 - WordPress Plugin : User Post Gallery <= 2.19 - Unauthenticated RCE

Shell script to scan domains for CVE-2024-4577 PHP remote code execution vulnerability via crafted POST requests, exporting vulnerable targets for…

Proof-of-concept exploit script for CVE-2024-24919 that scans target URLs via HTTP POST requests, analyzes responses for unauthorized access or data…

Batch scanner and exploitation script for CVE-2017-9841, a PHPUnit remote code execution vulnerability triggered via HTTP POST requests with PHP…

Mass checks VMware vCenter servers for CVE-2021-22005 RCE by sending telemetry API POST requests and flagging HTTP 201 responses as vulnerable.

Burp extension to scan Log4Shell (CVE-2021-44228) vulnerability pre and post auth.

Time-based SQL injection detection template for SMM Panel targeting the service_detail parameter via crafted POST requests to /ajax_data, using…

Linux post exploitation privilege escalation enumeration

Kubesploit is a cross-platform post-exploitation HTTP/2 Command & Control server and agent written in Golang, focused on containerized environments.