

forbidden
 ivan-sincek/forbidden
Bypass 4xx HTTP response status codes and more. The tool is based on Python Requests, PycURL, and HTTP Client.
fuzzingids-ips-evasioninformation-gathering+5
257
ivan-sincek/forbiddenBypass 4xx HTTP response status codes and more. The tool is based on Python Requests, PycURL, and HTTP Client.
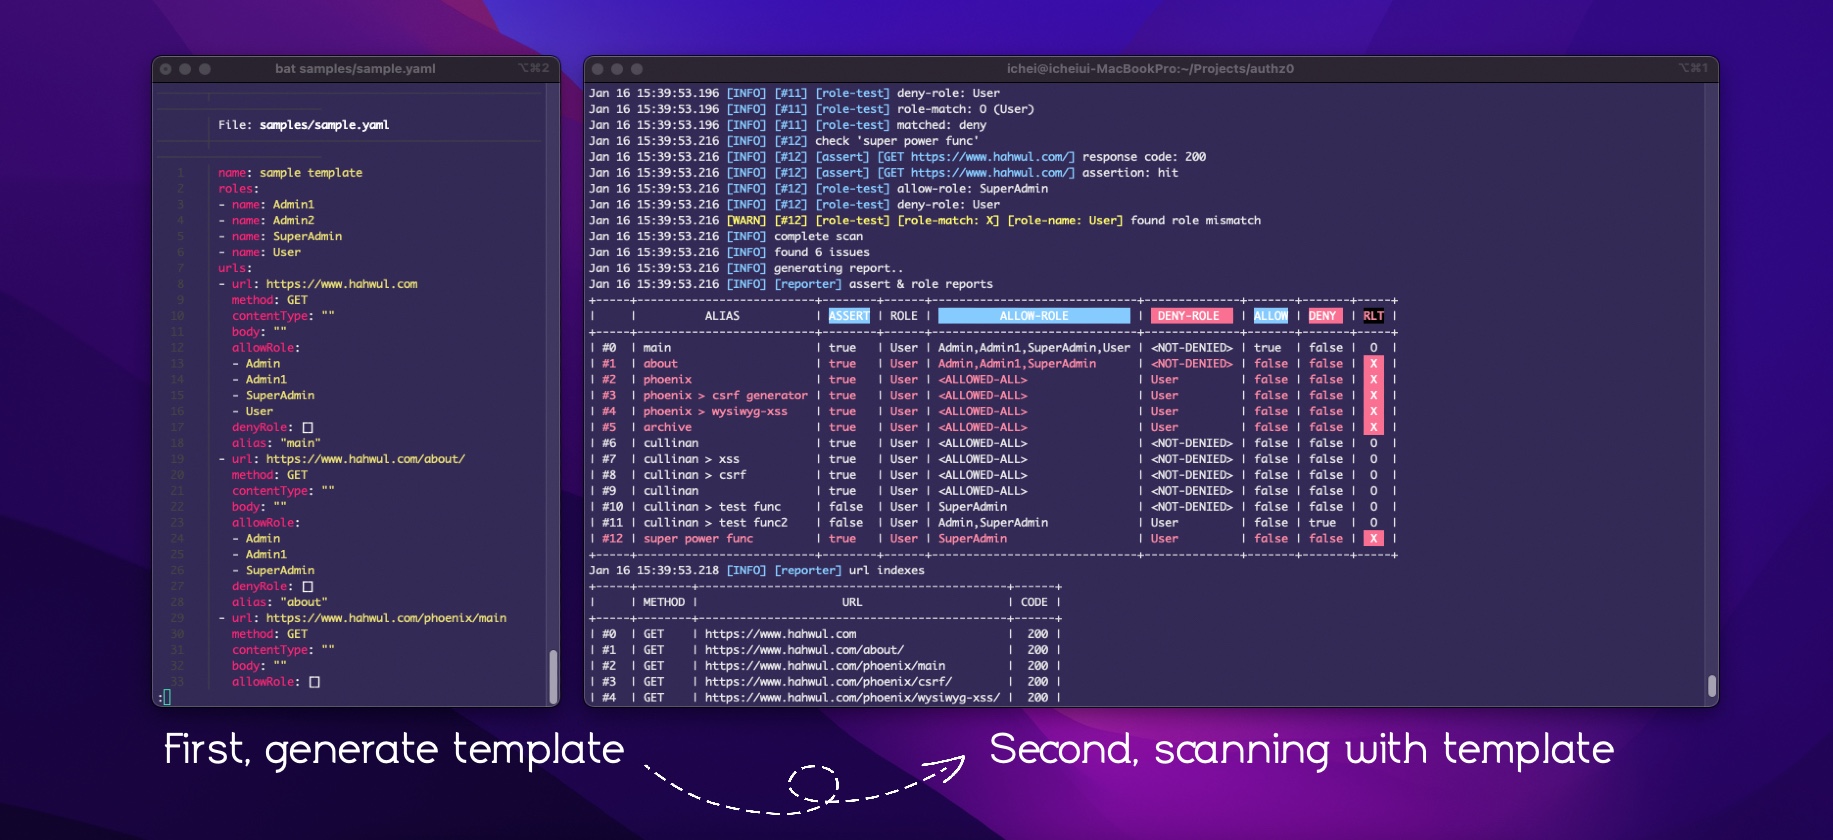 hahwul/authz0
Automated authorization testing tool that detects unauthorized access by scanning URLs with role-based credentials using YAML templates.
 squ1shification/grafana-plugin-enumerator-cve-2021-43798
Bash-based scanner that enumerates Grafana plugin IDs and tests for CVE-2021-43798 directory traversal by attempting to read /etc/passwd or win.ini…
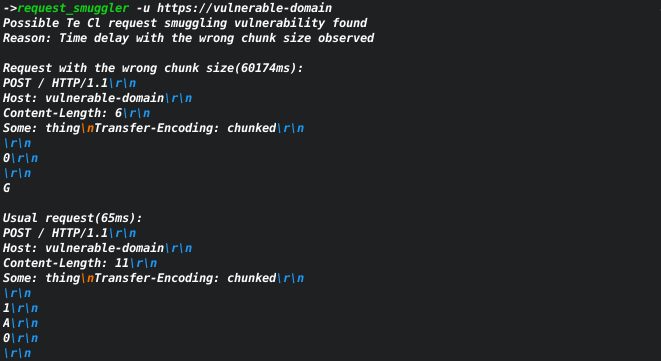 sh1yo/request_smuggler
Http request smuggling vulnerability scanner
 kvesta/vesta
A static analysis of vulnerabilities, Docker and Kubernetes cluster configuration detect toolkit based on the real penetration of cloud computing
 preempt/ntlm-scanner
A simple python tool based on Impacket that tests servers for various known NTLM vulnerabilities
 dywhoami/cve-2021-34527-scanner-based-on-cube0x0-poc
Scanner for Windows Print Spooler service vulnerability CVE-2021-34527, based on cube0x0's PoC, enabling detection of exploitable targets.