

polaris
 fairwindsops/polaris
Validation of best practices in your Kubernetes clusters
cloud-infrastructure-securitycloud-securityconfiguration-auditing+5
3.4k1 day ago
fairwindsops/polarisValidation of best practices in your Kubernetes clusters
 ottosulin/awesome-ai-security
A collection of awesome resources related AI security
 santandersecurityresearch/corsair_scan
Automated CORS misconfiguration scanner that tests Origin header injection, wildcard reflection, and credential leakage across web applications and…
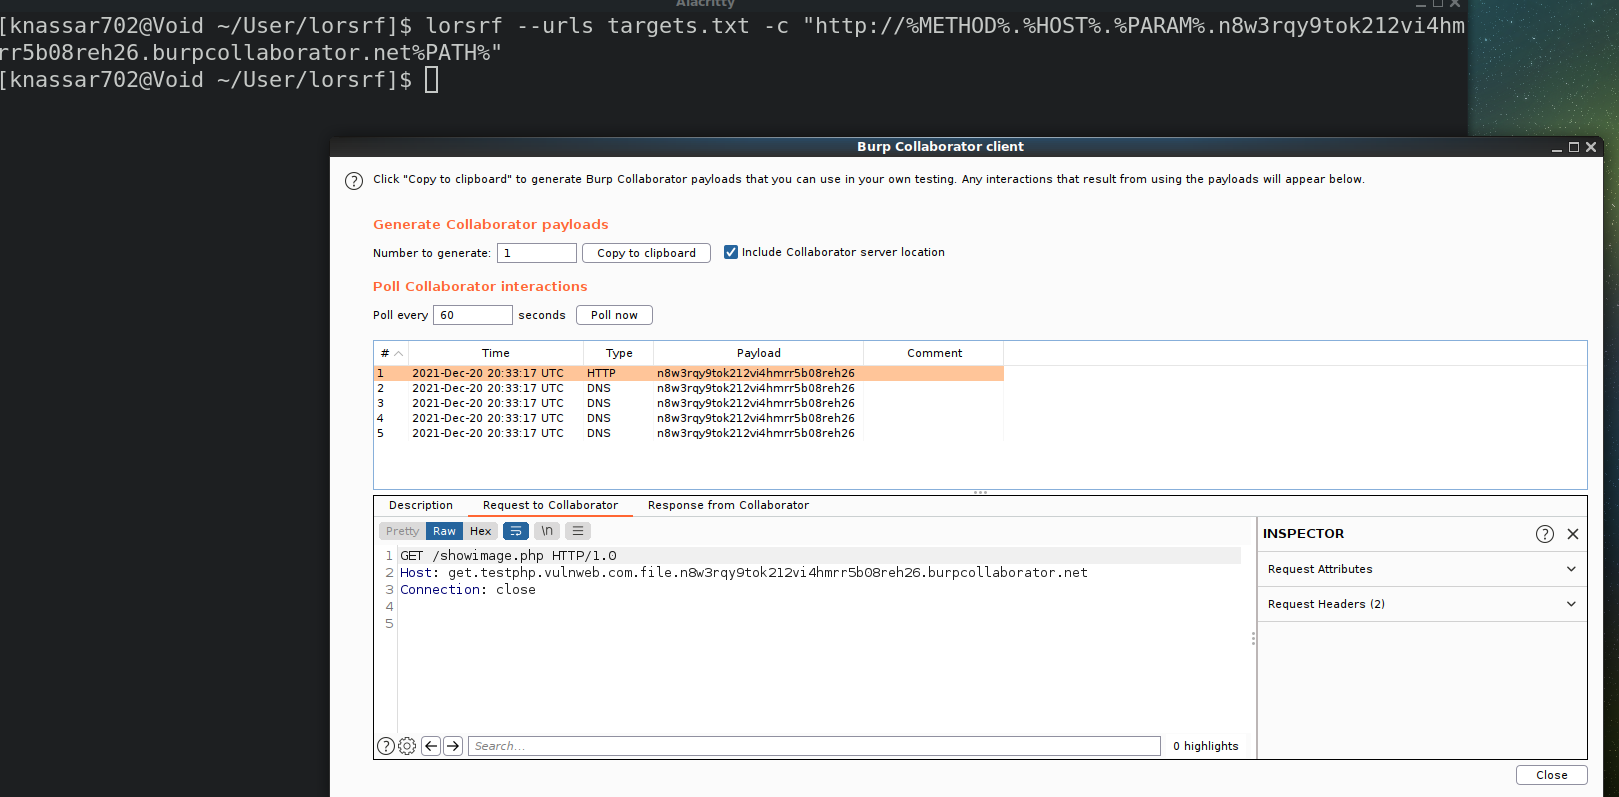 mindpatch/lorsrf
Fast CLI tool to find the parameters that can be used to find SSRF or Out-of-band resource load :artificial_satellite: :crab:
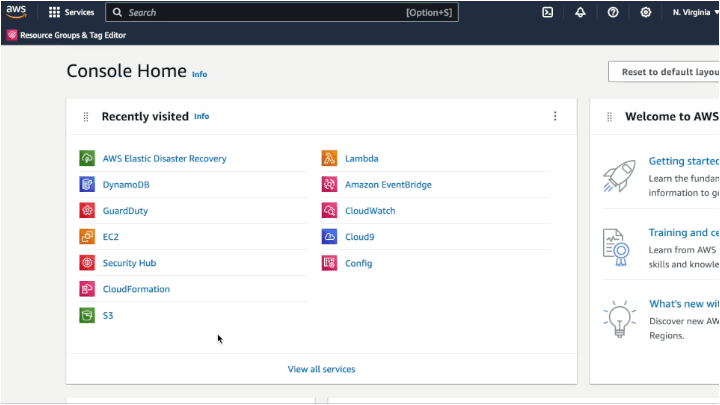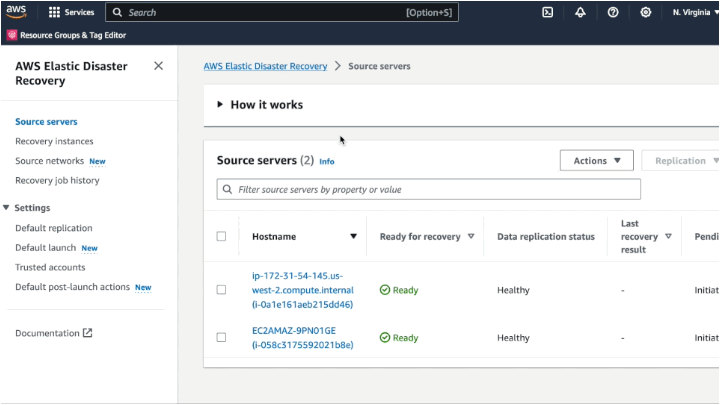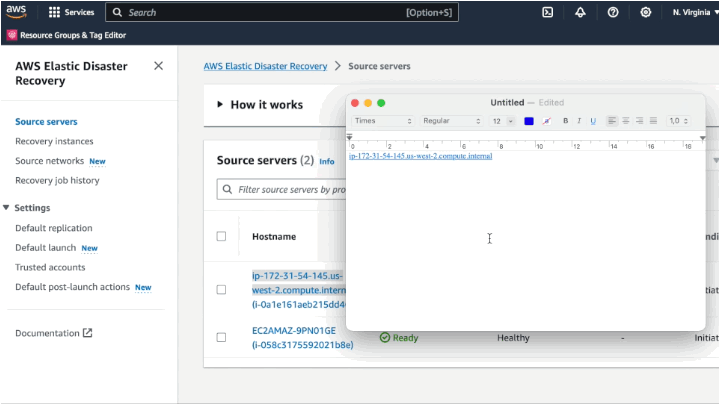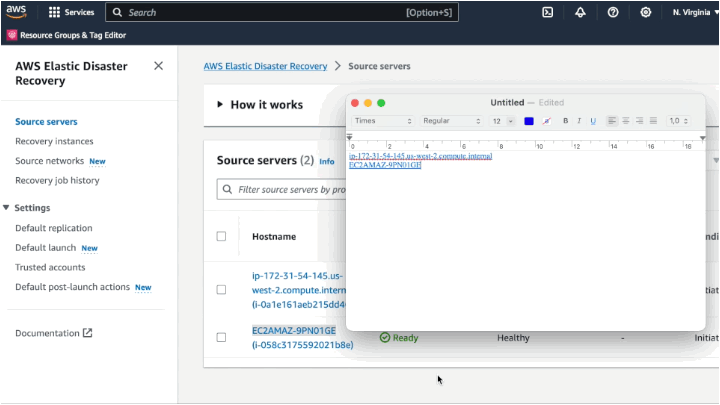 aws-samples/drs-malware-scan
Perform file-based malware scan on your on-prem servers with AWS
 r00ts3c/ddos-rootsec
Explore RootSec's DDOS Archive, featuring top-tier scanners, powerful botnets (Mirai & QBot) and other variants, high-impact exploits, advanced…
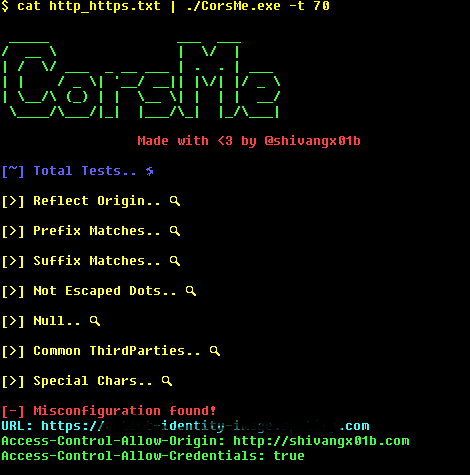 shivangx01b/corsme
Cross Origin Resource Sharing MisConfiguration Scanner
 google/gcp_scanner
GCP resource scanner that evaluates access levels of compromised credentials by enumerating cloud services, projects, and IAM permissions across…
 rub-nds/corstest
A simple CORS misconfiguration scanner
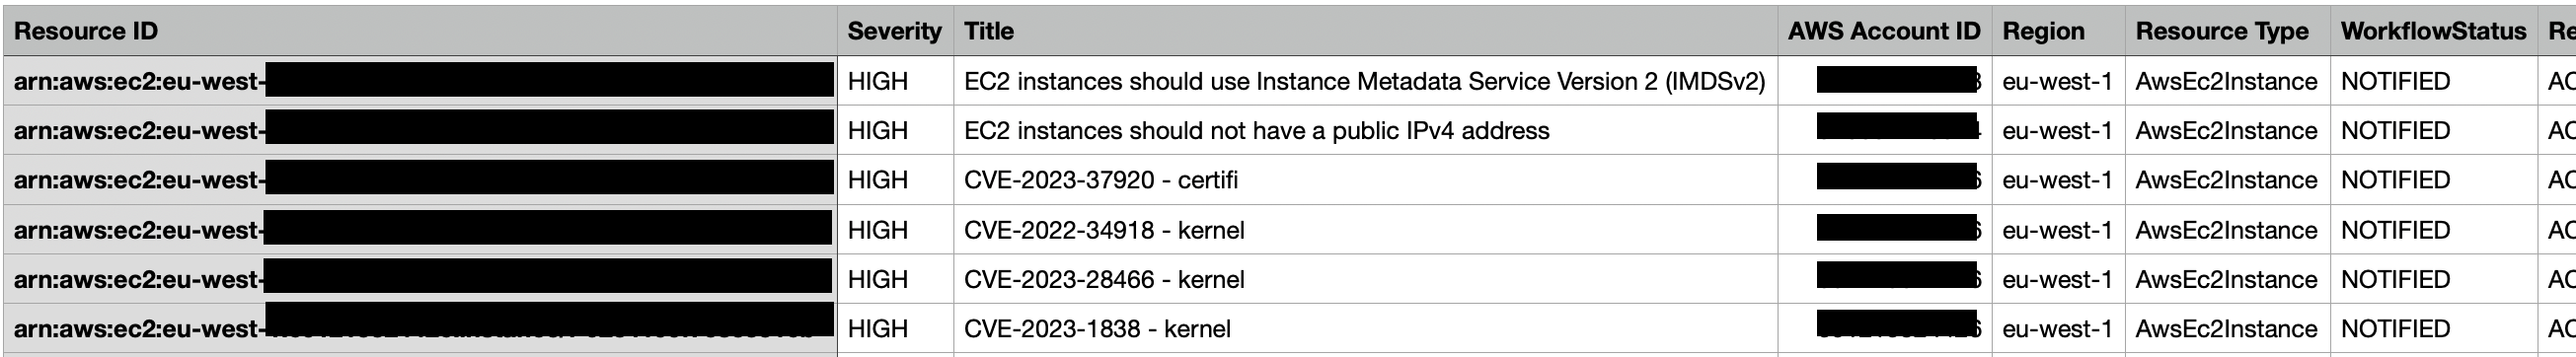 gabrielsoltz/metahub
Automated security findings enrichment and impact evaluation tool for AWS. Enriches vulnerability data with resource context, associations, and tags…
 amnnrth/cve-2025-34291_cors_security_scanner
A lightweight Python-based security assessment tool for detecting dangerous Cross-Origin Resource Sharing (CORS) misconfigurations - CVE-2025-34291.
 lc/theftfuzzer
TheftFuzzer is a tool that fuzzes Cross-Origin Resource Sharing implementations for common misconfigurations.
 aquasecurity/trivy-plugin-kubectl
A Trivy plugin that scans the images of a kubernetes resource
 r00tpgp/http-pulse_ssl_vpn.nse
Nmap NSE script to detect Pulse Secure SSL VPN file disclosure CVE-2019-11510
 aquasecurity/trivy-enforcer
[EXPERIMENTAL] Kubernetes Operator for Image Assurance
 graysignal/apache-ofbiz-auth-bypass-and-rce-exploit-cve-2023-49070-cve-2023-51467
This exploit scans whether the provided target is vulnerable to CVE-2023-49070/CVE-2023-51467 and also exploits it depending on the choice of the…