

semgrep
 semgrep/semgrep
Lightweight static analysis for many languages. Find bug variants with patterns that look like source code.
api-securityapi-security-testingcode-analysis+9
17.4k1 day ago
semgrep/semgrepLightweight static analysis for many languages. Find bug variants with patterns that look like source code.
 samugit83/redamon
Autonomous AI red team framework that chains reconnaissance, exploitation, and post-exploitation into a single pipeline, then triages findings,…
 owasp/secretsifter
OWASP Incubator project: detects credentials exposed in browser-delivered content (JavaScript, config responses, live traffic).
 coreruleset/ftw
YAML-driven framework for testing Web Application Firewall (WAF) rules using OWASP Core Rule Set baselines. Automates regression detection and…
 ffffffff0x/f8x
红/蓝队环境自动化部署工具 | Red/Blue team environment automation deployment tool
 owasp/docksec
AI-powered Docker security scanner that explains vulnerabilities in plain English. An OWASP Lab Project.
 securecodebox/securecodebox
Kubernetes-native security scanning orchestrator that automates continuous vulnerability detection by integrating multiple open-source scanners into…
 cream-sec/cve-2019-0708-msf--
CVE-2019-0708-Msf-验证
 ashishb/android-security-awesome
A collection of android security related resources
 raghavd3v/crlfsuite
The most powerful CRLF injection (HTTP Response Splitting) scanner.
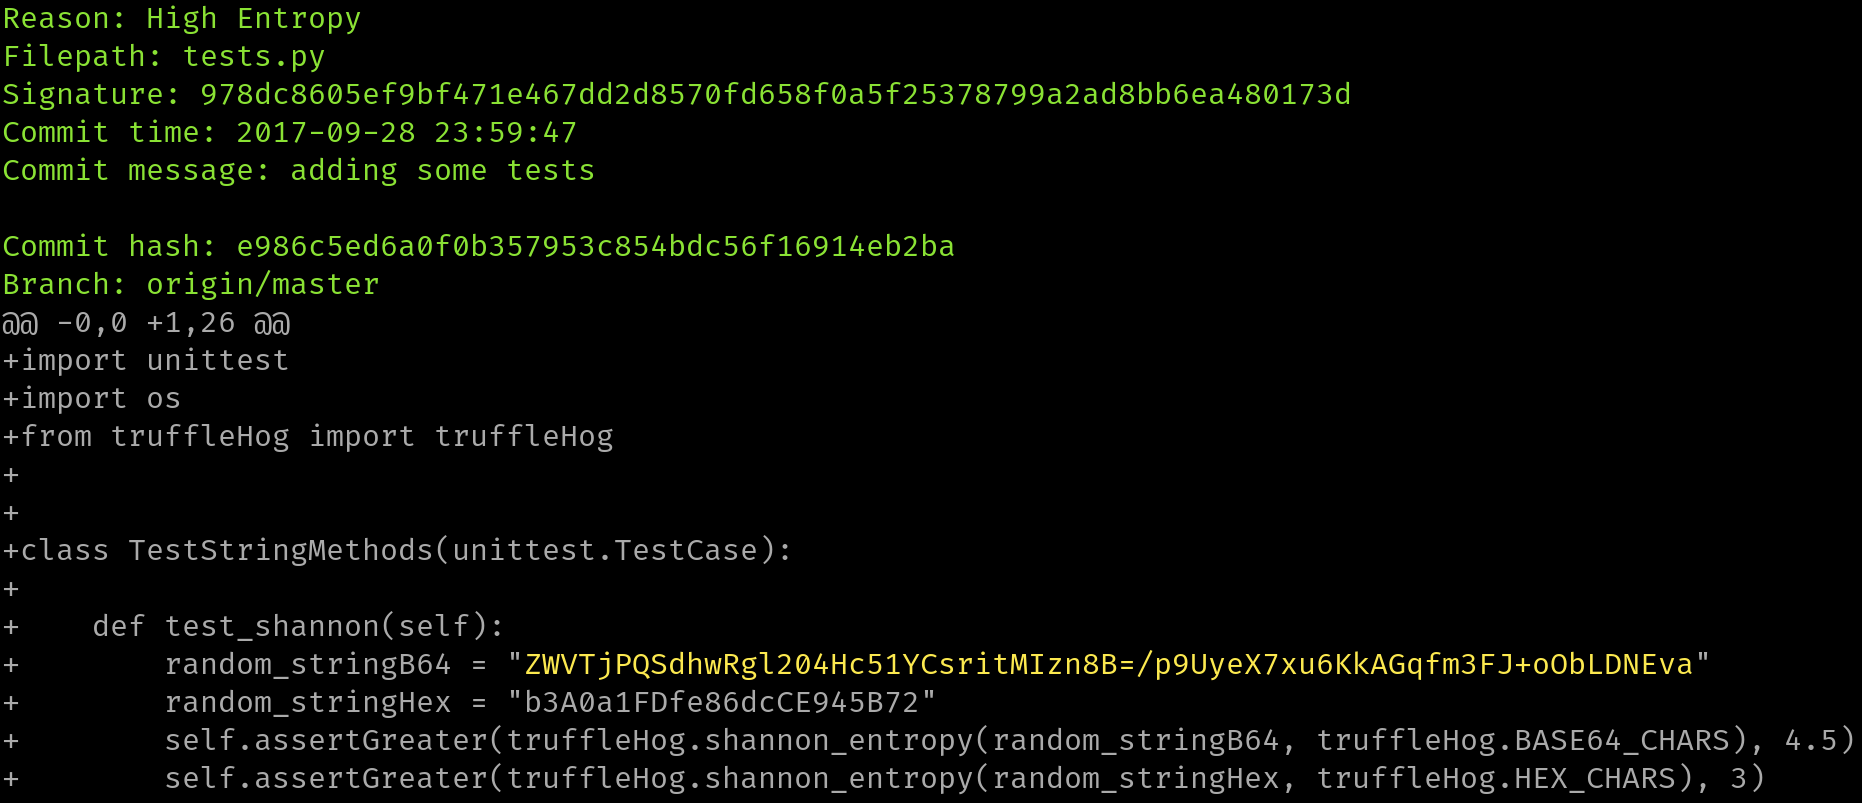 godaddy/tartufo
Searches through git repositories for high entropy strings and secrets, digging deep into commit history
 swiftdevcollective/xcodeprojectsecurity
A macOS app to scan Xcode project files for possible security issues.
 umidguluzada/cyberdefense-lab
A complete Blue Team Cybersecurity Lab featuring pfSense, Suricata, and ELK Stack for network monitoring and threat detection.
 daryllundy/cve-2025-53770
Network-based vulnerability scanner for detecting systems vulnerable to CVE-2025-53770 (unsafe deserialization). Includes PowerShell and Python…
 notsosecure/blacklist3r
Audits ASP.NET applications for pre-published machine keys to detect ViewState deserialization vulnerabilities and insecure forms authentication…
 jaeles-project/jaeles-signatures
Default signature for Jaeles Scanner
 projectdiscovery/nuclei-templates-ai
Repository of AI-generated Nuclei templates for public CVEs not yet covered by existing templates, enhancing detection speed and coverage 👾
 v1d1an/s1em
This project is a SIEM with SIRP and Threat Intel, all in one.